Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Havoc — The Havoc Framework | Kitploit
Tools/GitHubGitHub/havocframework/havoc
Penetration Testing FrameworksExploit FrameworksPayload GenerationShellcodePost-ExploitationCommand and ControlRed TeamingShellcode GenerationArchived
GitHubhavocframework/havoc

Havoc

The Havoc Framework

8.5k1.2k9511 months agoReviewed by Kitploit
View RepositoryWebsite
Share

Havoc


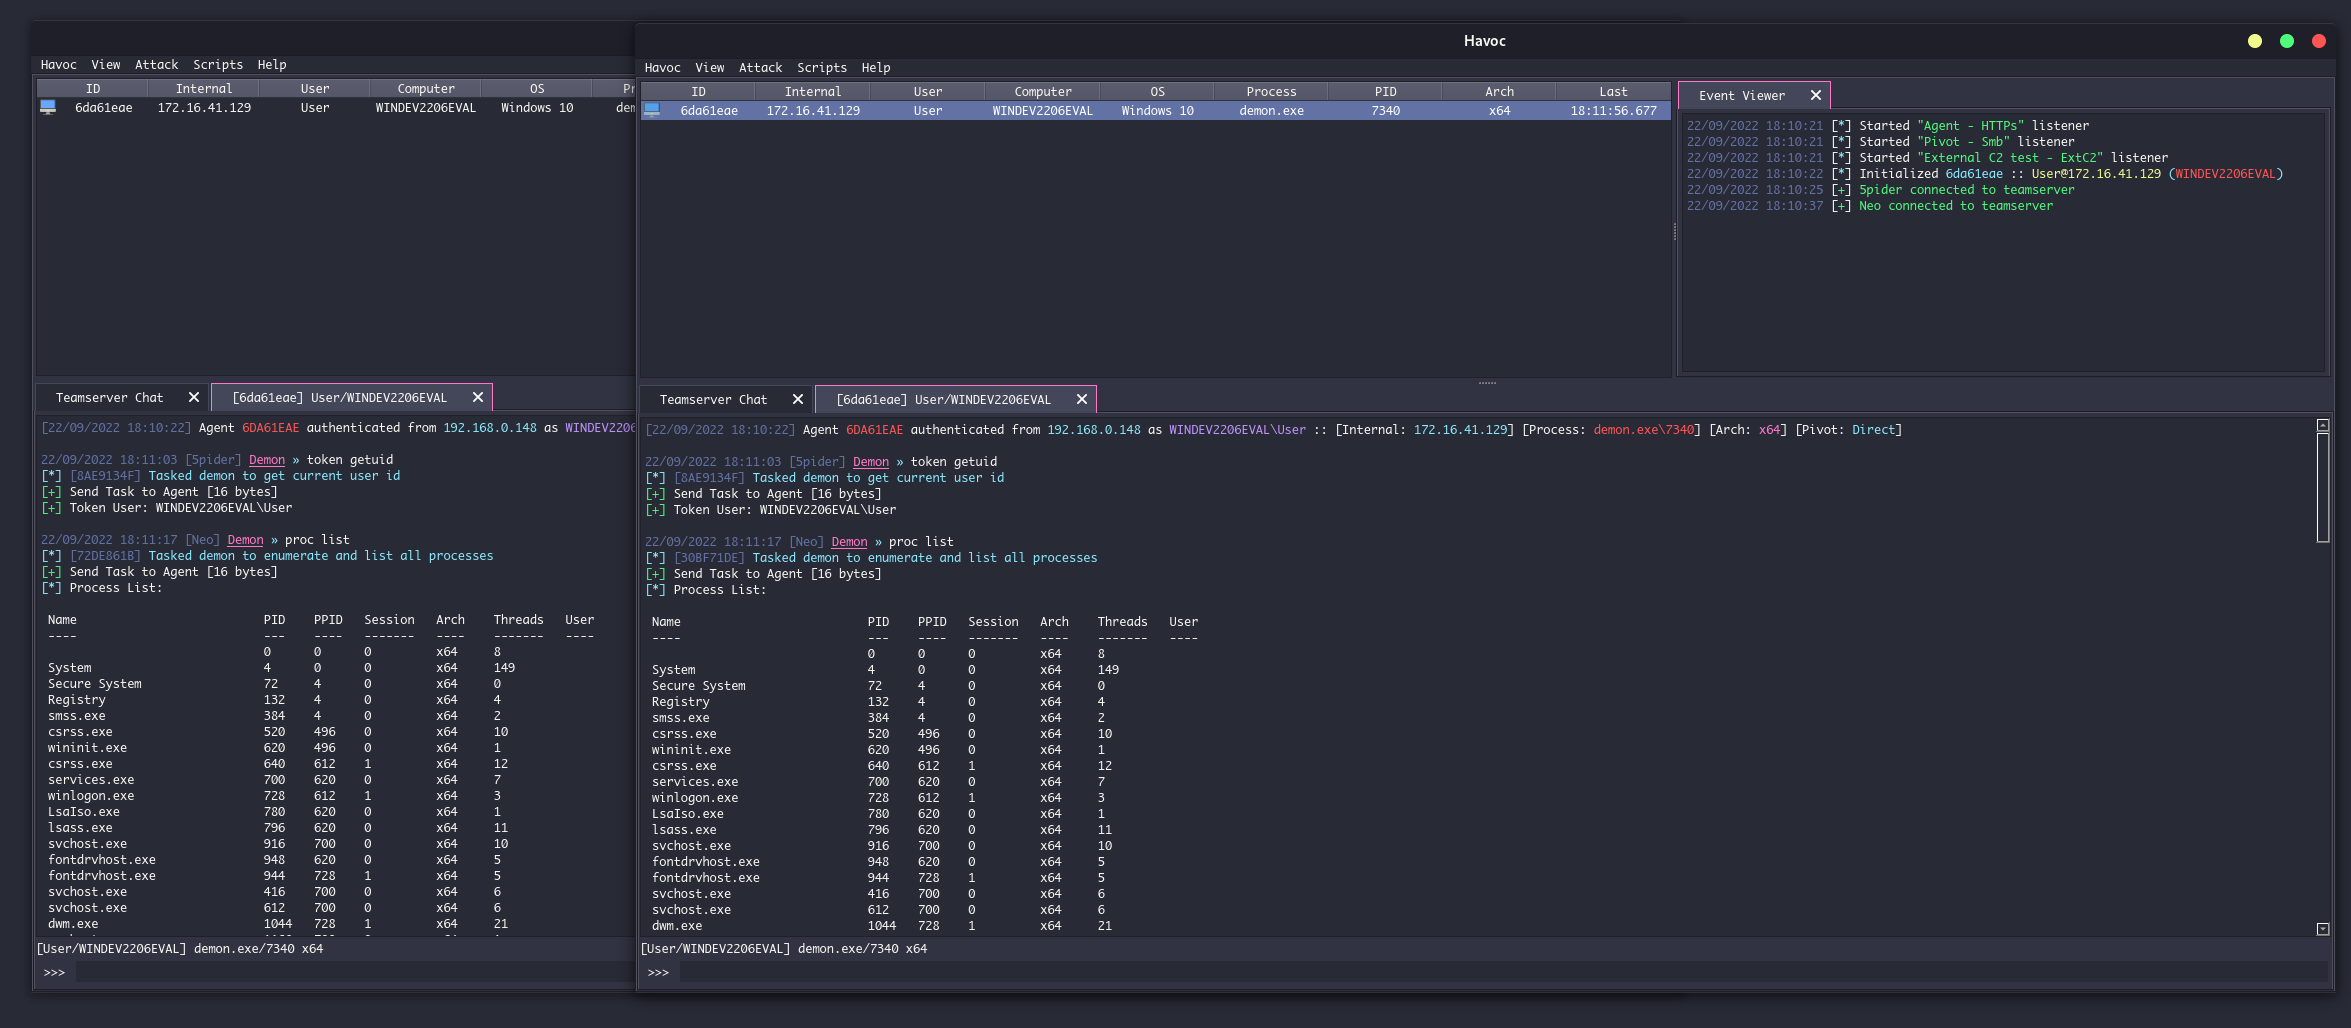
Havoc is a modern and malleable post-exploitation command and control framework, created by @C5pider.



Quick Start

Please see the Wiki for complete documentation.

Havoc works well on Debian 10/11, Ubuntu 20.04/22.04 and Kali Linux. It's recommended to use the latest versions possible to avoid issues. You'll need a modern version of Qt and Python 3.10.x to avoid build issues.

See the Installation docs for instructions. If you run into issues, check the Known Issues page as well as the open/closed Issues list.


Features

Client

Cross-platform UI written in C++ and Qt

  • Modern, dark theme based on Dracula

Teamserver

Written in Golang

  • Multiplayer
  • Payload generation (exe/shellcode/dll)
  • HTTP/HTTPS listeners
  • Customizable C2 profiles
  • External C2

Demon

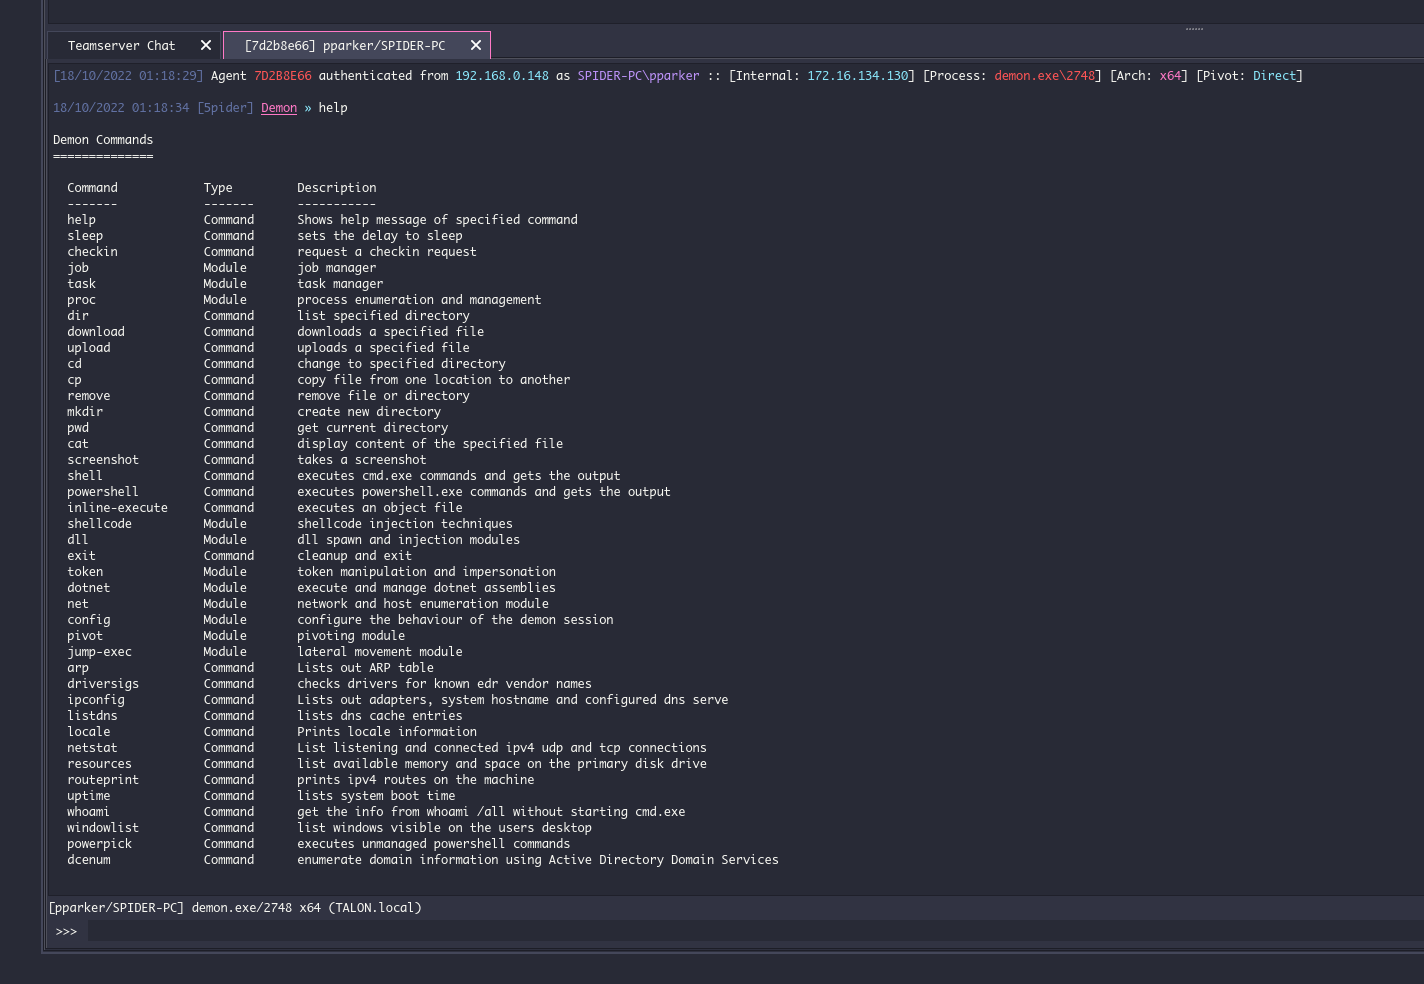
Havoc's flagship agent written in C and ASM
  • Sleep Obfuscation via Ekko, Ziliean or FOLIAGE
  • x64 return address spoofing
  • Indirect Syscalls for Nt* APIs
  • SMB support
  • Token vault
  • Variety of built-in post-exploitation commands
  • Patching Amsi/Etw via Hardware breakpoints
  • Proxy library loading
  • Stack duplication during sleep.

Extensibility

  • External C2
  • Custom Agent Support
    • Talon
  • Python API
  • Modules

Community

You can join the official Havoc Discord to chat with the community!

Note

Please do not open any issues regarding detection.

The Havoc Framework hasn't been developed to be evasive. Rather it has been designed to be as malleable & modular as possible. Giving the operator the capability to add custom features or modules that evades their targets detection system.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →