Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
190 results
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

command-and-controldatabase-securitydata-exfiltration+20
39.2k

10h 17m ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
12.2k11h 19m ago
mcp-gamehacking preview

mcp-gamehacking

GitHub1llu50ry/mcp-gamehacking

MCP server exposing a 4,100+ skill game-hacking and reverse-engineering knowledge base with source archives, specialized agents, subagents, plugins…

ai-assisted-reversingbinary-analysiscurated-resources+6
541 day ago
actual-php2shell preview

actual-php2shell

GitHubcookiengineer/actual-php2shell

🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)

binary-exploitationcontainer-securityexploitation+5
171 day ago
Medusa preview

Medusa

GitHubmythicagents/medusa

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…

command-and-controlexploit-frameworkslateral-movement+8
2112 days ago
ConfluenceC2 preview

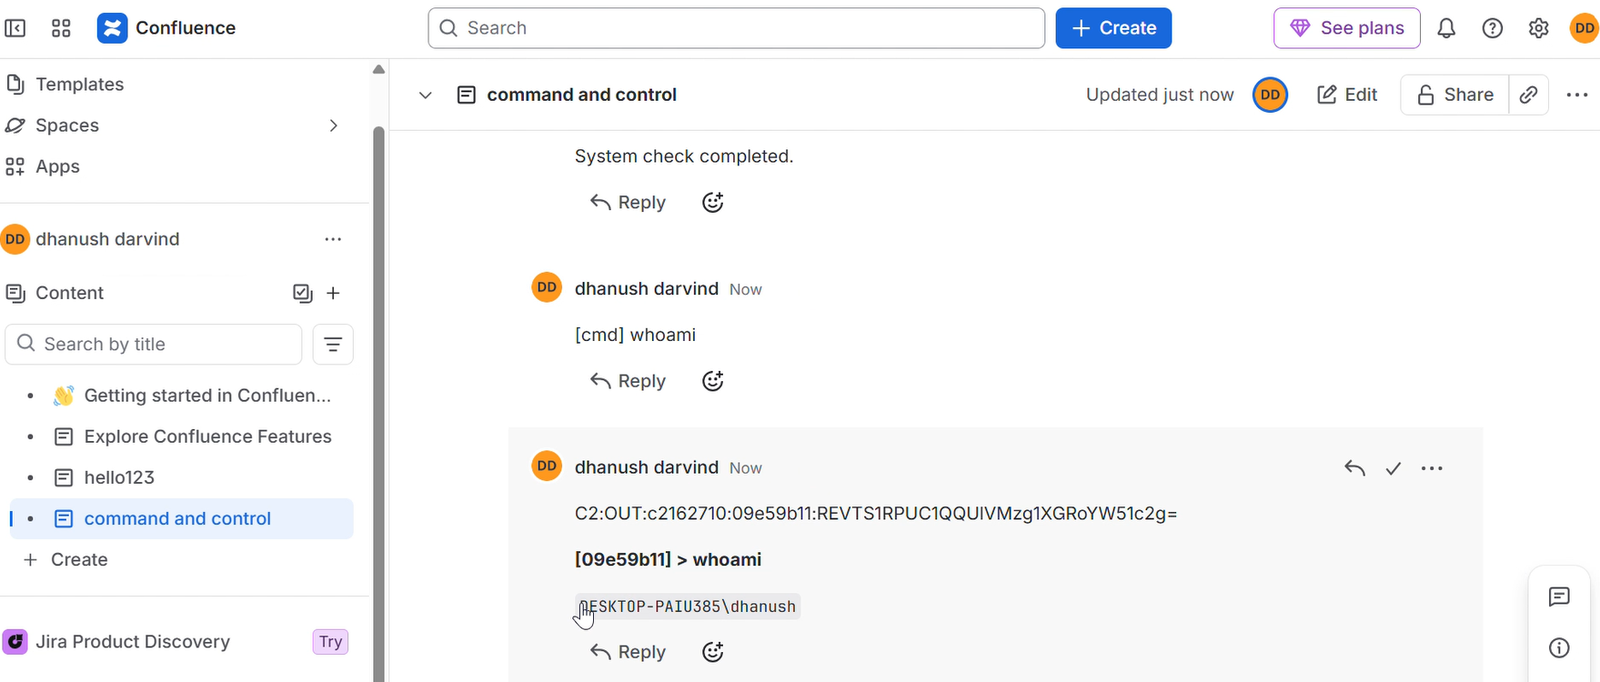
ConfluenceC2

GitHubdagowda/confluencec2

This is a project aimed to make every other Saas product a C2, confluence is just the beginning.

command-and-controldata-exfiltrationlateral-movement+9
132 days ago
SyscallRevenant preview

SyscallRevenant

GitHubsilentisvox/syscallrevenant

Clean Indirect Syscalls with Syscall Tampering.

binary-exploitationexploitationids-ips-evasion+6
15 days ago
NTDLL-reconstruction preview

NTDLL-reconstruction

GitHubsk4r4b/ntdll-reconstruction

A technique that mixes NTDLL unhooking and hellsgate gate varients

binary-exploitationdefensive-toolsids-ips-evasion+6
327 days ago
ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent preview

ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent

GitHubjm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent

Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

command-and-controlexploit-frameworksids-ips-evasion+5
9921 days ago
exploitgym preview

exploitgym

GitHubsunblaze-ucb/exploitgym

ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.

ai-securitybinary-exploitationctf+9
1.2k24 days ago
InjectSetConsole preview

InjectSetConsole

GitHubtwosevenonet/injectsetconsole

Proof of Concept for Process Code Injection Without Using WriteProcessMemory

command-and-controlexploitationids-ips-evasion+7
15526 days ago
Neo preview

Neo

GitHubstillbigjosh/neo

The NeoC2 Framework

command-and-controlexploit-frameworksids-ips-evasion+8
401 month ago
unicorn preview

unicorn

GitHubtrustedsec/unicorn

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

command-and-controlexploit-frameworksids-ips-evasion+8
4.0k1 month ago
MS09-050 preview

MS09-050

GitHubbytejmp/ms09-050

Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…

exploitationinformation-gatheringnetwork-security+7
1 month ago
Project-Onyx preview

Project-Onyx

GitHubx-3306/project-onyx

Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…

ai-securitycommand-and-controlcryptography+6
1191 month ago
MSRMapper preview

MSRMapper

GitHubull0a/msrmapper

Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…

binary-exploitationexploitationmemory-forensics+6
31 month ago
EVENSTAR preview

EVENSTAR

GitHubwinterknife/evenstar

Intel 64/Windows low-level experiments

binary-analysisbinary-exploitationdebuggers+5
1181 month ago
CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter preview

CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter

GitHubsneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter

Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.

binary-exploitationexploitationmemory-forensics+3
51 month ago
Previous12…11Next