metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

CVE-2024-36401 exploit with webshell-like functionality for limited environments, supporting self-signed TLS sessions and remote command execution…

MCP server exposing a 4,100+ skill game-hacking and reverse-engineering knowledge base with source archives, specialized agents, subagents, plugins…

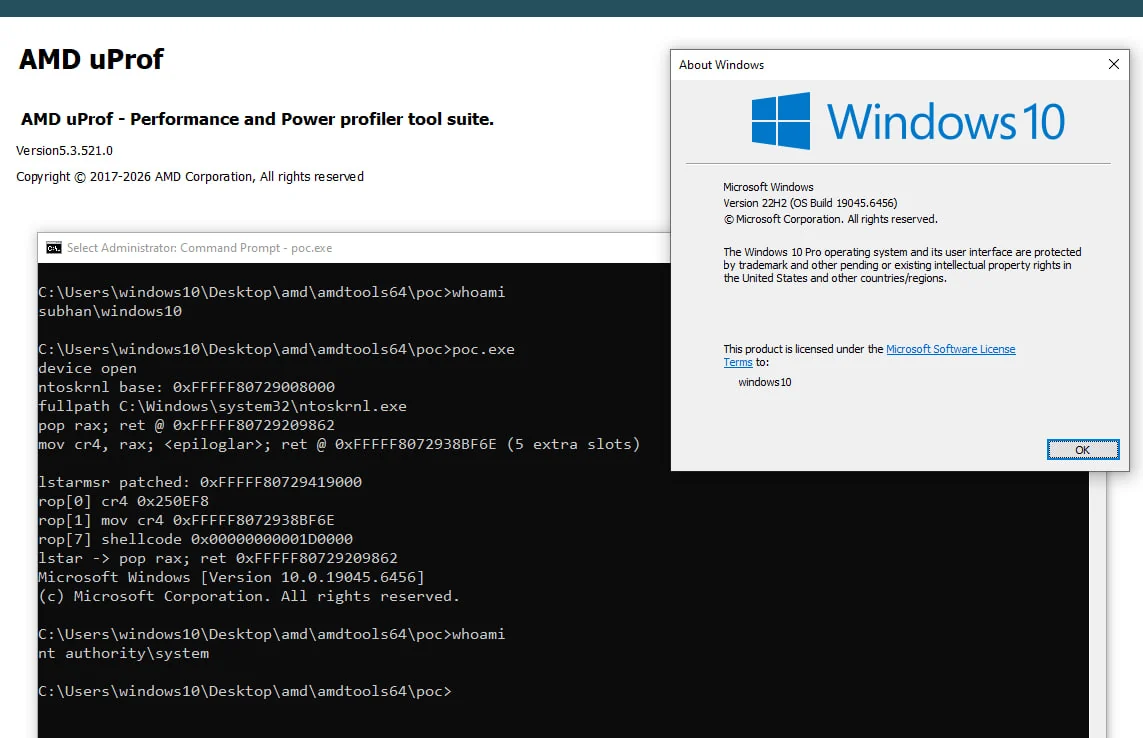
Proof-of-concept exploiting AMD AmdTools64.sys MSR read/write IOCTLs to overwrite IA32_LSTAR, bypass SMEP and escalate from administrator to SYSTEM…

exploitdb // The official Exploit-Database repository

Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…

Clean Indirect Syscalls with Syscall Tampering.

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…

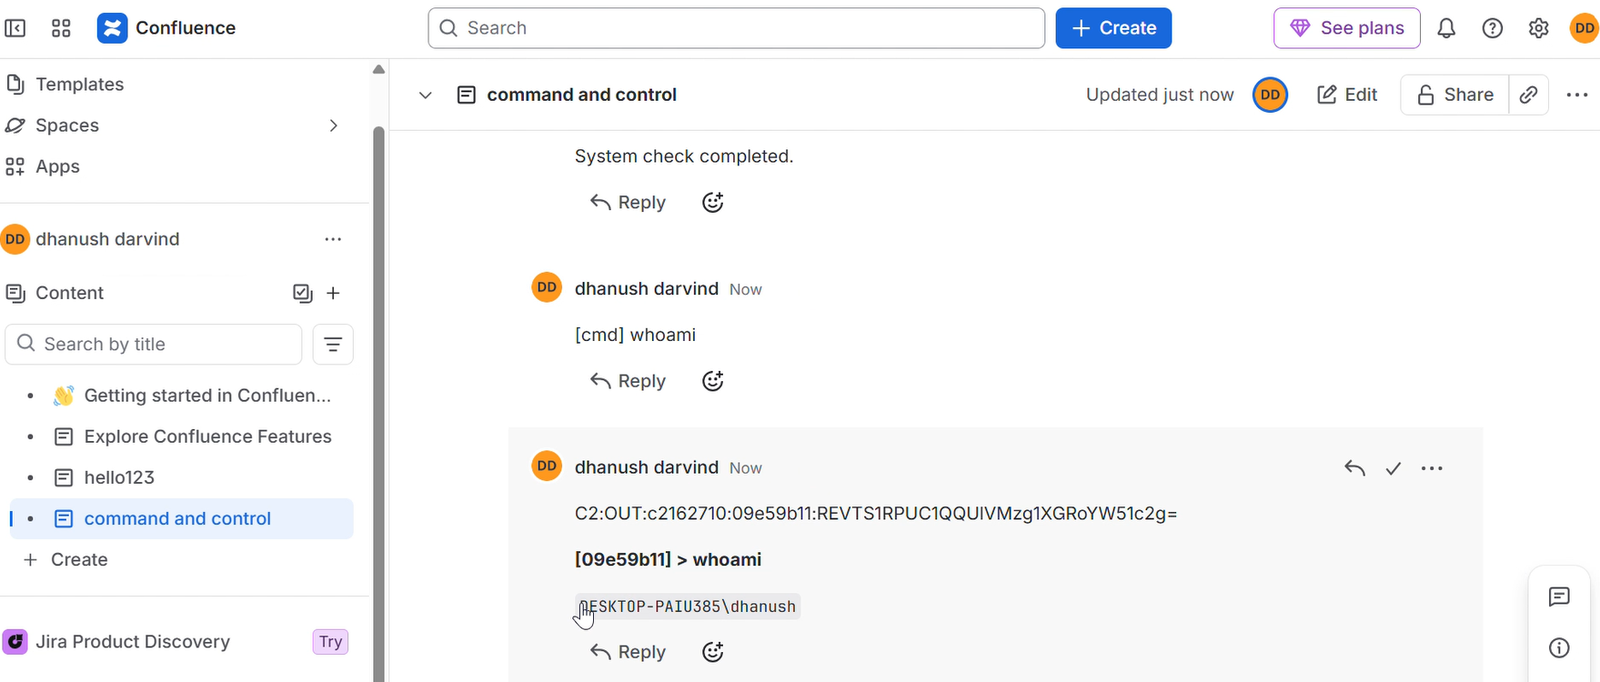
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.

Linux C2 beacon with native in-memory ELF BOF loader, AES-256-CFB encrypted polling, and a Python C2 server for fileless post-exploitation modules.

Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…

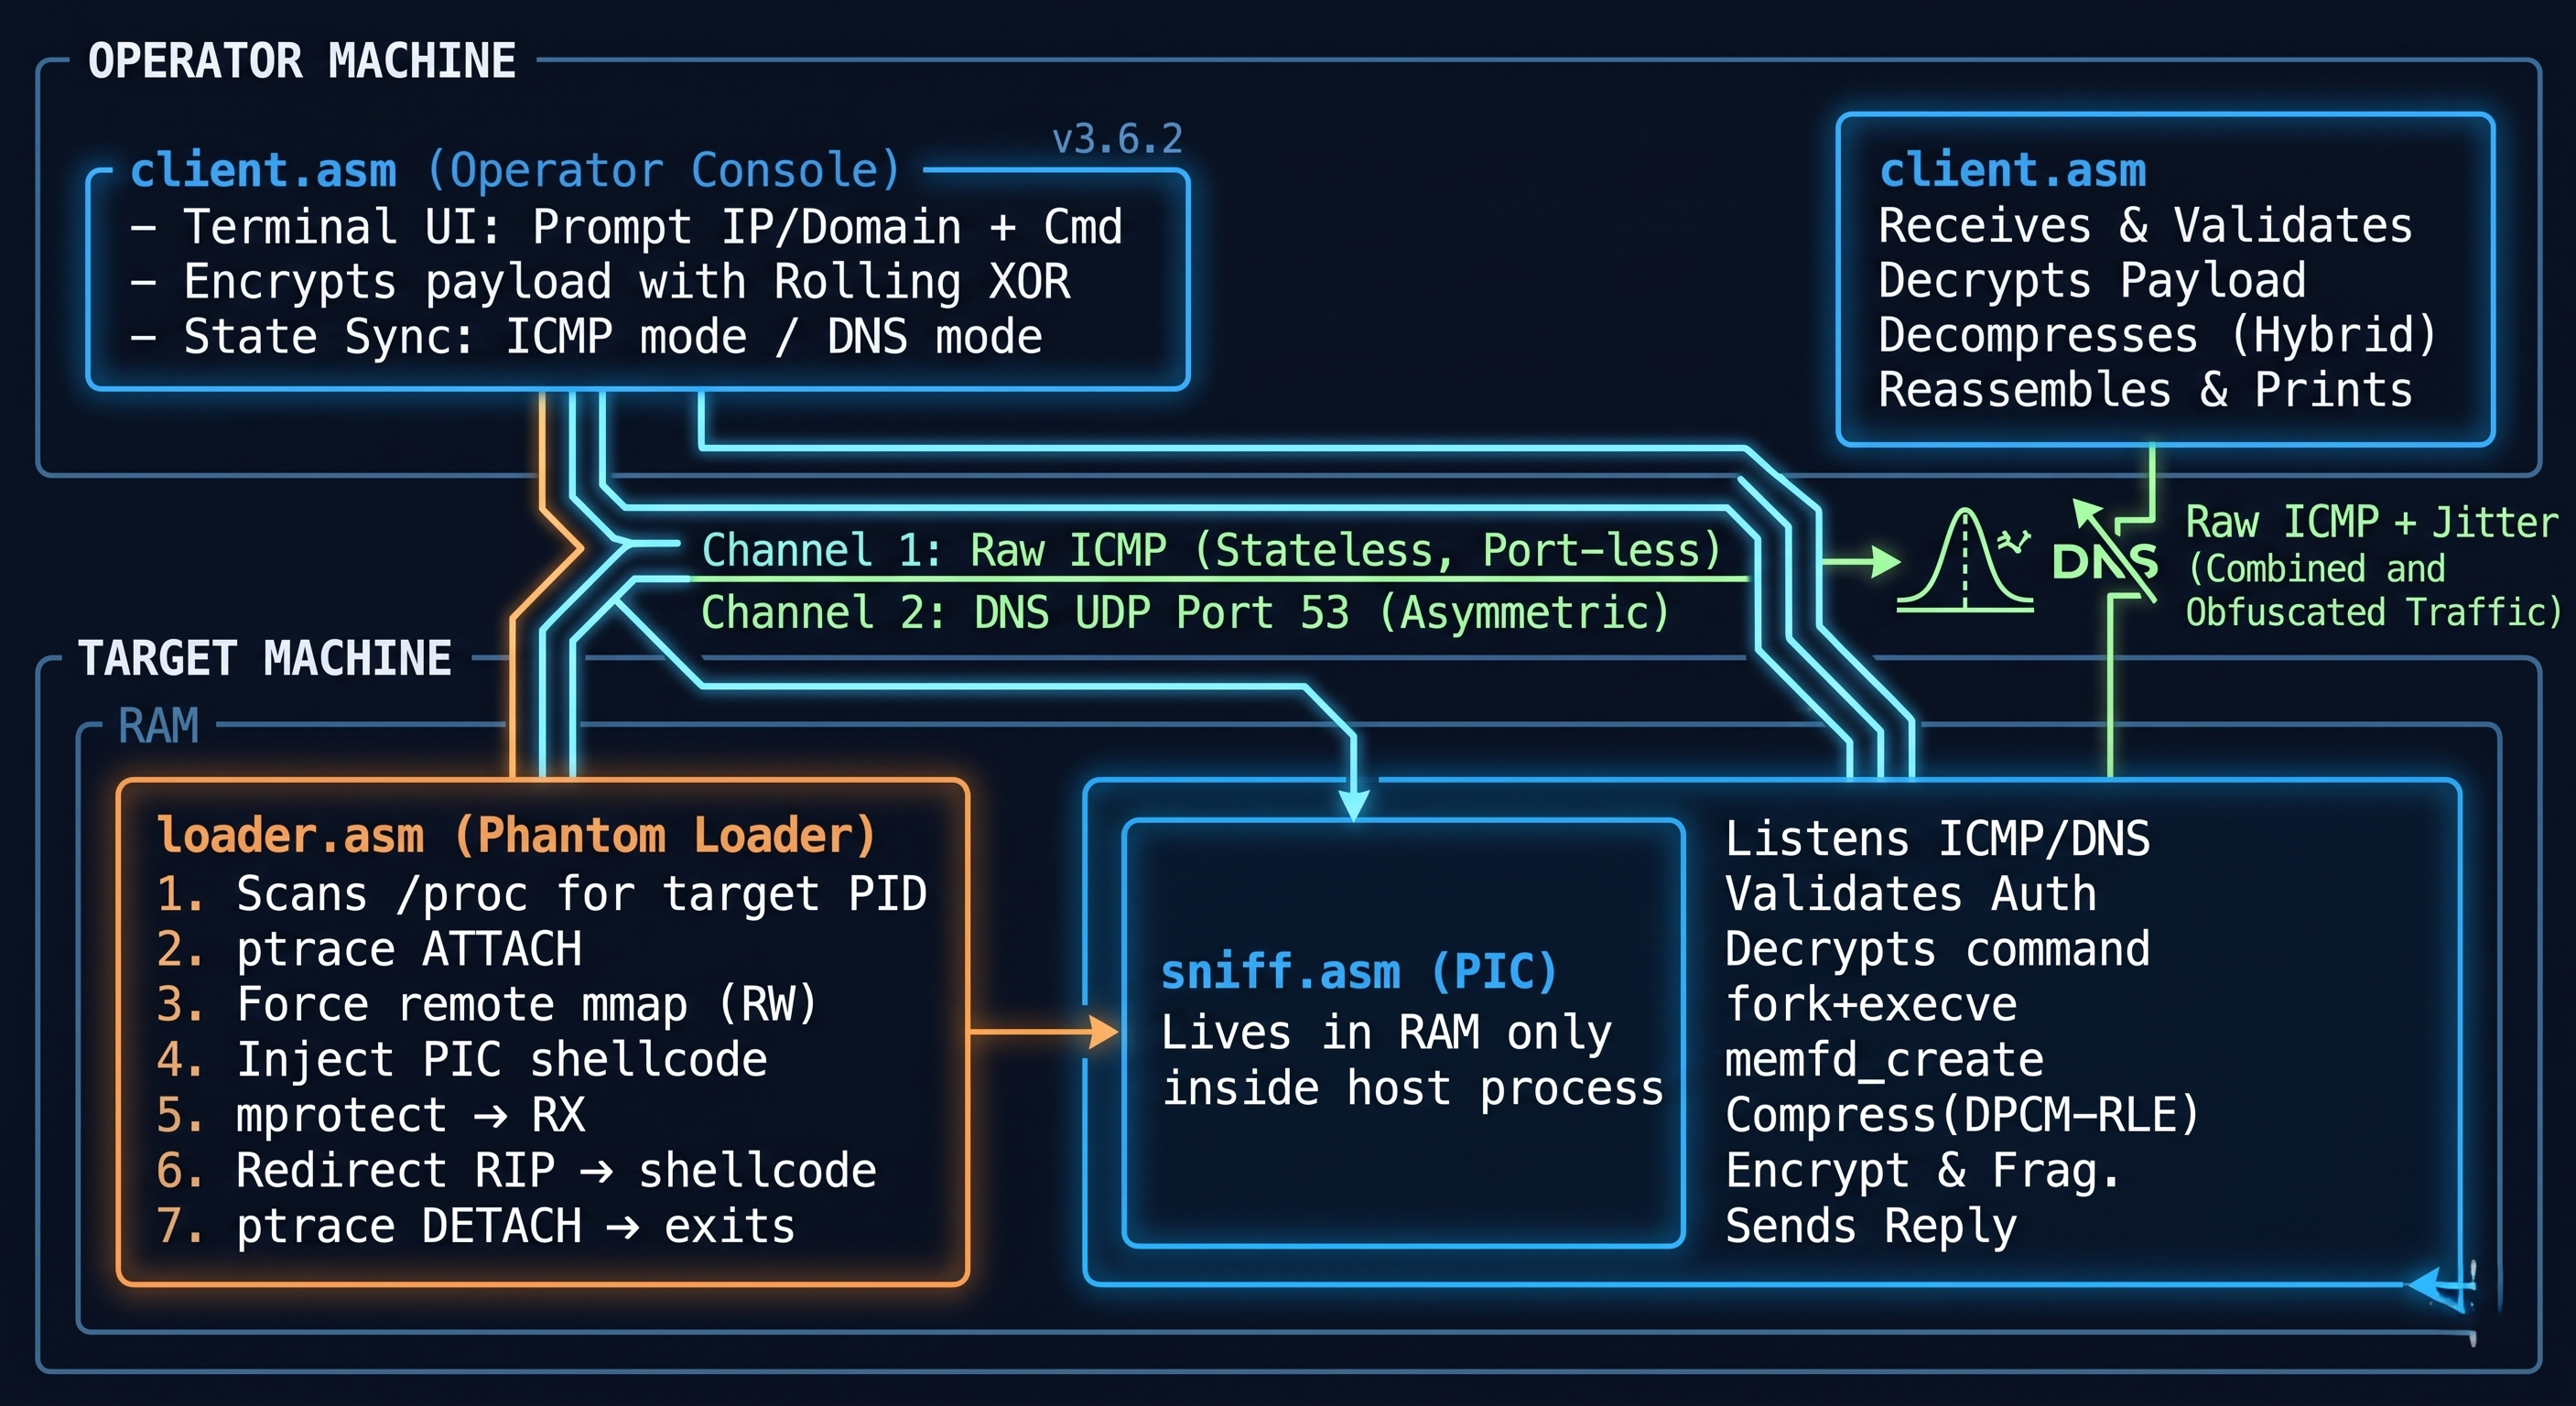
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…

Hands-on lab reproducing CVE-2025-22457: sets up Docker attacker/victim containers, finds stack addresses with GDB, and delivers a msfvenom reverse…

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)

Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…