AndroSH
 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
android-securitycontainer-securityeducation+6
248
ahmed-alnassif/androshAndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
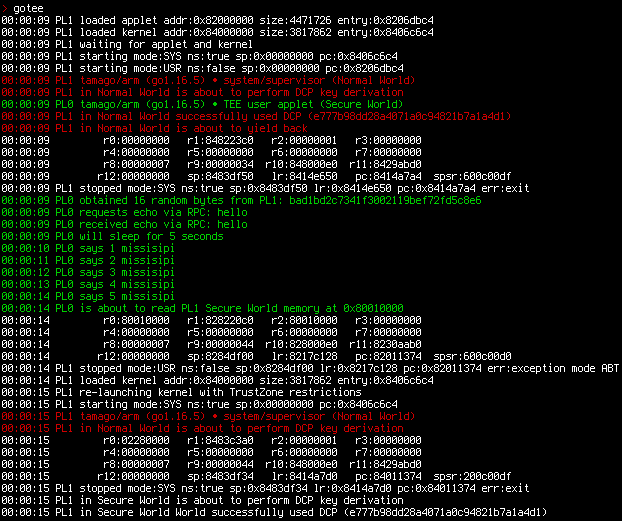 usbarmory/gotee
Go Trusted Execution Environment (TEE)
 0xballpoint/load
Lord Of Active Directory - automatic vulnerable active directory on AWS
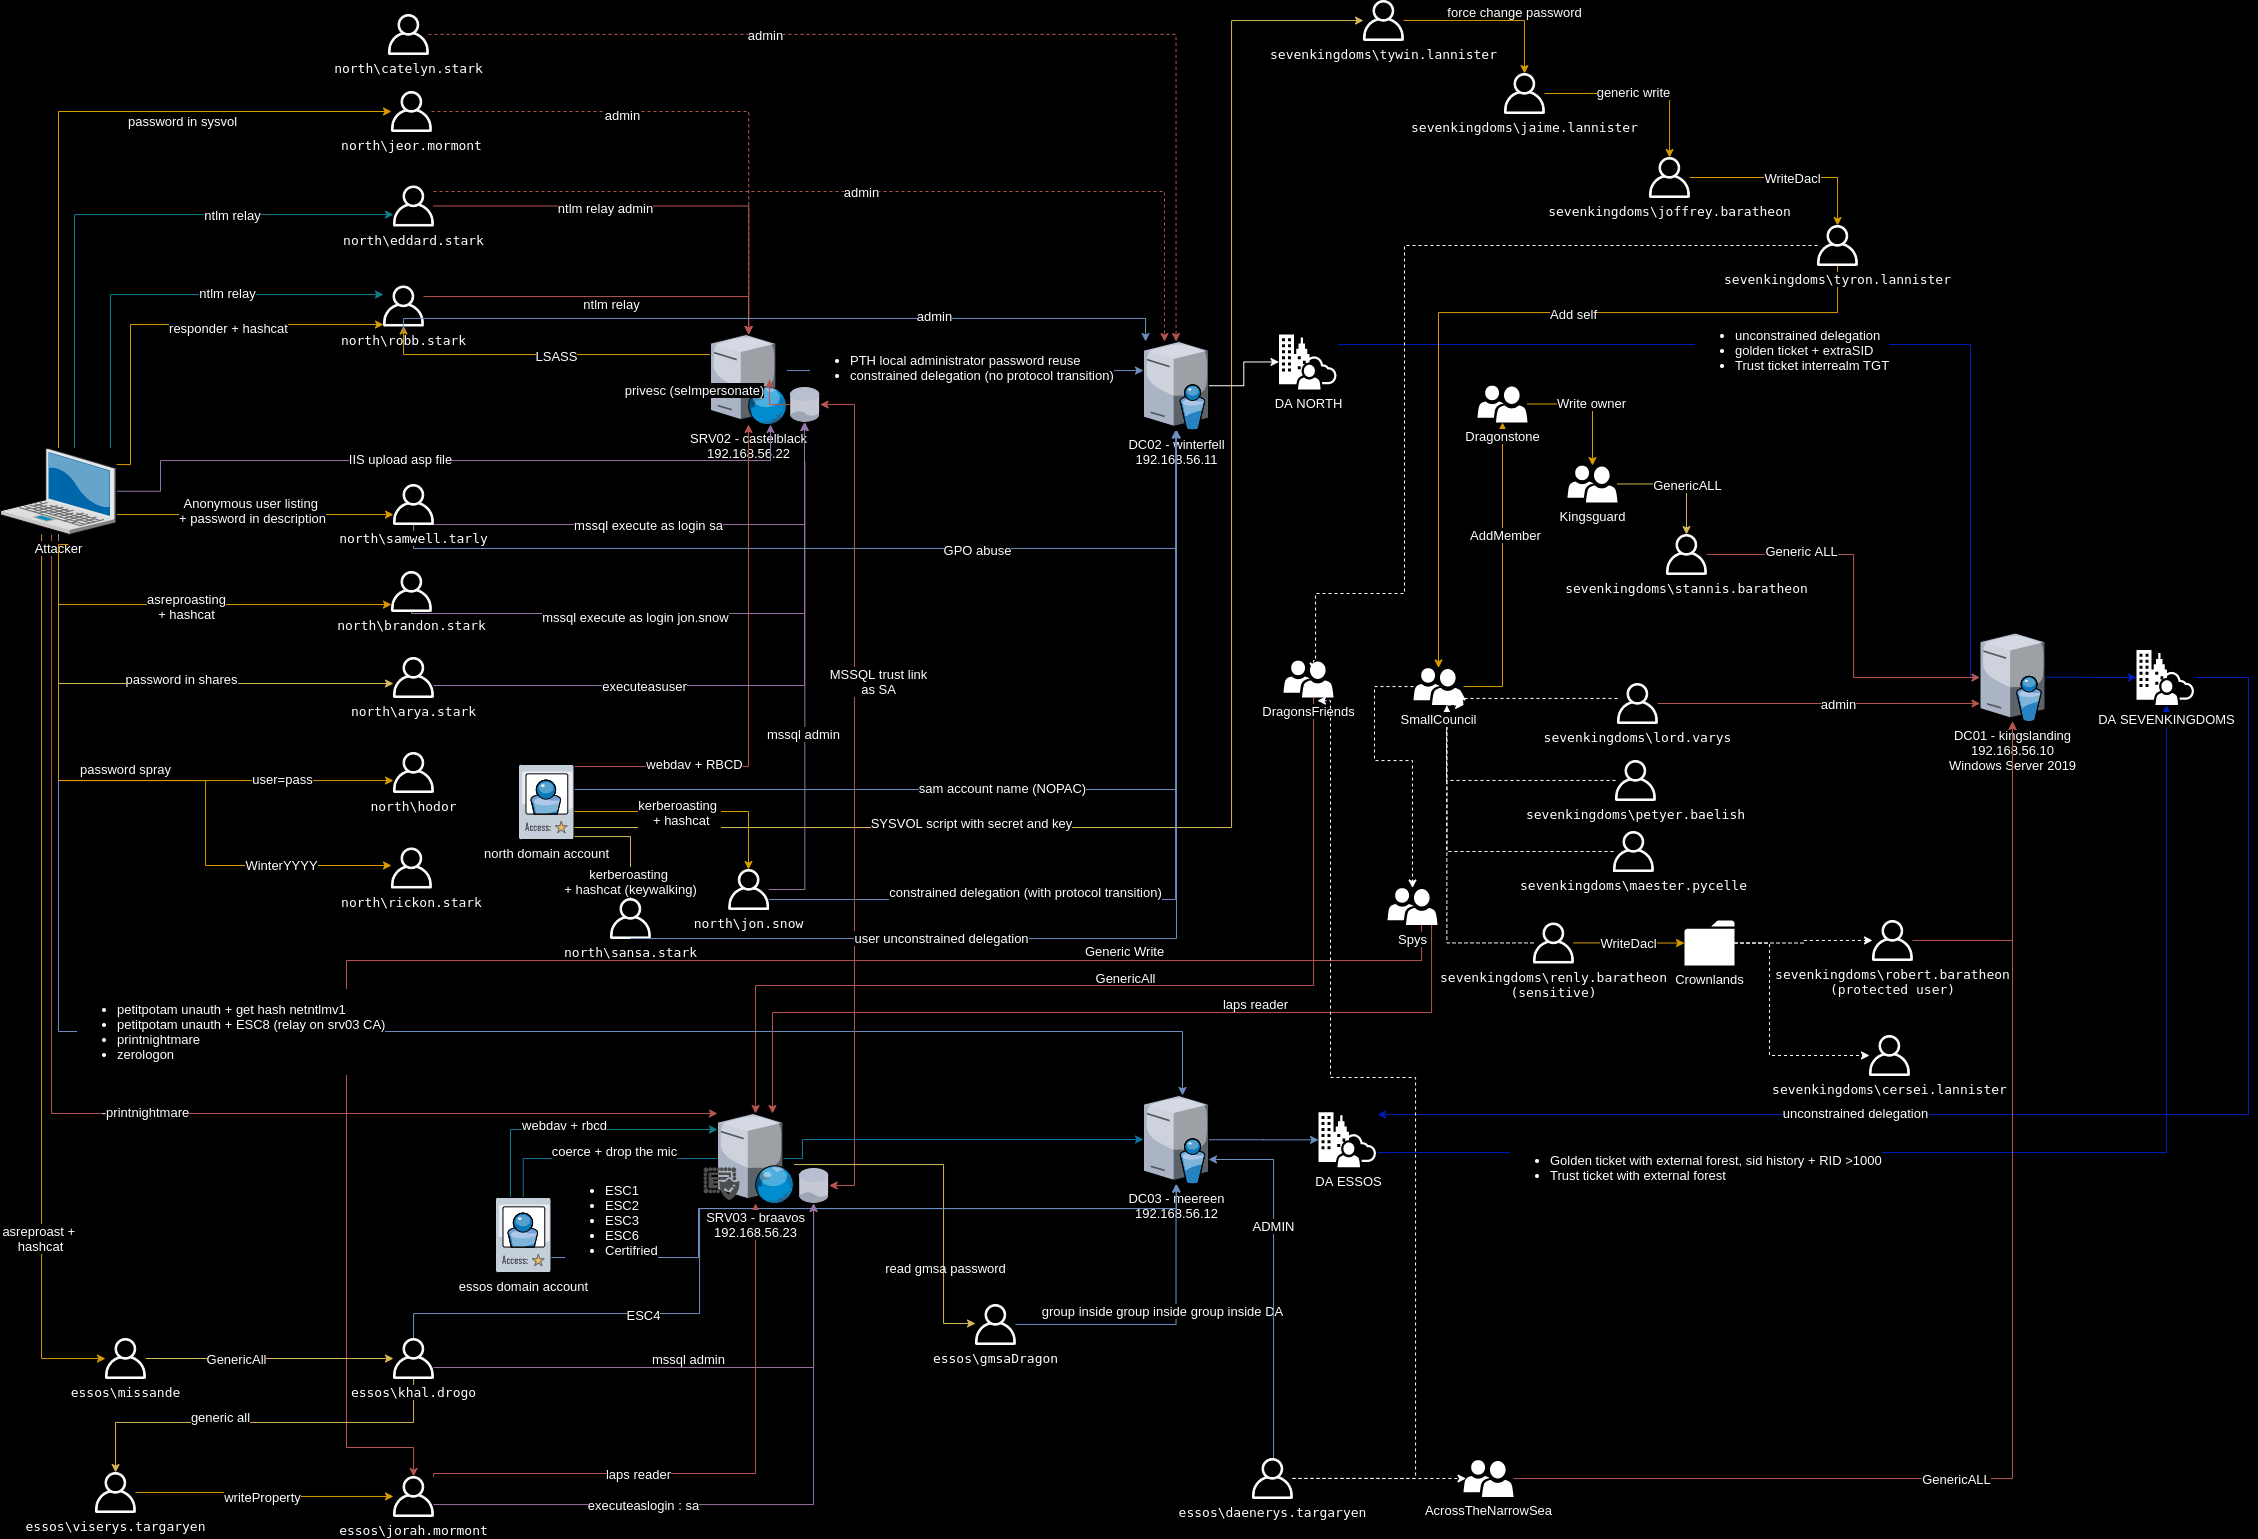 lkarlslund/deploy-goad
Script to install prerequisites for deploying GOAD on Ubuntu Linux 22.04
 synacktiv/mofos
Virtual machines manipulation framework
 armourbird/csf
ArmourBird CSF - Container Security Framework
 zephrfish/ludus-defender-lab
MDE/MDI Defender setup for Ludus
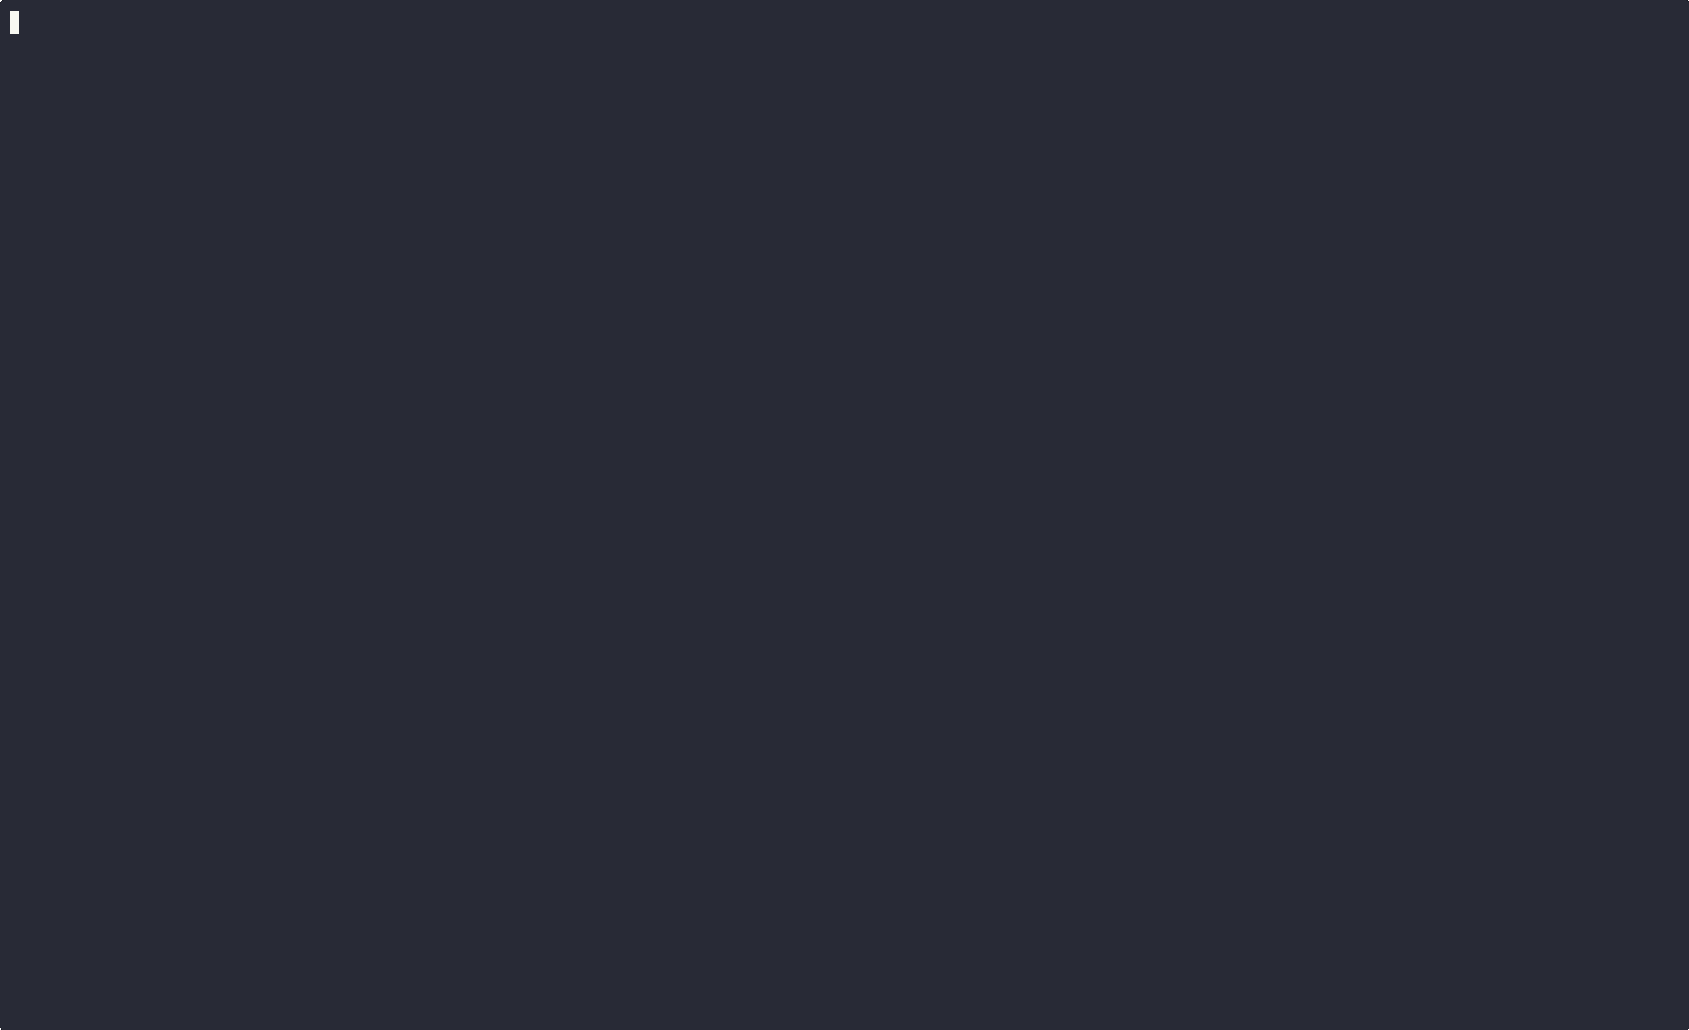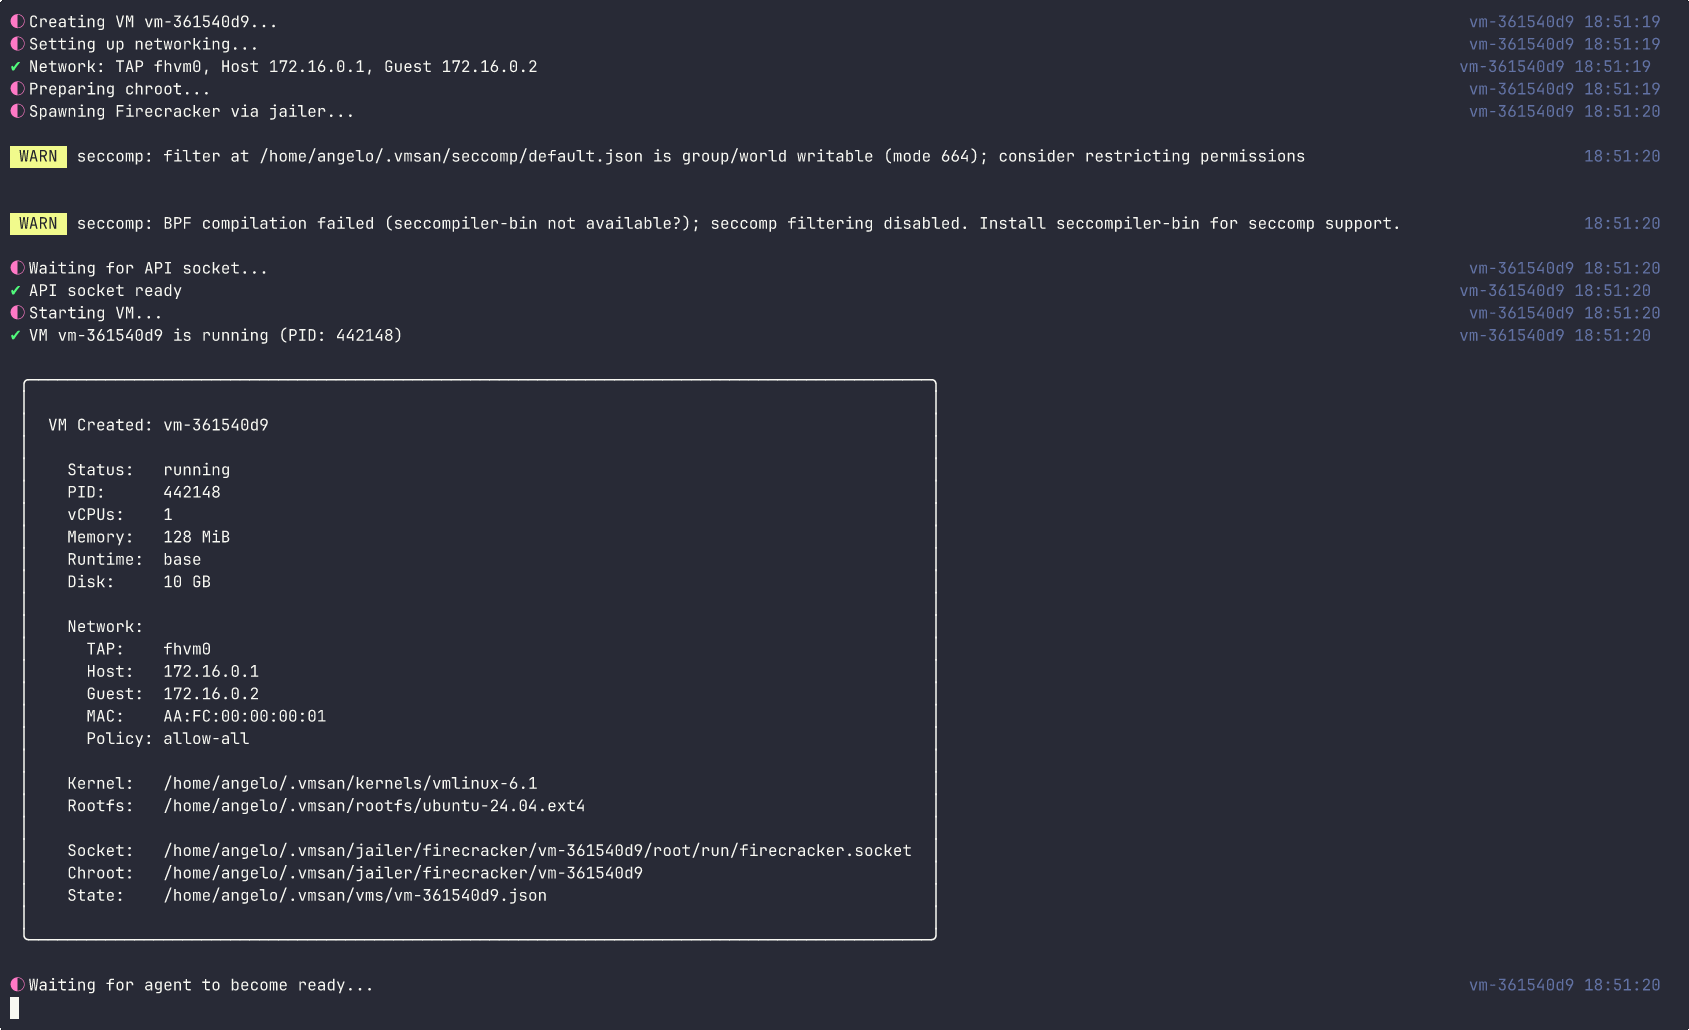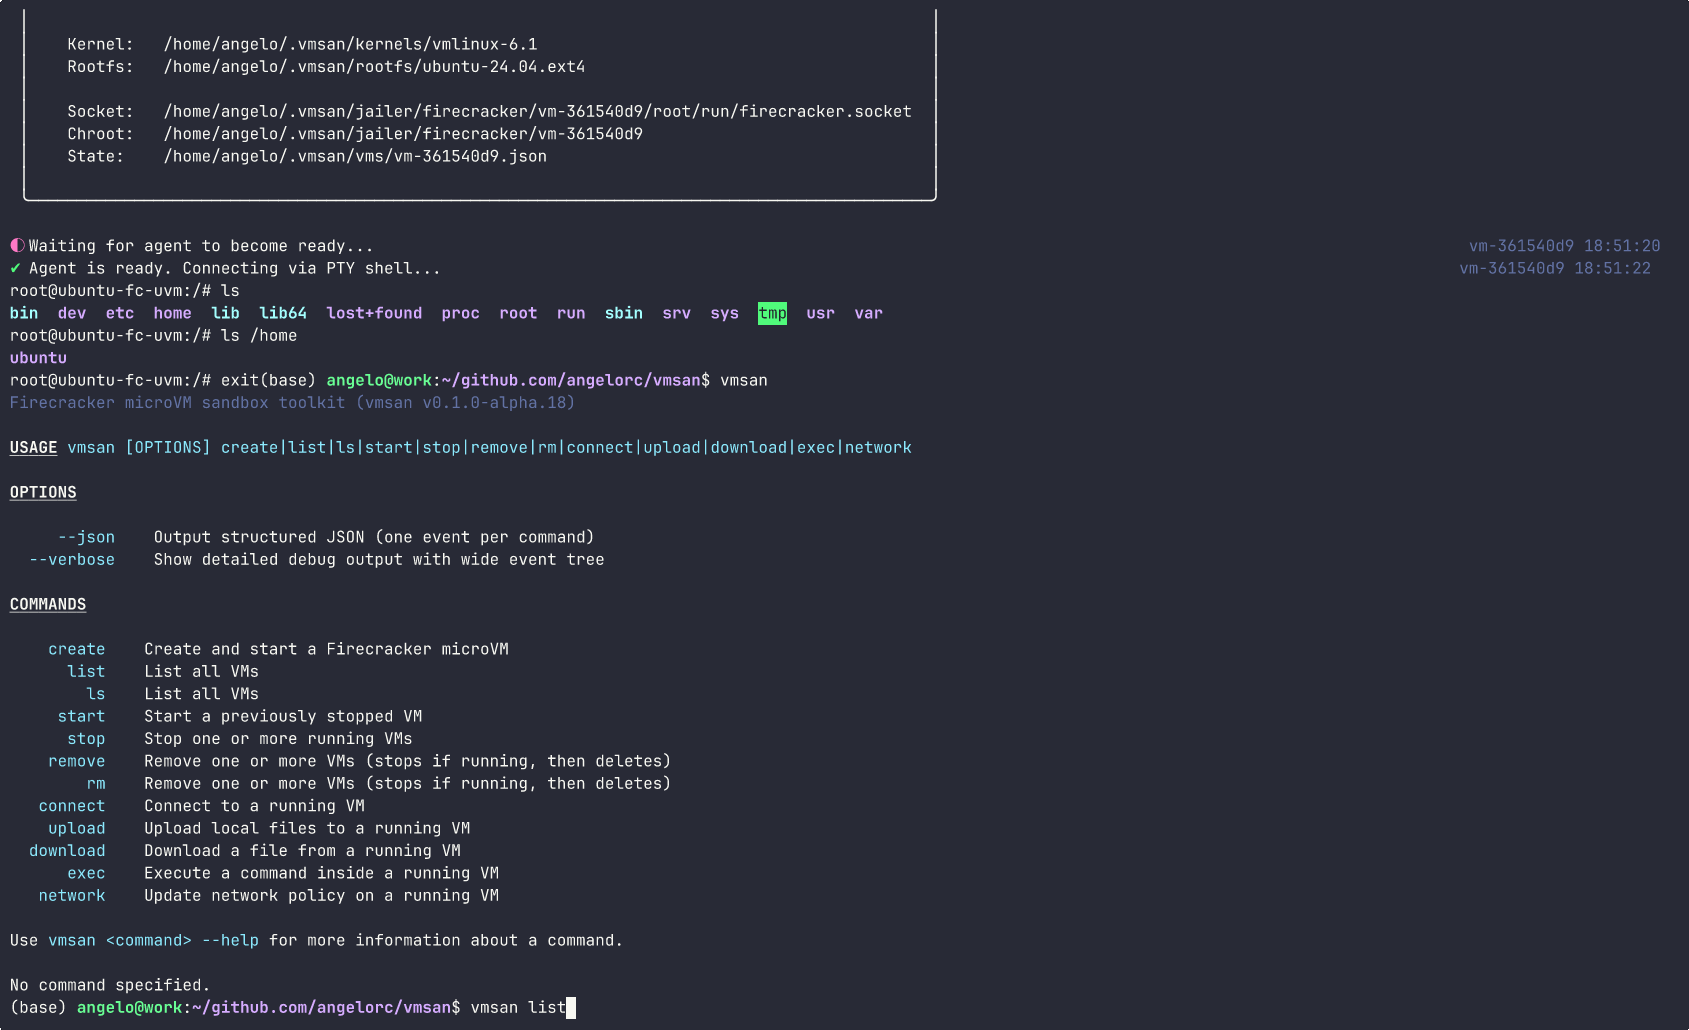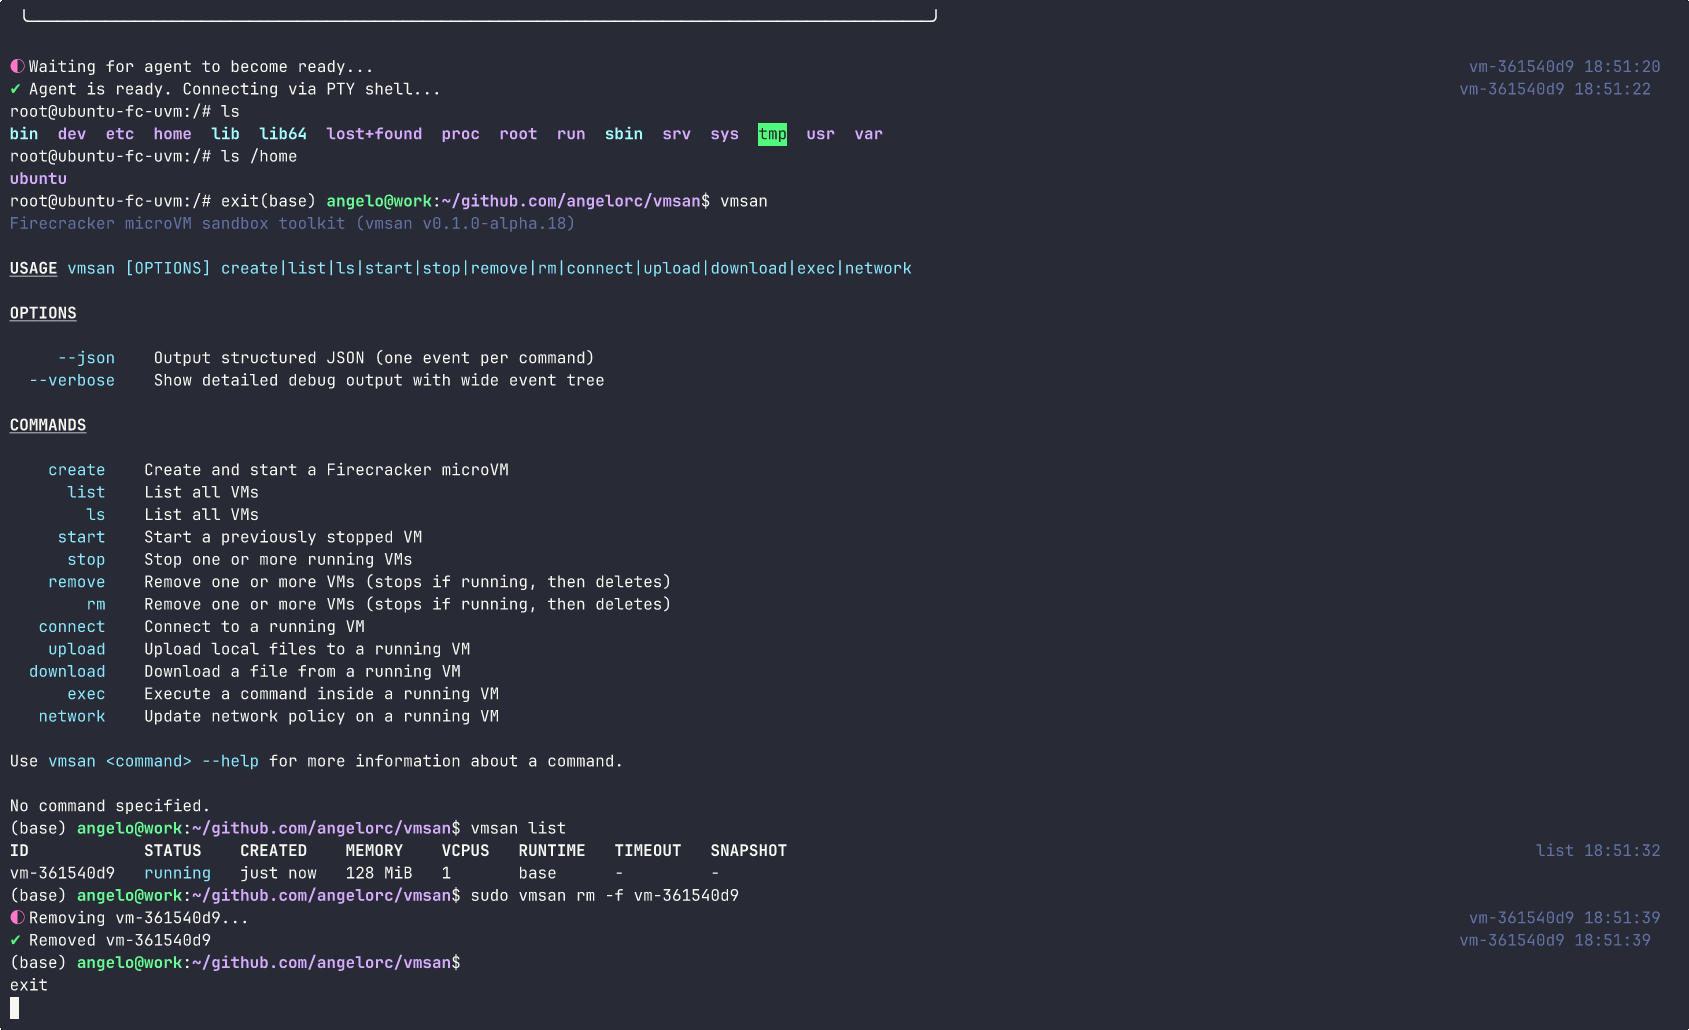 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 libriscv/libloong
The fastest LoongArch sandbox
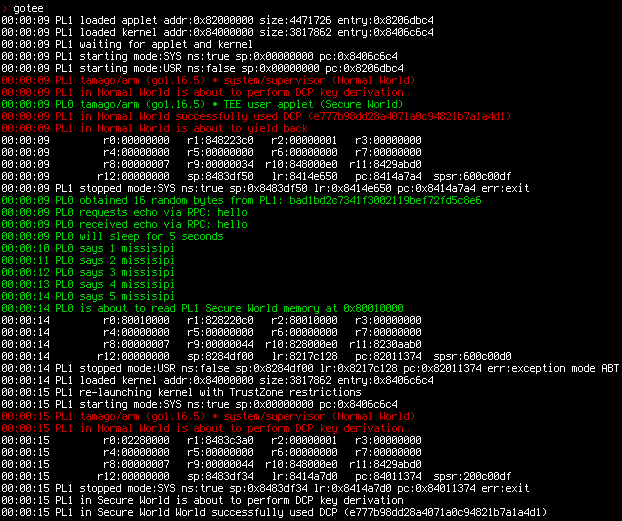 usbarmory/gotee-example
GoTEE - example application
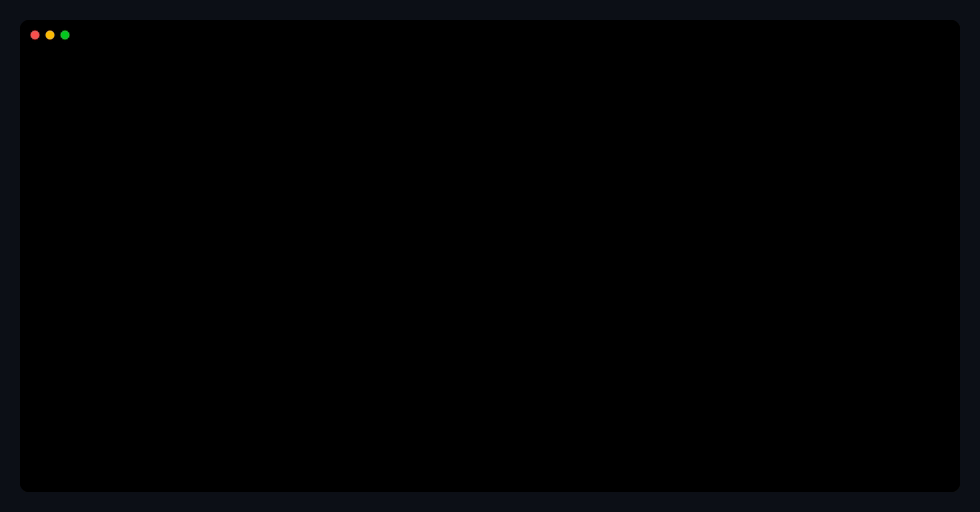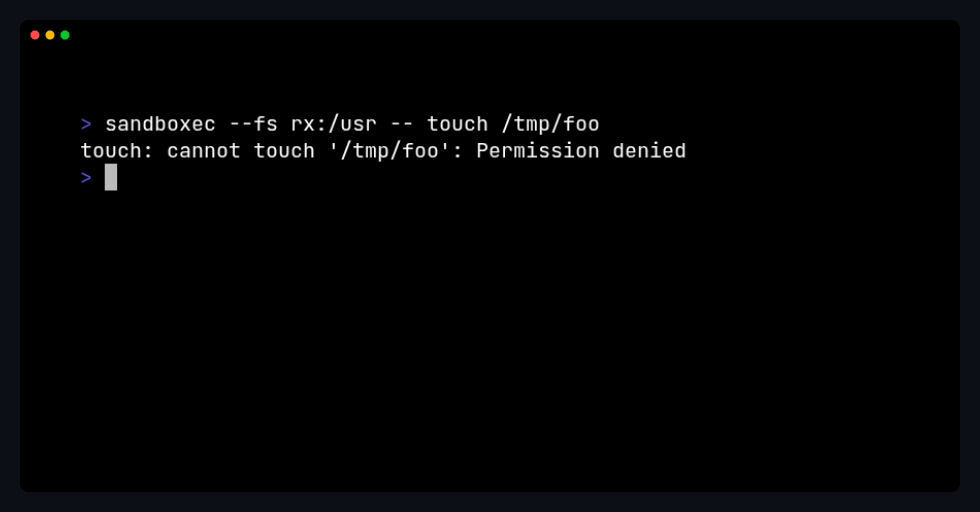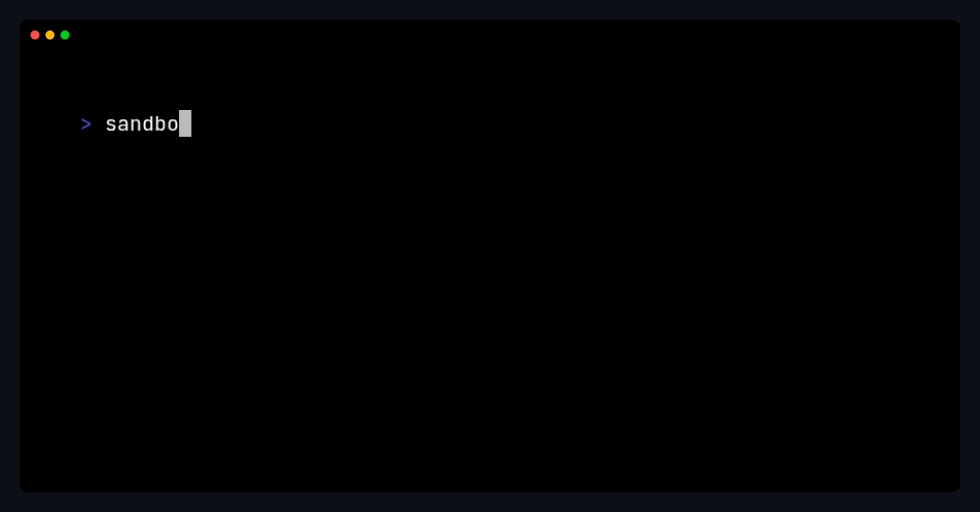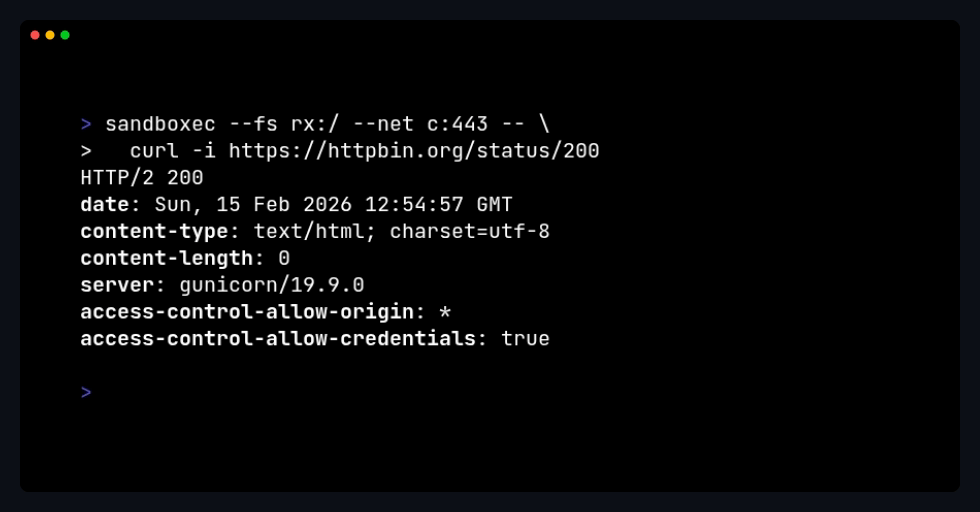 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
 aarif450/aarif450.github.io
Exploit KVM/x86 guest-to-host escape CVE-2026-64561 with Zapscape, a proof-of-concept demonstrating hypervisor vulnerability.
 vatson112/deny-af-alg-bpf
eBPF LSM program that blocks AF_ALG socket creation to mitigate CVE-2026-31431, with userspace daemon logging denied attempts via ring buffer.
 siyad01/agentbox
Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.
 trungnguyen1909/qemu-t8030
iPhone 11 emulated on QEMU