
keyhacks
 streaak/keyhacks
Curated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…
api-securitypenetration-testingsecret-detection+1
streaak/keyhacksCurated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…
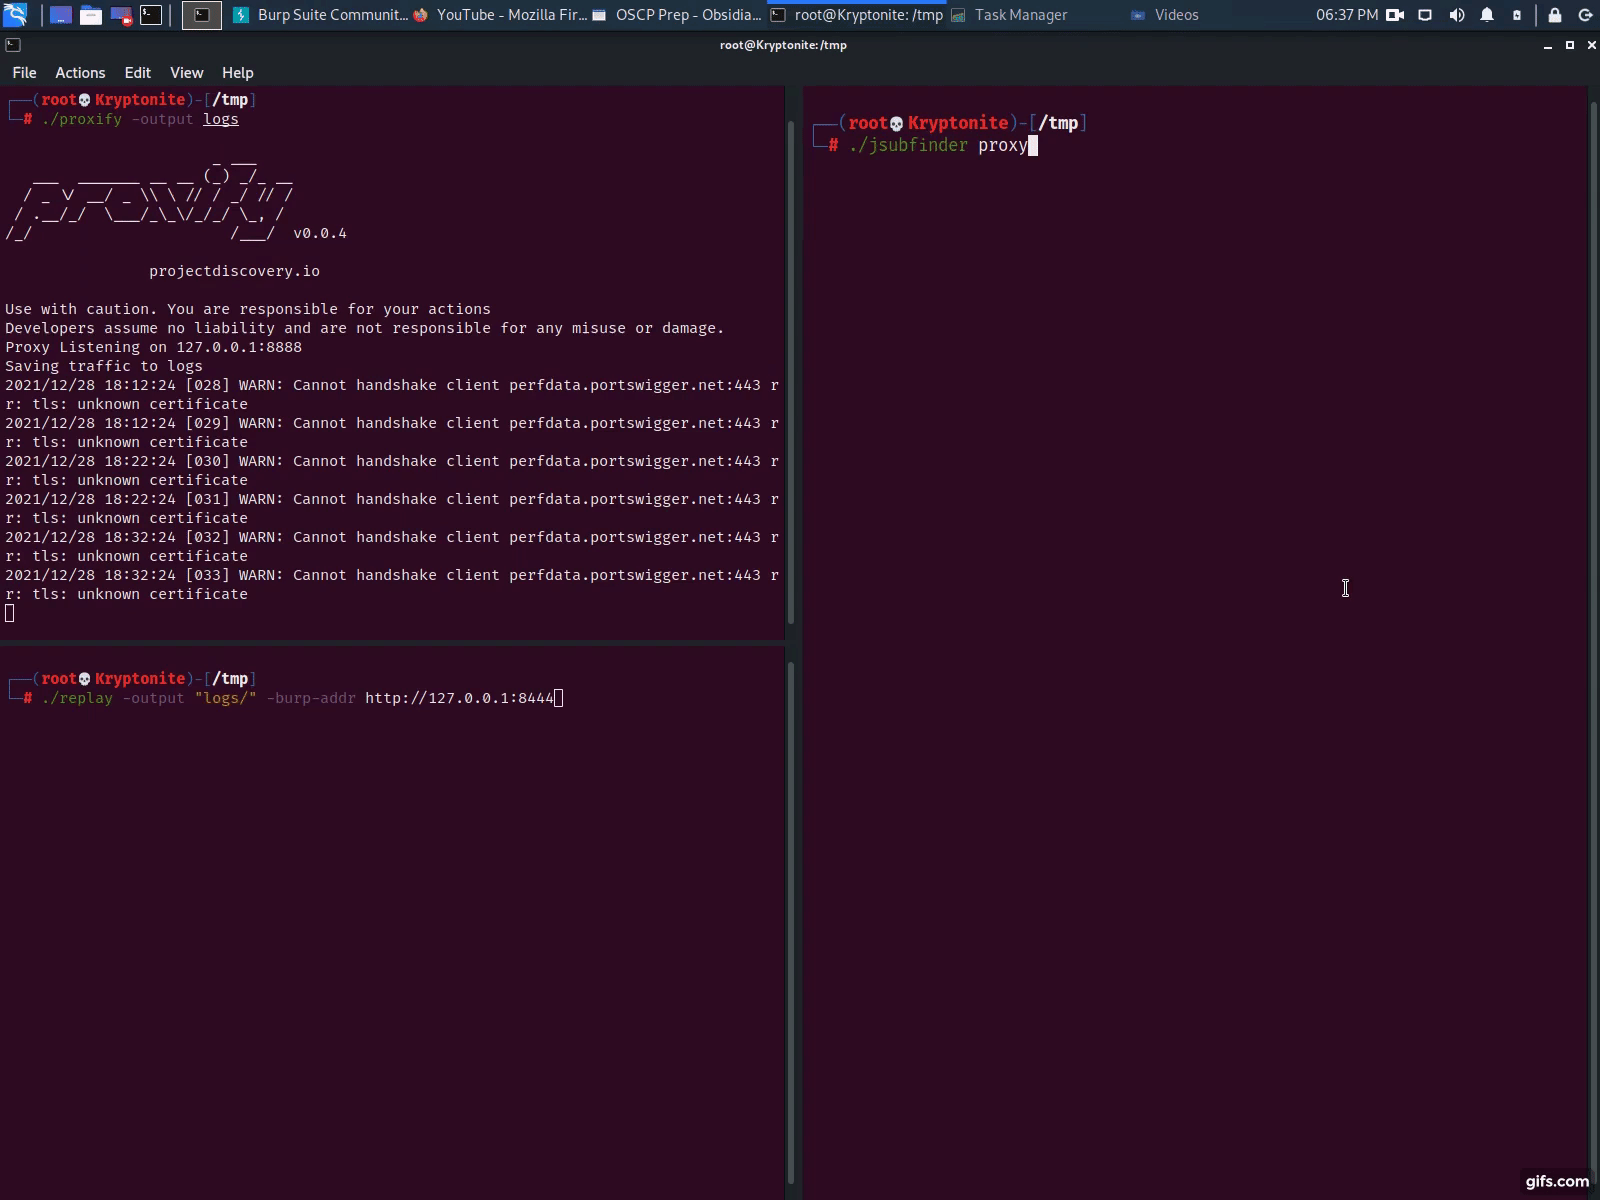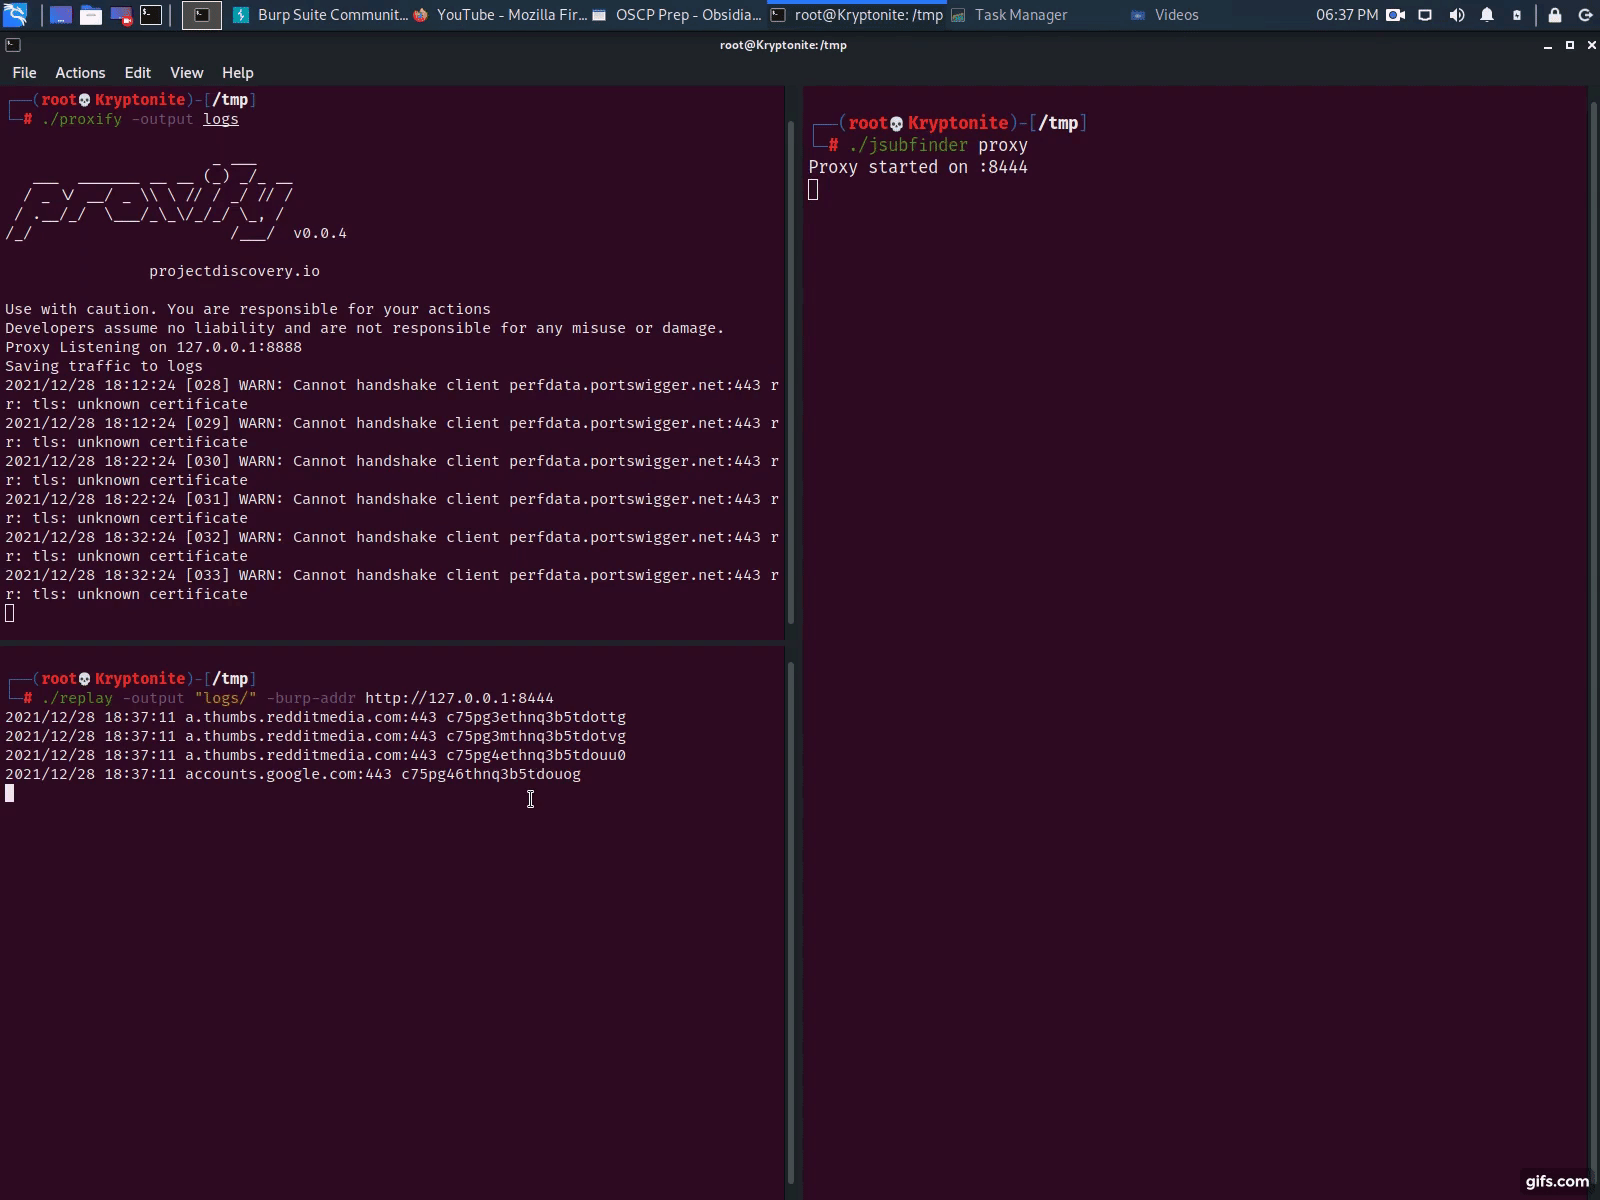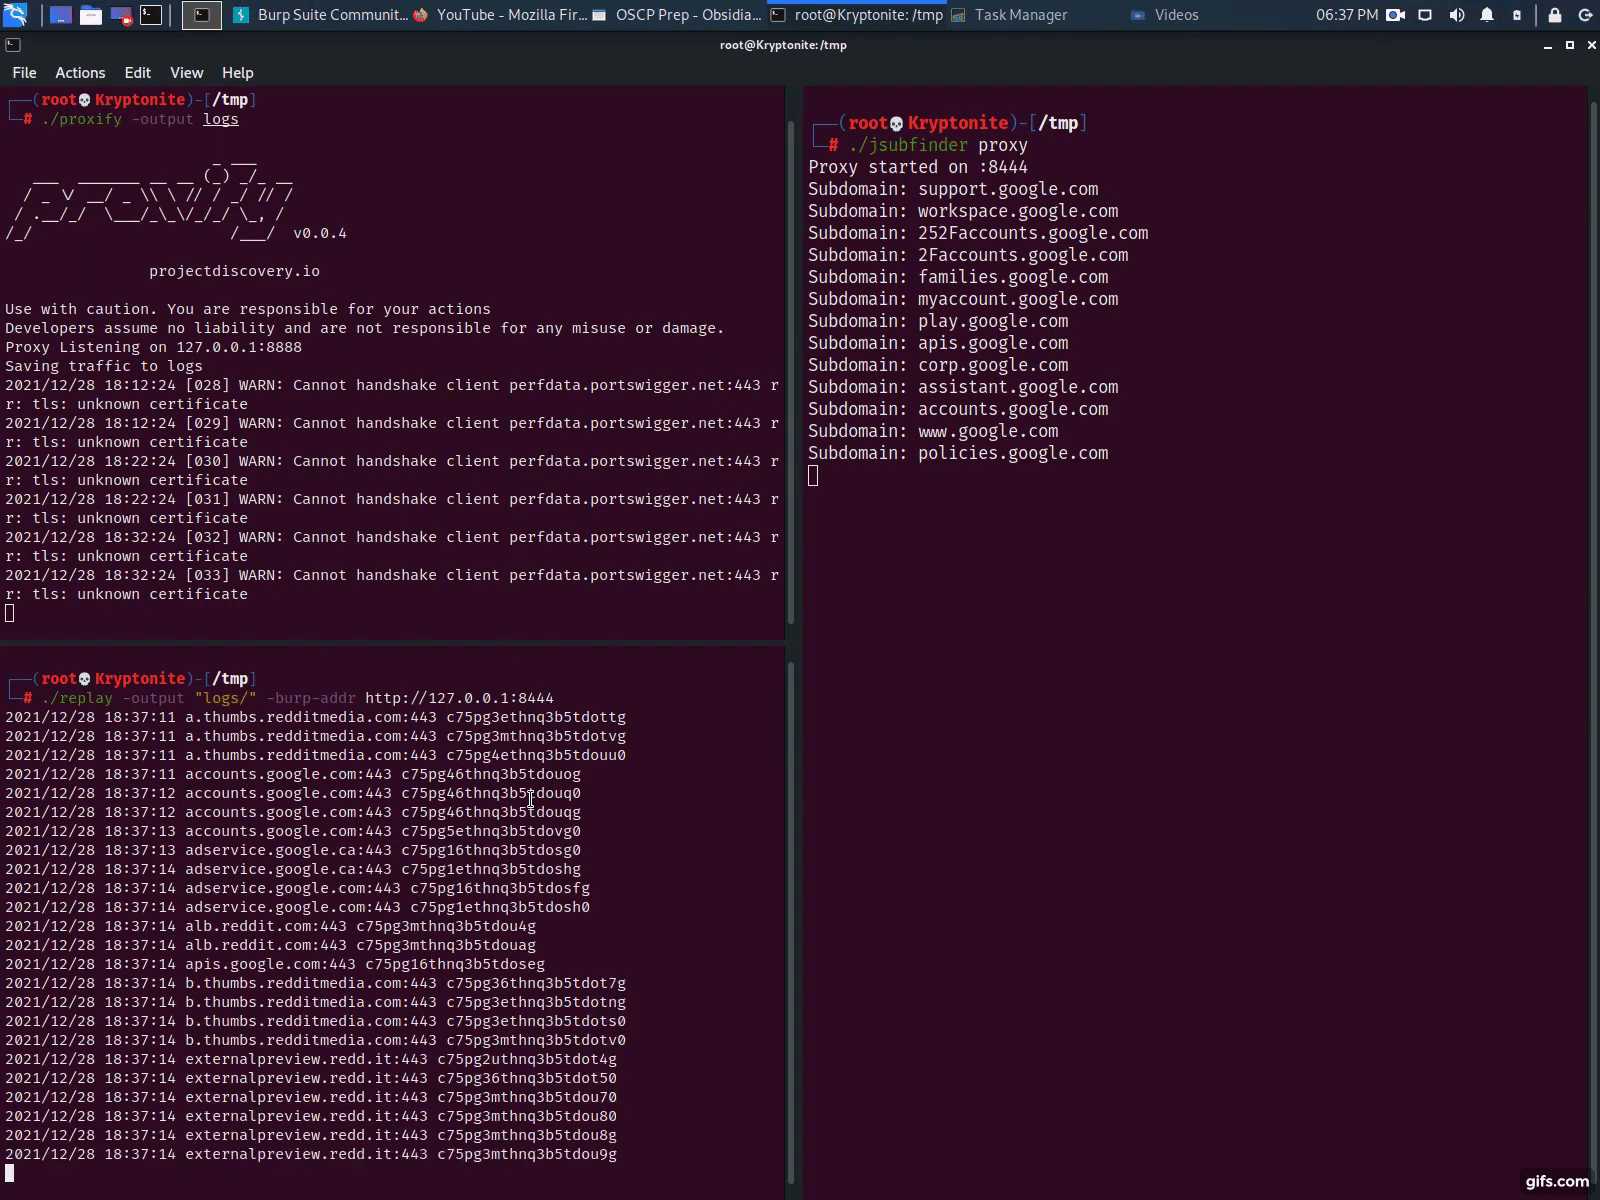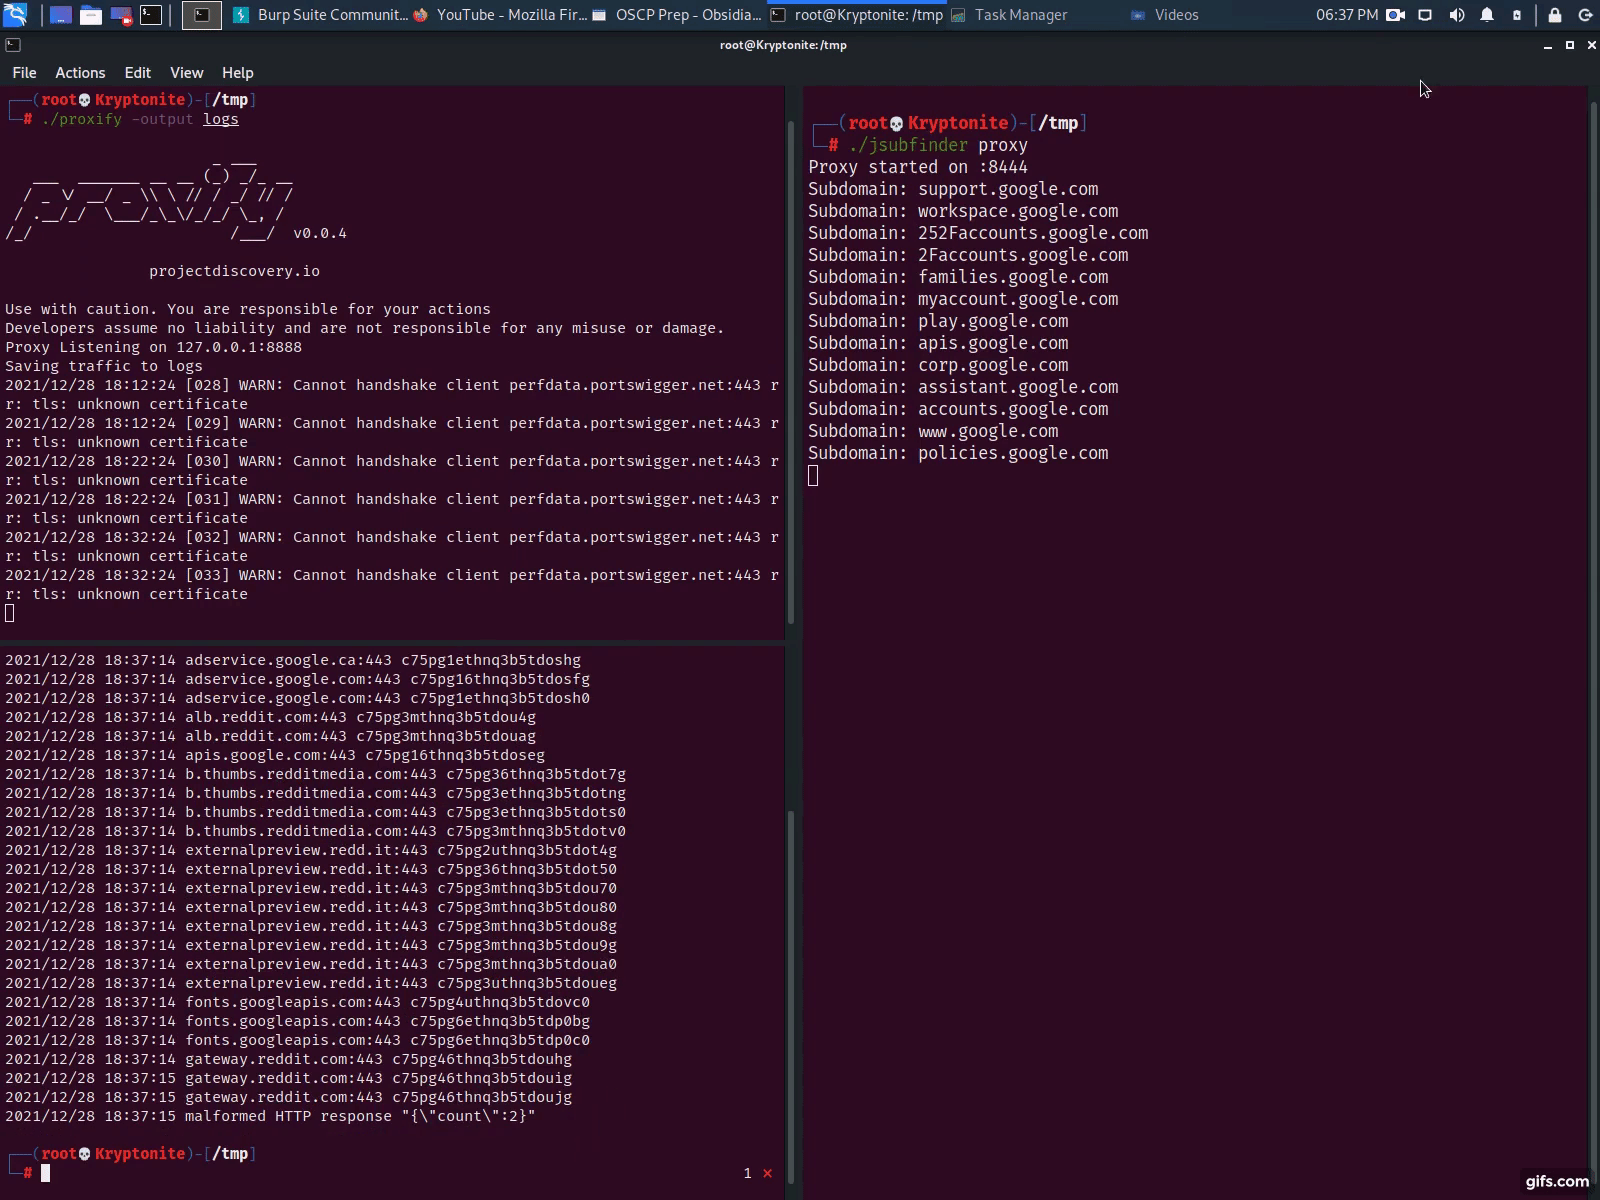 threatunknown/jsubfinder
Go-based tool that scans webpages and JavaScript files to discover hidden subdomains and secrets, with optional crawling and real-time proxy analysis…
 ustayready/golddigger
Recursively searches files for sensitive information using customizable regex patterns, designed for penetration testers to rapidly discover secrets…
 r3curs1v3-pr0xy/vajra
Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
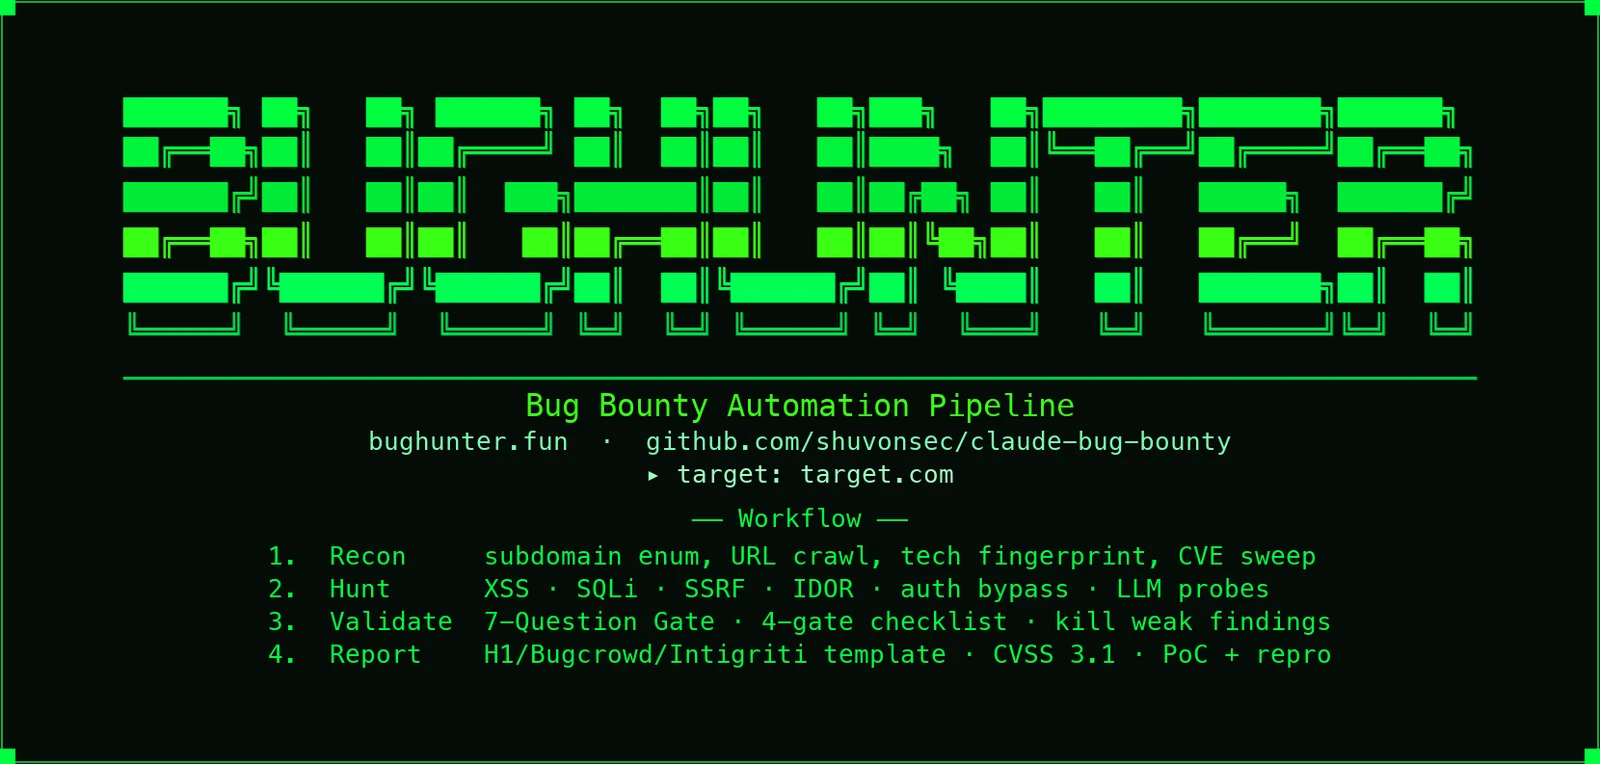 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 dwisiswant0/apkleaks
Scanning APK file for URIs, endpoints & secrets.
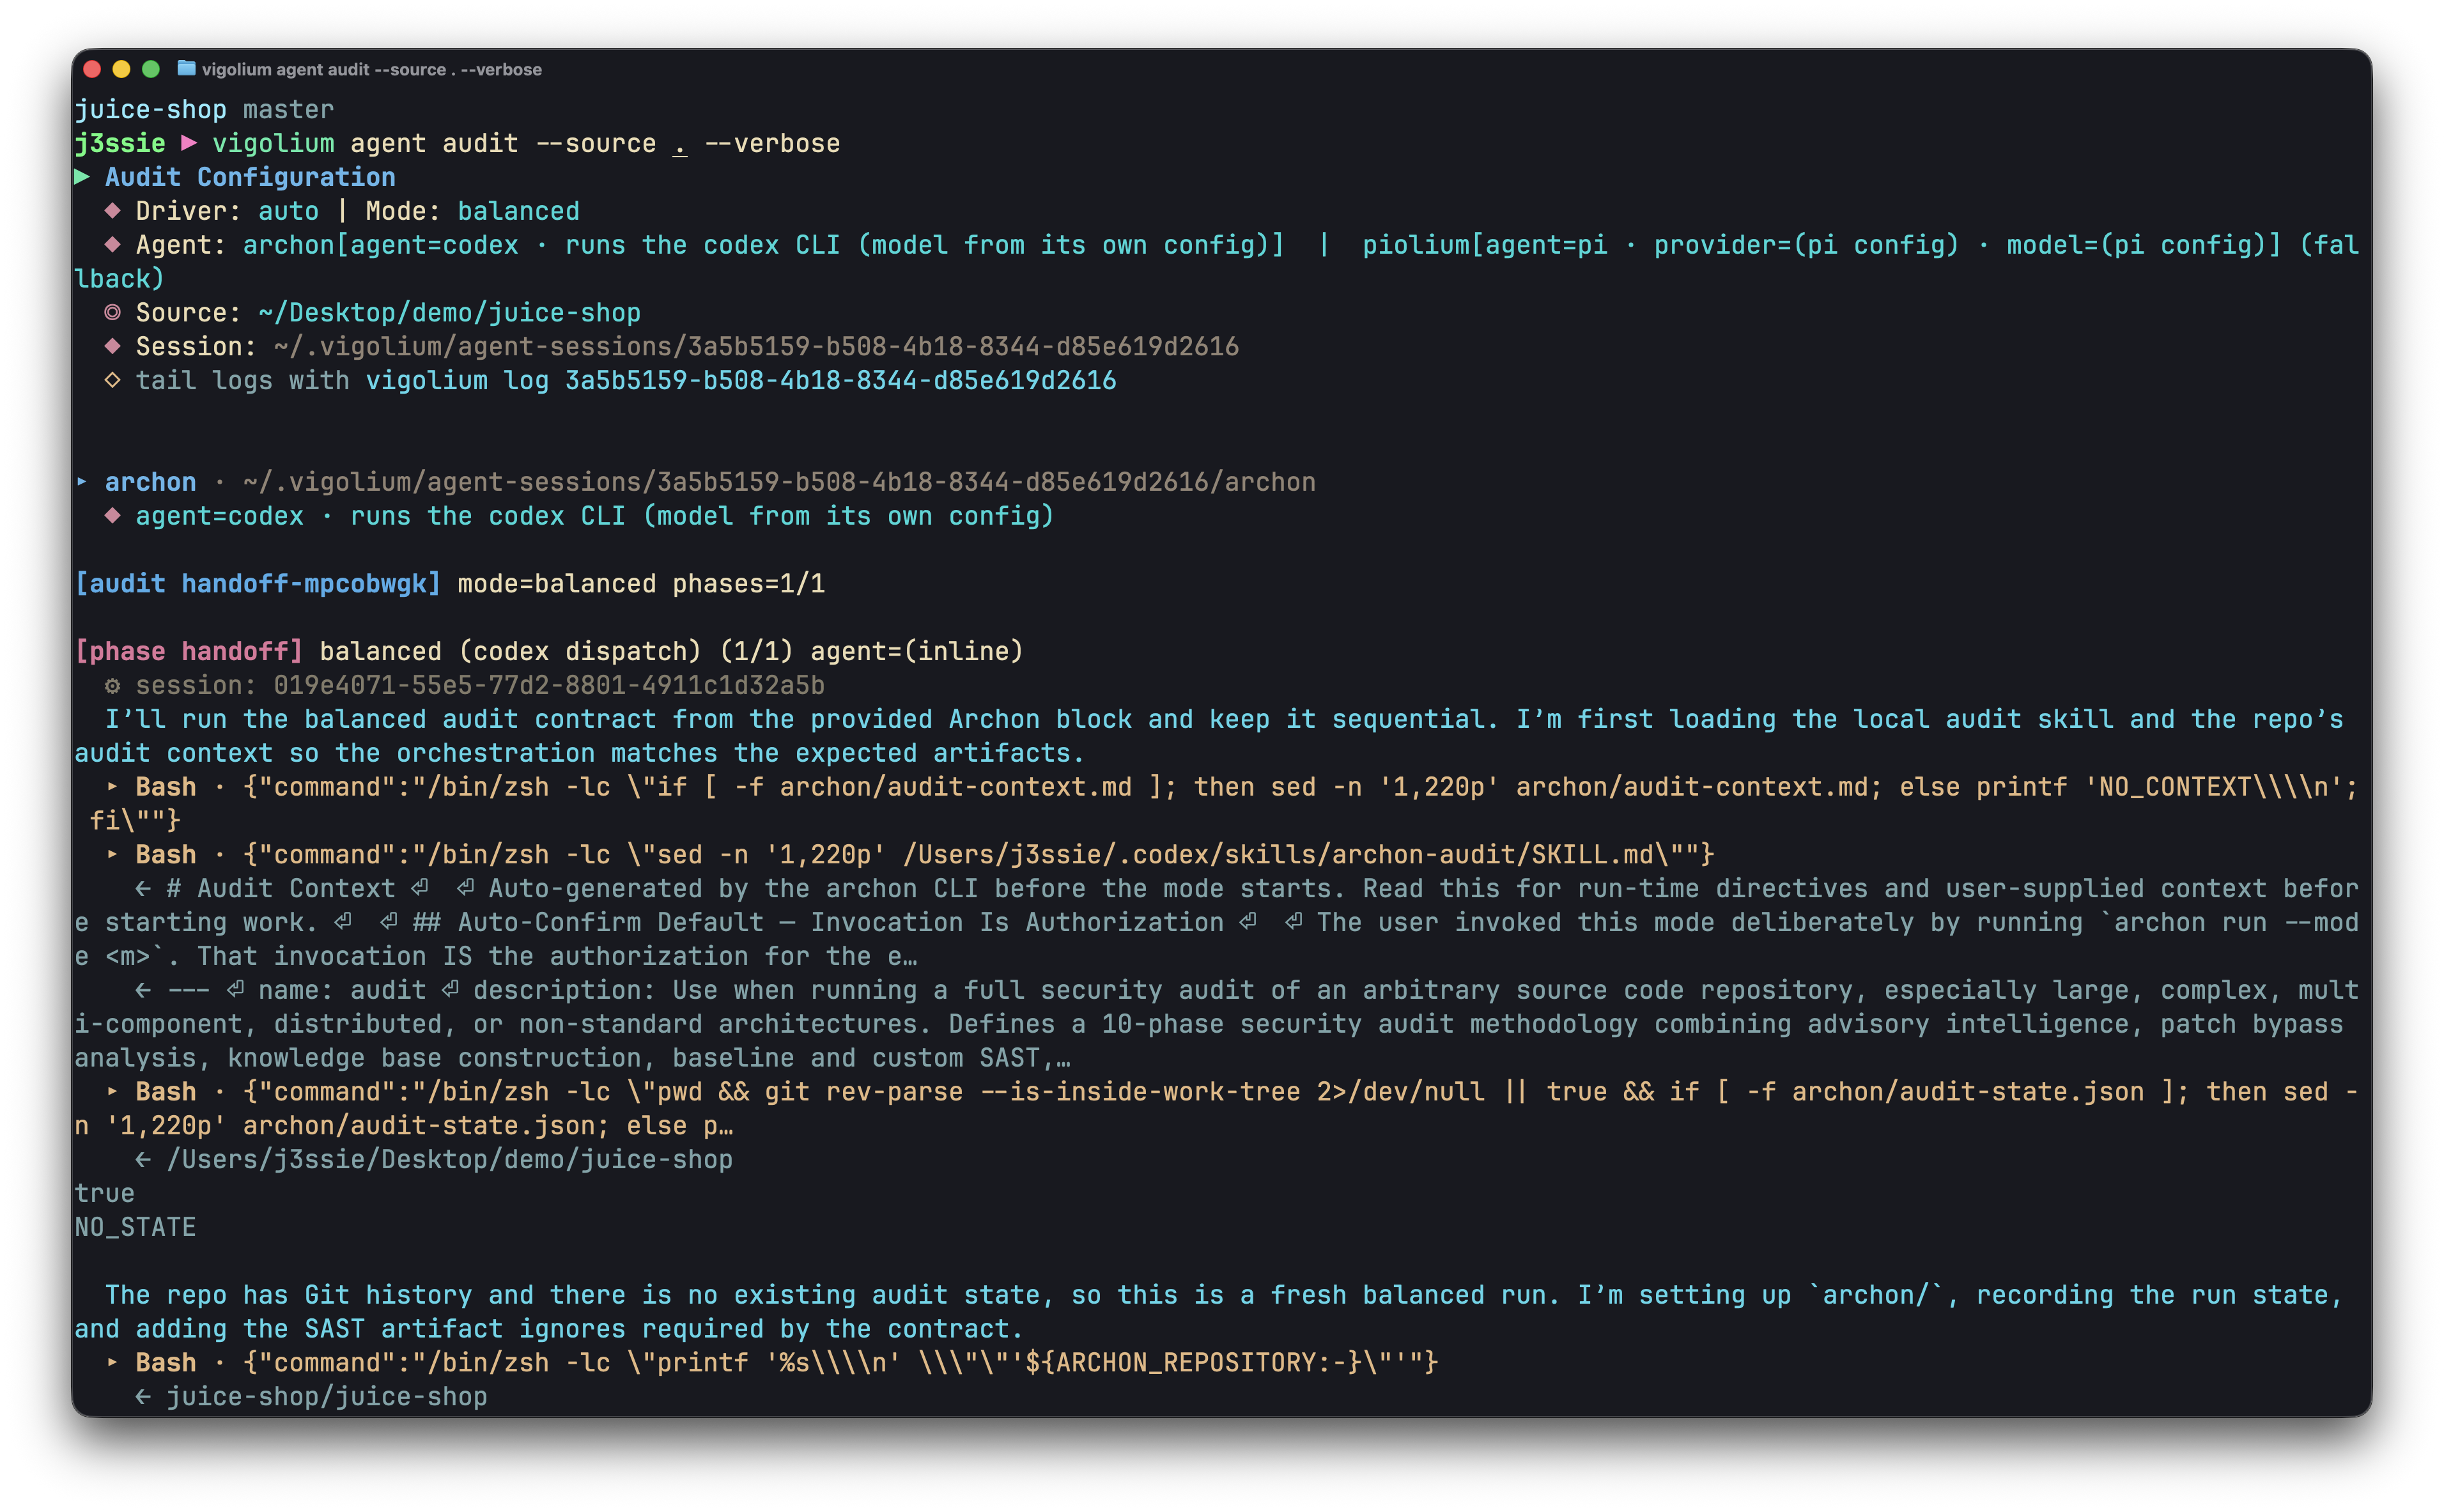 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
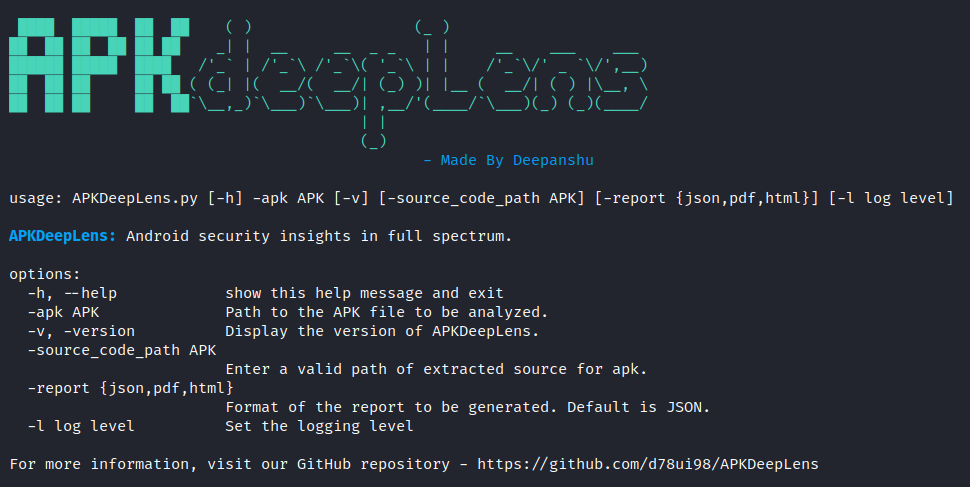 d78ui98/apkdeeplens
Android security insights in full spectrum.
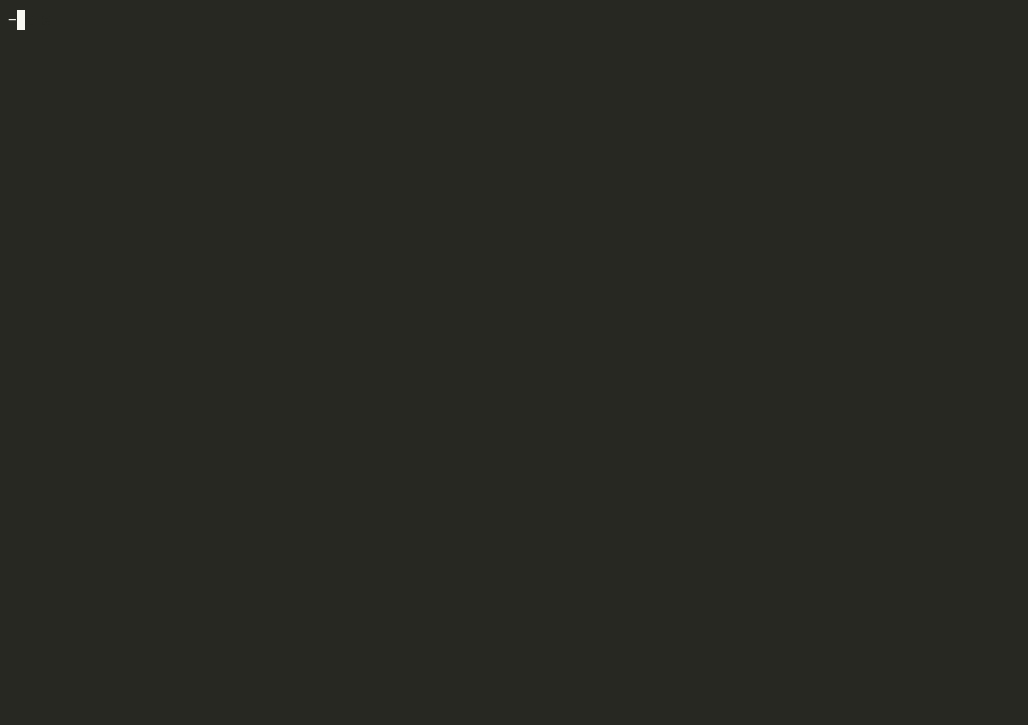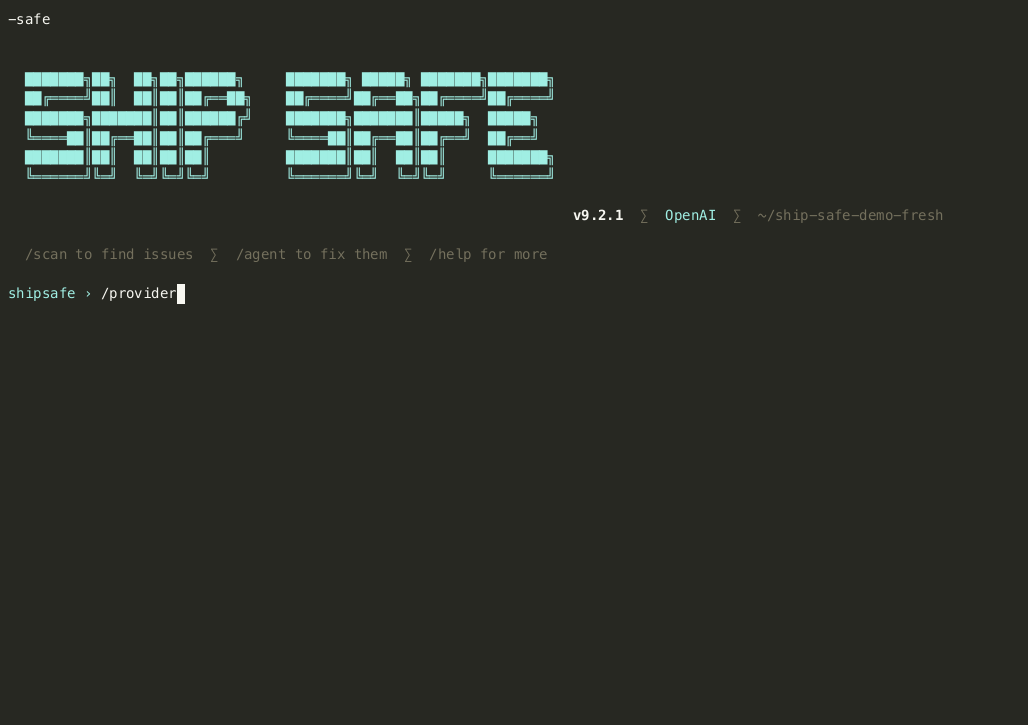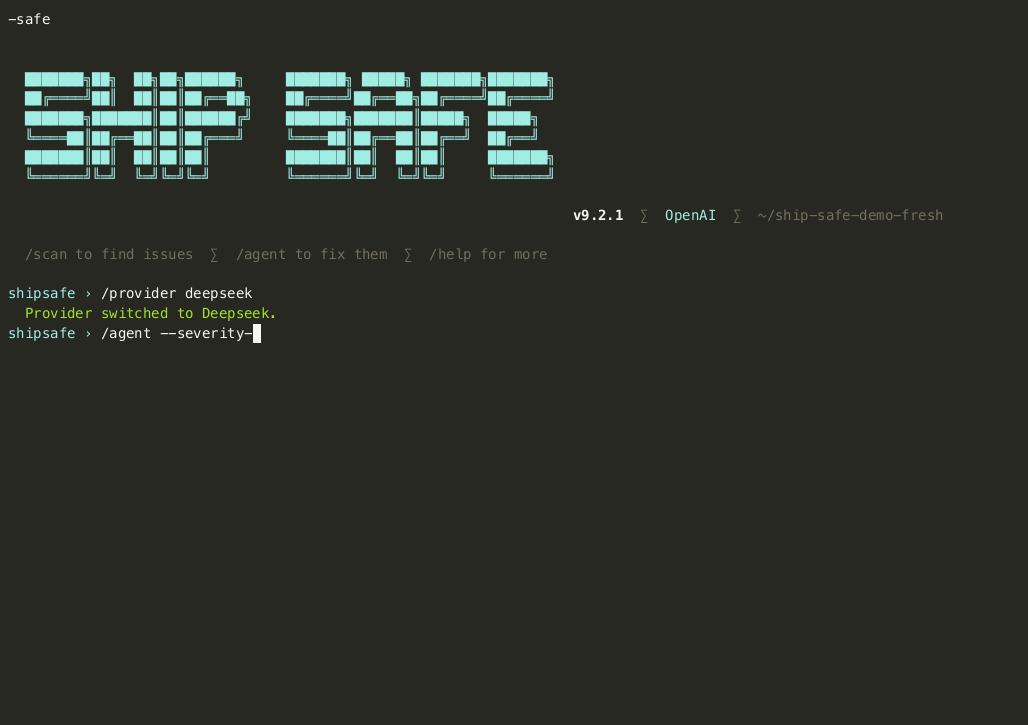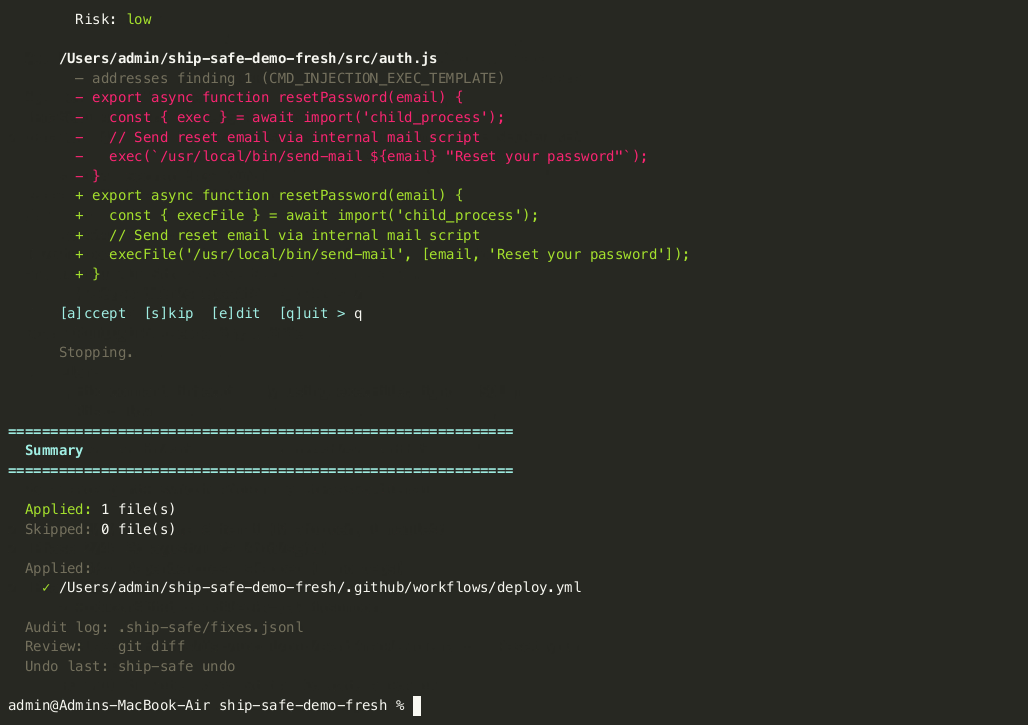 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
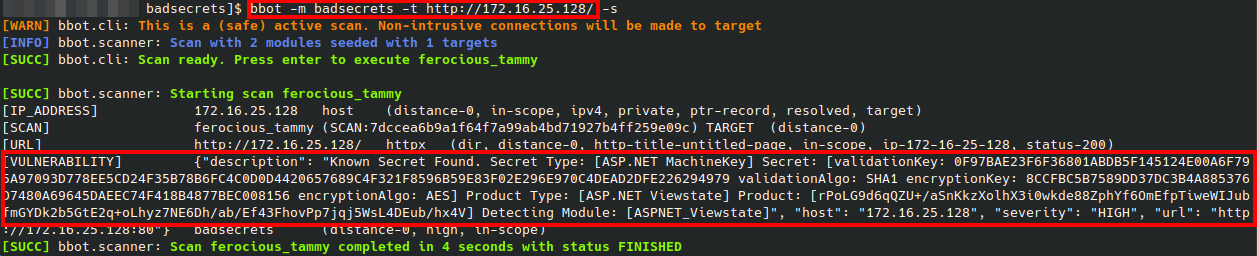 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
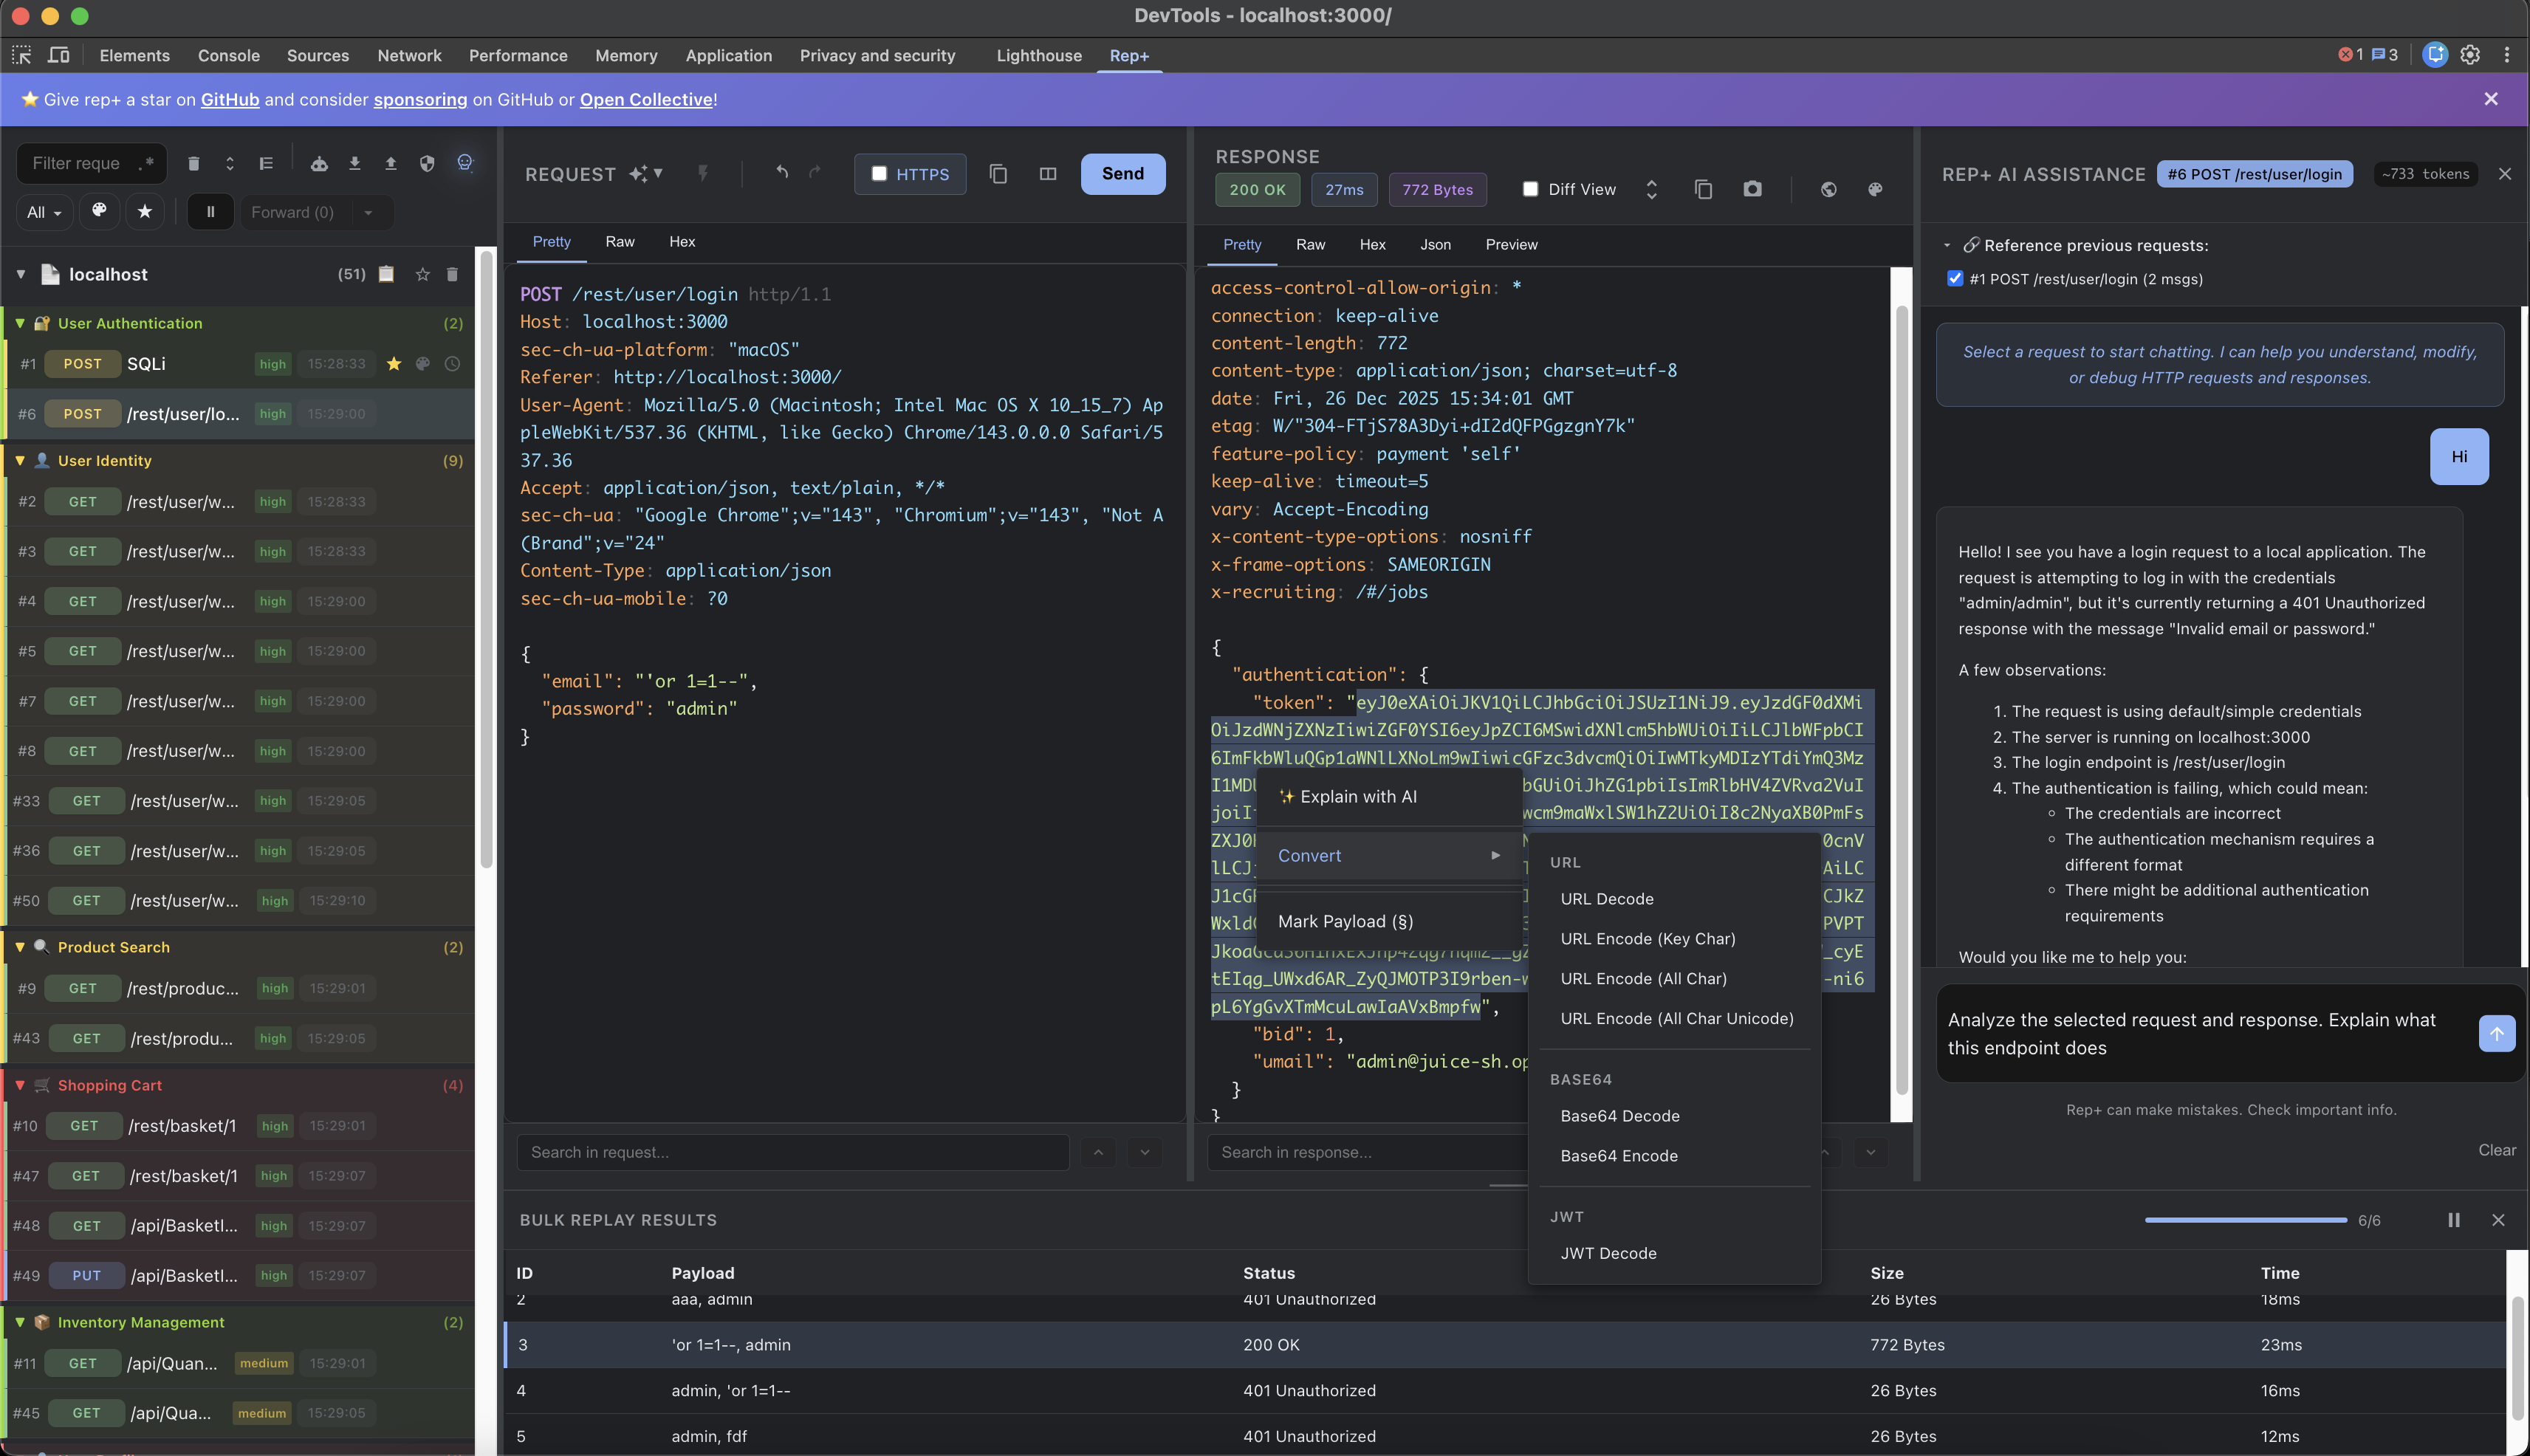 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
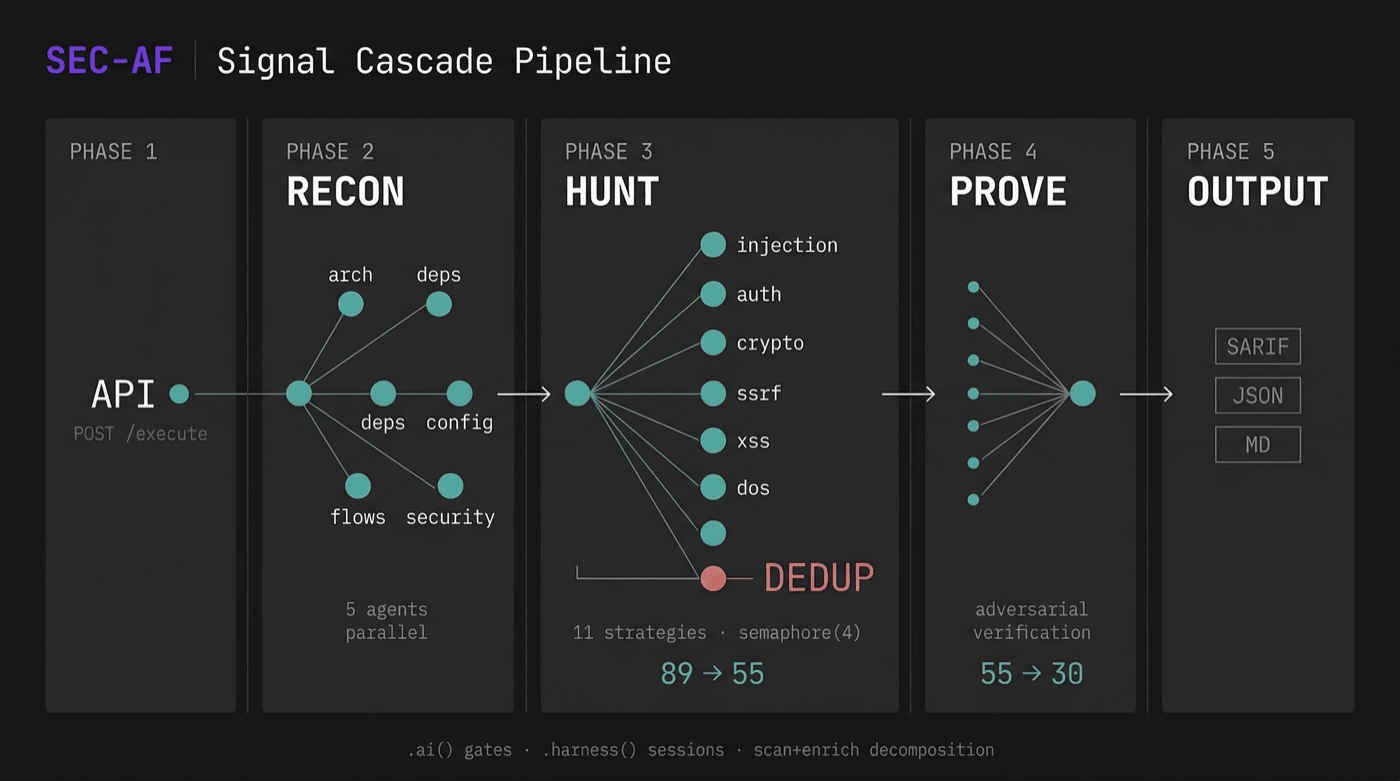 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
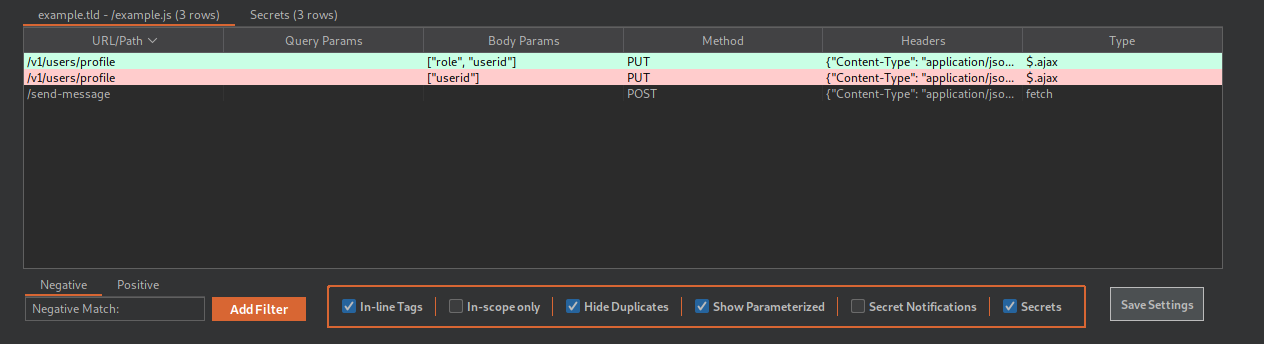 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
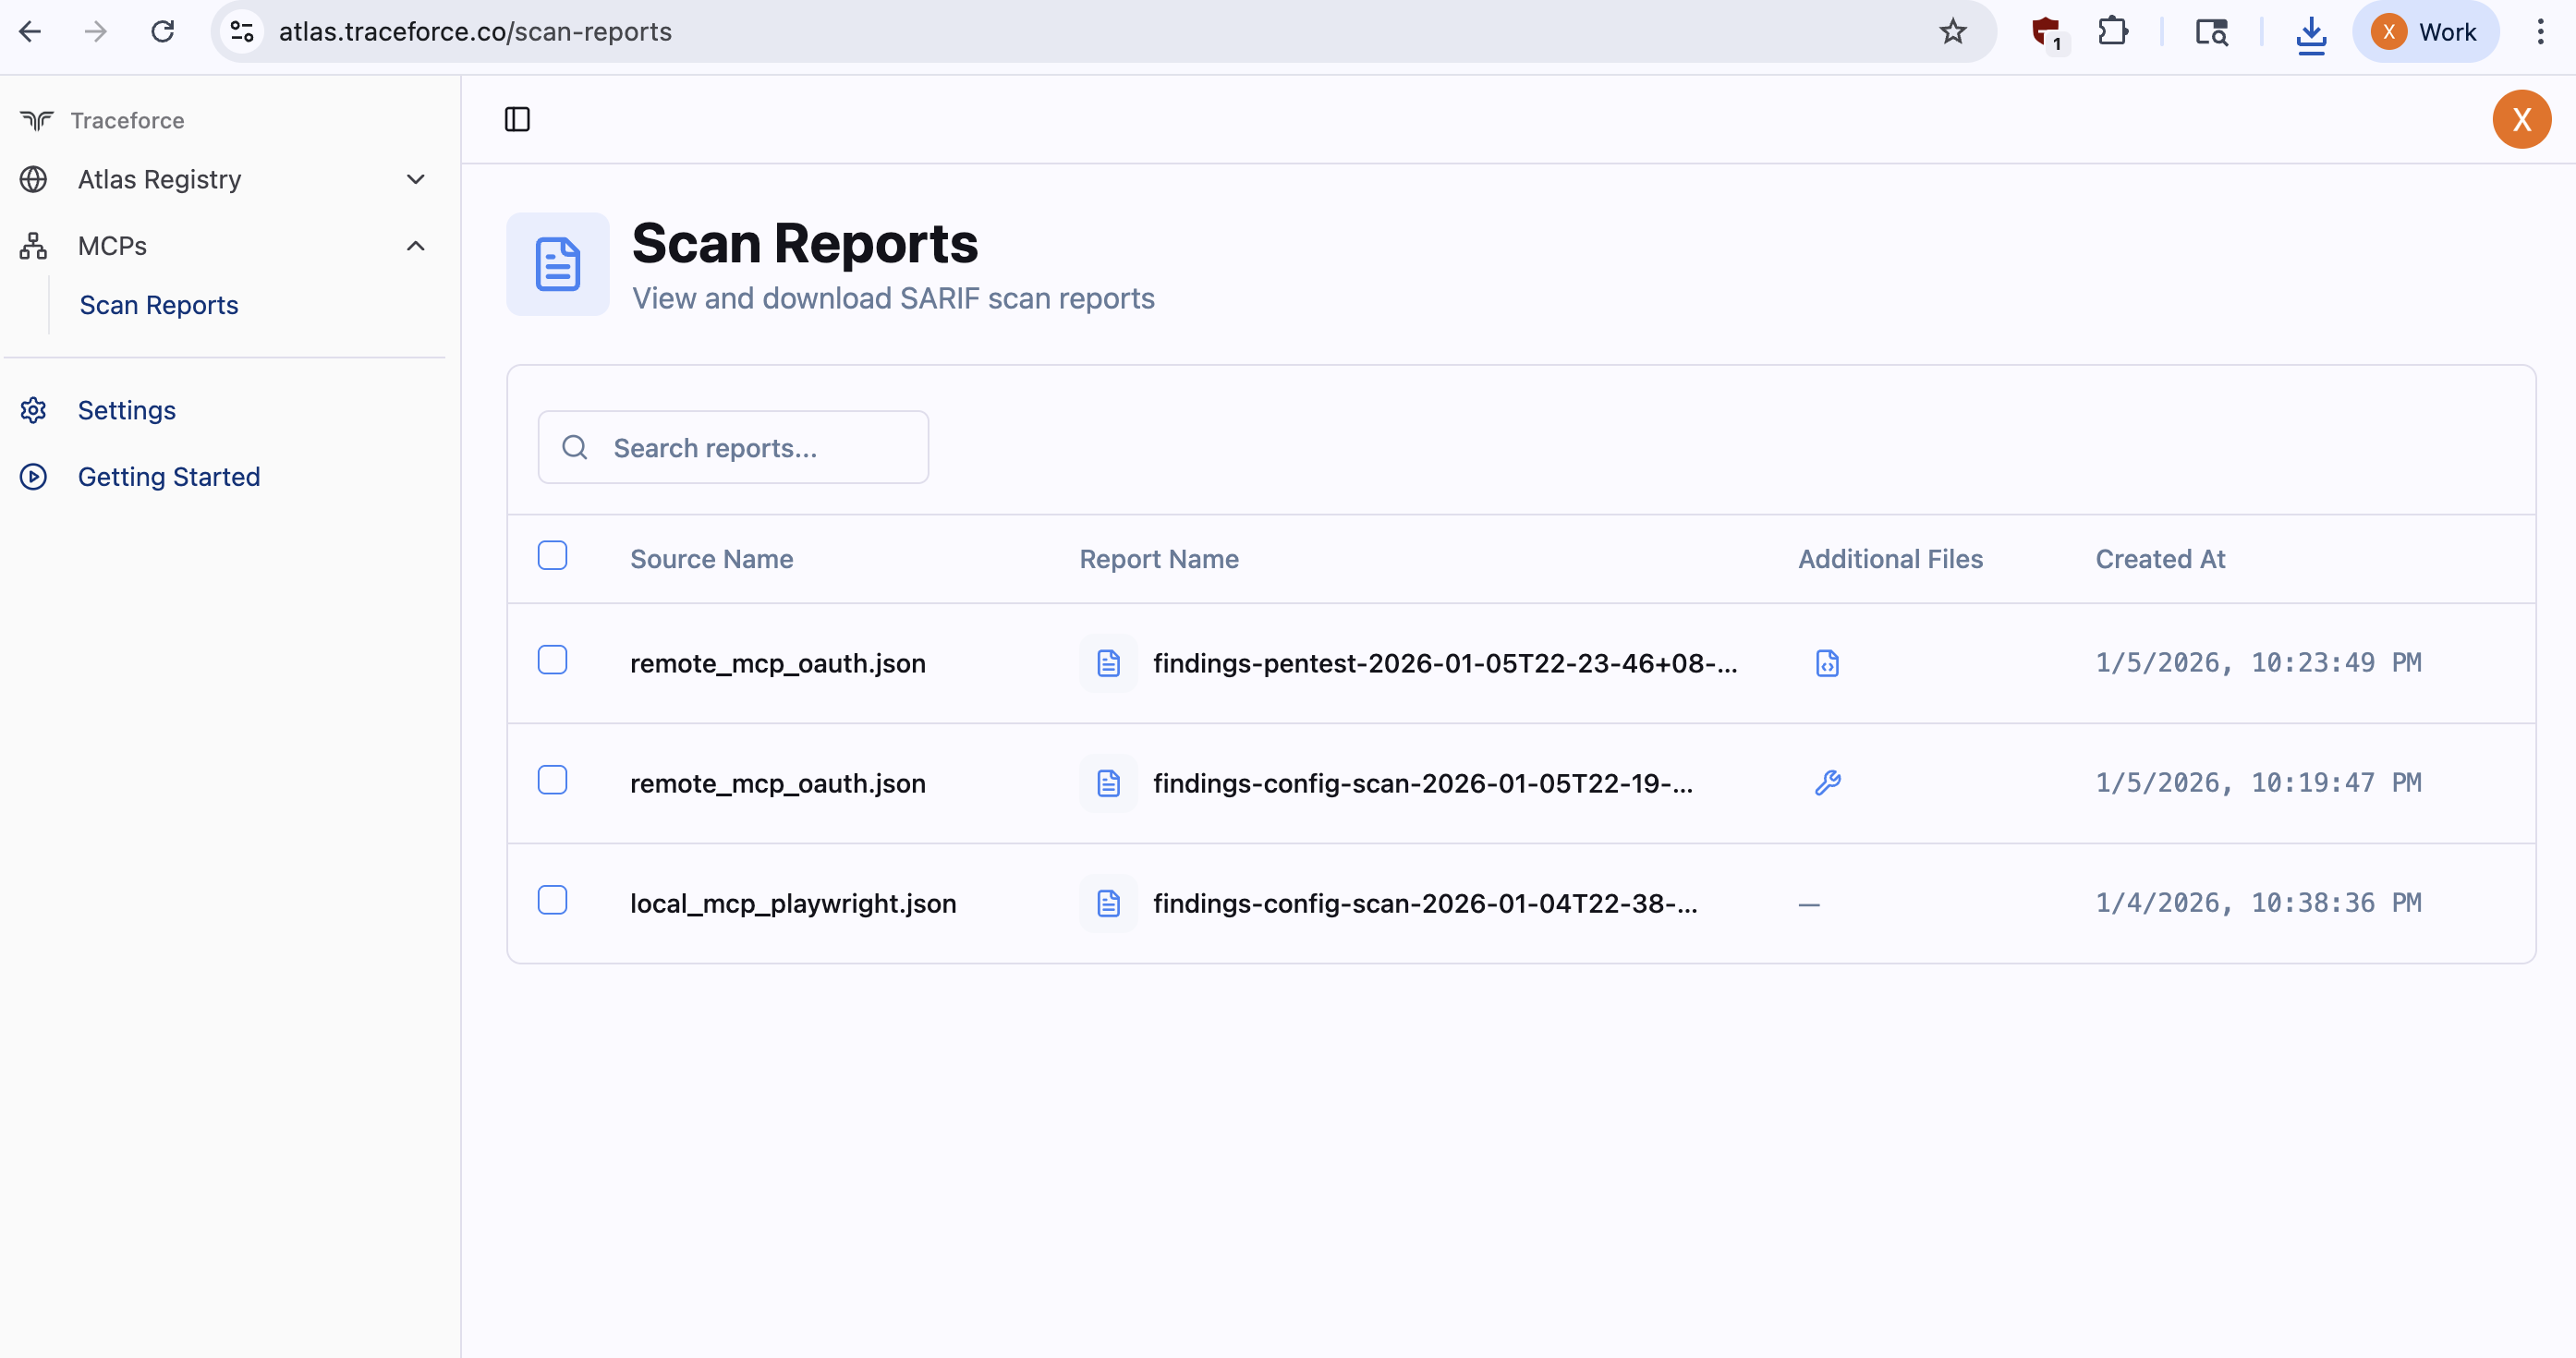 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…