

bearer
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
code-analysisdevsecopsprivacy+3
bearer/bearerCode security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 sepehrdaddev/zap-scripts
Zed Attack Proxy Scripts for finding CVEs and Secrets.
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
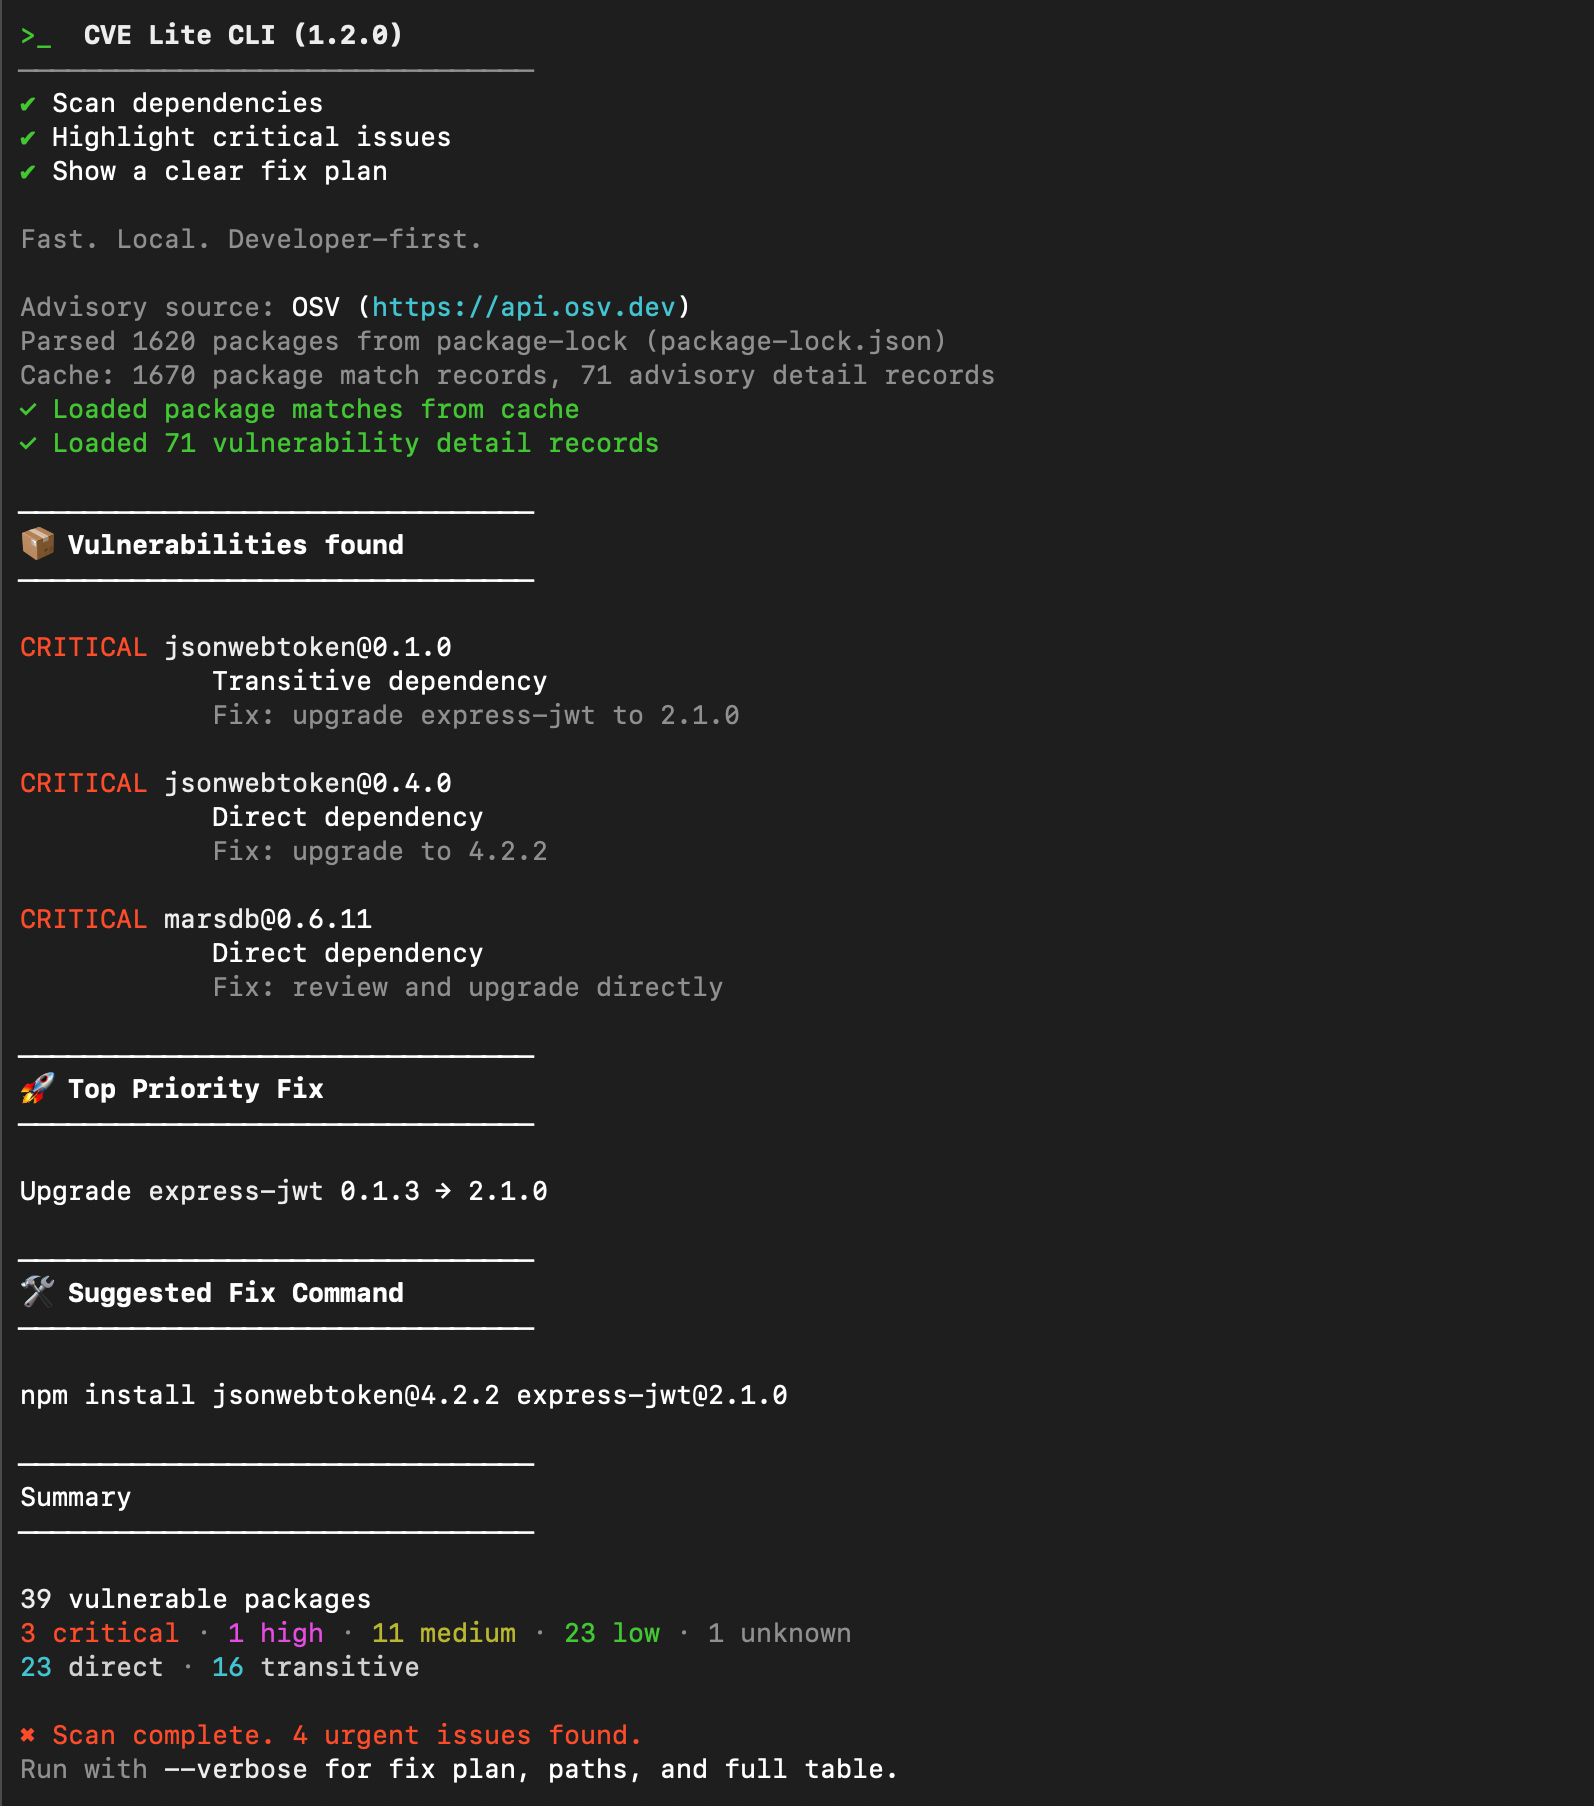 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
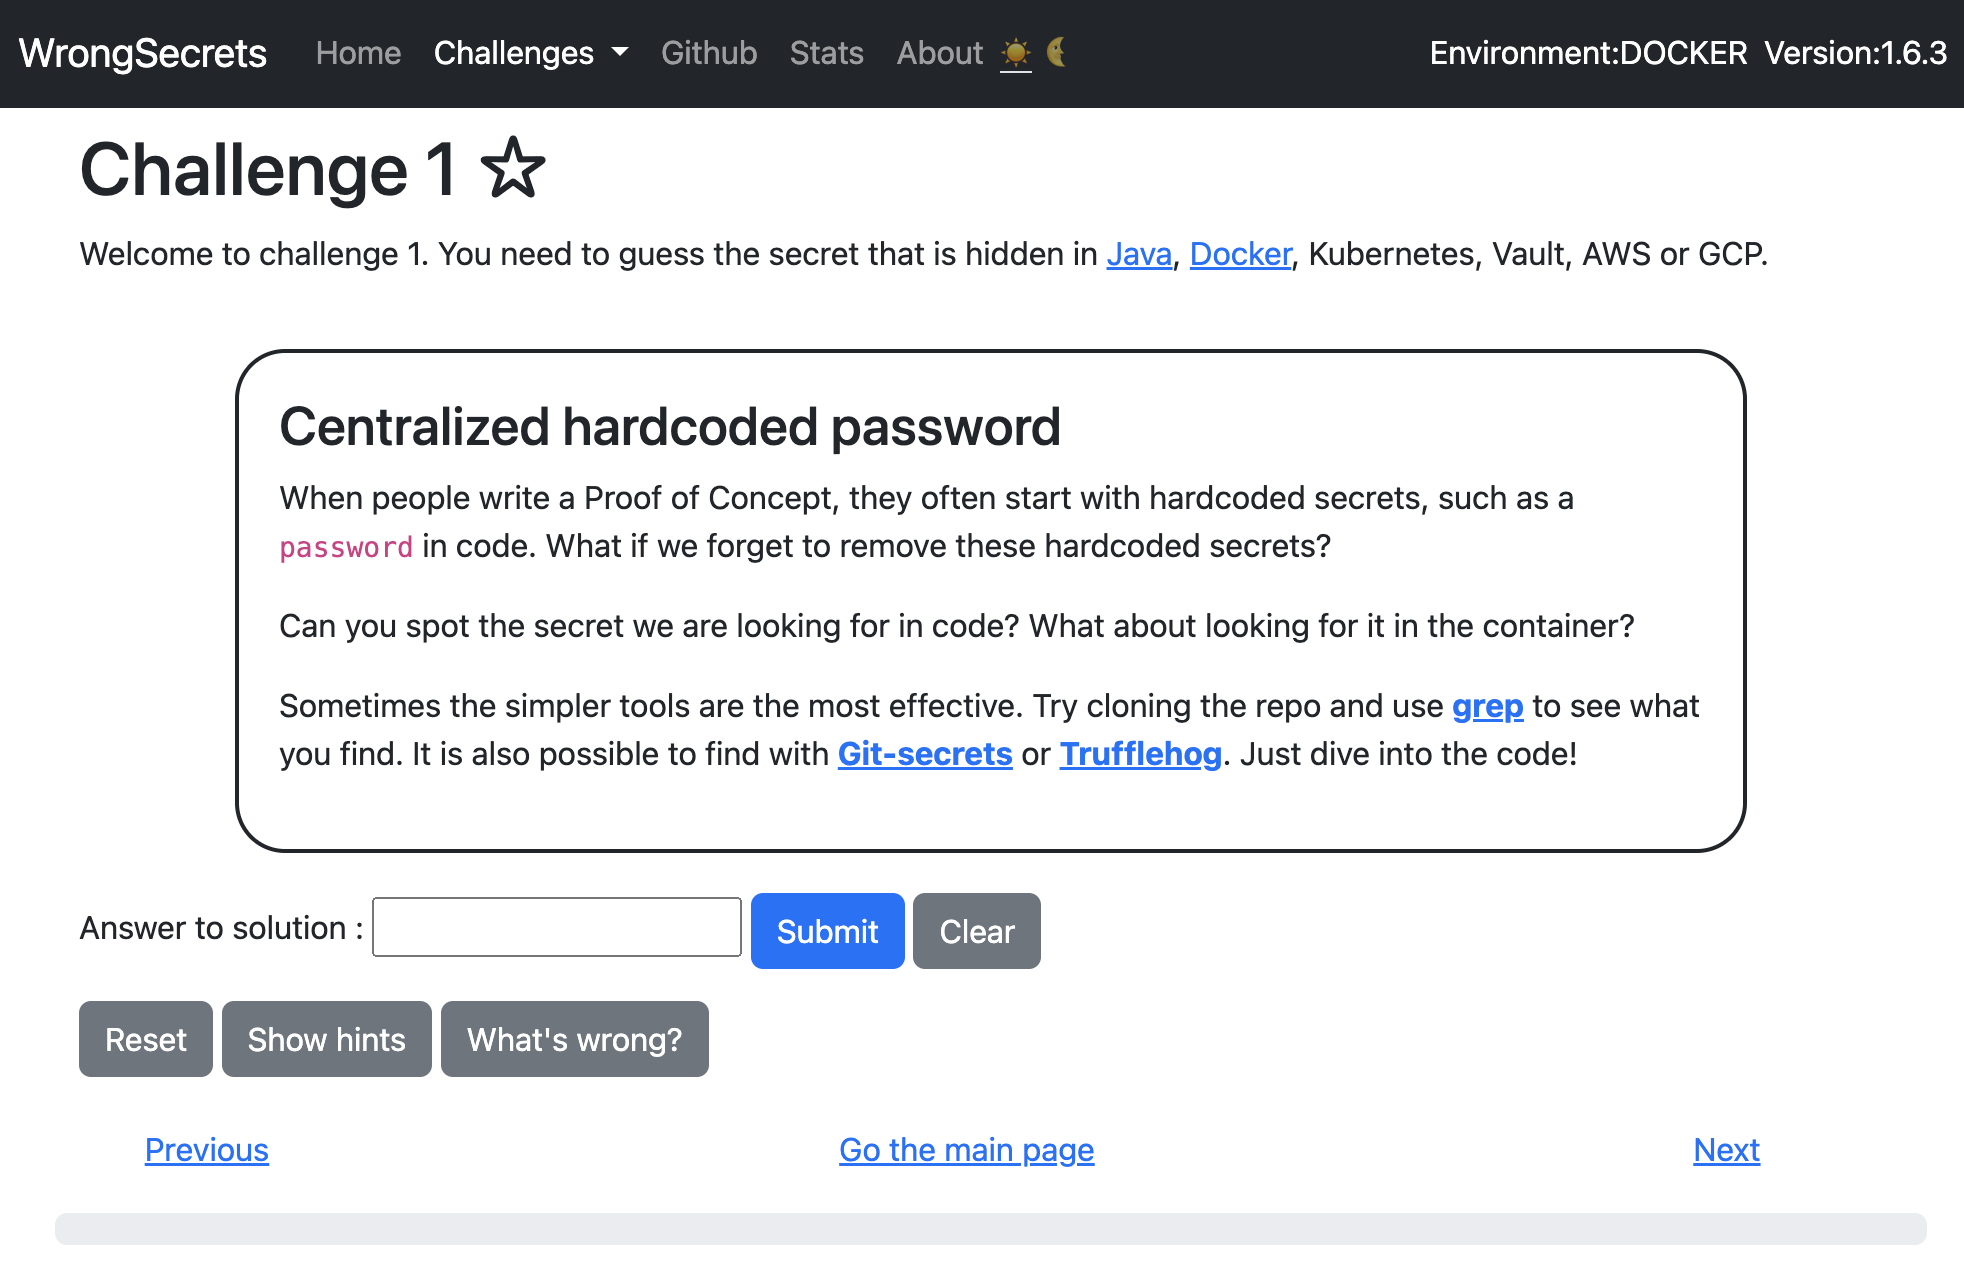 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
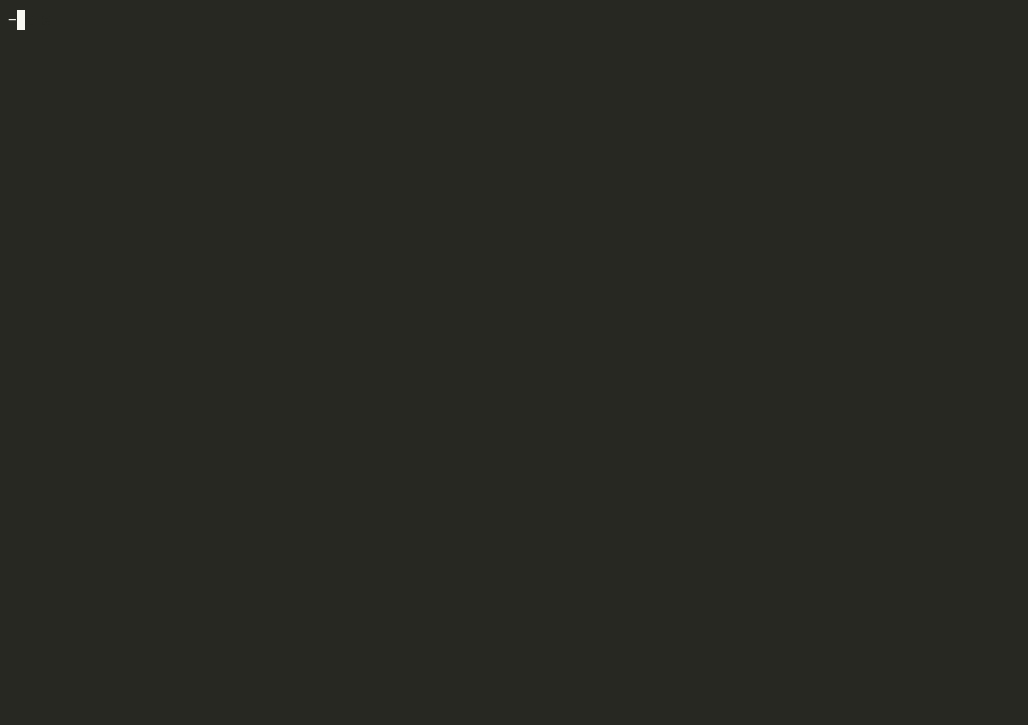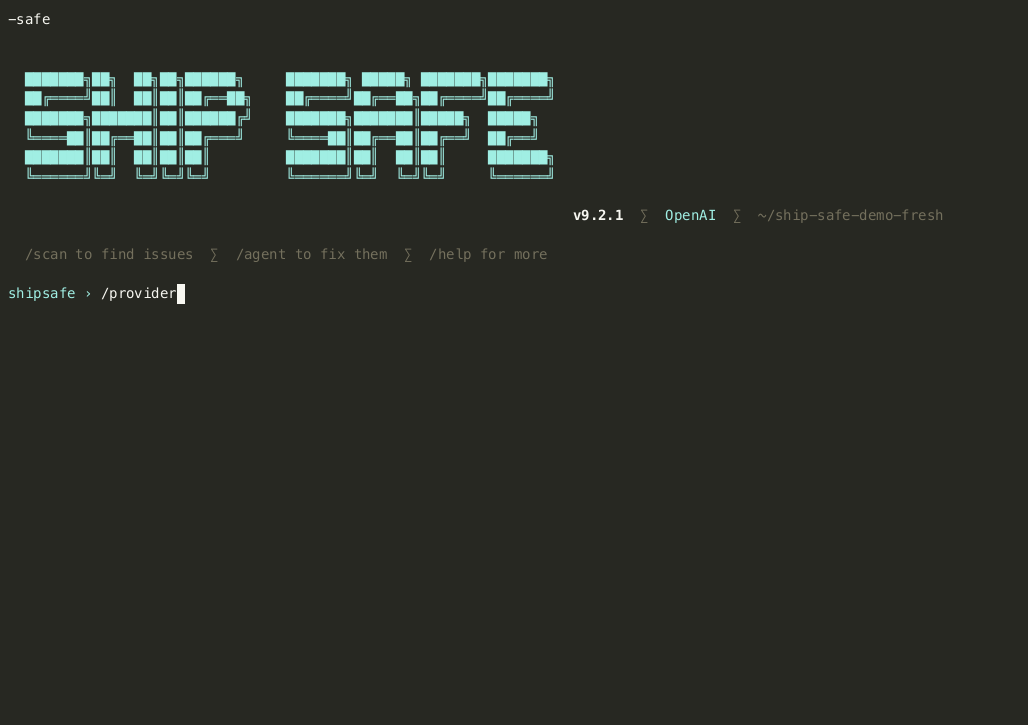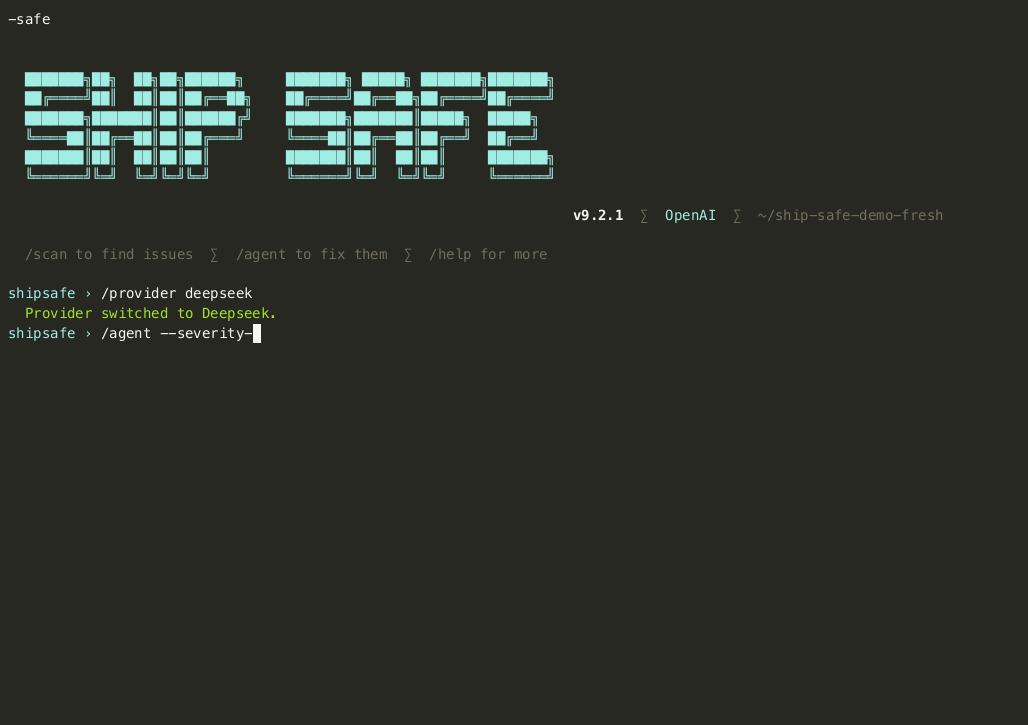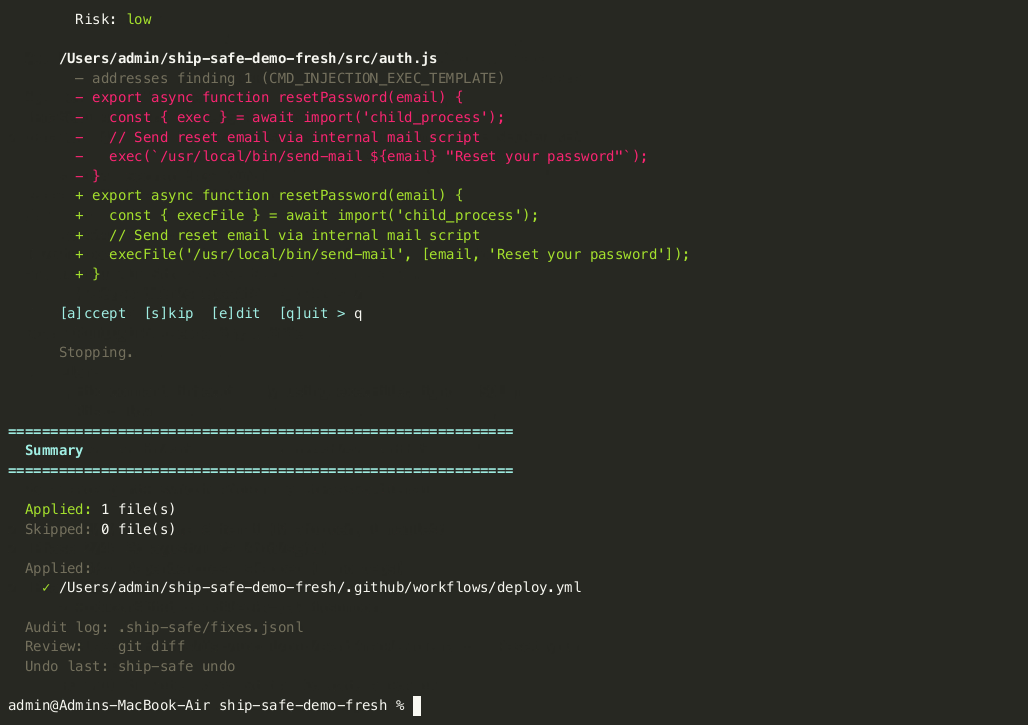 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
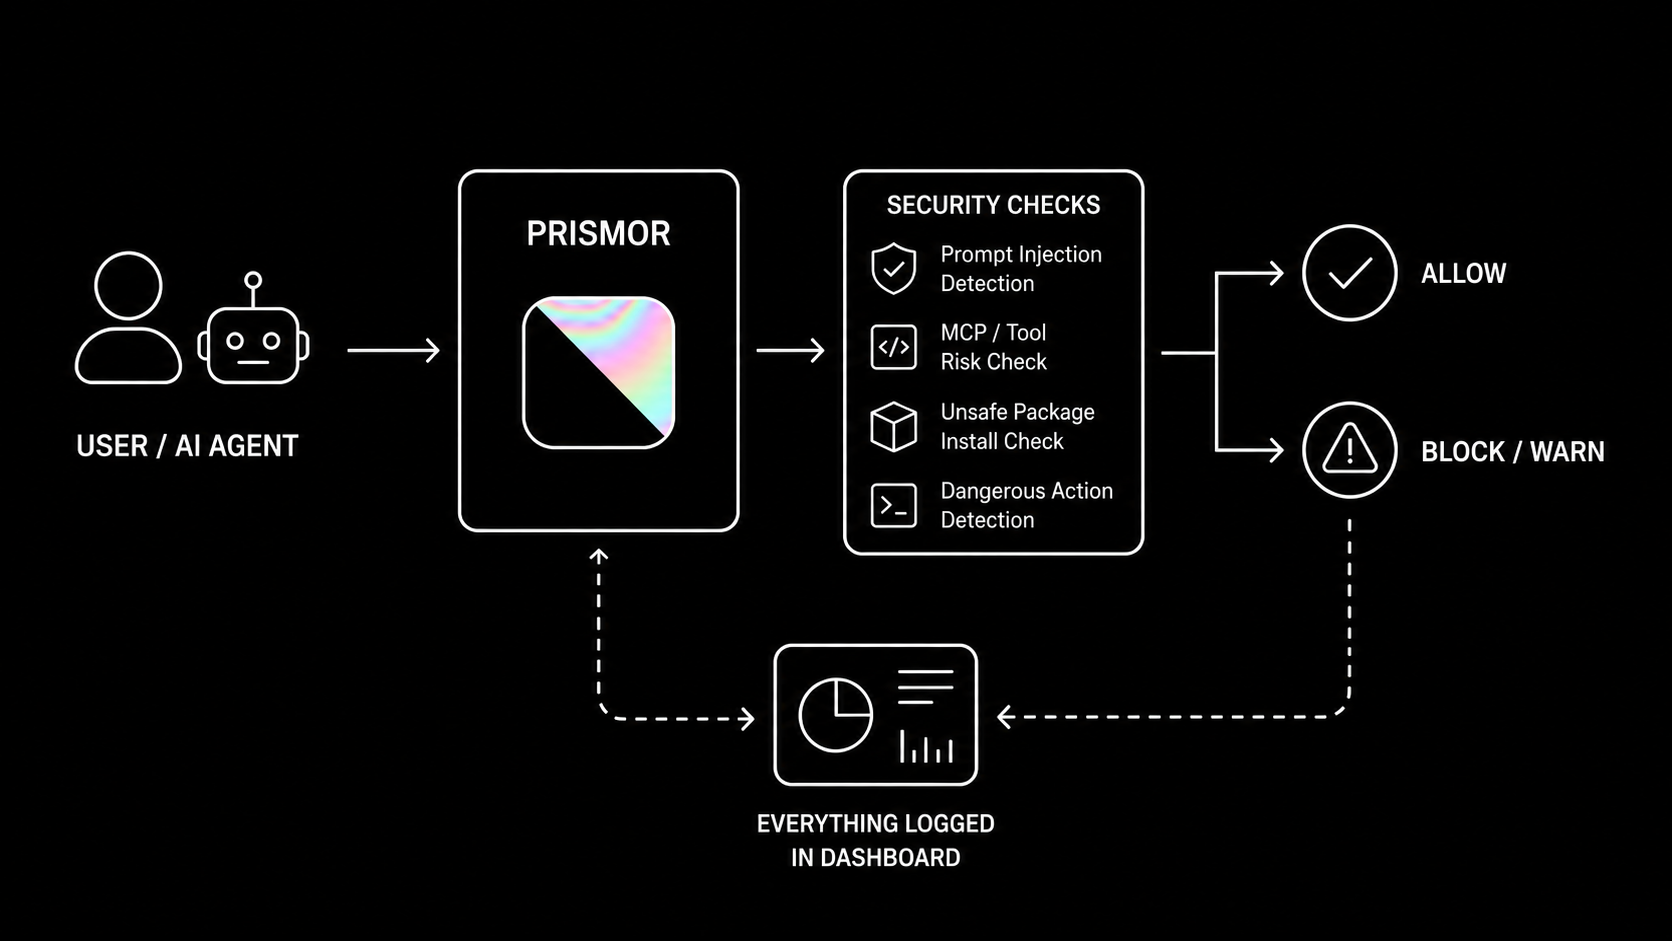 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
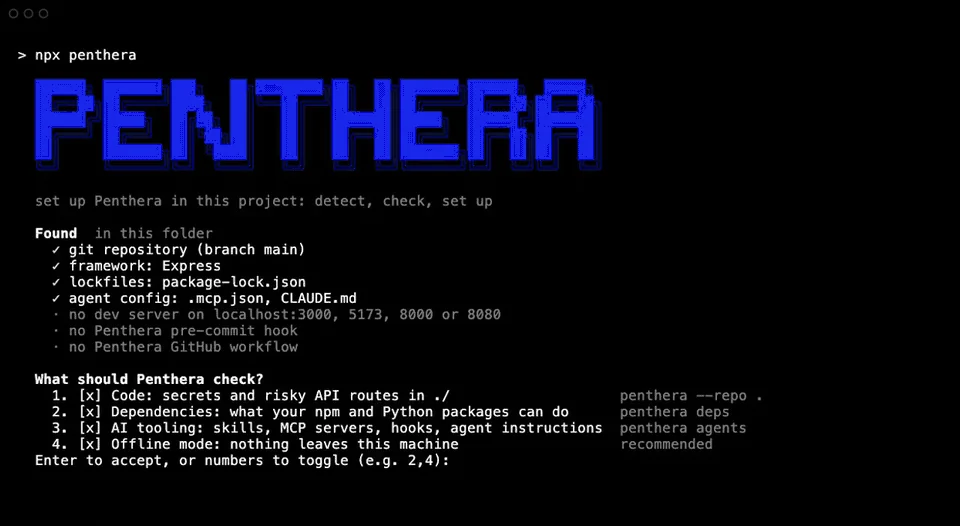 danoszz/penthera
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…