
VulnClaw
 netw0rknoob/vulnclaw
基于 AI Agent + MCP 工具链 + 渗透 Skill 编排, 配合大语言模型, 自然语言输入 → 自动完成「信息收集 → 漏洞发现 → 漏洞利用 → 报告生成」全流程。
ai-securitycommand-and-controlctf+9
3.9k5 days ago
netw0rknoob/vulnclaw基于 AI Agent + MCP 工具链 + 渗透 Skill 编排, 配合大语言模型, 自然语言输入 → 自动完成「信息收集 → 漏洞发现 → 漏洞利用 → 报告生成」全流程。
 lauriewired/jadxecute
JADX-gui scripting plugin for dynamic decompiler manipulation
 xsanflip/anti-begal.py
Python script that exploits a resource-exhaustion flaw in the B.E.G.A.L C2 collector endpoint, flooding it with spoofed XOR/Base64 payloads to…
 ph4ntom-rev/ph4ntom-ida-bridge
Secure local REST, CLI, MCP, and agent bridge for IDA Pro 9.x
 xsscx/fuzz
Commodity Injection Signatures, Malicious Inputs, XSS, HTTP Header Injection, XXE, RCE, Javascript, XSLT
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 bitplugg/kitsune
🦊 nine-tailed pentest framework — nmap + msf + aircrack + sqlmap в одном CLI · 25 модулей · SQLite-сессия · TUI · REST API · pipx install
 mordavid/bruteforceai
Advanced LLM-powered brute-force tool combining AI intelligence with automated login attacks
 zu1k/good-mitm
Rule-based MITM engine. Rewriting, redirecting and rejecting on HTTP(S) requests and responses, supports JavaScript rule.
 david-alvarez-rosa/php-rce
Exploits for CVE-2026-109618 / CVE-2026-109619 to achieve RCE on PHP targets
 david-alvarez-rosa/php-rce
Exploits for CVE-2026-109618 / CVE-2026-109619 to achieve RCE on PHP targets
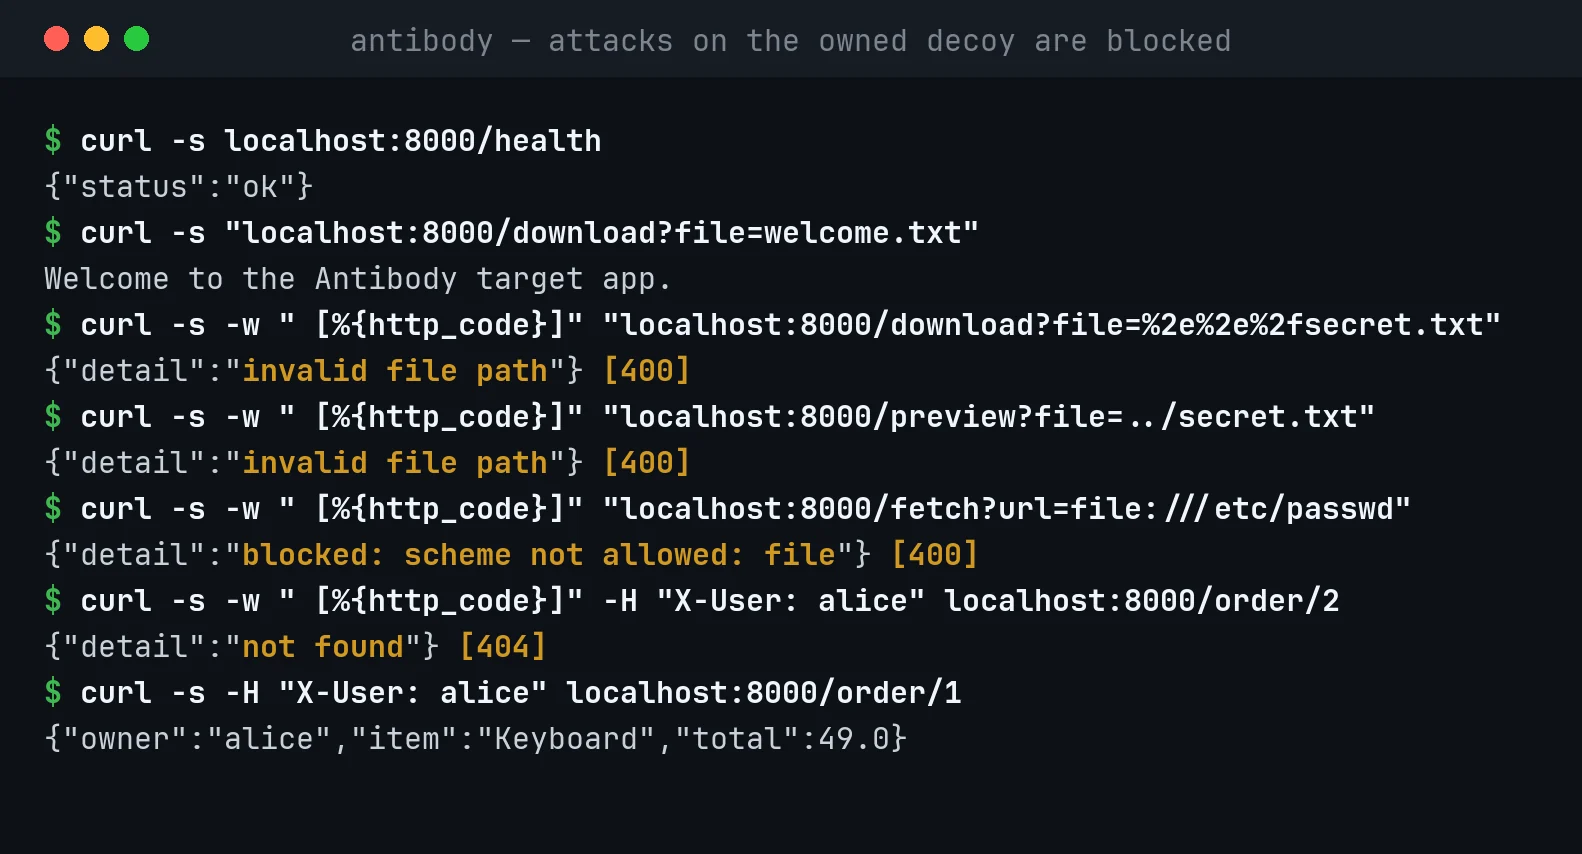 lsudoko/antibody
GitLab Duo DevSecOps loop where a second AI re-attacks every AI-written fix, saving each successful bypass as a permanent antibody replayed in CI and…
 2t8a/cve-2025-49132
Python scanner for CVE-2025-49132 that exploits a path traversal in Pterodactyl Panel's locale endpoint to extract exposed database configuration…
 infobyte/ai-pentest-agent
Standalone autonomous AI pentest agent with a plan→act→judge loop, generic skills, destructive-action gate, and swappable LLM providers, plus a…
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 oscarsantanaarias/ida-ghidra-bridge
TCP JSON bridge servers for IDA Pro and Ghidra exposing decompilation, xrefs, symbols, vtables, RTTI and memory patching to external scripts and…
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…