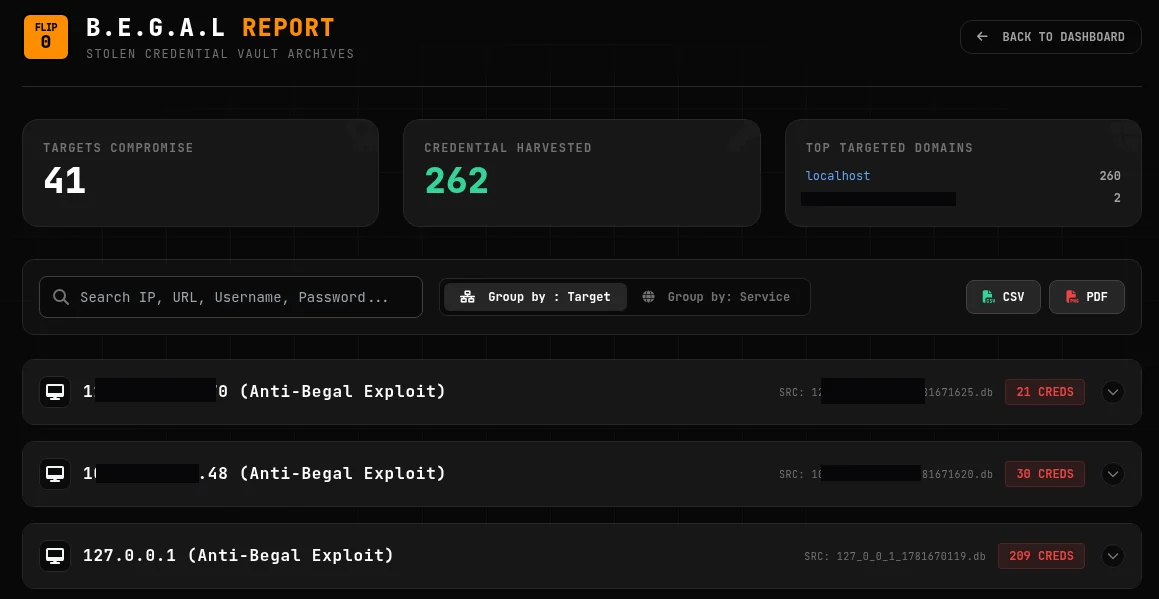
 xsanflip/anti-begal.py
Python script that exploits a resource-exhaustion flaw in the B.E.G.A.L C2 collector endpoint, flooding it with spoofed XOR/Base64 payloads to disrupt rogue command-and-control servers.

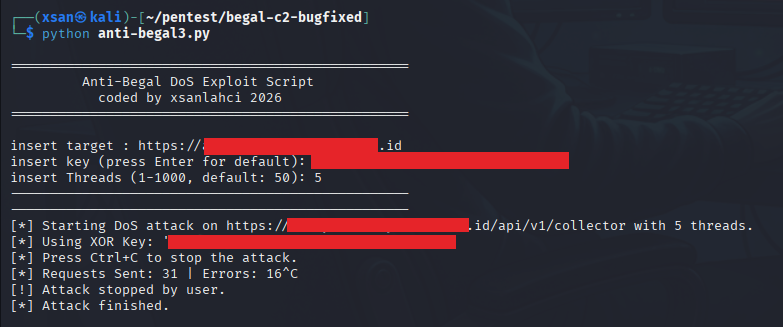
Anti-Begal (anti-begal.py) is an Active Defense and tactical disruption script designed specifically to target and neutralize unauthorized instances of the B.E.G.A.L (Backdoor Exfiltration Gateway for Advanced Looting) Command and Control (C2) framework.
This script acts as the "vaccine" to the B.E.G.A.L framework. It exploits a deliberate architectural vulnerability (Resource Exhaustion via an unauthenticated endpoint) left within the original B.E.G.A.L source code to allow Blue Teams and Security Researchers to dismantle rogue C2 servers deployed by malicious actors.
This tool is released strictly for Educational Purposes, Active Defense Research, and Authorized Takedown Operations.
Authorization is Mandatory: You must have explicit, legal authorization to target the infrastructure you are aiming this script at (e.g., you are a system administrator defending your network, or participating in a sanctioned law enforcement takedown).
No Malicious Use: Using this tool to perform Denial of Service (DoS) attacks against public network infrastructure or third-party servers without consent is illegal and strictly prohibited.
No Liability: The developer (xsanlahci) assumes zero liability and is not responsible for any misuse, damage, or legal consequences caused by the use of this program.
By using this software, you agree to these terms.
The B.E.G.A.L C2 framework relies on an unauthenticated data collection endpoint (/api/v1/collector) to receive obfuscated (XOR + Base64) payload data from its bot agents.
Because the C2 server dynamically allocates memory (ACTIVE_SESSIONS and CREDENTIAL_VAULT) and creates a new SQLite database file for every unique bot UUID it receives, it is highly susceptible to Resource Exhaustion.
anti-begal.py automates the exploitation of this design flaw:
Payload Generation: It replicates B.E.G.A.L's XOR cipher and Base64 encoding.
UUID Spoofing: It generates thousands of fake bot UUIDs.
Junk Data Injection: It injects massive amounts of junk data into the payload to amplify the storage impact.
Multi-Threading: It floods the target /api/v1/collector endpoint with these spoofed, encrypted requests using concurrent threads.
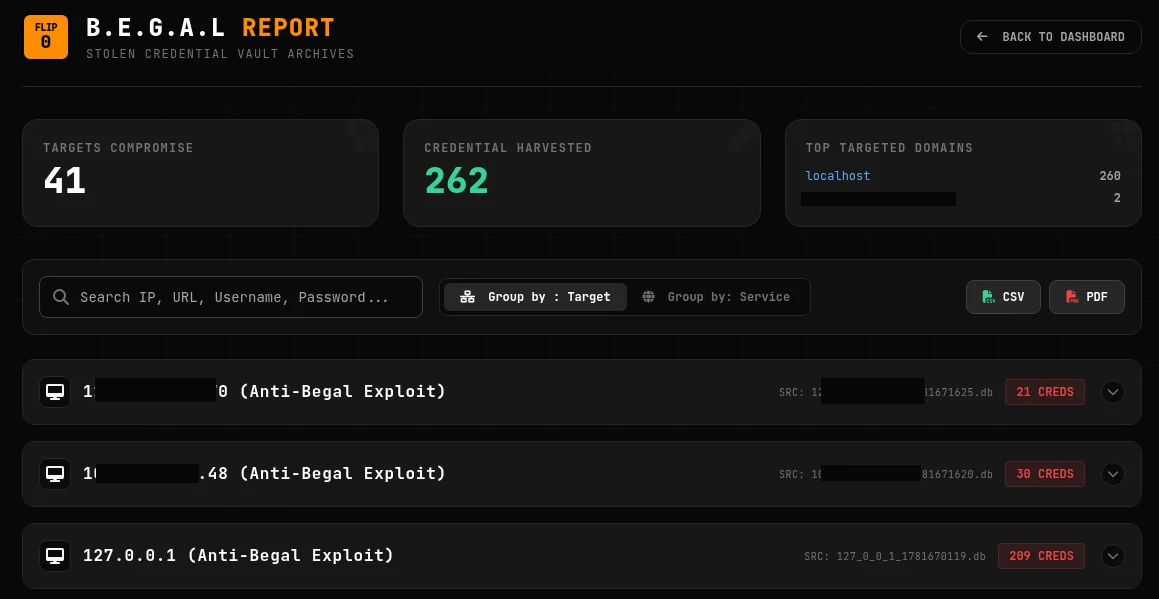
Memory Exhaustion (OOM): The Python Flask server's memory allocation will skyrocket, causing the C2 interface to lag severely or crash completely.
Storage/Inode Starvation: The target server's hard drive will be flooded with thousands of fake SQLite .db files, preventing the threat actor from saving actual stolen credentials.
Data Poisoning: The threat actor's credential vault will be rendered useless, buried under thousands of fake bot entries.
Python 3.x
requests library (pip install requests)
You can run the script interactively. It will prompt you for the necessary parameters.
python3 anti-begal.py
insert target : The base URL of the rogue B.E.G.A.L C2 server (e.g., http://192.168.1.100:31337 or https://rogue-c2.example.com). The script will automatically append the /api/v1/collector path.
insert key (press Enter for default): The XOR key used by the target C2. If you don't know it, pressing Enter will use the default B.E.G.A.L key. (Note: Even with an incorrect key, the attack may still consume server resources processing the bad payload).
insert Threads (1-1000, default: 50): The number of concurrent attack threads. Higher numbers increase the flood rate but consume more CPU/RAM on your attacking machine. 50 to 200 is usually sufficient to disrupt a standard Flask deployment.
==================================================
         Anti-Begal DoS Exploit Script
           coded by xsanlahci 2026
==================================================

insert target : http://10.10.10.50:31337
insert key (press Enter for default):
[*] Using default key: FLIPPER_SECURE_XOR_KEY_1337
insert Threads (1-1000, default: 50): 100
--------------------------------------------------
--------------------------------------------------
[*] Starting DoS attack on http://10.10.10.50:31337/api/v1/collector with 100 threads.
[*] Using XOR Key: 'FLIPPER_SECURE_XOR_KEY_1337'
[*] Press Ctrl+C to stop the attack.
[*] Requests Sent: 4520 | Errors: 12
If you are running B.E.G.A.L for educational purposes in a lab and want to patch this "Kill-Switch":
Implement Rate Limiting: Add Flask-Limiter to restrict the number of requests per IP to the /api/v1/collector endpoint.
Authentication/Pre-Shared Key: Require a pre-shared cryptographic token in the request header before processing the payload or allocating memory.
Payload Size Limits: Strictly enforce a maximum content-length for incoming requests.
Created by xsanlahci - 2026
