
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
VulnClaw — 基于 AI Agent + MCP 工具链 + 渗透 Skill 编排, 配合大语言模型, 自然语言输入 → 自动完成「信息收集 → 漏洞发现 → 漏洞利用 → 报告生成」全流程。 | Kitploit
Tools/GitHubGitHub/netw0rknoob/vulnclaw
ReconnaissanceVulnerability ScannersPayload GenerationVulnerability AnalysisExploitationScripting & AutomationWeb Application ExploitationInformation GatheringCTFPenetration TestingCommand and Control
3.9k53784 days agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
AI Security
GitHubnetw0rknoob/vulnclaw

VulnClaw

基于 AI Agent + MCP 工具链 + 渗透 Skill 编排, 配合大语言模型, 自然语言输入 → 自动完成「信息收集 → 漏洞发现 → 漏洞利用 → 报告生成」全流程。

View RepositoryWebsite
Share

VulnClaw 🦞

AI-Powered Penetration Testing CLI — Speak plainly, find real bugs.

License: MIT Python 3.10+ OpenAI Compatible MCP PyPI codecov Security Discord AtomGitStars Kimi Open Source Friends

🌐 中文版: README.md

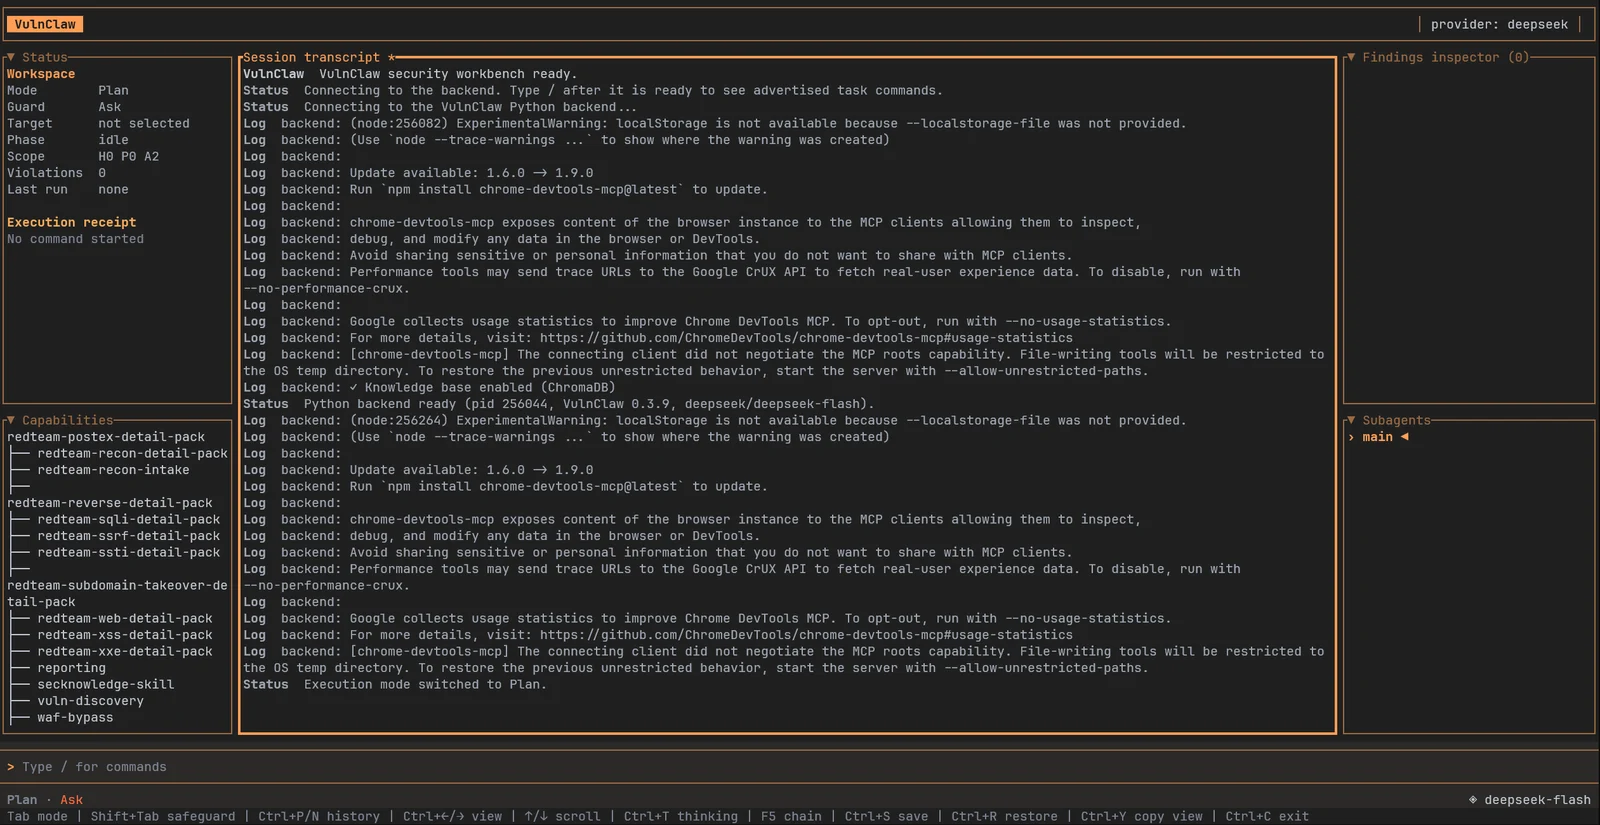
This project is a standalone AI penetration testing Agent.
Official Website: https://unclecheng-li.github.io/vulnclaw.com/

Built on LLM Agent + MCP Toolchain + optional Skill reference material, compatible with OpenAI / Anthropic / MiniMax / DeepSeek and similar models. Natural language input → automated "Recon → Vulnerability Discovery → Exploitation → Reporting".

Quick Start · Architecture · Built-in Skills


What It Does

Give it a natural language command and watch it run a full pentest:

User:   "Run a penetration test on http://target.example.com"

VulnClaw executes:
  Round 1:  Recon → Fingerprinting, port scan, directory enumeration
  Round 2:  Vulnerability Discovery → Injection points, known CVEs, misconfigs
  Round 3:  Exploitation → PoC verification, access obtained
  Round 4:  Reporting → Structured report + Python PoC script
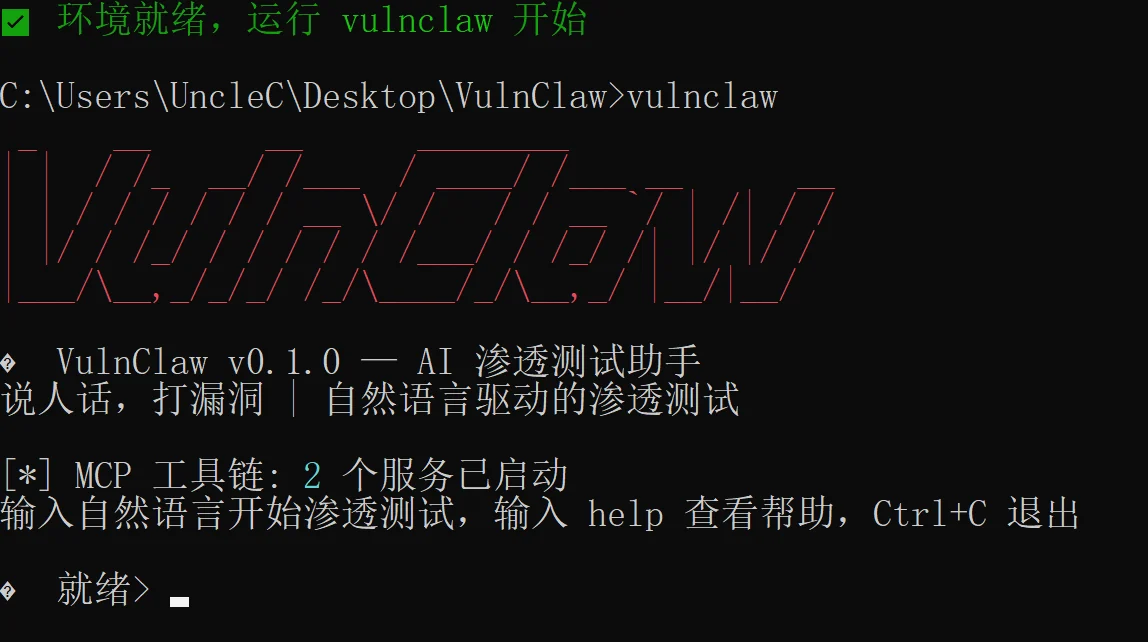
image image

Suitable for authorized pentests, CTF competitions, security training, and red team operations.


Features

Download Tool