
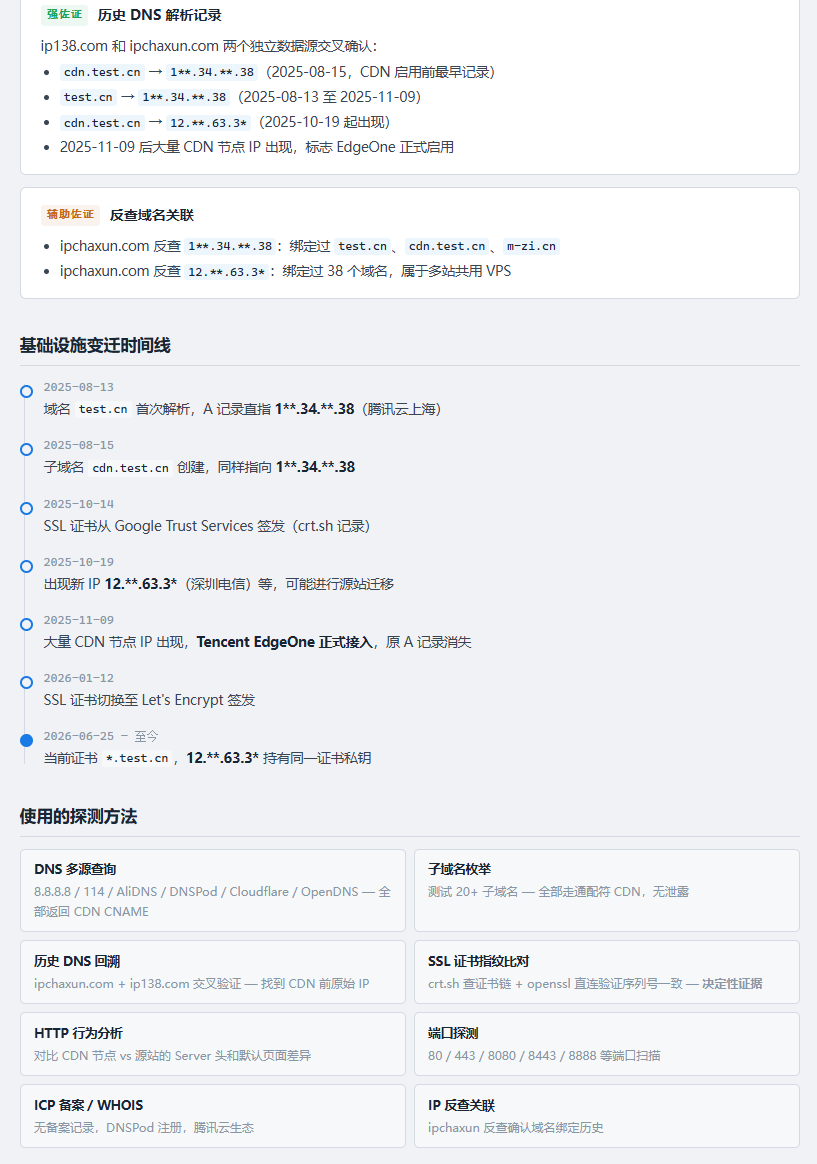
FUCK-CDN
 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
dns-analysisdns-subdomain-enumerationinformation-gathering+9
169
0xshe/fuck-cdnAutomated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
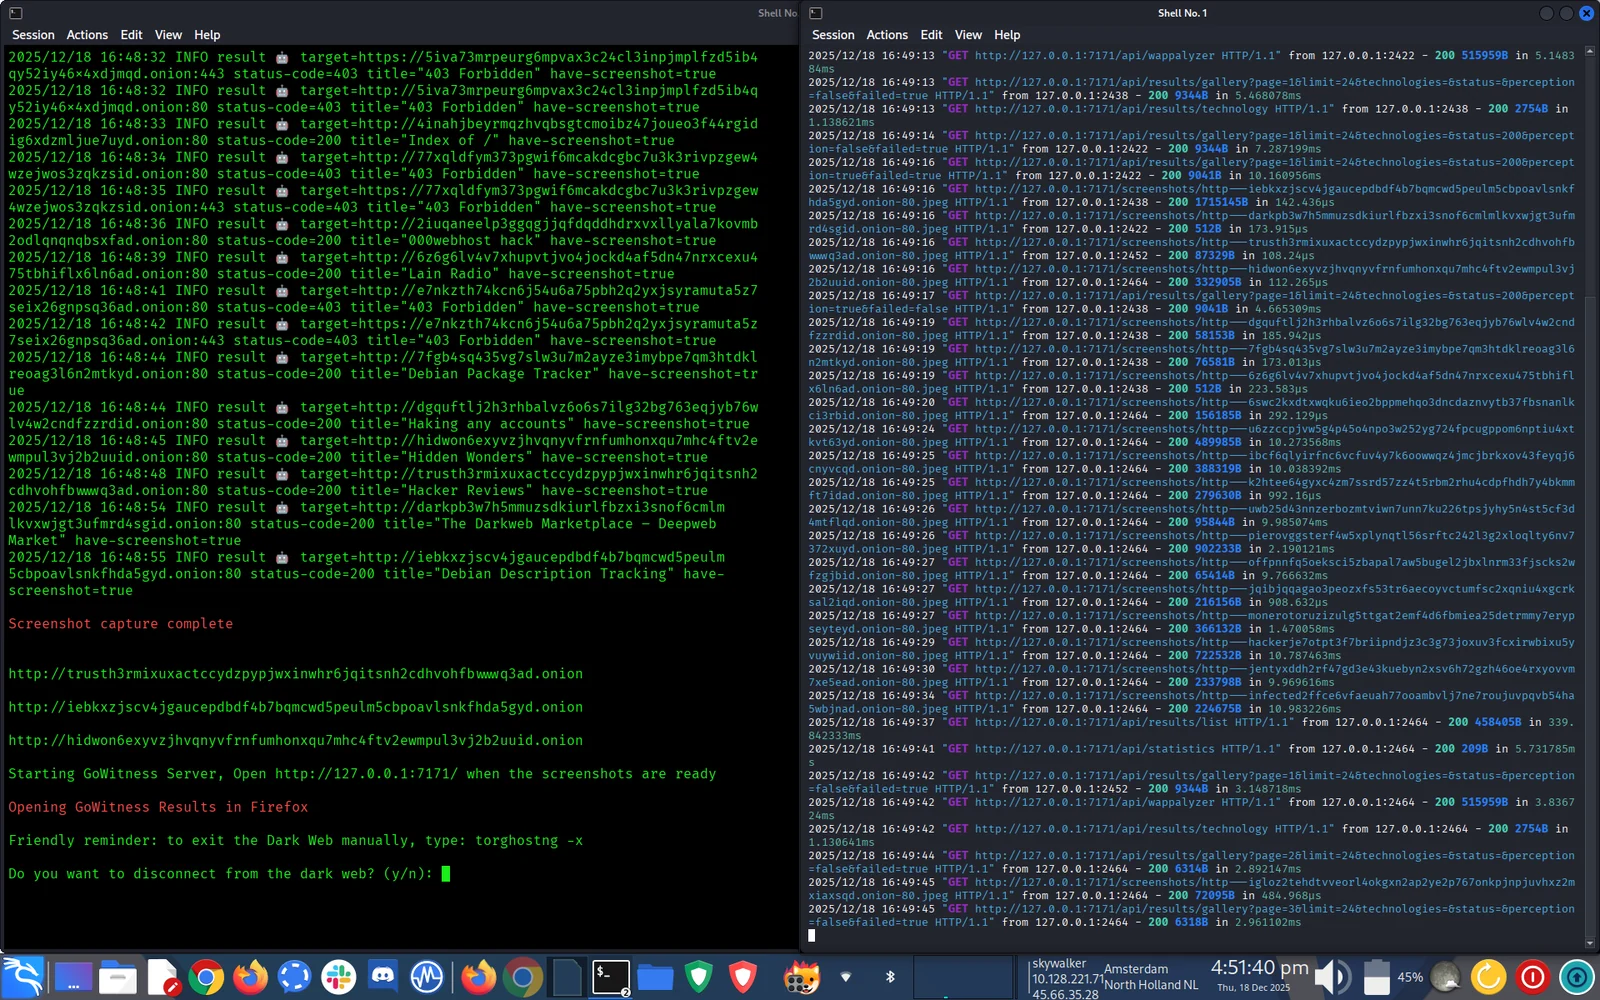 aryanguenthner/darkfox
CTI Cyber Threat Intelligence OSINT Dark Web Deep Web Research. Ransomware gang information gathering tool.
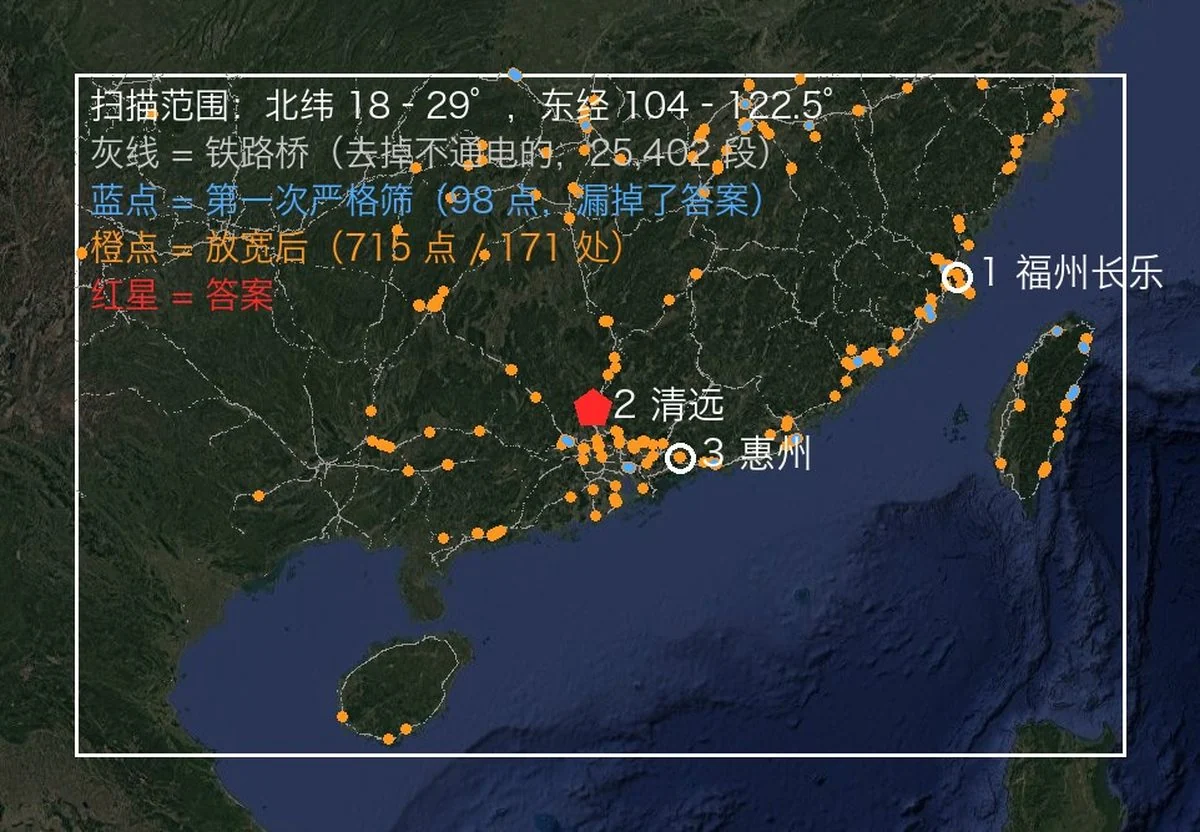 oldcircle/geo-sleuth
An agent skill that finds where a photo was taken — OpenStreetMap geometry, elevation skylines, satellite imagery and street view — and shows its…
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
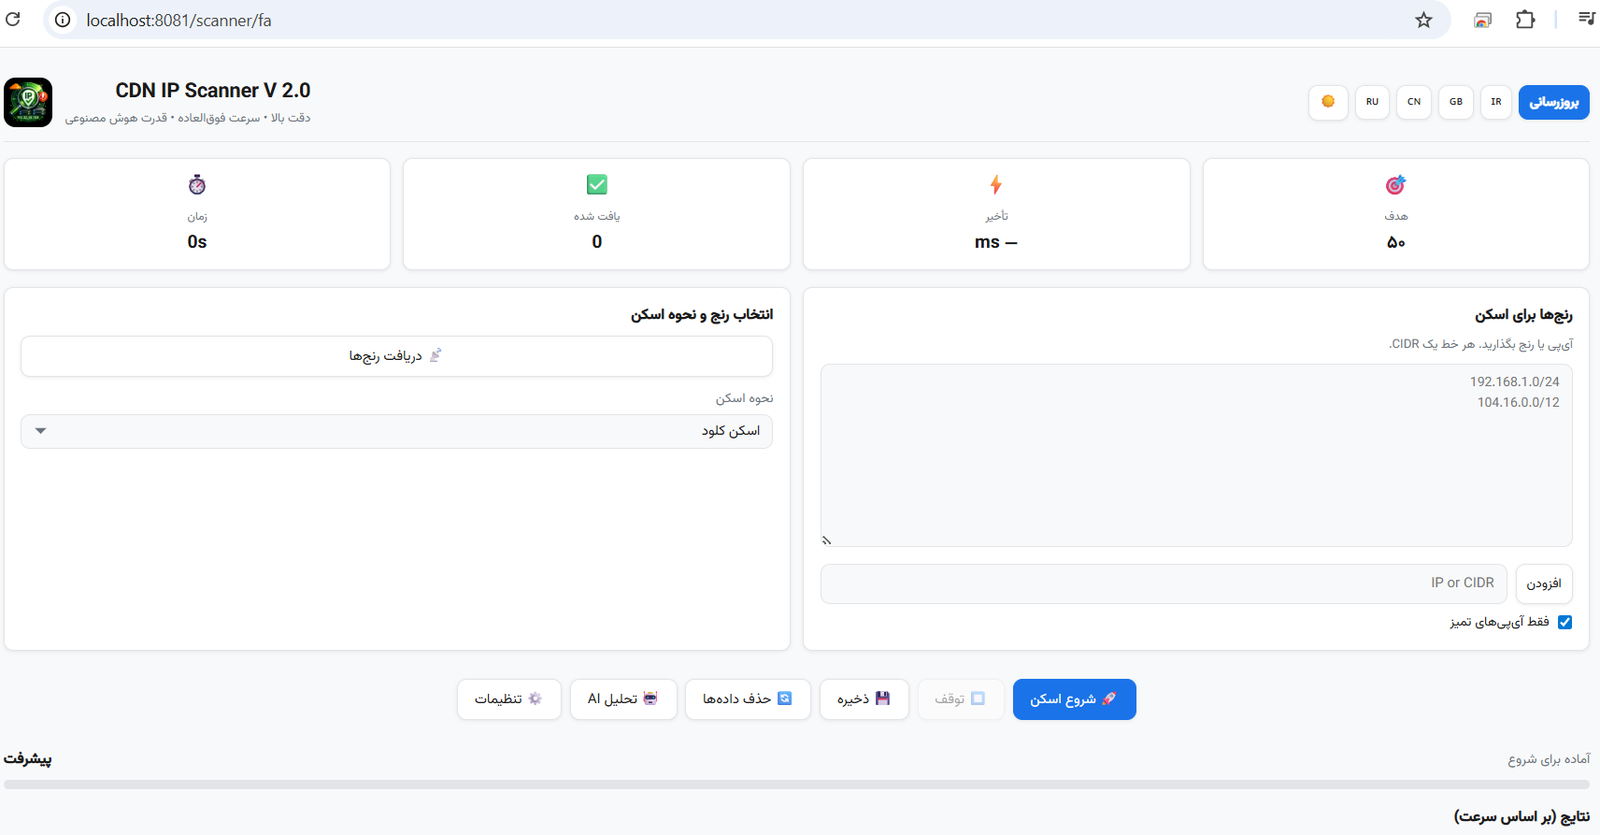 shahinst/cdn-ip-scanner
Web-based scanner that discovers fast, low-latency CDN IP addresses from Cloudflare, Fastly and other providers using multi-threaded 5-attempt…
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 kevincrrl/evillimiter-ng
EvilLimiter Next Generation: monitor, analyze and limit the bandwidth
 dedsecinside/torbot
Crawls .onion sites over Tor to collect page titles, hostnames, and link relationships, exporting JSON trees and visualizations for dark web OSINT…
 mikemeliz/torcrawl.py
Crawl and extract (regular or onion) webpages through TOR network
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 projectdiscovery/naabu
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface…
 rthalley/dnspython
Python DNS toolkit supporting queries, zone transfers, dynamic updates, TSIG, EDNS0, DNSSEC, DNS-over-HTTPS, and DNS-over-QUIC with high- and…