NtTrace
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
api-security-testingdebuggersdynamic-code-analysis+2
rogerorr/nttraceAn strace-like program for the Windows 'native' API
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
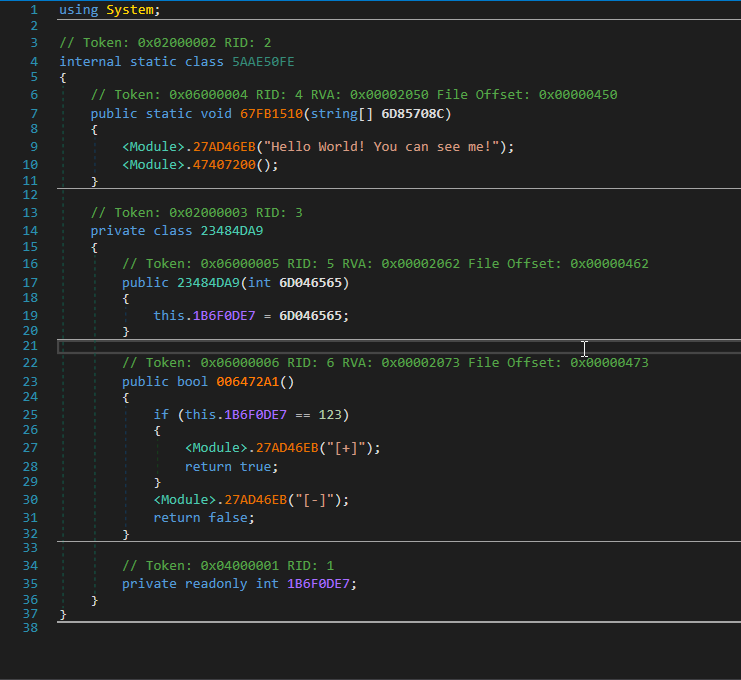 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
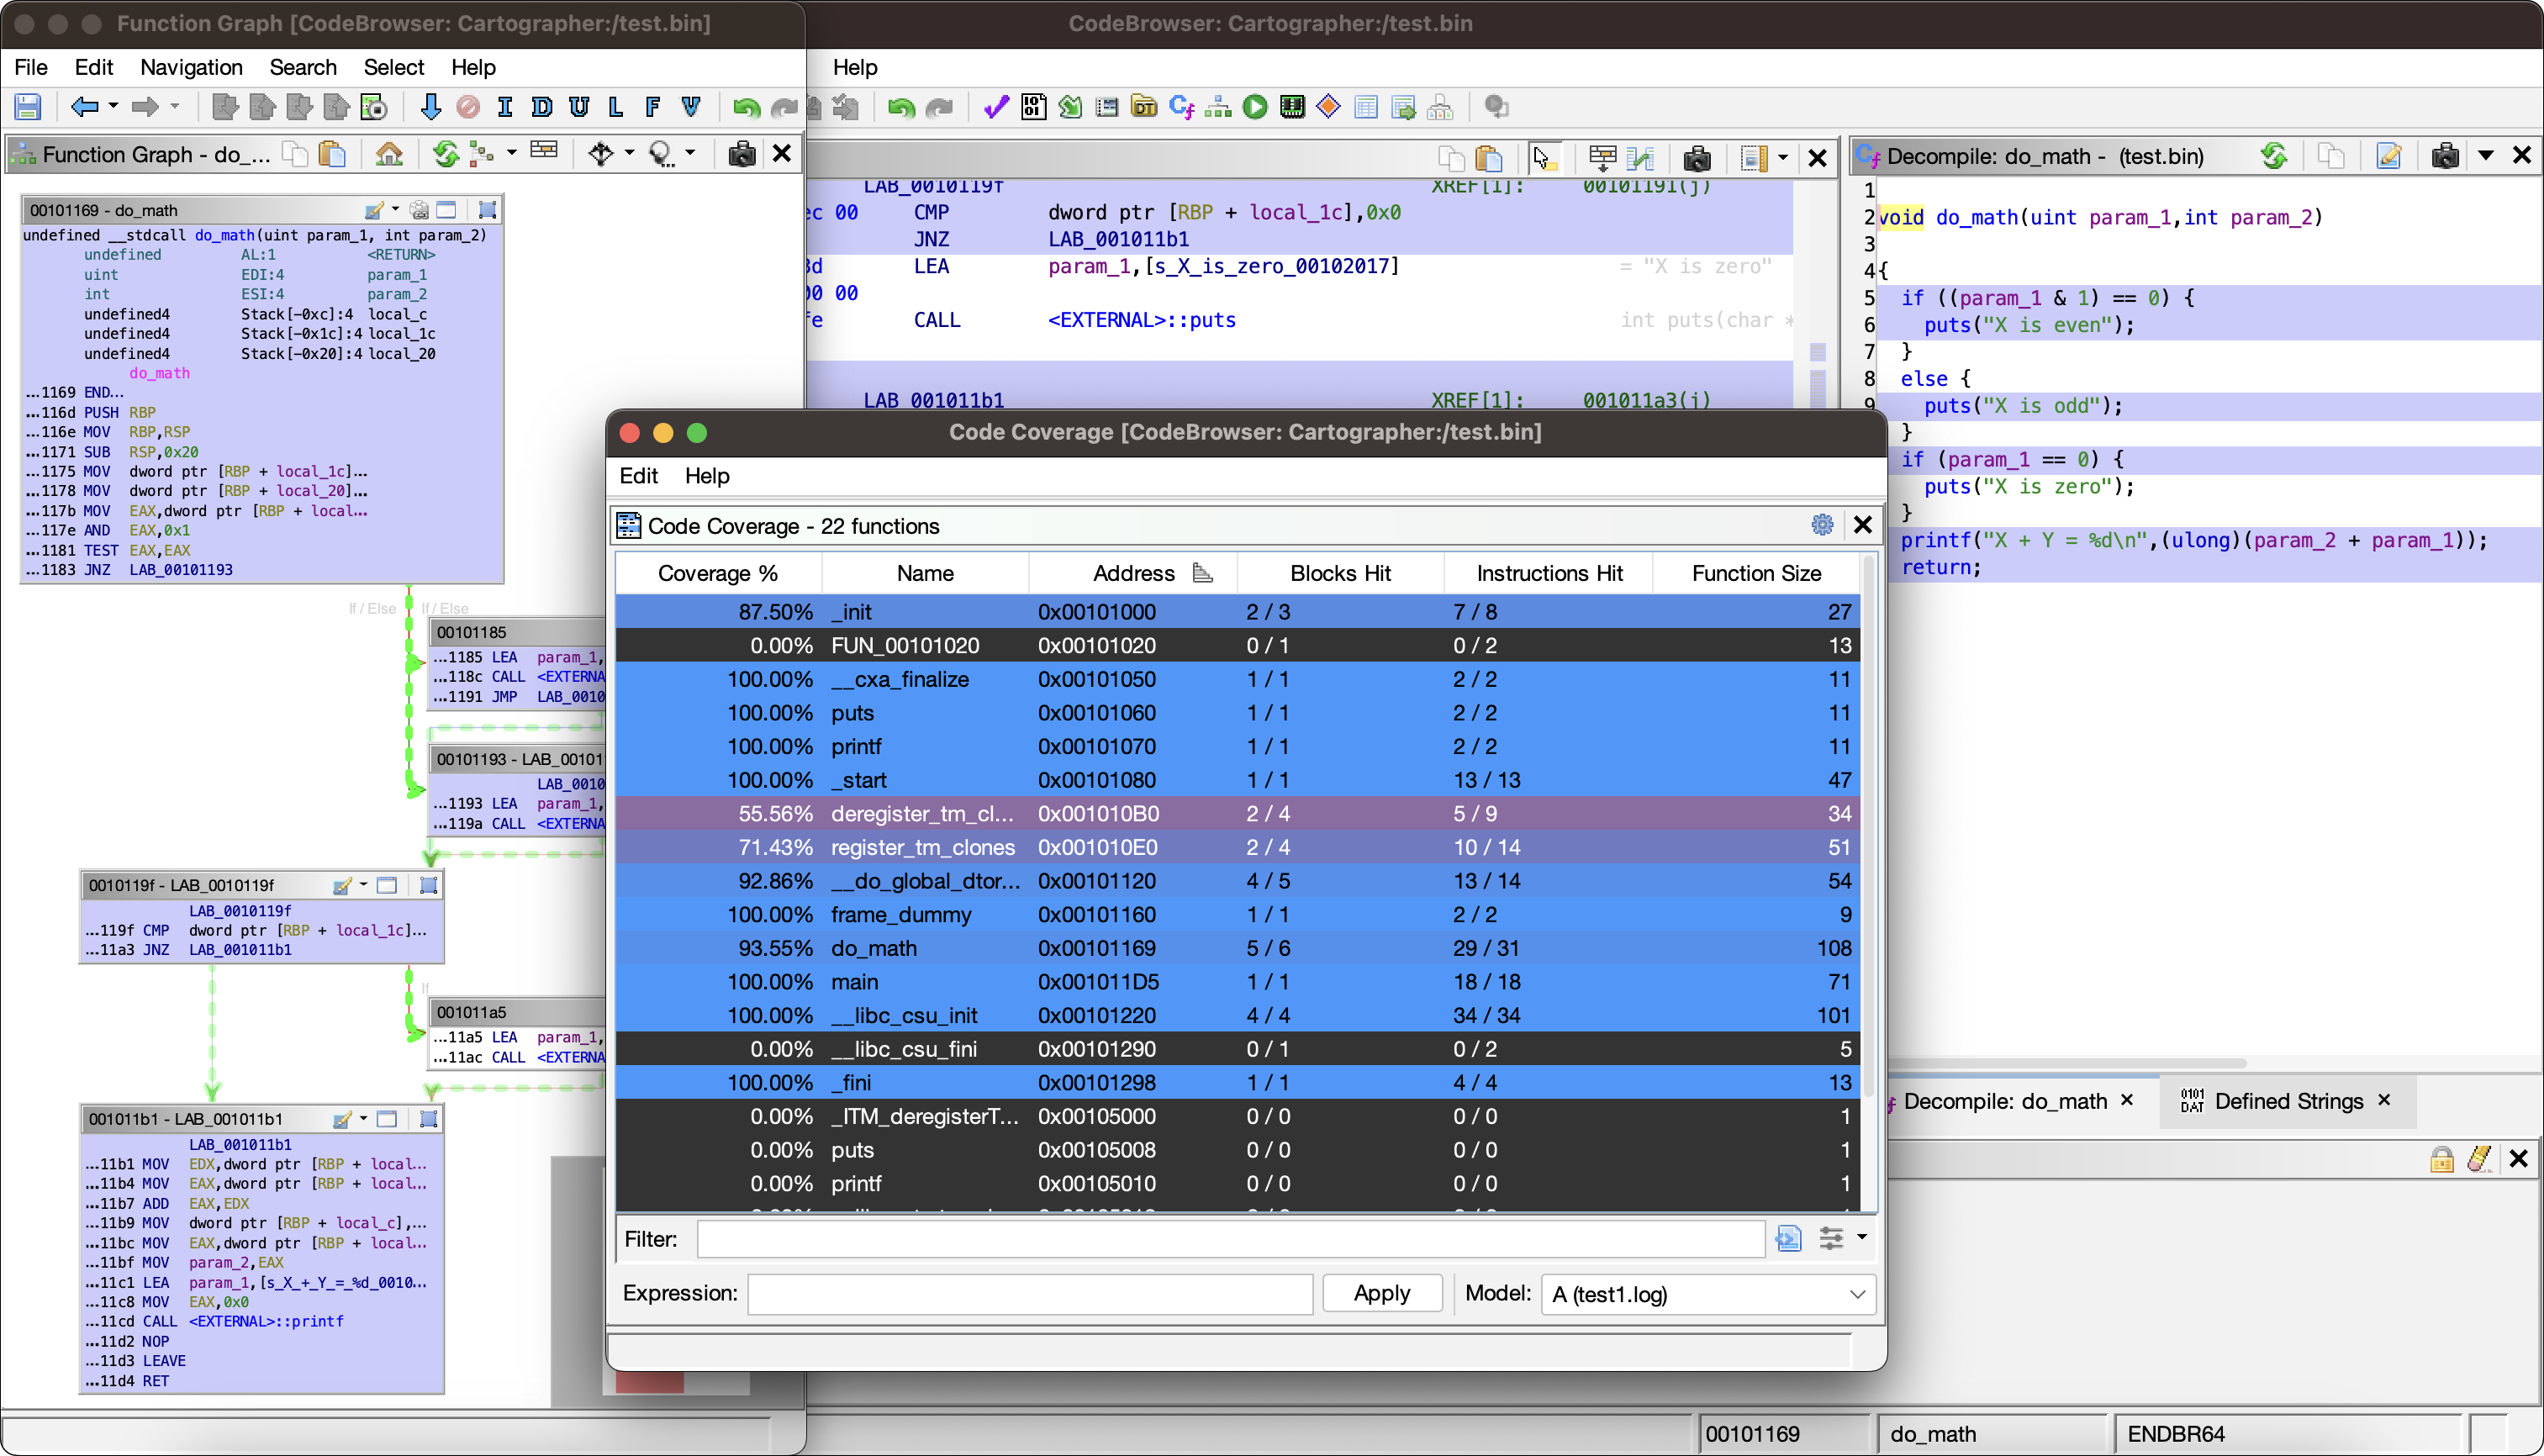 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
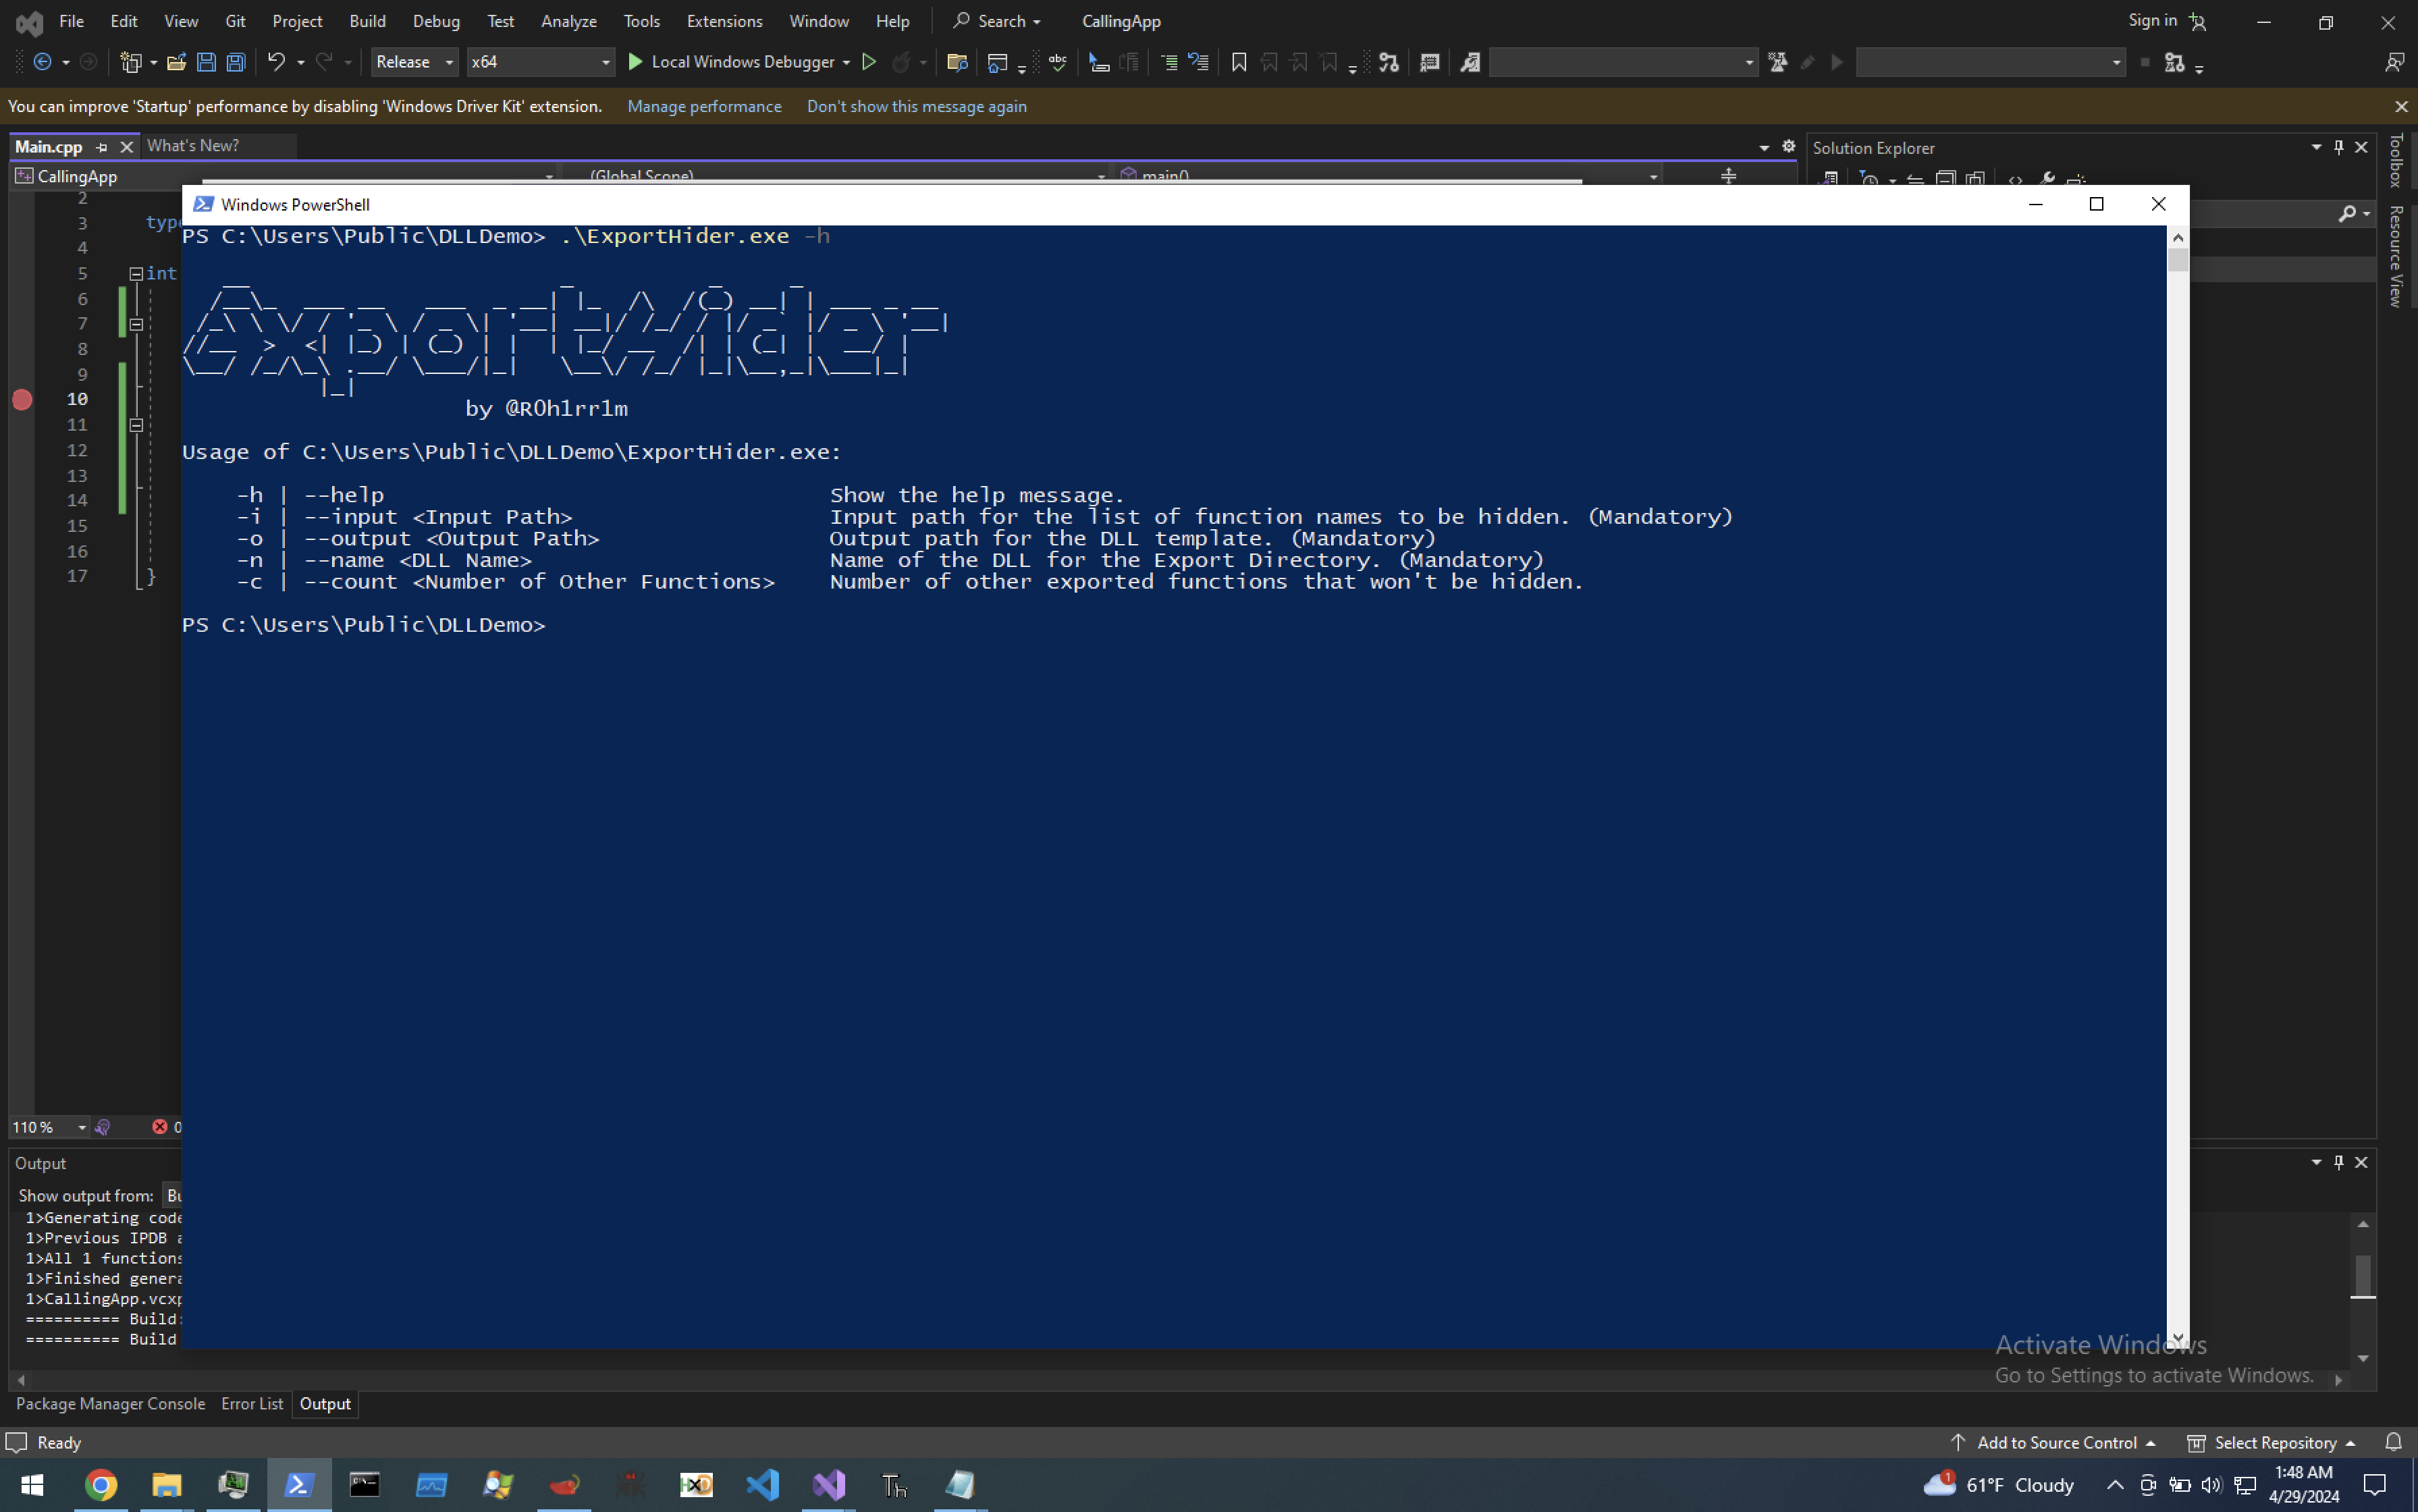 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
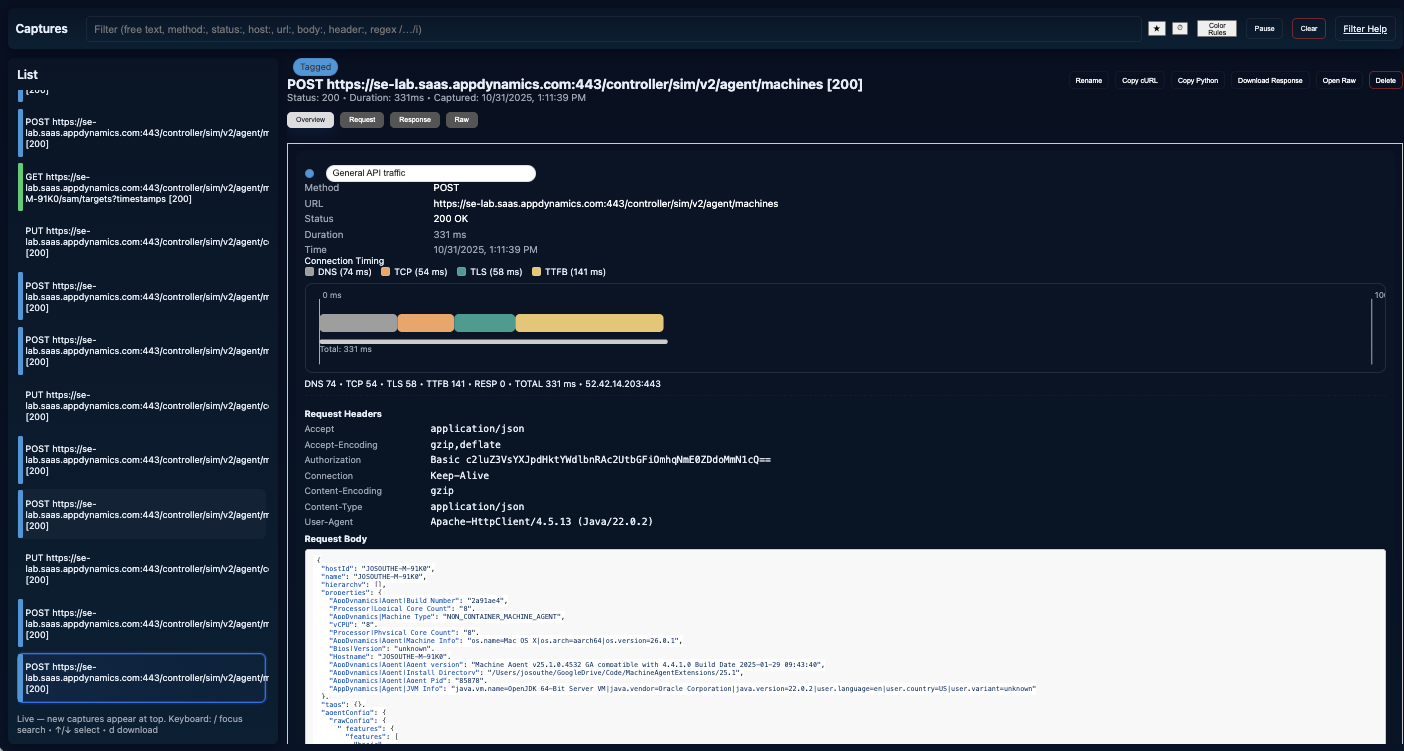 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
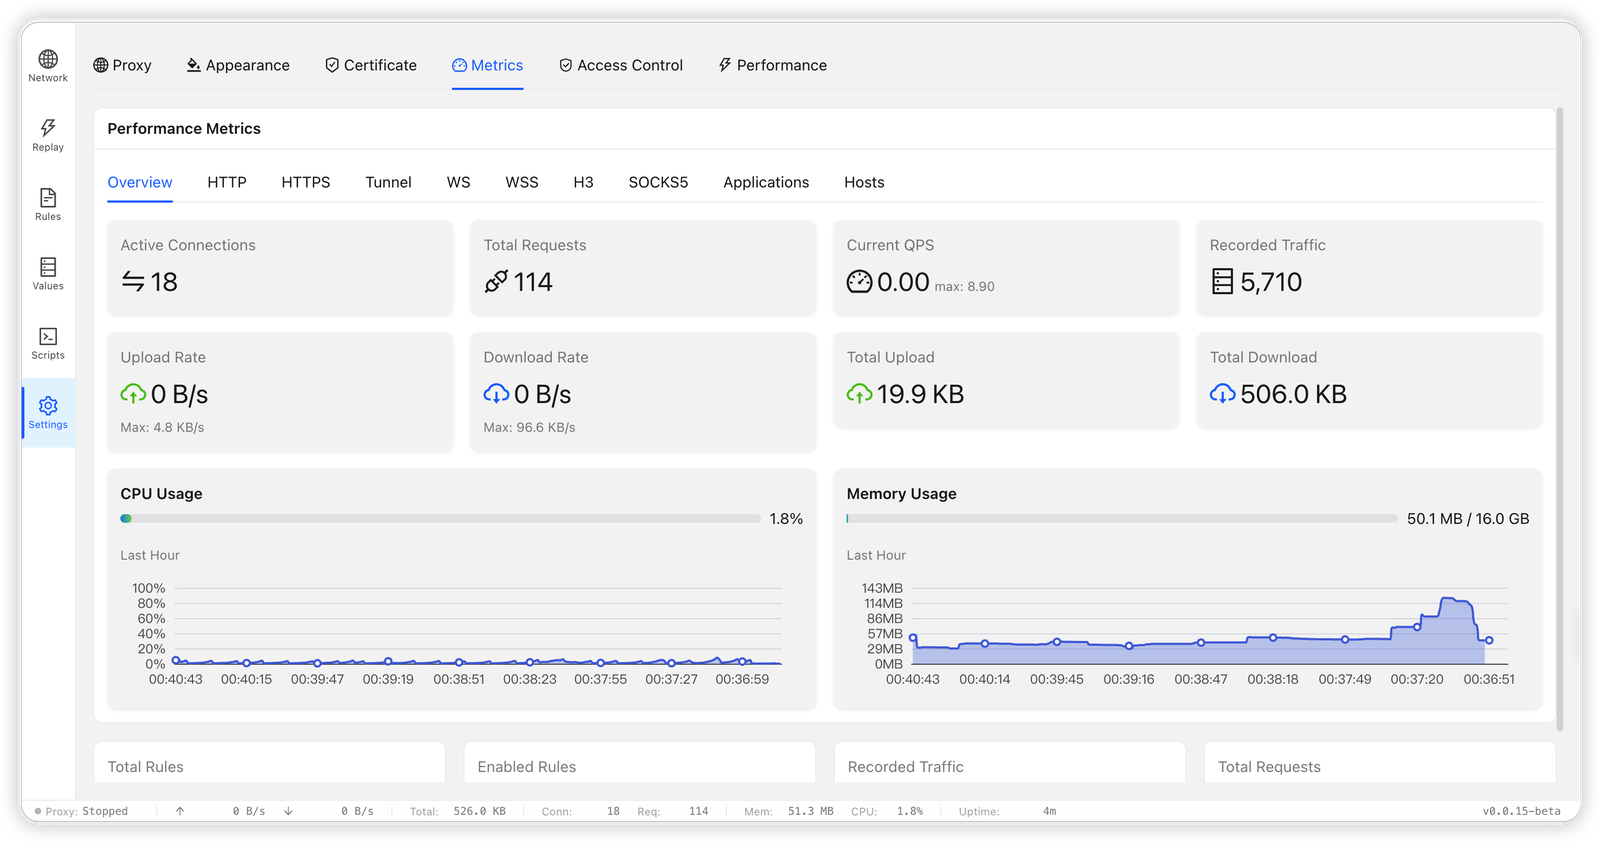 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…