

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
29 results
SuperGhidra preview

SuperGhidra

GitHubyuatemycat/superghidra

Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
ai-assisted-reversingandroid-securitybinary-analysis+8
180
11h 51m ago
awesome-android-security preview

awesome-android-security

GitHubsaeidshirazi/awesome-android-security

A curated list of Android Security materials and resources For Pentesters and Bug Hunters
android-securitycurated-resourceseducation+6
2.0k2 days ago
bifrost preview

bifrost

GitHubbifrost-proxy/bifrost

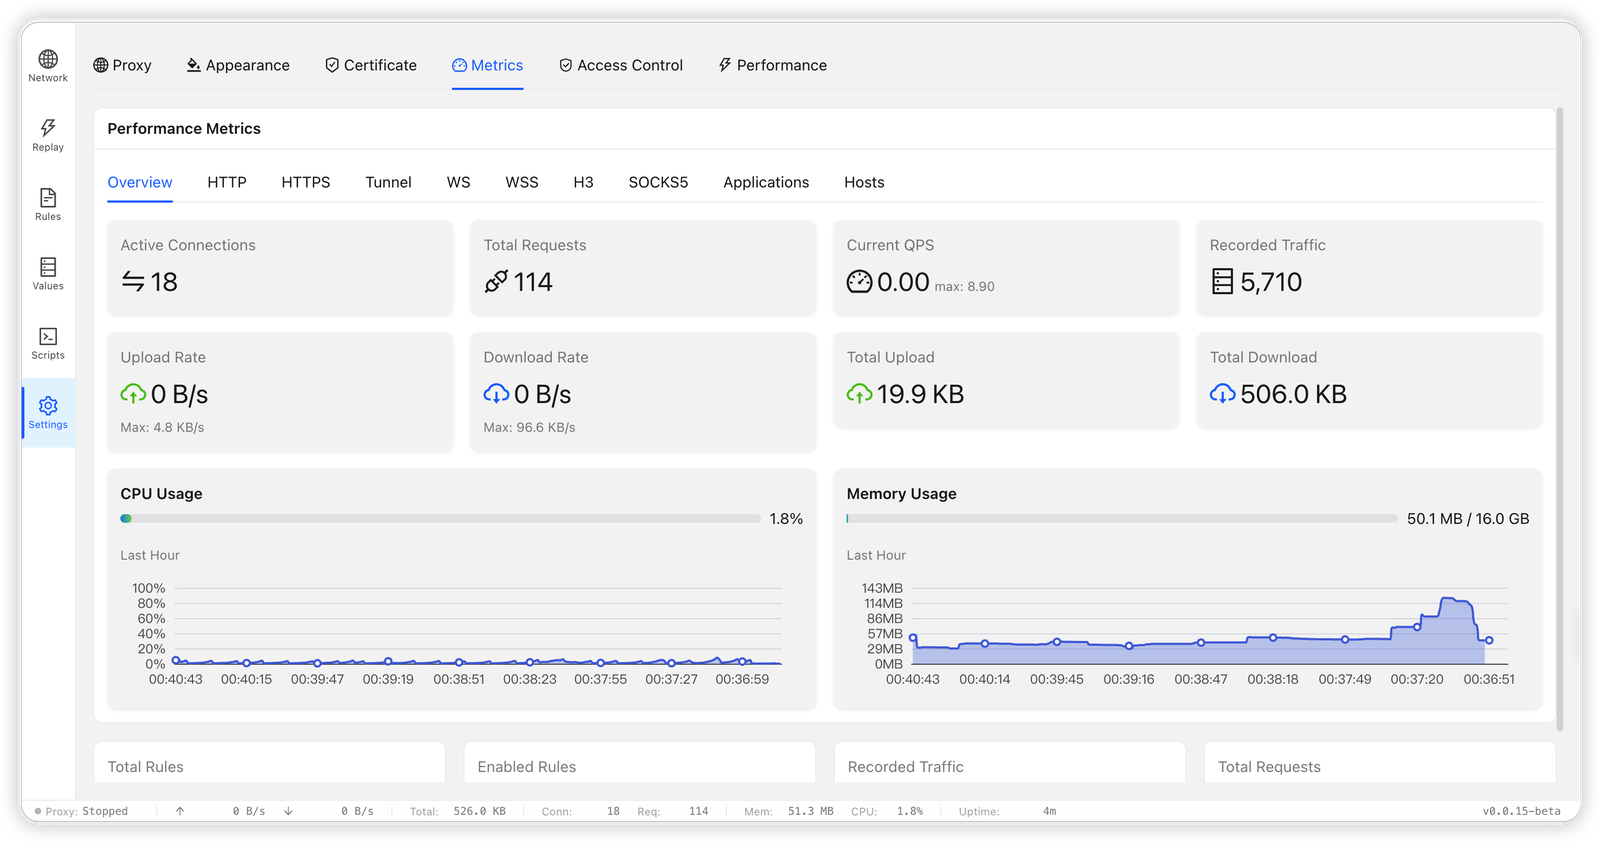
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
api-security-testingnetwork-securitypacket-sniffing-analysis+6
1672 days ago
grapefruit preview

grapefruit

GitHubchichou/grapefruit

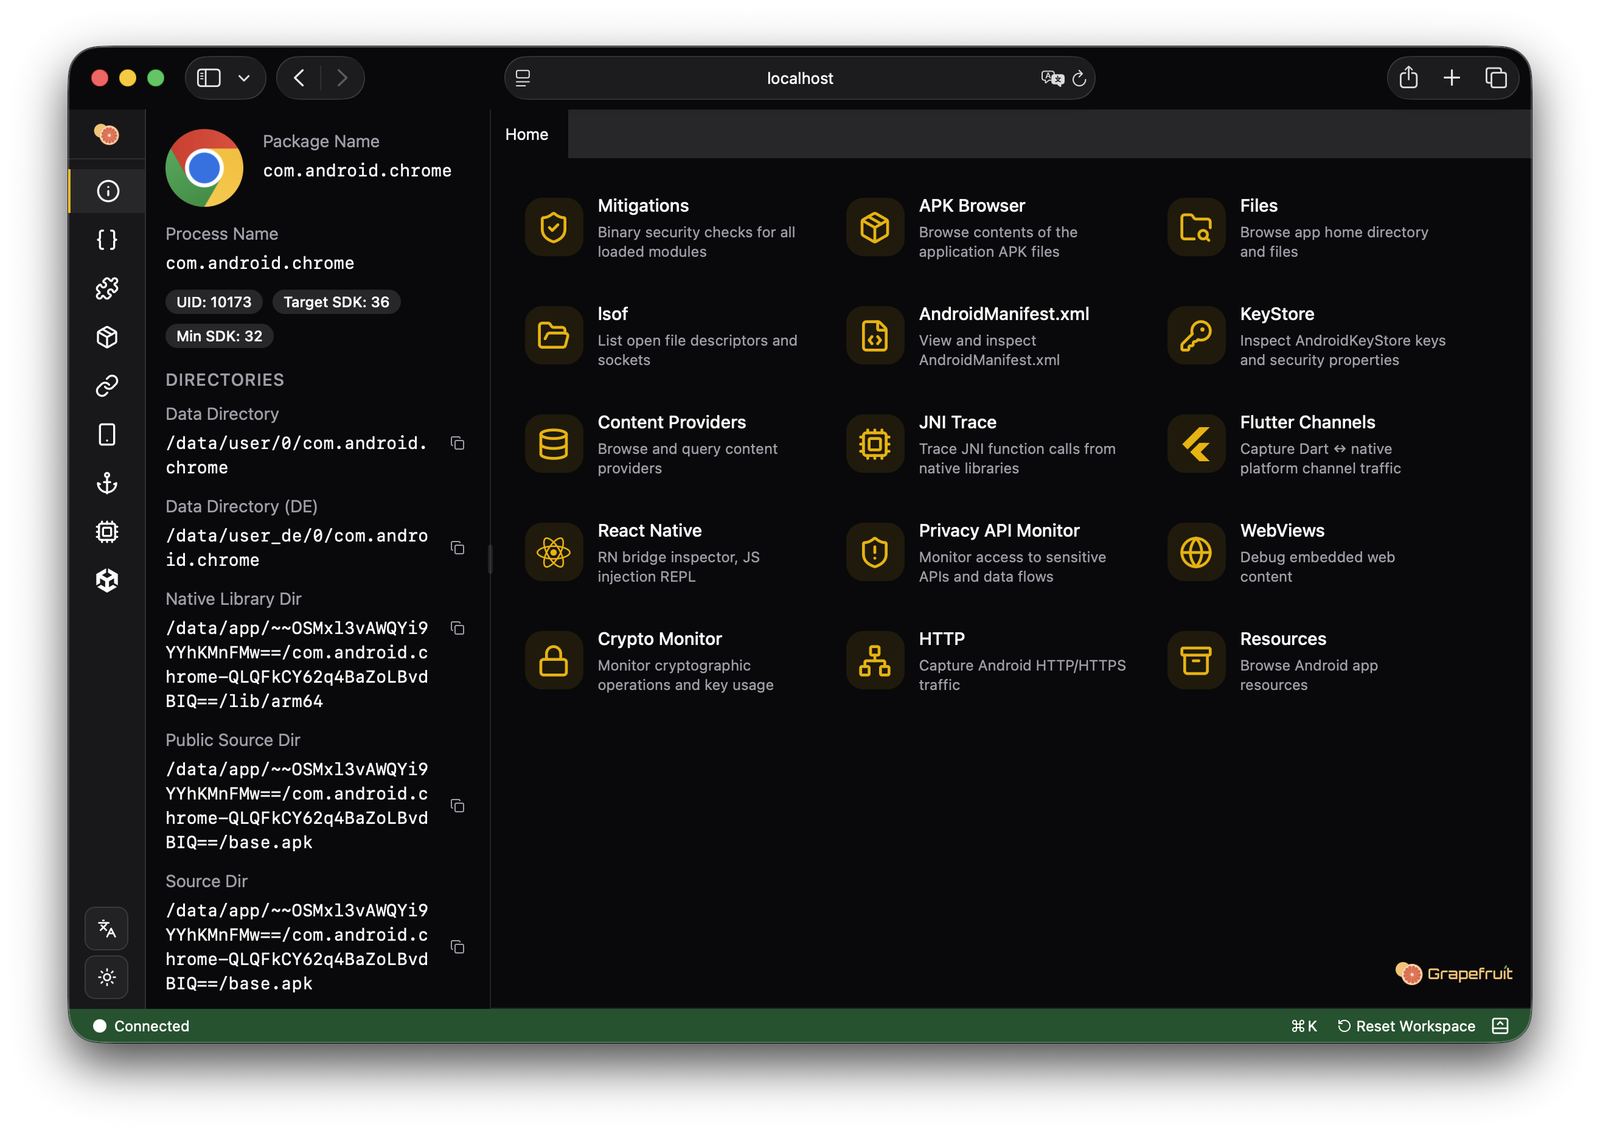
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
android-securitybinary-analysisdynamic-code-analysis+5
1.4k5 days ago
malware-research preview

malware-research

GitHubeset/malware-research

Code written as part of our various malware investigations
digital-forensicsdynamic-code-analysismalware-analysis+4
41723 days ago
fnprint preview

fnprint

GitHub1rhino2/fnprint

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
binary-analysisdynamic-code-analysisfirmware-analysis+3
5724 days ago
javascript-deobfuscator preview

javascript-deobfuscator

GitHublolcaken/javascript-deobfuscator

Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
code-analysisdynamic-code-analysismalware-analysis+4
826 days ago
ifuncd-up preview

ifuncd-up

GitHubrobertdfrench/ifuncd-up

GNU IFUNC is the real culprit behind CVE-2024-3094
binary-analysisdynamic-code-analysiseducation+5
601 month ago
NtTrace preview

NtTrace

GitHubrogerorr/nttrace

An strace-like program for the Windows 'native' API
api-security-testingdebuggersdynamic-code-analysis+2
3881 month ago
recaptcha preview

recaptcha

GitHubelyelysiox/recaptcha

Documentation and reverse engineering of reCAPTCHA

anti-botcaptcha-bypassdynamic-code-analysis+3
2274 months ago
apiscope preview

apiscope

GitHubkaisonox/apiscope

An API hooking framework for intercepting and monitoring Windows applications
api-security-testingbinary-analysisdebuggers+4
204 months ago
web3-decoder preview

web3-decoder

GitHubnccgroup/web3-decoder

Burp Suite extension for decoding Web3 JSON-RPC traffic, including smart contract function calls, responses, and ABI resolution with proxy-aware and…

api-securityinformation-gatheringpenetration-testing+3
1155 months ago
polytracker preview

polytracker

GitHubtrailofbits/polytracker

An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
binary-analysisdynamic-code-analysiseducation+4
6015 months ago
matrix-rs preview
Archived

matrix-rs

GitHubmemn0ps/matrix-rs

Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
dynamic-code-analysiseducationids-ips-evasion+3
3565 months ago
ExportHider preview

ExportHider

GitHubfrkngksl/exporthider

ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.

binary-analysisdynamic-code-analysisexploitation+4
336 months ago
maps_scanner preview

maps_scanner

GitHubhackinglz/maps_scanner

MAPS cloud scanner and response parser for Microsoft Defender research.
api-security-testingdynamic-analysis-sandboxingfuzzing+6
948 months ago
ghidra_stack_strings preview

ghidra_stack_strings

GitHubzxgio/ghidra_stack_strings

A script to detect stack-strings by using emulation (leveraging Unicorn)
binary-analysisdynamic-code-analysismalware-analysis+1
3511 months ago
Log4Shell-CVE-2021-44228 preview

Log4Shell-CVE-2021-44228

GitHubdrhaitham/log4shell-cve-2021-44228

Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…

command-and-controleducationexploitation+7
11 months ago
Previous12Next