

capstone
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
ai-assisted-reversingbinary-analysisbinary-exploitation+7
9.0k
capstone-engine/capstoneMulti-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 prox0959/trueverdict
Zero-dependency Windows PE provenance and false-positive reduction engine (Embedded Authenticode + OS Security Catalogs, Rich Header ROL32…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 exifdev/prineo_re
Reverse engineering of the engine powering the PriPara games on arcade.
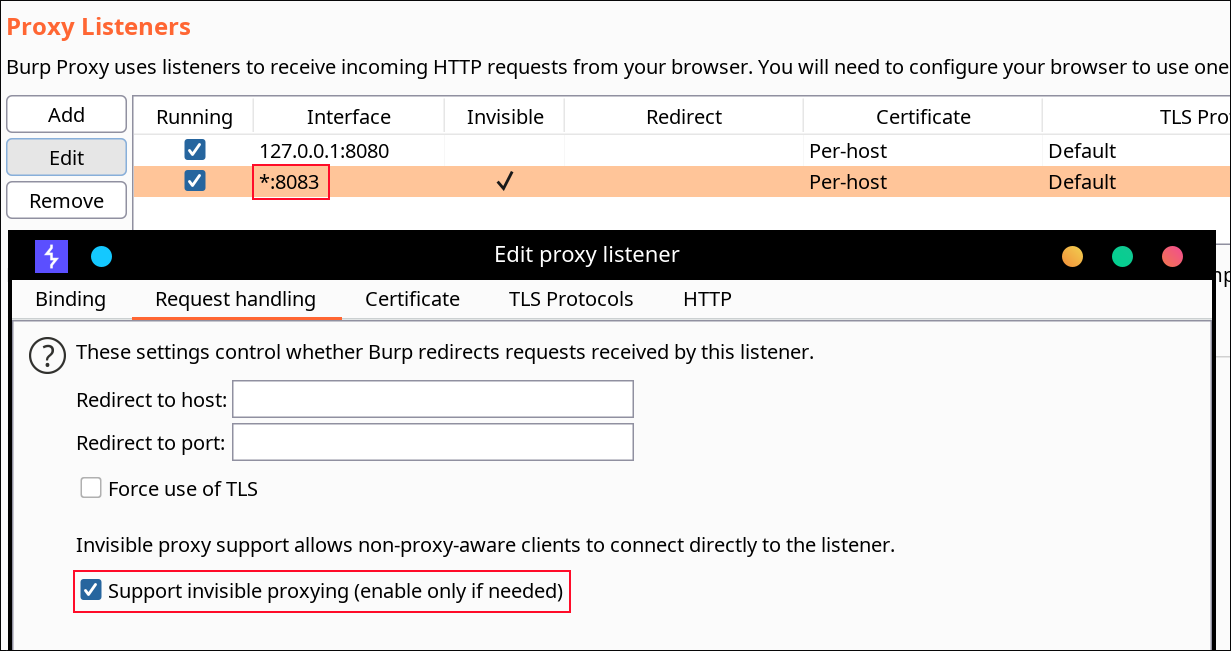 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
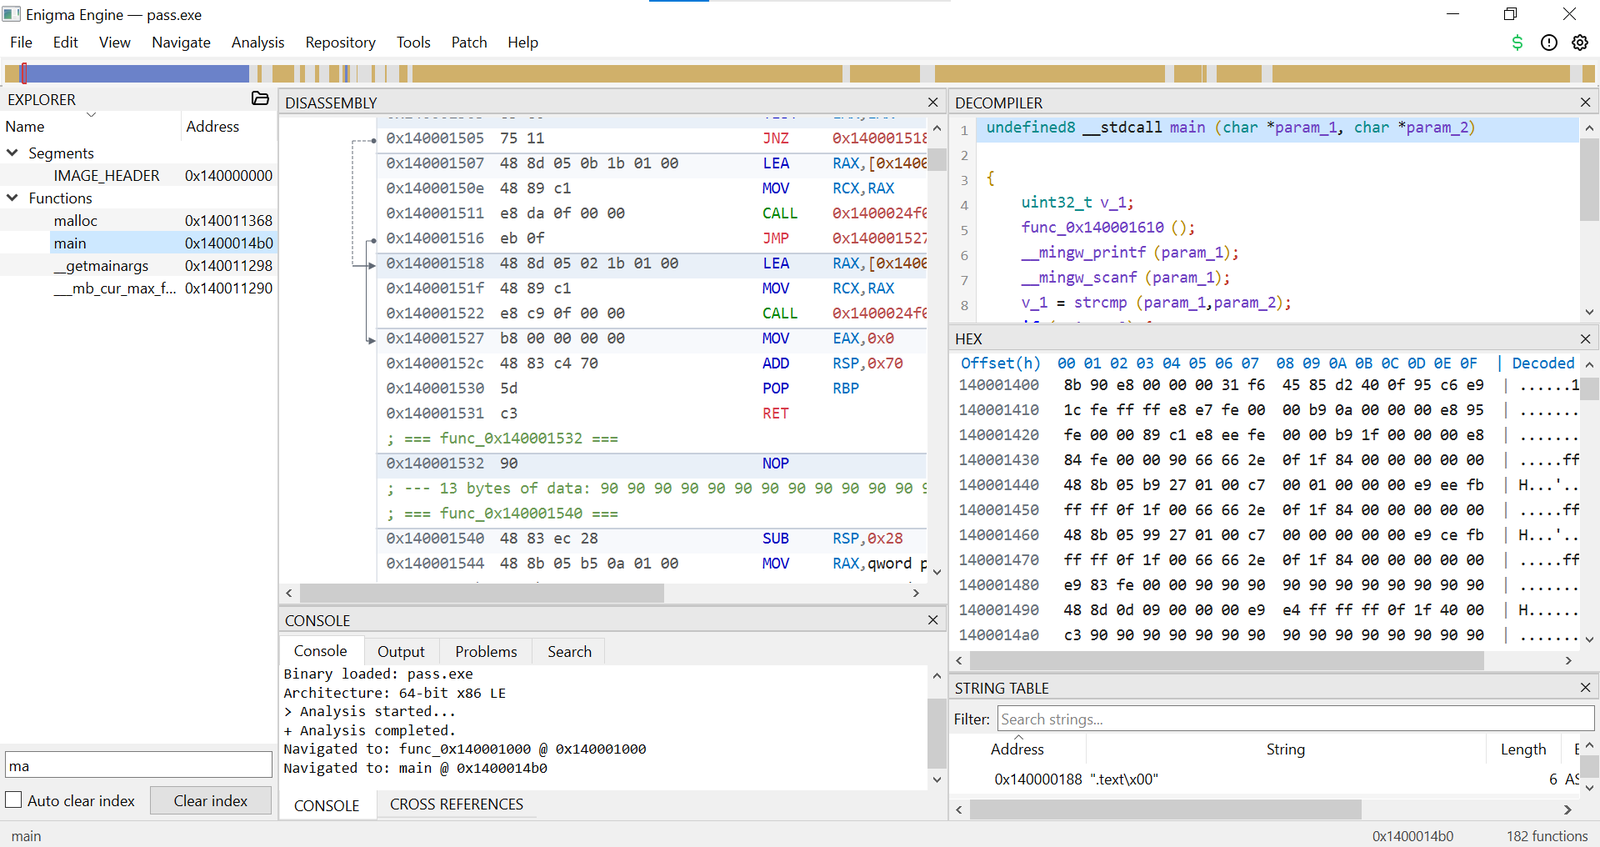 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
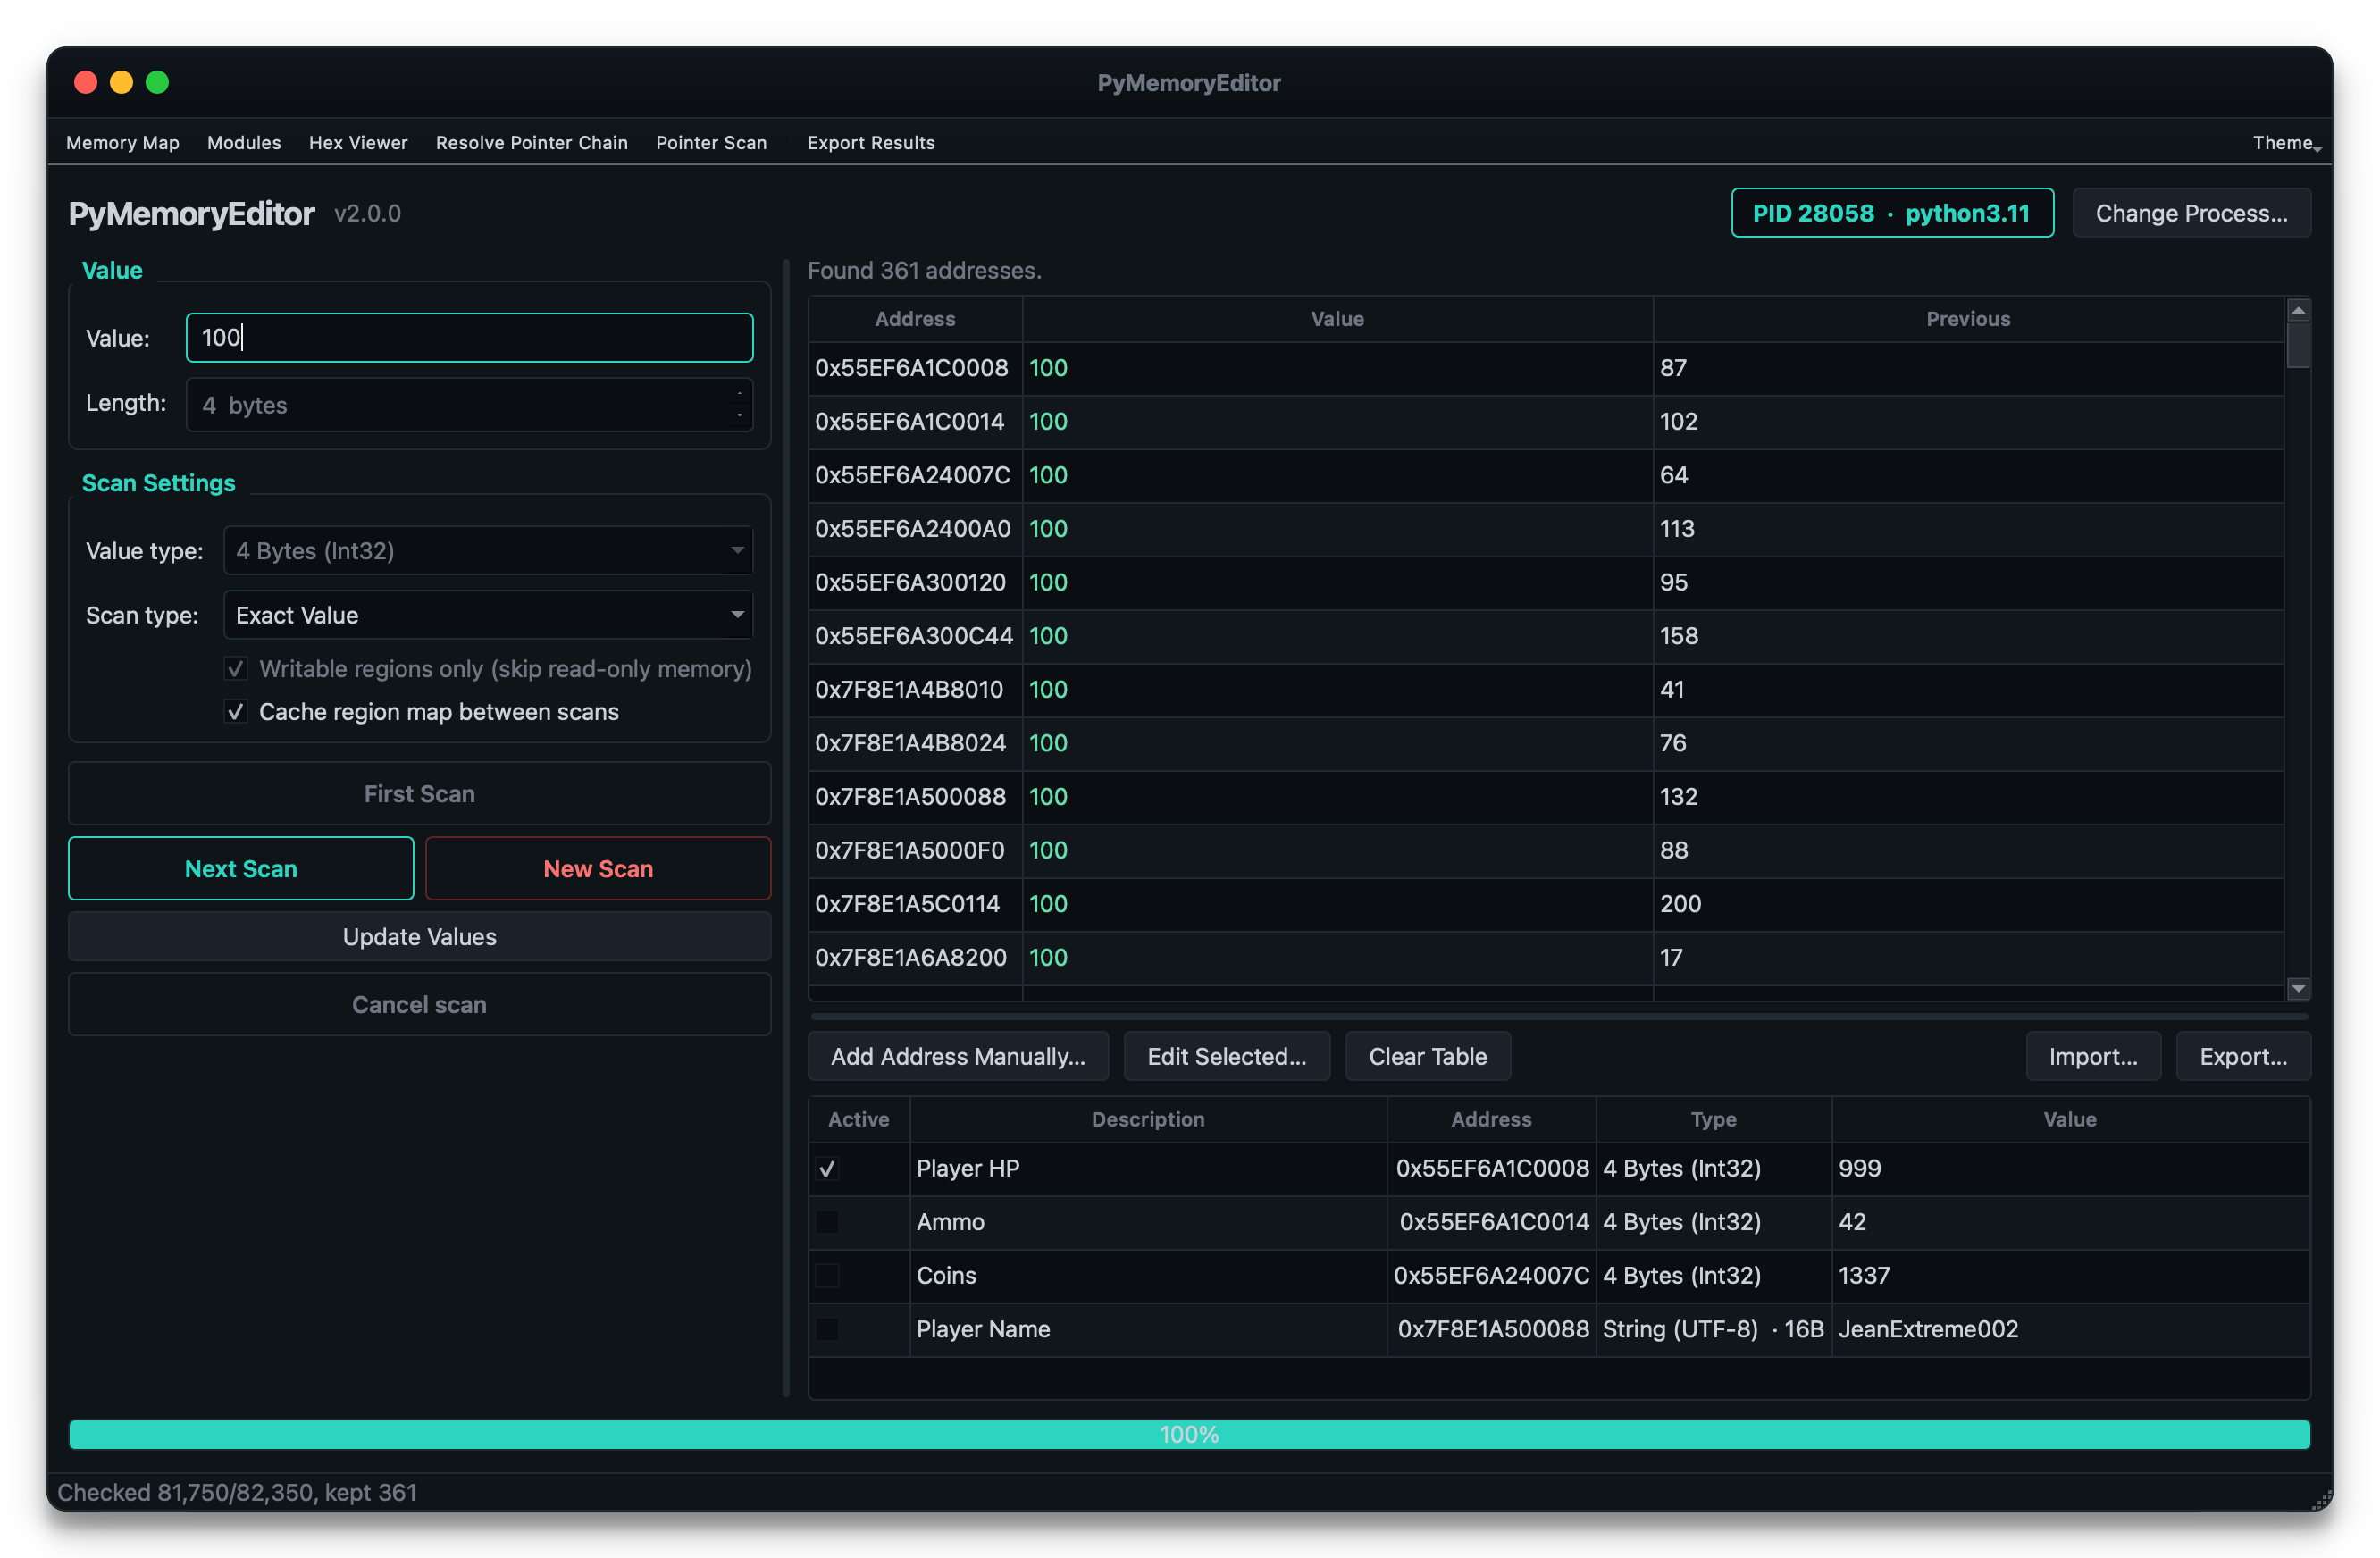 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 vxlang/vxlang-page
Code obfuscation, virtualization, and anti-tamper protector for x86-64 Windows binaries (EXE/DLL/SYS) and .NET modules, with beta ELF support.…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 misterdengi/cve-2026-1801c
Static reverse-engineering analysis of movement input heuristics in Source 2 engine, identifying structural edge cases in input automation and jump…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
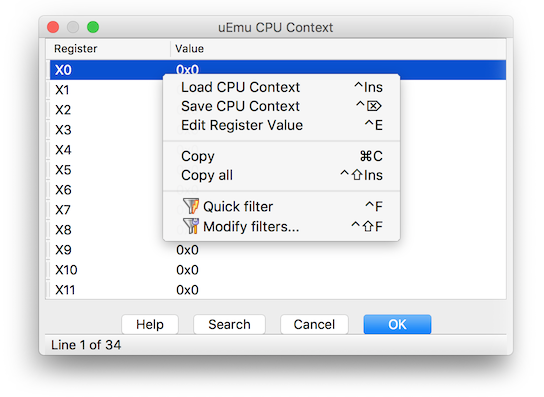 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.