
awesome-blackhat-arsenal
 elbraino/awesome-blackhat-arsenal
Curated collection of cybersecurity tools featured in Black Hat Arsenal events.
curated-resourcesdefensive-toolsinformation-gathering+8
192
elbraino/awesome-blackhat-arsenalCurated collection of cybersecurity tools featured in Black Hat Arsenal events.
 jankammerath/bogusmips
Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
 bb1nfosec/information-security-tasks
Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
 s12cybersecurity/whatpatchguardprotects
Reference of all kernel structures, routines, and MSRs monitored by PatchGuard (KPP) on Windows.
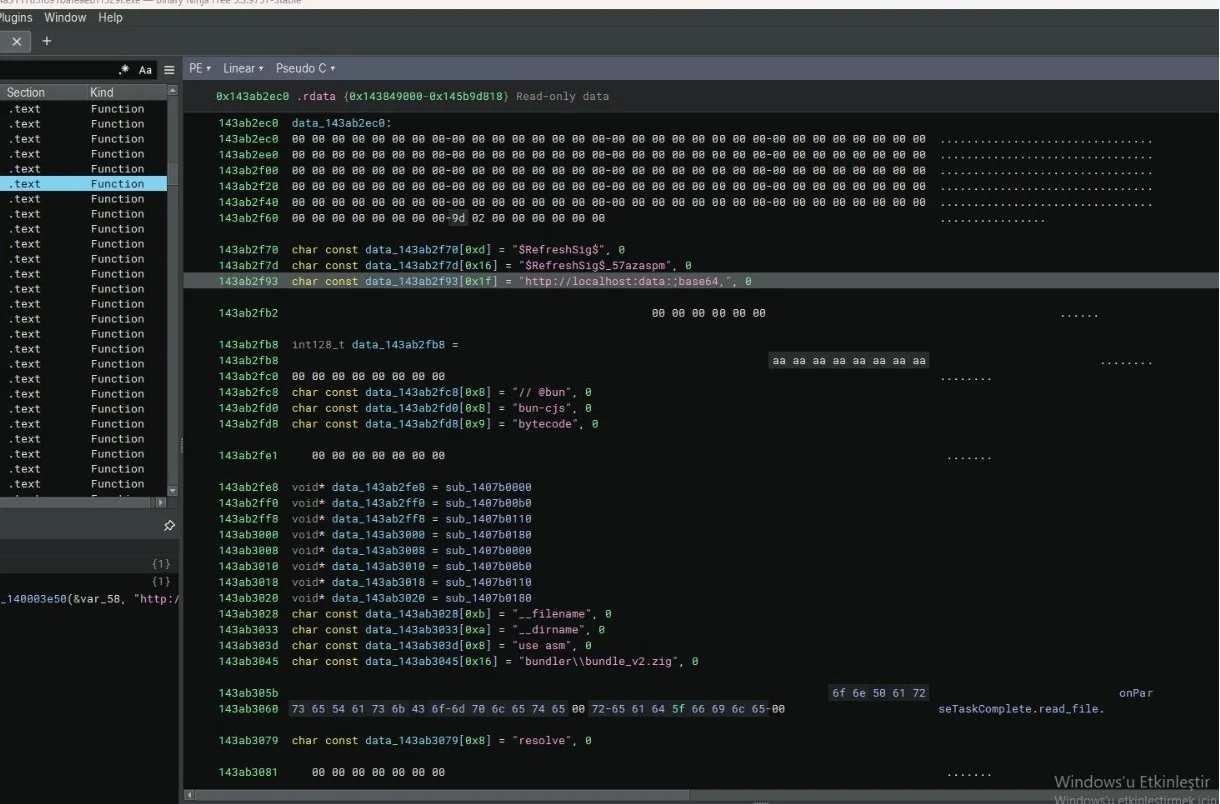 kaandemir993/nwh-stealer-analysis-fileless-bun-runtime-execution-clipboard-image-theft-cloud-c2-aws-r2-
Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…
 1llu50ry/aegis
Single-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
 hunterdii/tryhackme-roadmap
Hello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
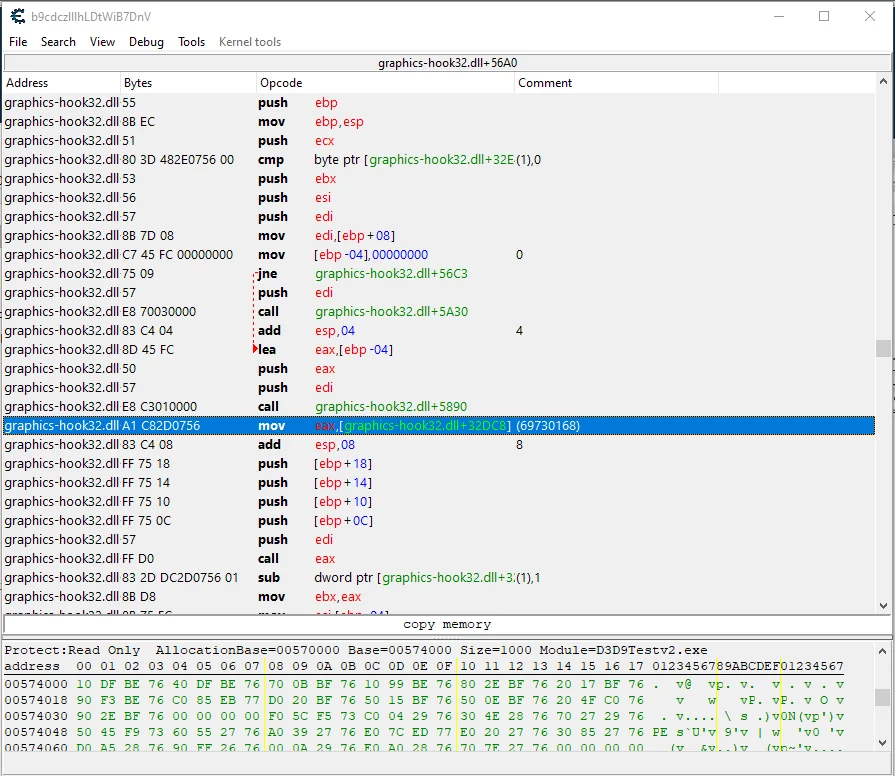 gmh5225/obs-graphics-hook32-hook
Demonstrates hooking OBS graphics-hook32.dll's D3D9 Present pointer to achieve stream-proof rendering that evades anti-cheat game capture detection.
 gmh5225/ollytlscatch
OllyDbg plugin that intercepts and dumps TLS/SSL plaintext traffic during debugging sessions, aiding reverse engineering and malware analysis of…
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 gmh5225/no-access-protection-x86
It encrypts the text section and set the protection to NO_ACCESS.
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 gmh5225/memory-relocalloc
C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…