

CVE-2026-124020
 llcforge/cve-2026-124020
Python PoC for CVE-2026-124020: Control Web Panel < 1.30.6 host header password-reset poisoning, recovery code capture, account takeover and RCE via…
exploitationinformation-gatheringpassword-attacks+6
llcforge/cve-2026-124020Python PoC for CVE-2026-124020: Control Web Panel < 1.30.6 host header password-reset poisoning, recovery code capture, account takeover and RCE via…
 tempiltin/duplicate2shell-cve-2026-123751
Python PoC for CVE-2026-123751: exploits an unauthenticated file upload in the WP Duplicate WordPress plugin to deploy a PHP webshell, with version…
 im0xfay/cve-2026-124990
PoC and Docker lab for CVE-2026-124990: unauthenticated PHP object injection in Masteriyo LMS <= 3.5.1 leading to file write and RCE, with payload…
 cuttlefish520/fastjson1.2.83-genprobe2
CVE-2026-16723 reproduction toolkit - fastjson 1.2.83 jar: remote class-loading payload generator (ASM-built POC.class with @JSONType + clinit exec)
 jamir0quai/cve-2026-16444
Technical write-up of CVE-2026-16444, a path traversal in TeamViewer Classical File Transfer that lets a controlled endpoint write arbitrary files on…
 sfewer-r7/cve-2026-123007
Proof-of-concept scripts for CVE-2026-123007, an NGINX HTTP/2 integer underflow, including a minimal trigger and an exploit demonstrating…
 ashrafzaryouh/cve-2026-21858
Advisory for CVE-2026-21858 ("Ni8mare"), an unauthenticated RCE in n8n workflow automation via webhook Content-Type confusion, with exploitation,…
 maxprog-svg/cve-2026-21509
Exploit toolkit for CVE-2026-21509 Microsoft Office RTF/OLE RCE: builds crafted RTF payloads, serves OLE stage resources, and captures reverse TCP…
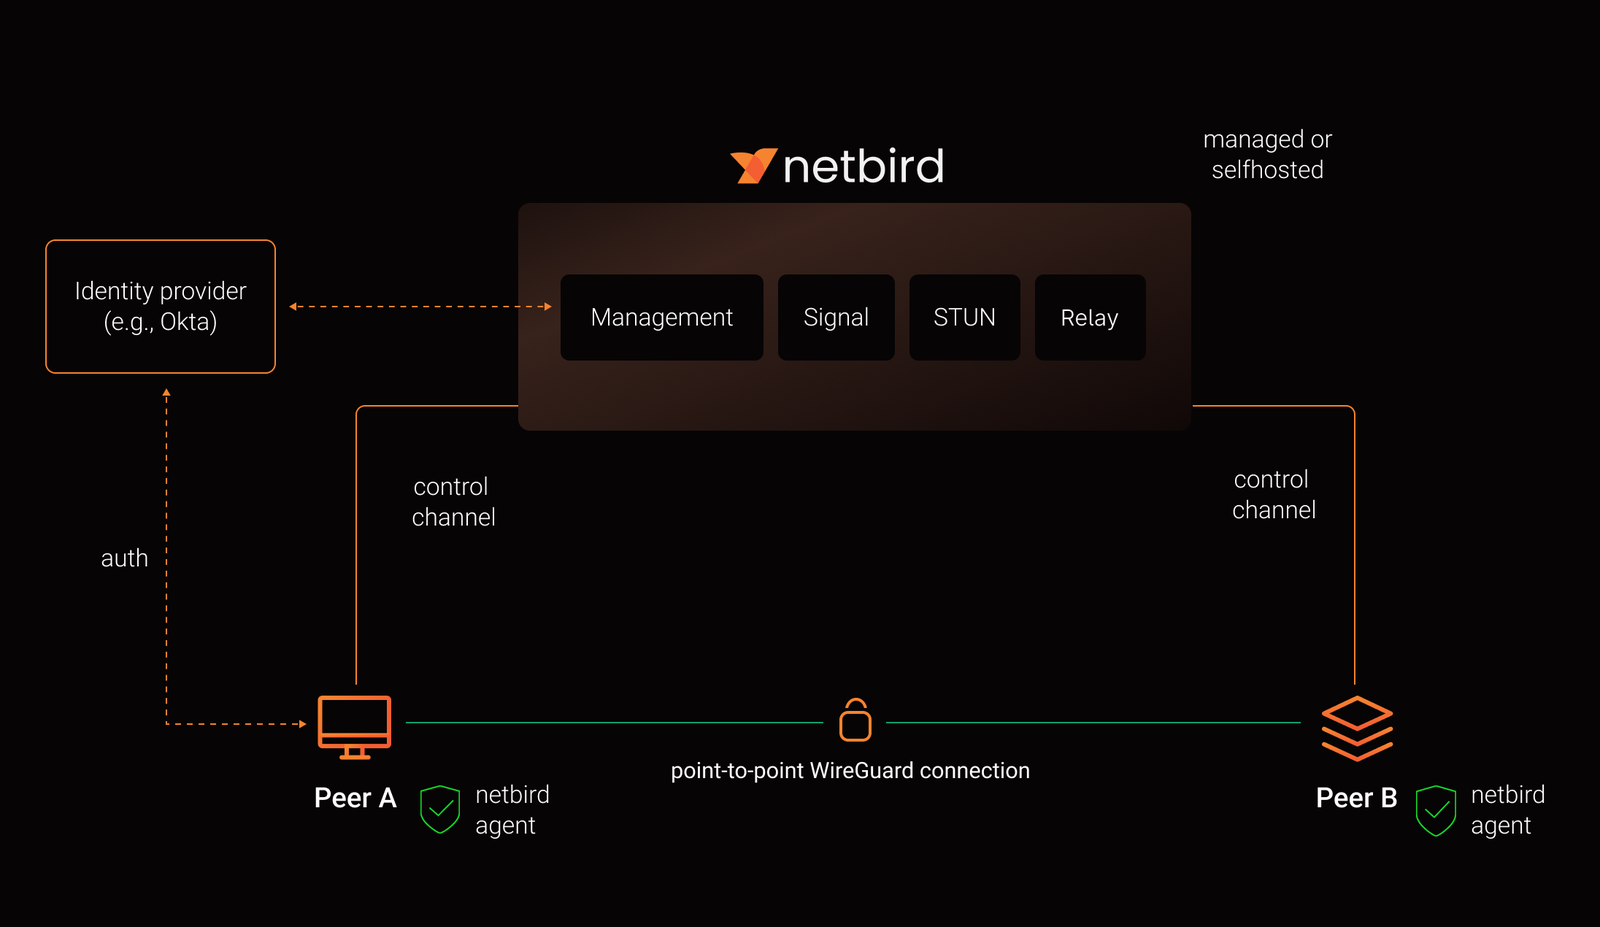 netbirdio/netbird
Identity-based Zero Trust networking platform that builds peer-to-peer WireGuard overlay networks with granular access policies, SSO/MFA, and…
 deathshotxd/sip2shell
One SIP text message to FreeSWITCH, and you are running commands. Exploit, scanner and a real vulnerable/patched Docker lab for CVE-2026-116779.
 racoten/suture-pic
A Windows implant development framework for offensive engineering and C2 research.
 jenderal92/metapwn-mass
CVE-2026-72898 — Mass exploitation & post-exploitation toolkit for Metabase. Session forgery, SQLi, PostgreSQL RCE via COPY TO PROGRAM, file…
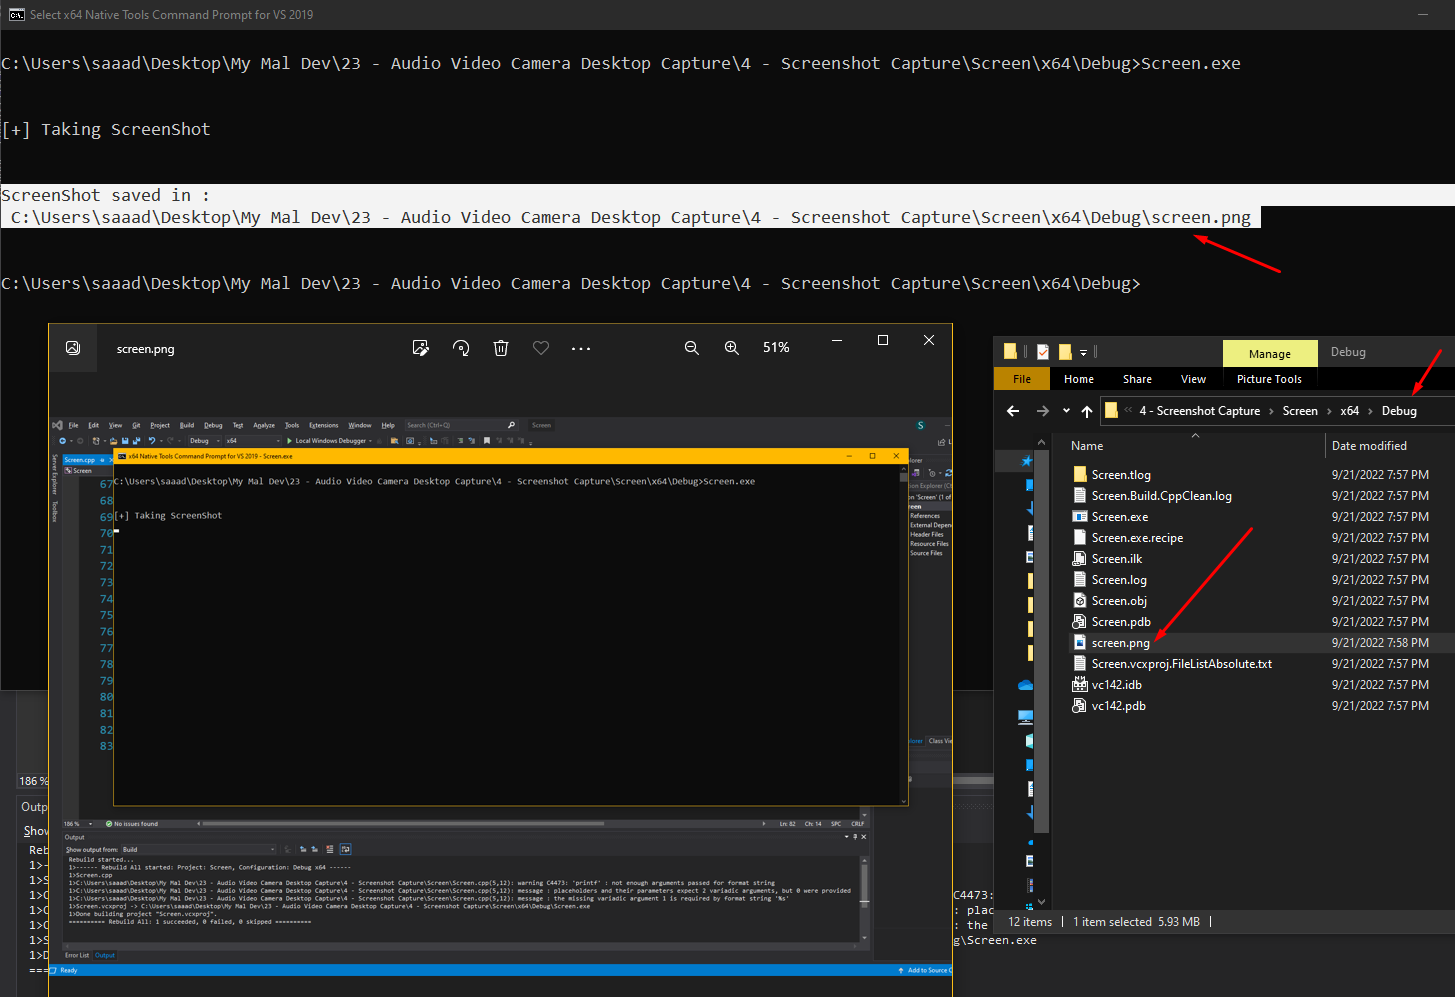 gmh5225/screenshot
C2 post-exploitation module that captures a screenshot of the compromised host's desktop and saves it as screen.png in the current working directory.
 hackerschoice/gsocket
Connect like there is no firewall. Securely.
 dinosn/cve-2026-76466
Python exploit and fleet detector for CVE-2026-76466, an unauthenticated root RCE in clustered Cisco Expressway via hard-coded Erlang distribution…
 ashrafzaryouh/cve-2026-28289
Proof-of-concept exploit and technical write-up for CVE-2026-28289 (Mail2Shell), a zero-click unauthenticated RCE in FreeScout via email attachment…
 shisones/cve-2026-27626
Python proof-of-concept for CVE-2026-27626: discovers OliveTin password-typed arguments, breaks out of sh -c quoting to inject commands, and provides…
 1337or420/cve-2026-33017-langflow-rce
Proof-of-concept exploit for CVE-2026-33017, an unauthenticated RCE in Langflow before 1.9.0 via the build_public_tmp flow API, injecting Python code…