

CVE-2024-29895-CactiRCE-PoC
 stuub/cve-2024-29895-cactirce-poc
CVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds
command-and-controlexploitationpenetration-testing+3
21
stuub/cve-2024-29895-cactirce-pocCVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
 wireghoul/lbmap
Advanced HTTP fingerprinting PoC
 ovotech/domain-protect
Automated detection of vulnerable domain configurations and subdomain takeover risks across cloud environments, with continuous monitoring and…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
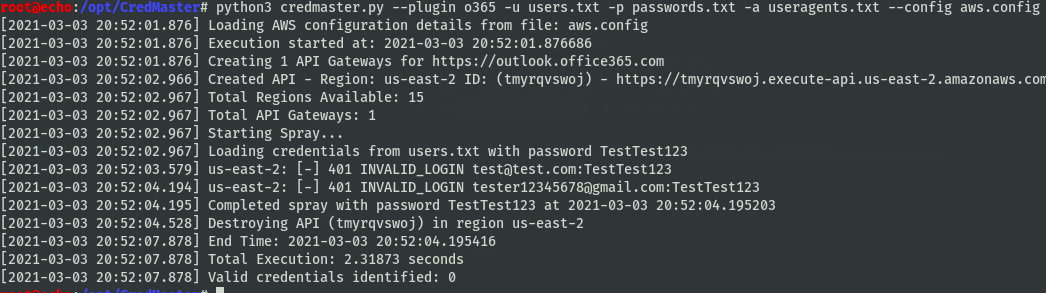 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 projectdiscovery/chaos-client
Go client to communicate with Chaos DB API.
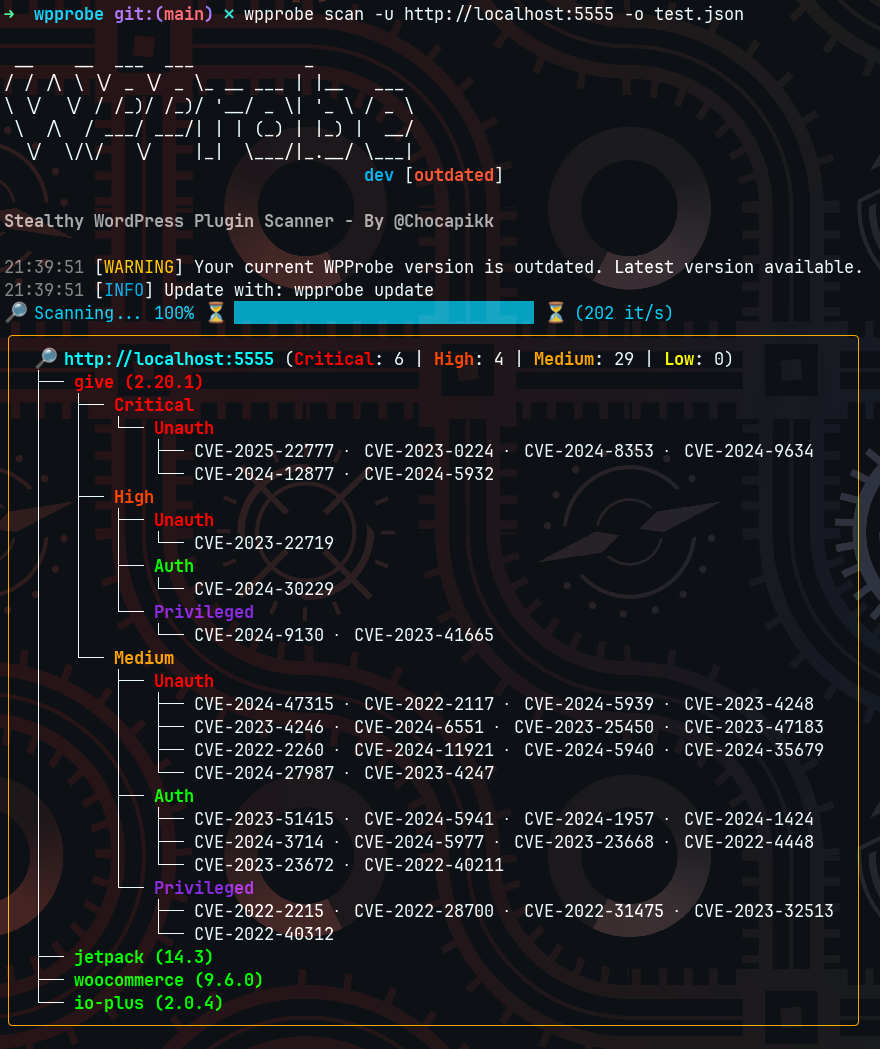 chocapikk/wpprobe
A fast WordPress plugin enumeration tool
 saffron-health/libretto
The AI toolkit for building reliable browser automations
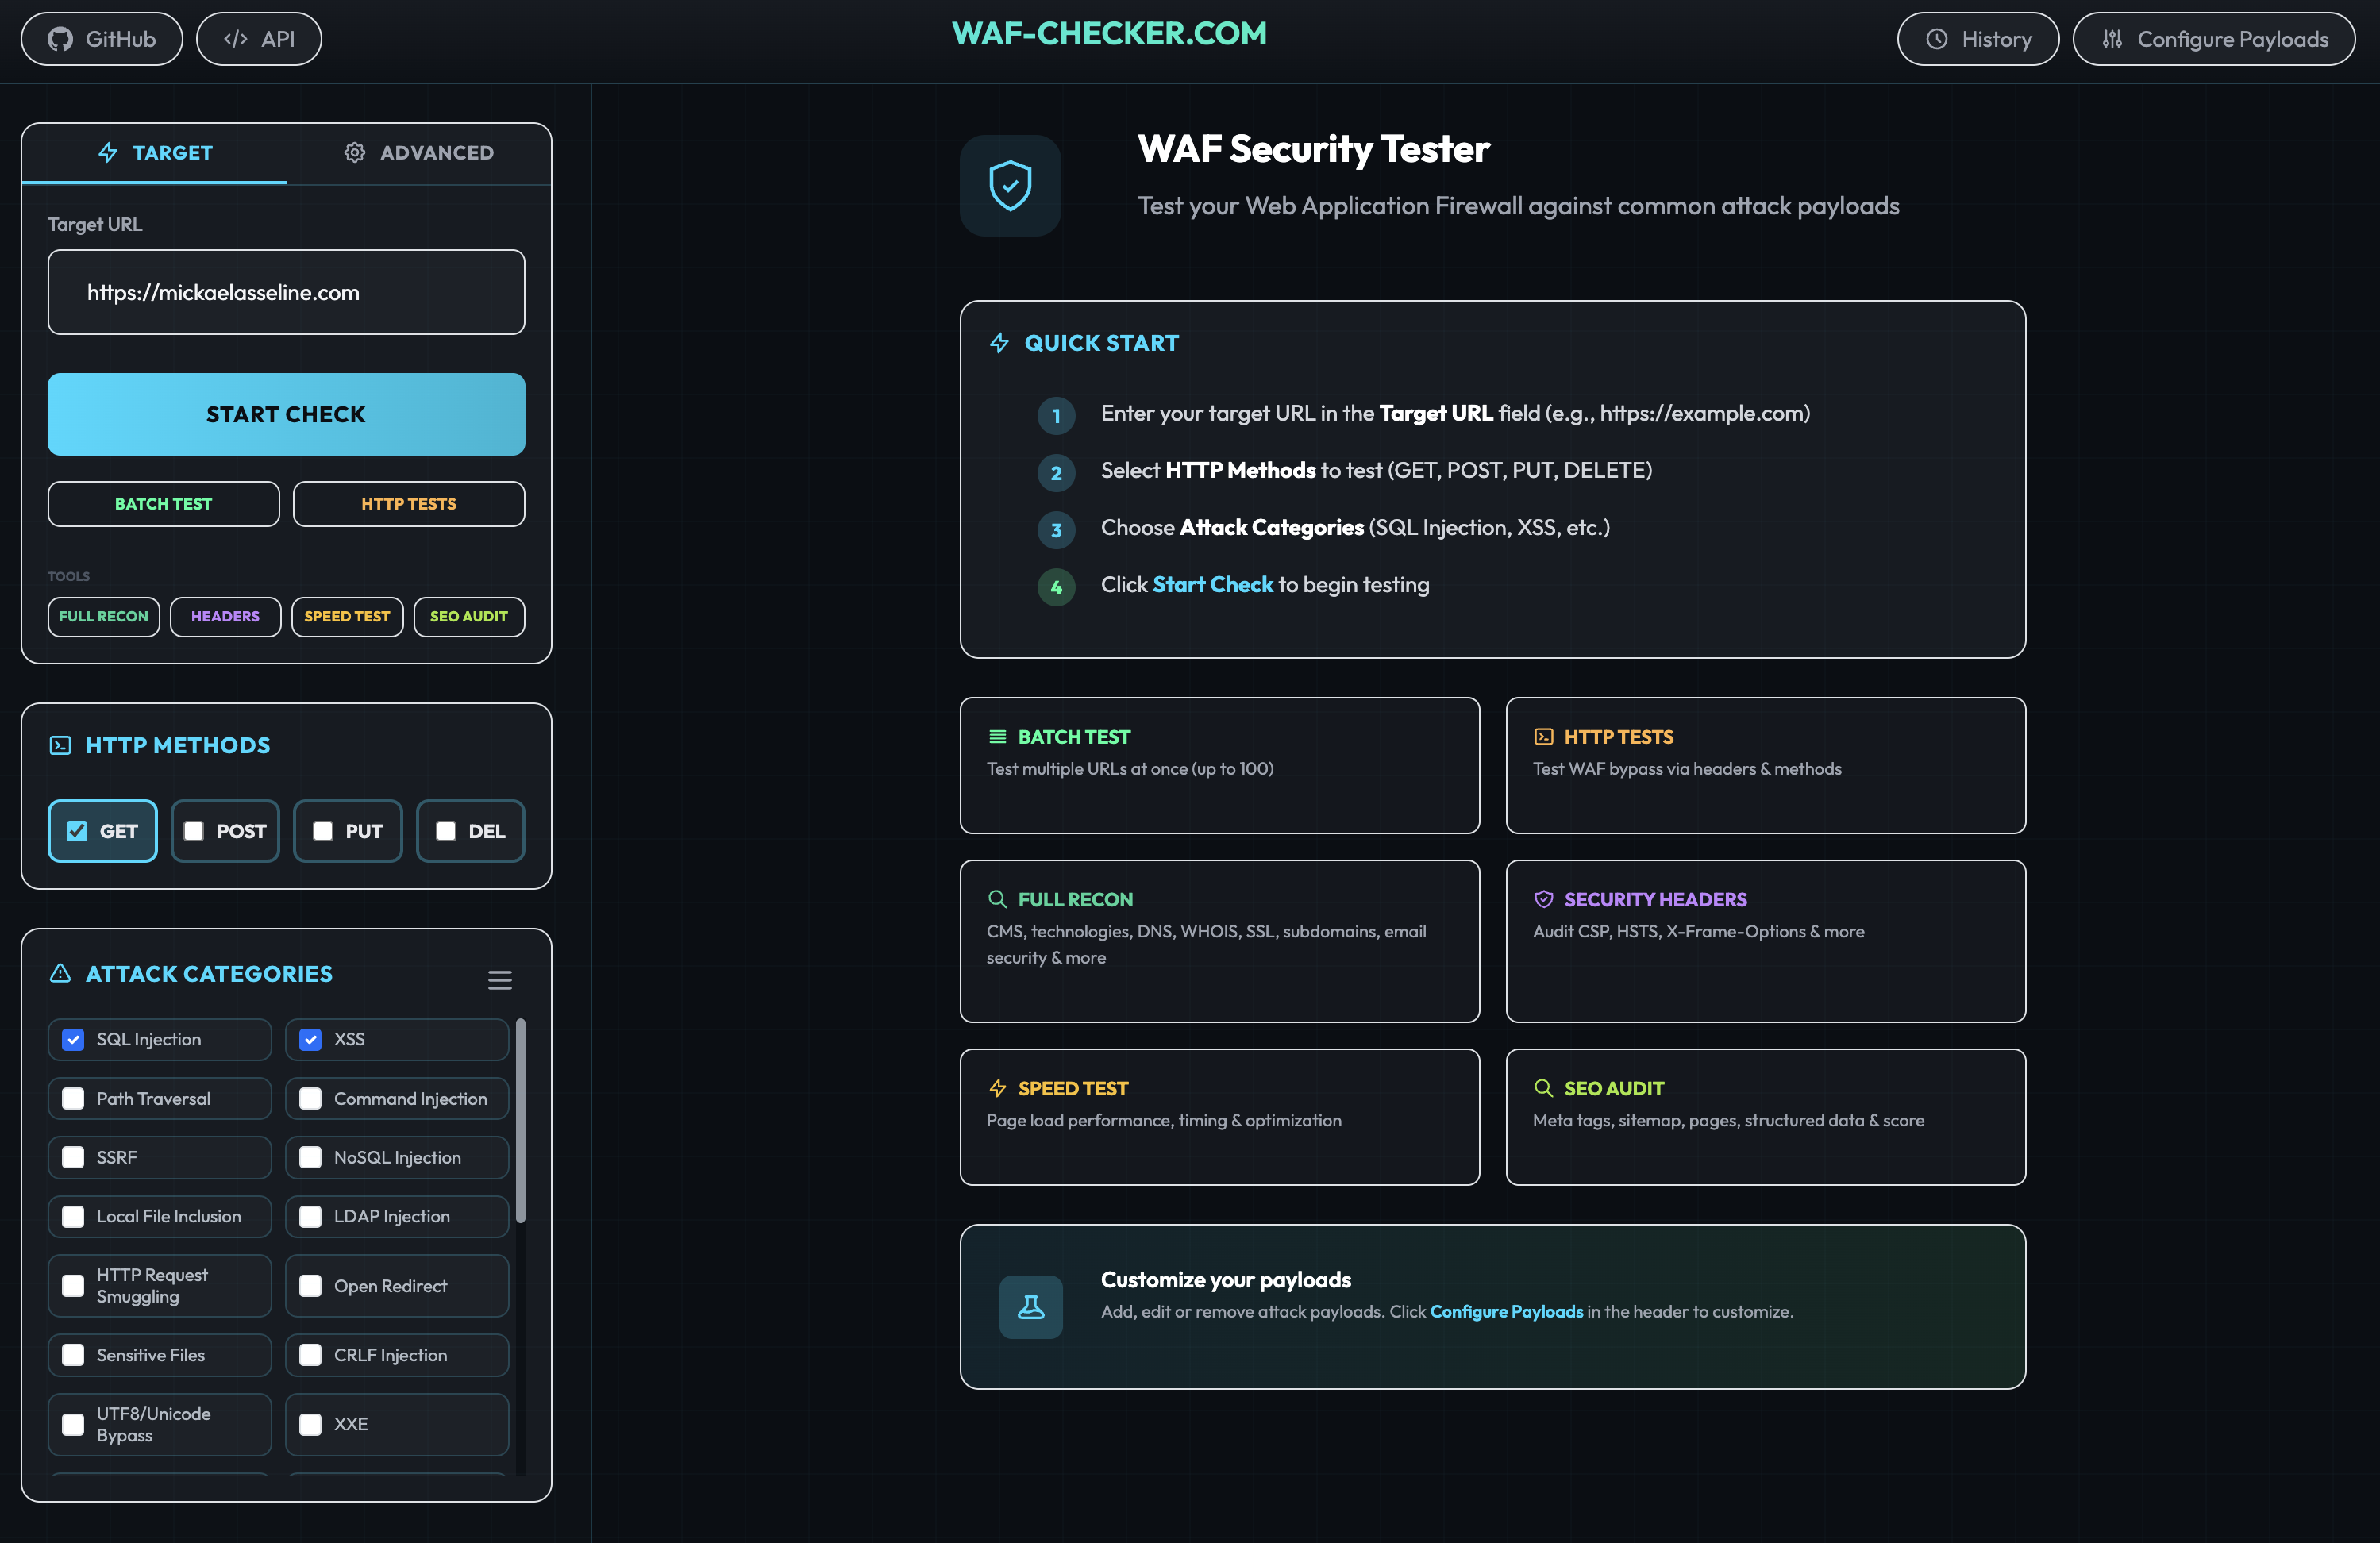 papamica/waf-checker
Tests your WAF with +160 payloads
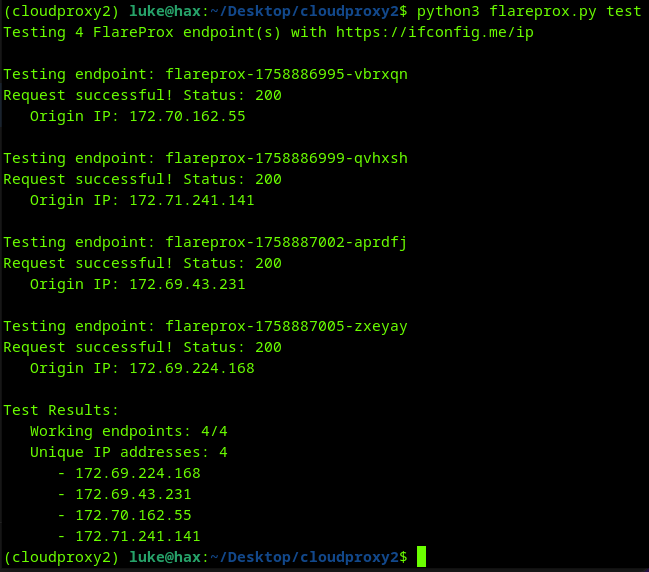 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
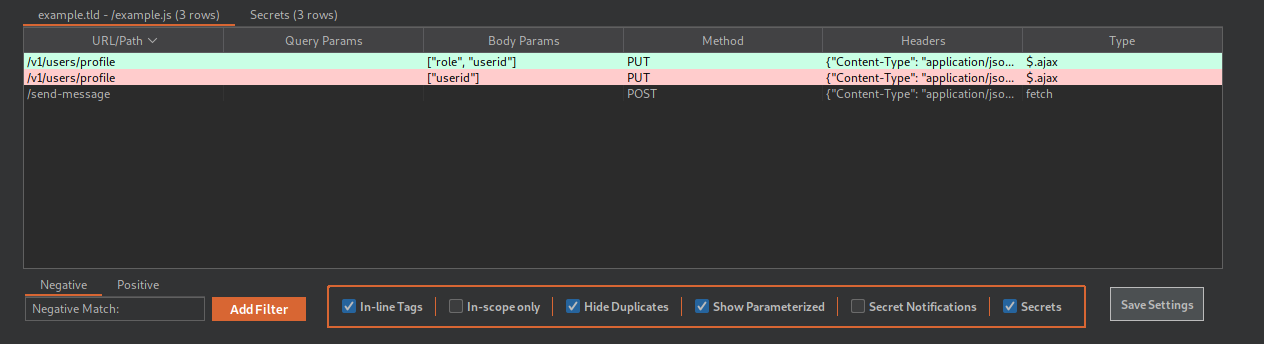 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 impact-i/x8-burp
Hidden parameters discovery suite
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.