
emp3r0r
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
anti-botcommand-and-controlids-ips-evasion+10
1.8k9h 30m ago
jm33-m0/emp3r0rSelf‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 xjoker/lenovo_y700_tb320fc_on_cve-2025-21479
In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…
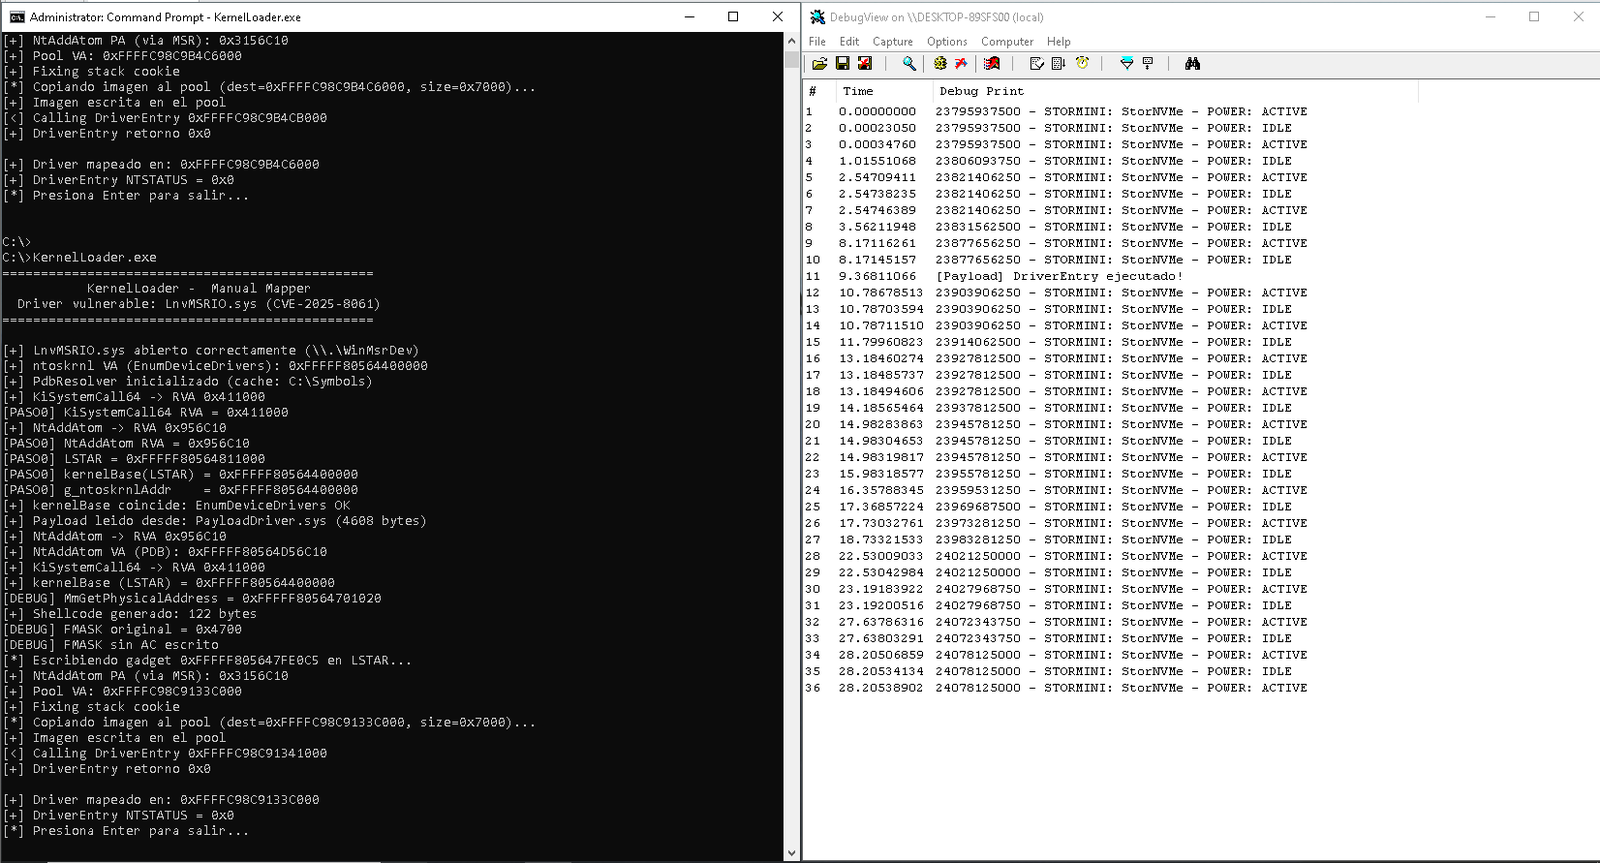 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 racoten/reflectivepluginloader
A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 tc4dy/cve-2026-41091-poc-exploit
CVE-2026-41091 RedSun | Microsoft Defender LPE exploit. Low-privileged users gain NT AUTHORITY\SYSTEM 🔥 via Cloud Files API + NTFS junction…
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
 cenobyte-vincit/dyen
In-memory Mach-O dylib loader for stock macOS Python; decrypts, maps, and runs payloads without dlopen or writing to disk, with optional encrypted…
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
 ricardojoserf/nativedump
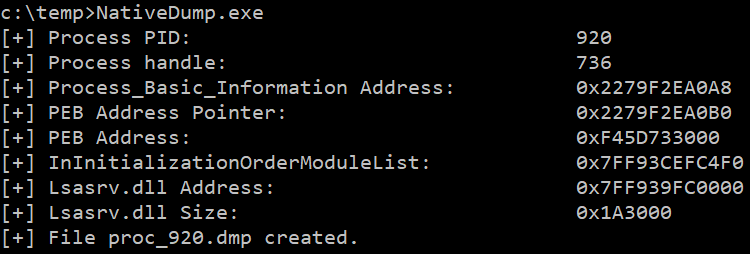
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
 ricardojoserf/trickdump
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…