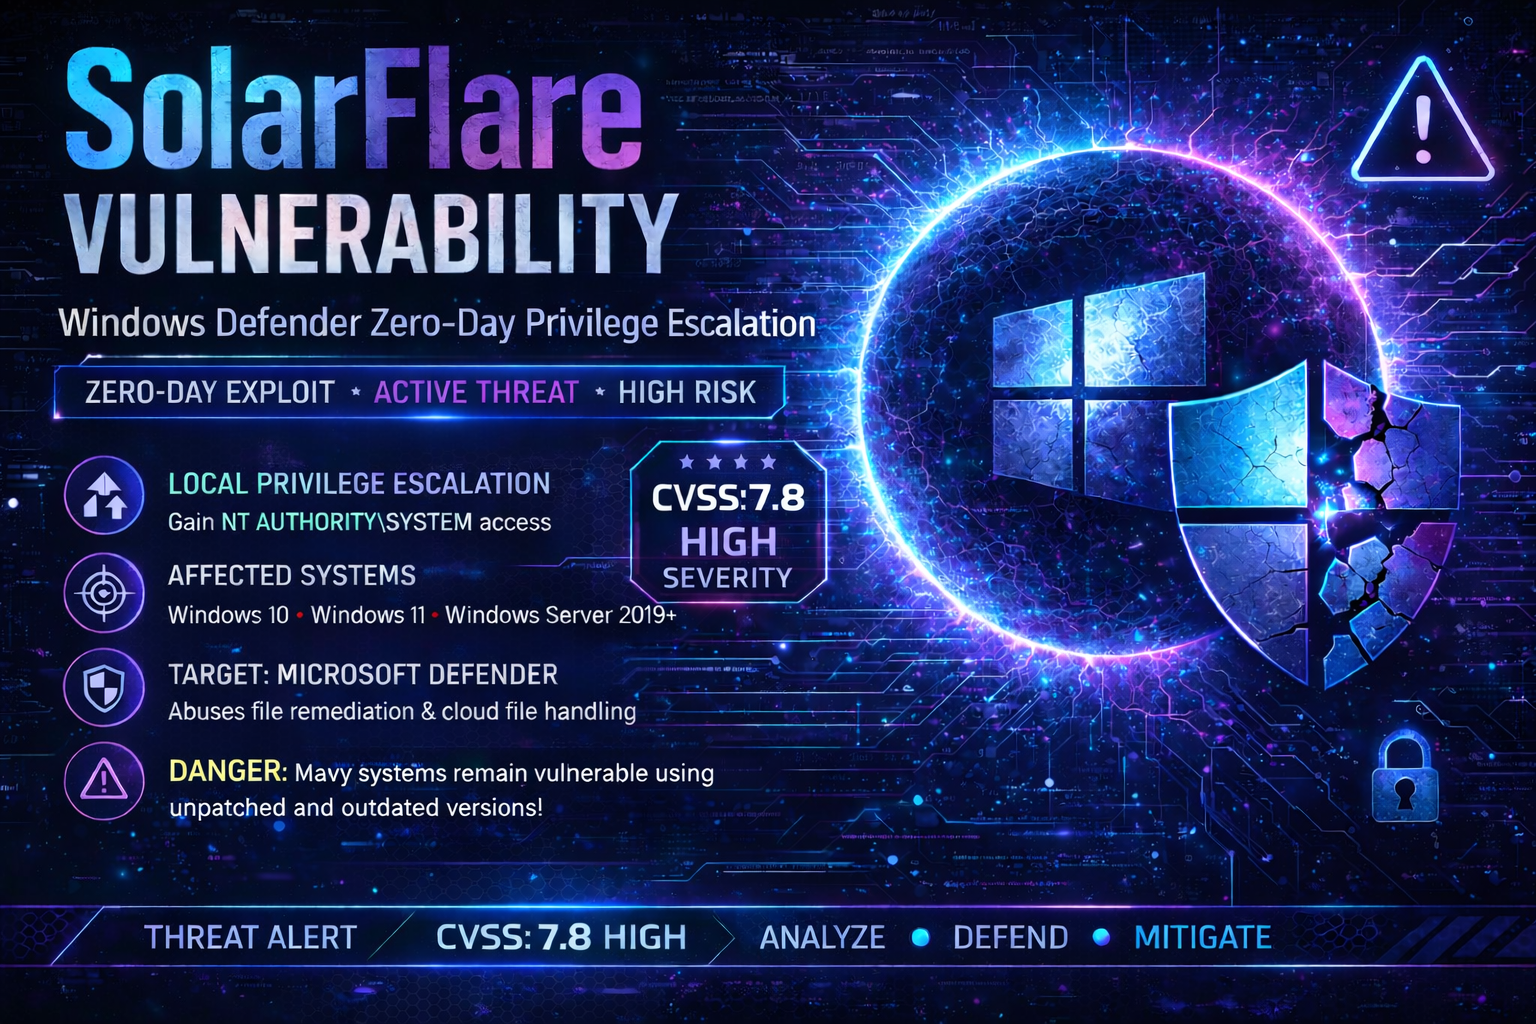
CVE-2026-41091 RedSun | Microsoft Defender LPE exploit. Low-privileged users gain NT AUTHORITY\SYSTEM 🔥 via Cloud Files API + NTFS junction trickery. Forces Defender to write malicious payloads to System32 with SYSTEM rights. ⚠️ Actively exploited in wild. CVSS 7.8. Patch: Defender Engine 1.1.26040.8. 🛡️ Educational PoC only.



This tool is provided for educational and authorized penetration testing purposes only. The authors and contributors are not responsible for any misuse or damage caused by this software. Users are solely responsible for ensuring they have explicit written permission from the target owner before testing. Unauthorized access to computer systems is illegal under applicable federal, state, and international cybercrime laws. By using this software, you agree to:
[!] WARNING: Active Directory elevation of privilege vulnerabilities present high risk to enterprise infrastructure. Unauthorized testing is strictly prohibited.
Microsoft Defender Link Following Vulnerability - Local Privilege Escalation to NT AUTHORITY\SYSTEM
This repository contains a full working Proof of Concept (PoC) exploit for CVE-2026-41091, a critical local privilege escalation vulnerability in Microsoft Defender (Microsoft Malware Protection Engine). By exploiting improper link resolution (CWE-59), an authenticated low-privileged attacker can gain NT AUTHORITY\SYSTEM privileges.
The vulnerability, also known as "RedSun" or "SolarFlare", allows attackers to trick Microsoft Defender into writing arbitrary files to protected system locations with SYSTEM privileges using Cloud Files API (CfAPI) and NTFS junction points.
Note: This repository includes two versions:
basic_poc.cpp- Simplified algorithm demonstration (educational)full_poc.cpp- Complete working exploit with all features
| Category | Feature | basic_poc.cpp | full_poc.cpp |
|---|---|---|---|
| Exploitation | Local Privilege Escalation to SYSTEM | [+] | [+] |
| Cloud Files API (CfAPI) Integration | [-] | [+] | |
| Cloud Placeholder Creation | [-] | [+] | |
| NTFS Junction Redirection | [~] | [+] | |
| COM Service Activation | [-] | [+] | |
| Techniques | Batch Oplock Abuse | [+] | [+] |
| VSS Snapshot Detection | [+] | [+] | |
| EICAR Trigger | [+] | [+] | |
| NTFS Reparse Point (Mount Point) | [+] | [+] | |
| File Disposition (NtSetInformationFile) | [-] | [+] | |
| Named Pipe Session ID Detection | [-] | [+] | |
| Console Session Launch (conhost.exe) | [-] | [+] | |
| WaitOnAddress / WakeByAddress | [-] | [+] | |
| SYSTEM Verification | [-] | [+] | |
| Target | Microsoft Defender < 1.1.26040.8 | [+] | [+] |
| Windows 10/11 | [+] | [+] | |
| Windows Server 2016 | [+] | [+] | |
| Windows Server 2019/2022 | [+] | [+] | |
| x64 only | [+] | [+] | |
| Usability | Structured Logging | [~] | [+] |
| Error Handling | [~] | [+] | |
| Random Directory Names | [+] | [+] | |
| Automatic Cleanup | [~] | [+] | |
| Retry Logic (NtCreateFile) | [-] | [+] |
| Attribute | Value |
|---|---|
| CVE ID | CVE-2026-41091 |
| CVSS Score | 7.8 (High) |
| CVSS Vector | AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H |
| Attack Vector | Local |
| Privileges Required | Low |
| User Interaction | None |
| Impact | SYSTEM-level code execution |
| CISA KEV | [+] Yes (actively exploited in the wild) |
| Patch Available | Microsoft Malware Protection Engine 1.1.26040.8 |
| Product | Affected Versions | Fixed Versions |
|---|---|---|
| Microsoft Malware Protection Engine | < 1.1.26040.8 | 1.1.26040.8+ |
| Microsoft Defender Antimalware Platform | < 4.18.26040.7 | 4.18.26040.7+ |

