

SyscallRevenant
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
binary-exploitationexploitationids-ips-evasion+6
1
silentisvox/syscallrevenantClean Indirect Syscalls with Syscall Tampering.
 racoten/reflectivepluginloader
Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…
 tc4dy/cve-2026-41091-poc-exploit
CVE-2026-41091 RedSun | Microsoft Defender LPE exploit. Low-privileged users gain NT AUTHORITY\SYSTEM 🔥 via Cloud Files API + NTFS junction…
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 zeromemoryex/cve-2025-26125
( 0day ) Local Privilege Escalation in IObit Malware Fighter
 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 r41n3rzuf477/ps-ppl-bypass
Process Explorer vulnerable driver PPL Bypass
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
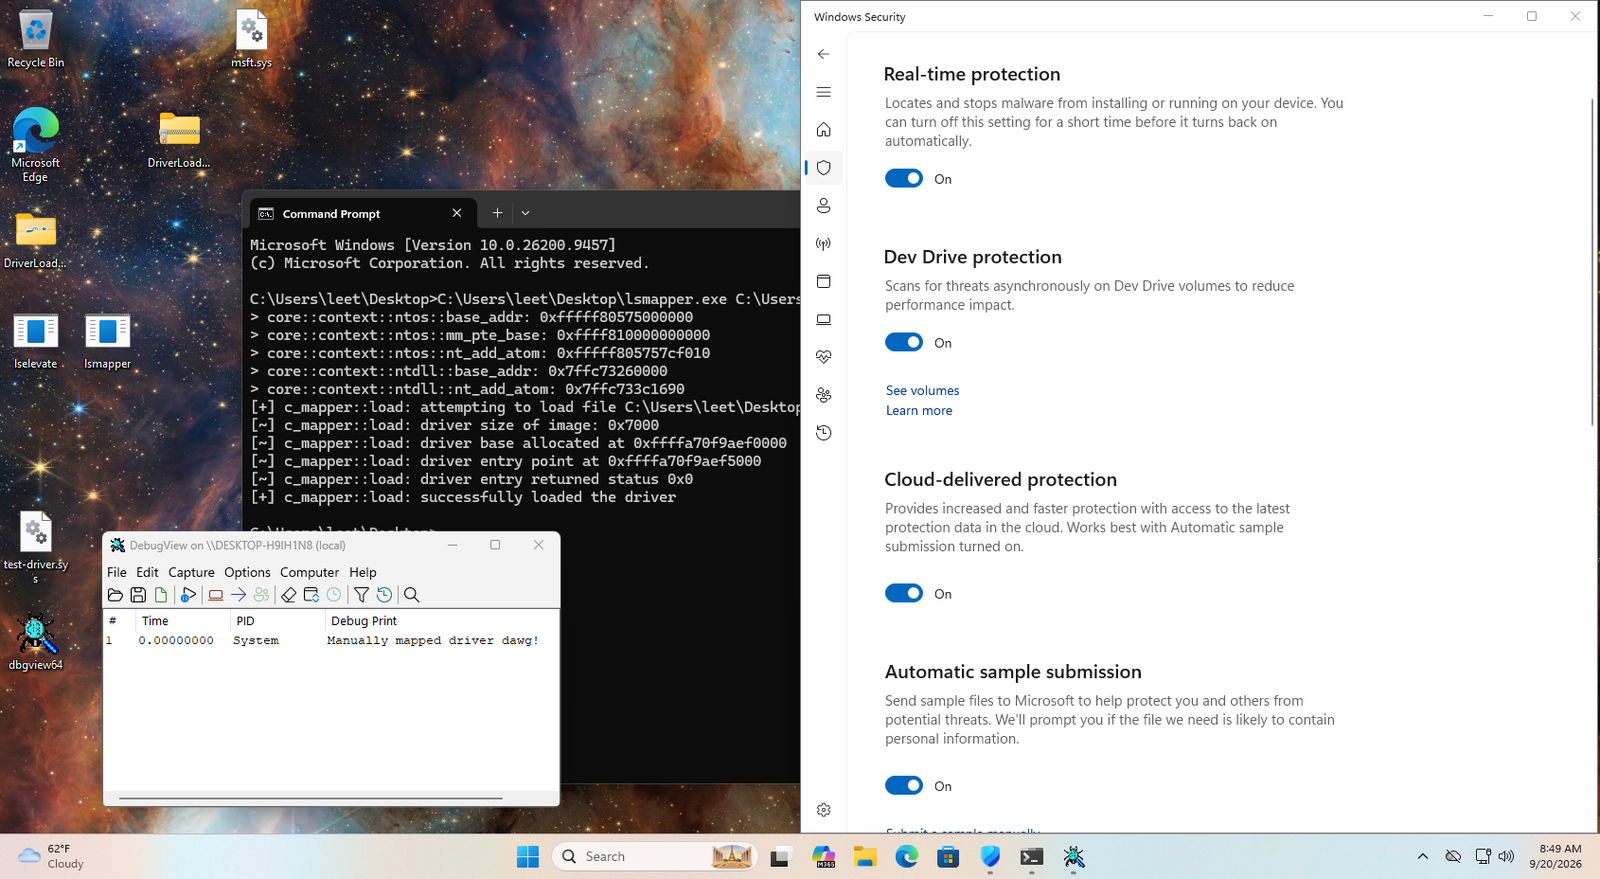 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 itm4n/pentest-windows
Collection of Windows internals research and exploitation techniques covering privilege escalation, token abuse, and post-exploitation tricks for red…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
 ahm3dgg/cve-2018-8611
Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.