
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux systems.



Silverseal is an open-source Linux bootkit research framework written in Rust. It demonstrates how a UEFI bootkit hooks the Linux boot process to load a Rust kernel module. The repository contains:
silverseal-bootkit/: the no_std UEFI bootkit, with architecture-specific assembly under asm/.silverseal-rootkit/: the Kbuild-managed Rust Linux kernel module.scripts/: environment, deployment, and recovery helpers.The project explores UEFI bootkit development, Linux boot-chain hooking, kernel-module loading, and pre-OS persistence in a research environment.
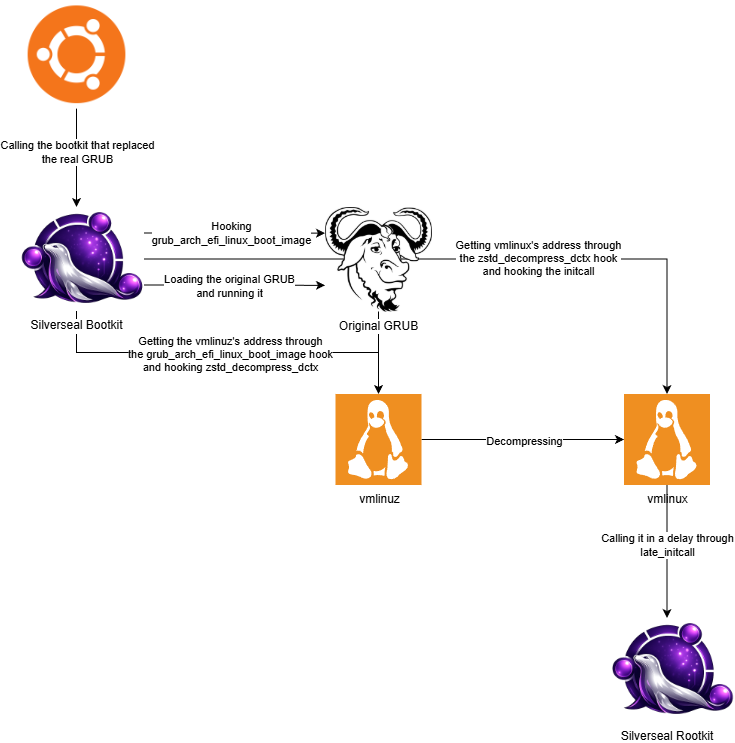
grubx64.efi is replaced by silverseal-bootkit.efi; the original is retained as grubx64.efi.original..text code caves, keeps their work_struct and arguments in a .data cave, and redirects that initcall entry to the stager.schedule_work, then jumps to the original initcall so it still runs.call_usermodehelper to run /sbin/insmod /silverseal_rootkit.ko from the real root filesystem.The x64 kernel hook uses signatures and layout assumptions from a specific Ubuntu kernel image. Matching build artifacts alone does not establish that the hook will work on another kernel; validate the target image and boot behavior in a disposable VM.
ARM64 mirrors the existing x86 deployment model:
grubaa64.efi is replaced by silverseal-bootkit.efi; the original is retained as grubaa64.efi.original.vmlinuz .linux section and observes its successful decompression into vmlinux.work_struct and calls the target kernel's schedule_work.isra.0. Its worker sleeps for 10 seconds, then invokes /sbin/insmod /silverseal_rootkit.ko from the real root filesystem.On Ubuntu, install_dependencies.sh installs build packages, Rust and rust-src, and bindgen-cli. It also checks whether the running kernel advertises CONFIG_RUST=y. Review the script before running it because it installs packages and changes the default Rust toolchain:
./scripts/install_dependencies.sh
On WSL2 with Ubuntu, wsl_setup.sh prepares a custom Rust-enabled WSL2 kernel, a modules VHDX, and a build tree for external modules. It can optionally write a Windows .wslconfig entry. Review its options and the changes it makes before running it:
./scripts/wsl_setup.sh --help
./scripts/wsl_setup.sh
The pinned ARM64 Ubuntu target has a separate setup flow below. ubuntu_target_setup.sh runs natively in that ARM64 VM and derives the required Rust version from its kernel configuration; it is not a generic WSL cross-build helper.
Use the native ARM64 Ubuntu VM on Apple Silicon. The real module must be built through the target kernel's Kbuild tree, not with Cargo's IDE stub:
cd Silverseal
./scripts/ubuntu_target_setup.sh 7.0.0-31-generic

cd silverseal-rootkit
make clean ARCH=arm64 LLVM= KDIR=/lib/modules/7.0.0-31-generic/build
PATH=/usr/bin:/bin:$PATH \
RUST_LIB_SRC=/path/printed/by/ubuntu_target_setup.sh \
make RUST_MIN_TOOLCHAIN= \
  ARCH=arm64 \
  LLVM= \
  KDIR=/lib/modules/7.0.0-31-generic/build \
  RUSTC=rustc-1.93 \
  RUSTDOC=rustdoc-1.93
Confirm that Kbuild produced the module for the pinned kernel:
file target/arm64/7.0.0-31-generic/silverseal_rootkit.ko
modinfo target/arm64/7.0.0-31-generic/silverseal_rootkit.ko | grep vermagic
Before runtime testing, validate the target kernel's work_struct layout from its BTF or DWARF: size 32 bytes, entry at offset 8, and func at offset 24. A mismatch is a hard stop because those values are encoded by the stager.
Apple Silicon can build the AArch64 UEFI binary directly. Install stable Rust with the aarch64-unknown-uefi target and PowerShell (pwsh) for fixture verification.
The large pinned artifacts are expected in tmp/silverseal-kernel-7.0.0-31-generic/. Generate the v3 profile after verifying their hashes, unique signatures, nested stock-zboot PE, caves, initcall, and linked System.map evidence:
cd Silverseal
pwsh ./scripts/verify_arm64_fixture.ps1 \
  -ArtifactDirectory ./tmp/silverseal-kernel-7.0.0-31-generic \
  -OutputDirectory ./target/arm64-fixture/7.0.0-31-generic-v3

export SILVERSEAL_ARM64_PROFILE="$PWD/target/arm64-fixture/7.0.0-31-generic-v3/7.0.0-31-generic.ssarm64p"
cargo build-bootkit-arm64 --release
The result is:
target/aarch64-unknown-uefi/release/silverseal-bootkit.efi
An ARM64 build with no SILVERSEAL_ARM64_PROFILE deliberately installs no hook. The profile and small signature fixtures live under fixtures/arm64/7.0.0-31-generic/; the large kernel and GRUB artifacts remain ignored.
Host-side contracts can be run with:
cargo test-arm64
cargo test -p silverseal-bootkit --bin silverseal-arm64-tool --features arm64-tools
Copy the bootkit and module into the VM, then put the module on the real root filesystem and replace the existing ARM64 GRUB binary:
sudo install -m 0644 \
  silverseal-rootkit/target/arm64/7.0.0-31-generic/silverseal_rootkit.ko \
  /silverseal_rootkit.ko

sudo ./scripts/setup_silverseal.sh arm64 \
  target/aarch64-unknown-uefi/release/silverseal-bootkit.efi
sudo reboot
Do not create a menu entry and do not rebuild initramfs. The VM should boot its normal existing Ubuntu entry. After boot, inspect the module result with:
sudo dmesg -w
lsmod | grep silverseal_rootkit
To restore the saved original GRUB image:
sudo ./scripts/restore_silverseal.sh arm64
The restore helper keeps the replaced image as grubaa64.efi.silverseal for recovery.
Add a virtual serial port to the powered-off ARM64 VM and configure its output to a file on macOS. The bootkit discovers the firmware's UEFI Serial I/O protocol; it does not assume QEMU's PL011 MMIO address. If Fusion firmware exposes no Serial I/O protocol, logging is silently disabled and boot continues.







