Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
ConfluenceMemshell — Confluence CVE 2021,2022,2023 利用工具,支持命令执行,哥斯拉,冰蝎 内存马注入 | Kitploit
Tools/GitHubGitHub/lotus6/confluencememshell
Persistence MechanismsVulnerability AnalysisExploitationWeb Application ExploitationPost-ExploitationWeb SecurityPenetration TestingRemote Access ToolPayload Development
GitHublotus6/confluencememshell

ConfluenceMemshell

57023132 years agoReviewed by Kitploit

Confluence CVE 2021,2022,2023 利用工具,支持命令执行,哥斯拉,冰蝎 内存马注入

View Repository
Share

ConfluenceMemshell

Confluence CVE 2021, 2022, 2023 exploitation tool, supports command execution, Godzilla, Behinder memory shell injection

  • Supported Confluence versions: CVE-2021-26084, CVE-2022-26134, CVE_2023_22515, CVE-2023-22527
  • (If it helps you and you think it's good, please give it a big ⭐️❗️)
  • Godzilla default password: pass, default key: key, request configuration - protocol header needs to add Connection: close
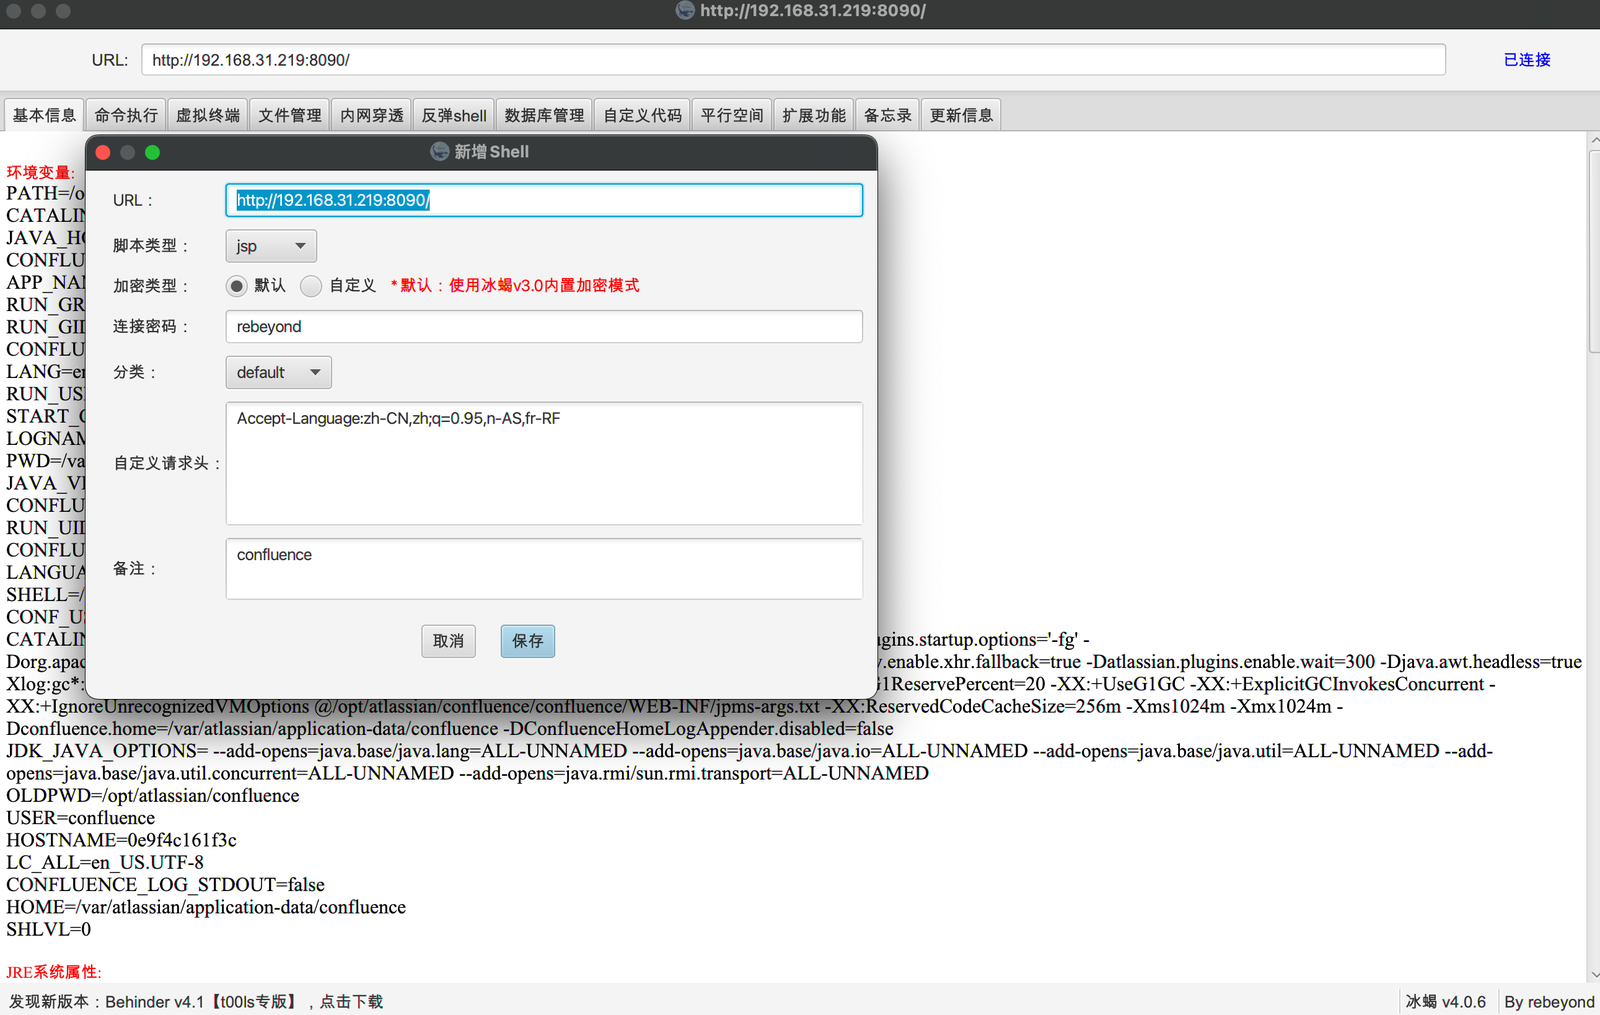
  • Behinder default password: rebeyond, default UA: Accept-Language:zh-CN,zh;q=0.95,n-AS,fr-RF
  • Only the CVE-2022-26134 version supports Godzilla and Behinder custom passwords; other versions all use default passwords

V1.1版本

  • 新增 CVE_2023_22515,用户创建,内存马注入,基于 CmdShell 的命令执行
  • table 双击复制当前行,shell路径,key,ua
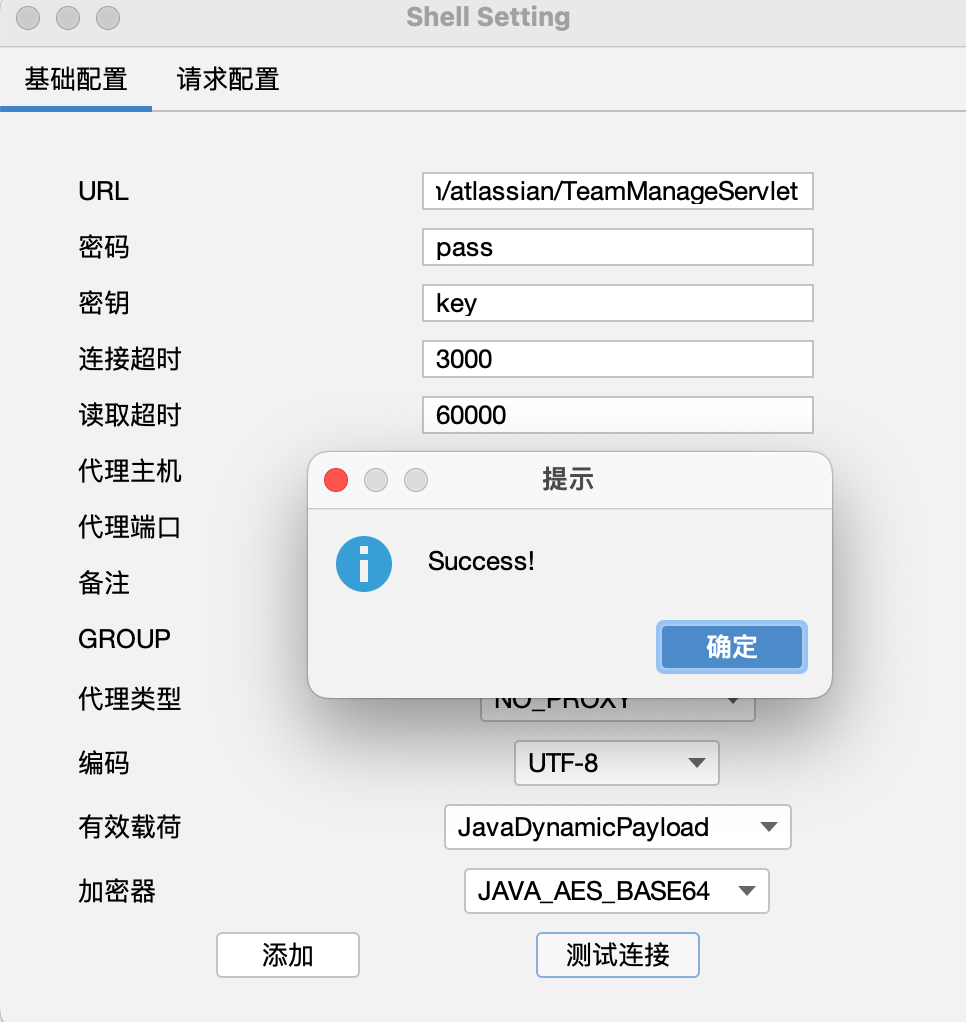
  • 哥斯拉 memshell 地址:url+/plugins/servlet/com/atlassian/TeamManageServlet
  • 哥斯拉默认密码:pass ,默认key:key ,请求配置 - 协议头 需加上 Connection: close
  • CmdShell 地址:url+/plugins/servlet/com/atlassian/TeamManageServlet?team=whoami
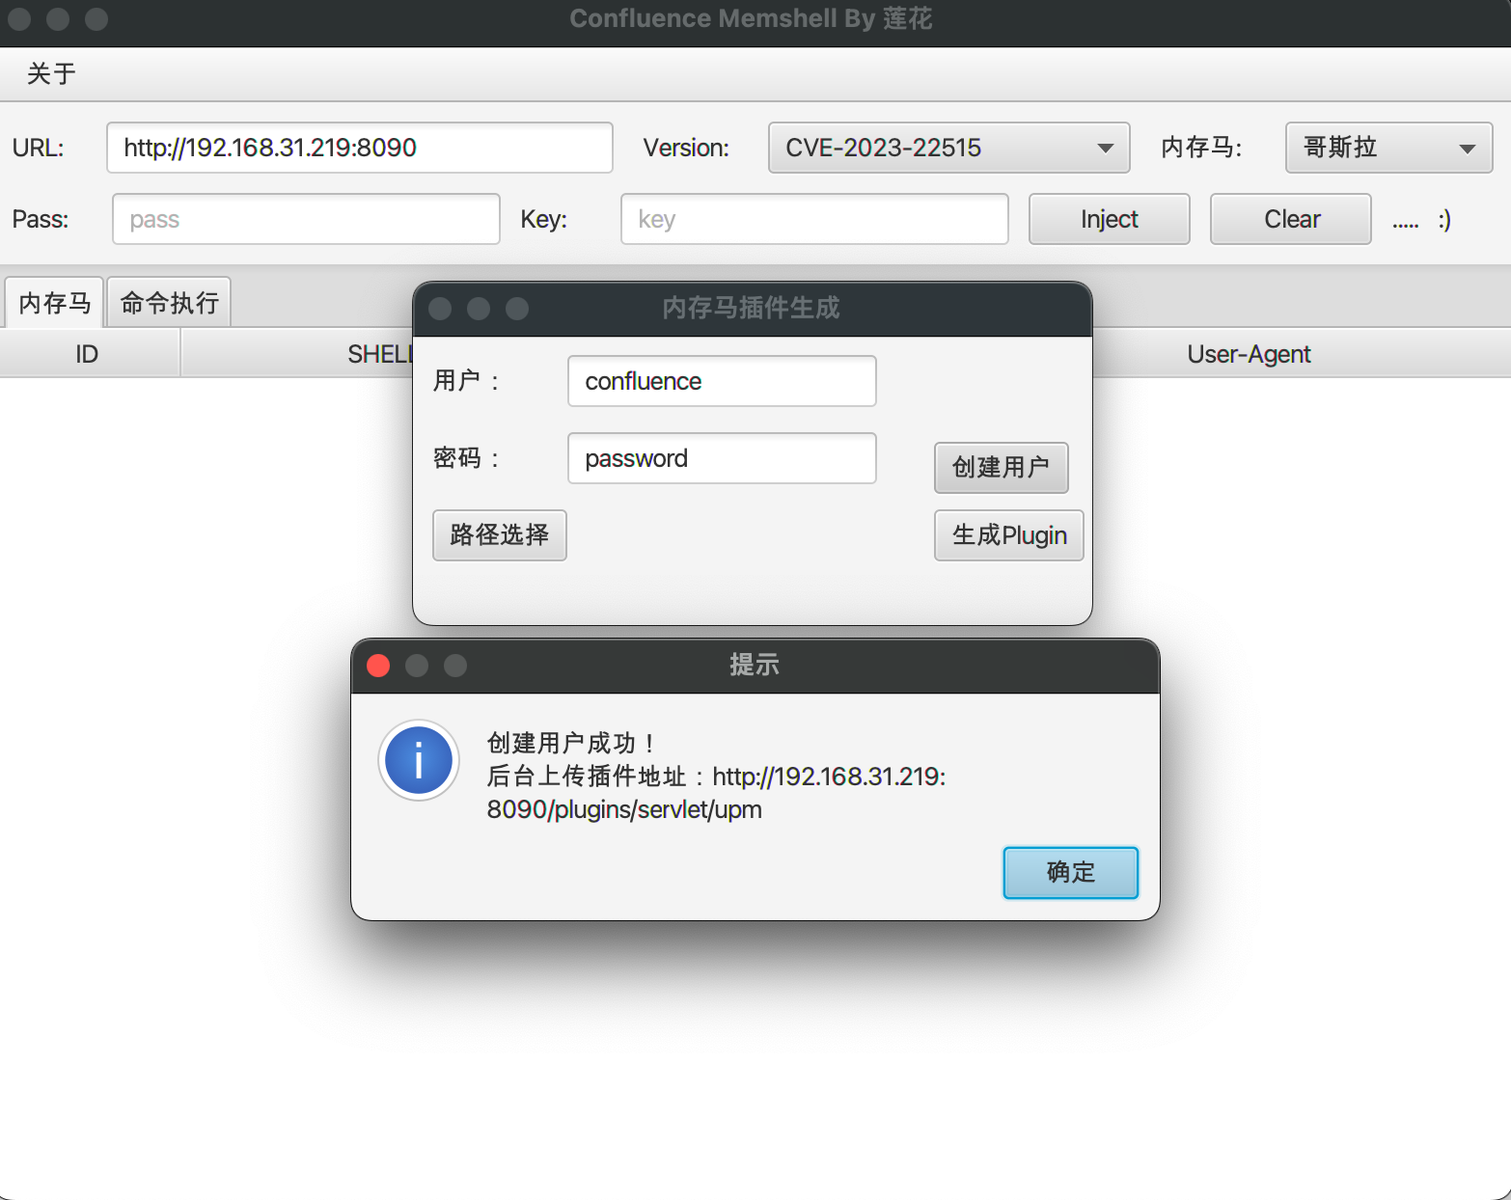
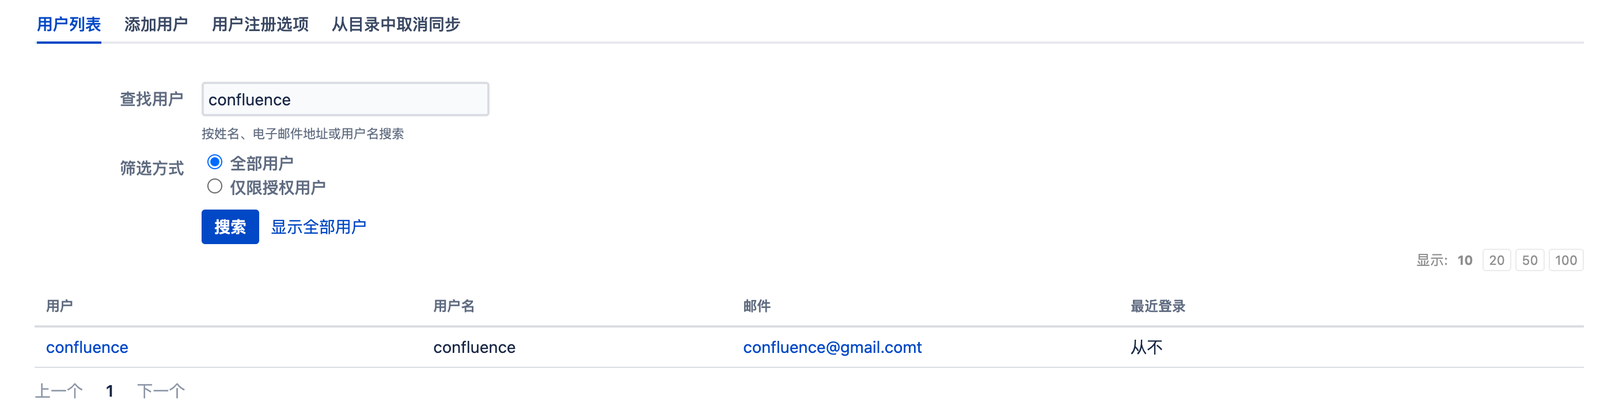
  1. Create user
image
  • Created successfully image
  1. Generate malicious plugin Jar package (contains Godzilla and CmdShell)
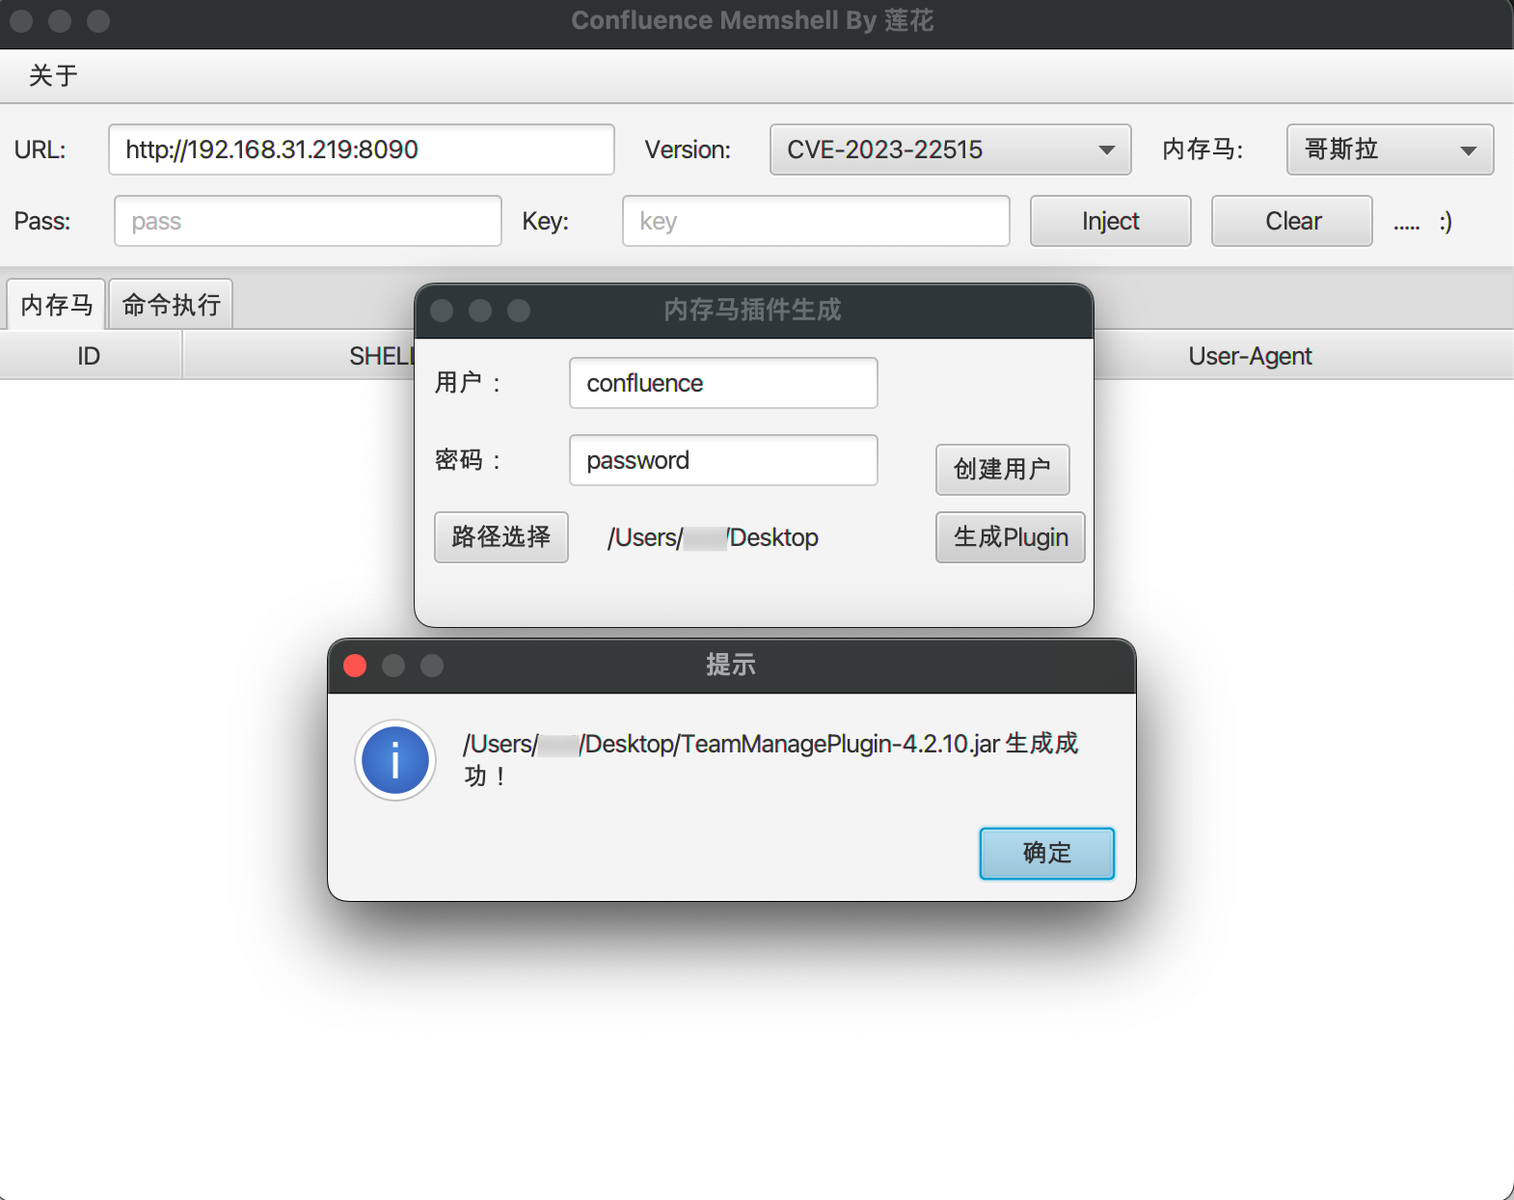
image
  • Displays the memory shell address, and pass:key (double-click to copy, shell path, key, ua)
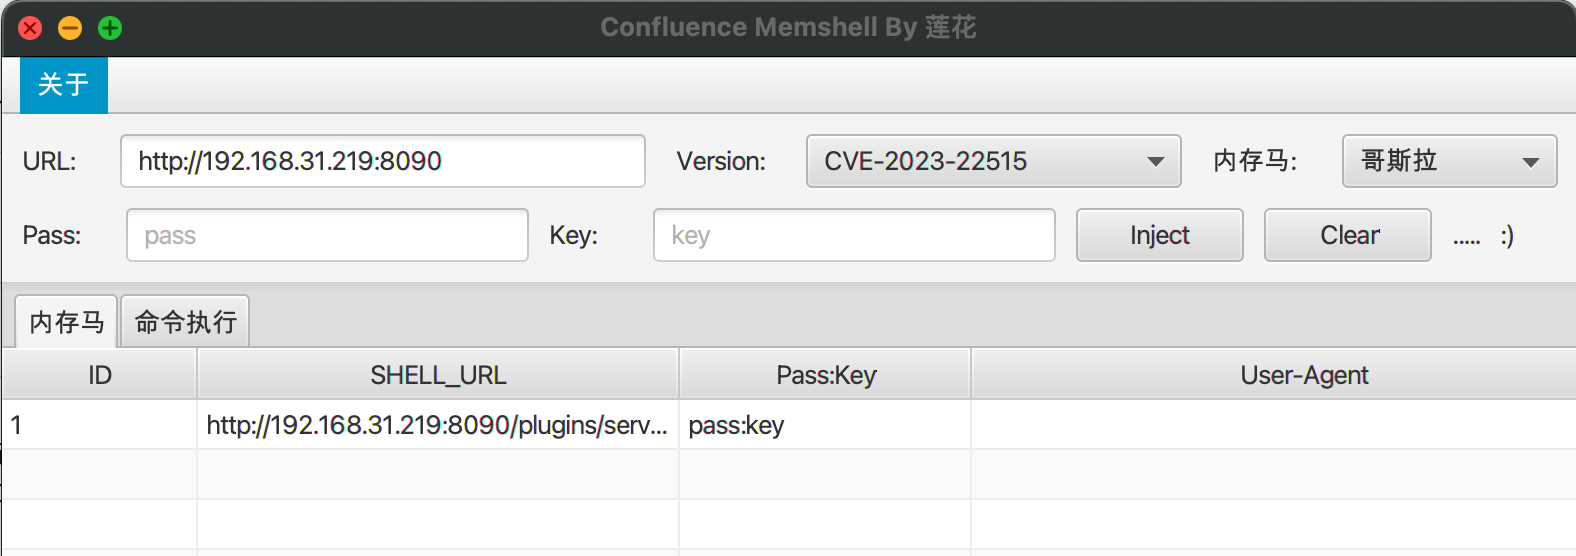
image
  1. Log in to the admin panel with the created user, plugin feature address: url+/plugins/servlet/upm, upload the plugin (no need to wait for the upload to finish, just refresh and it will be there).
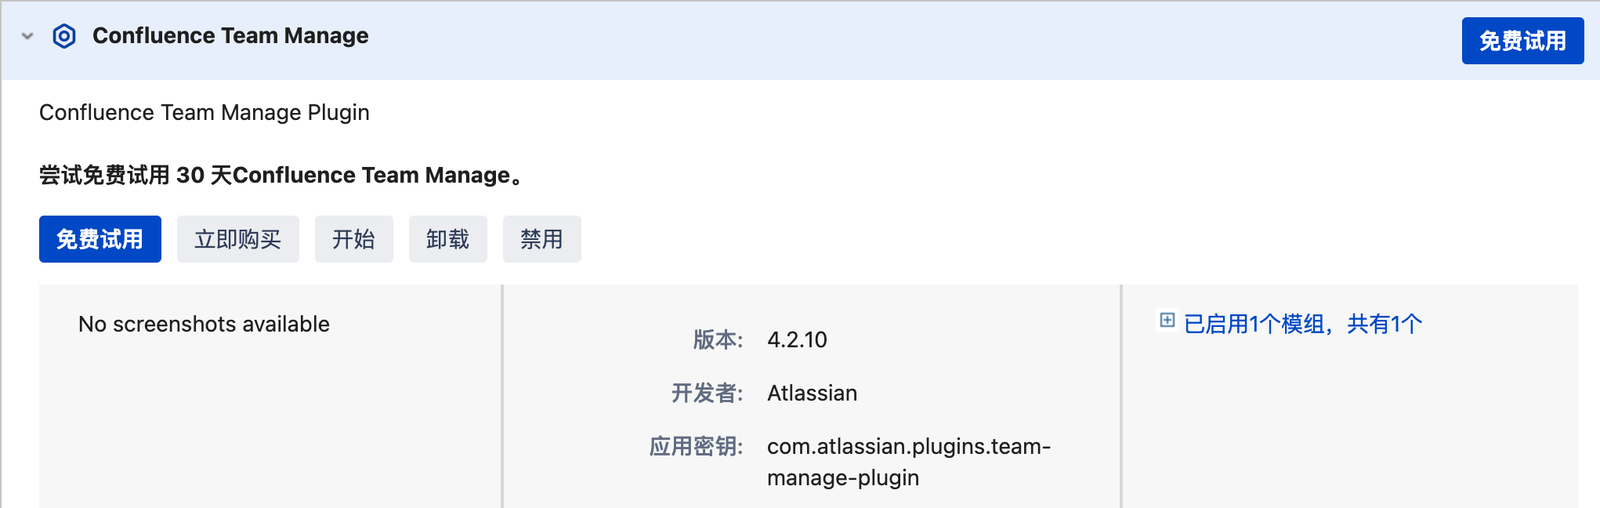
image
  1. Godzilla connection
image
  1. Command execution based on the CmdShell plugin image
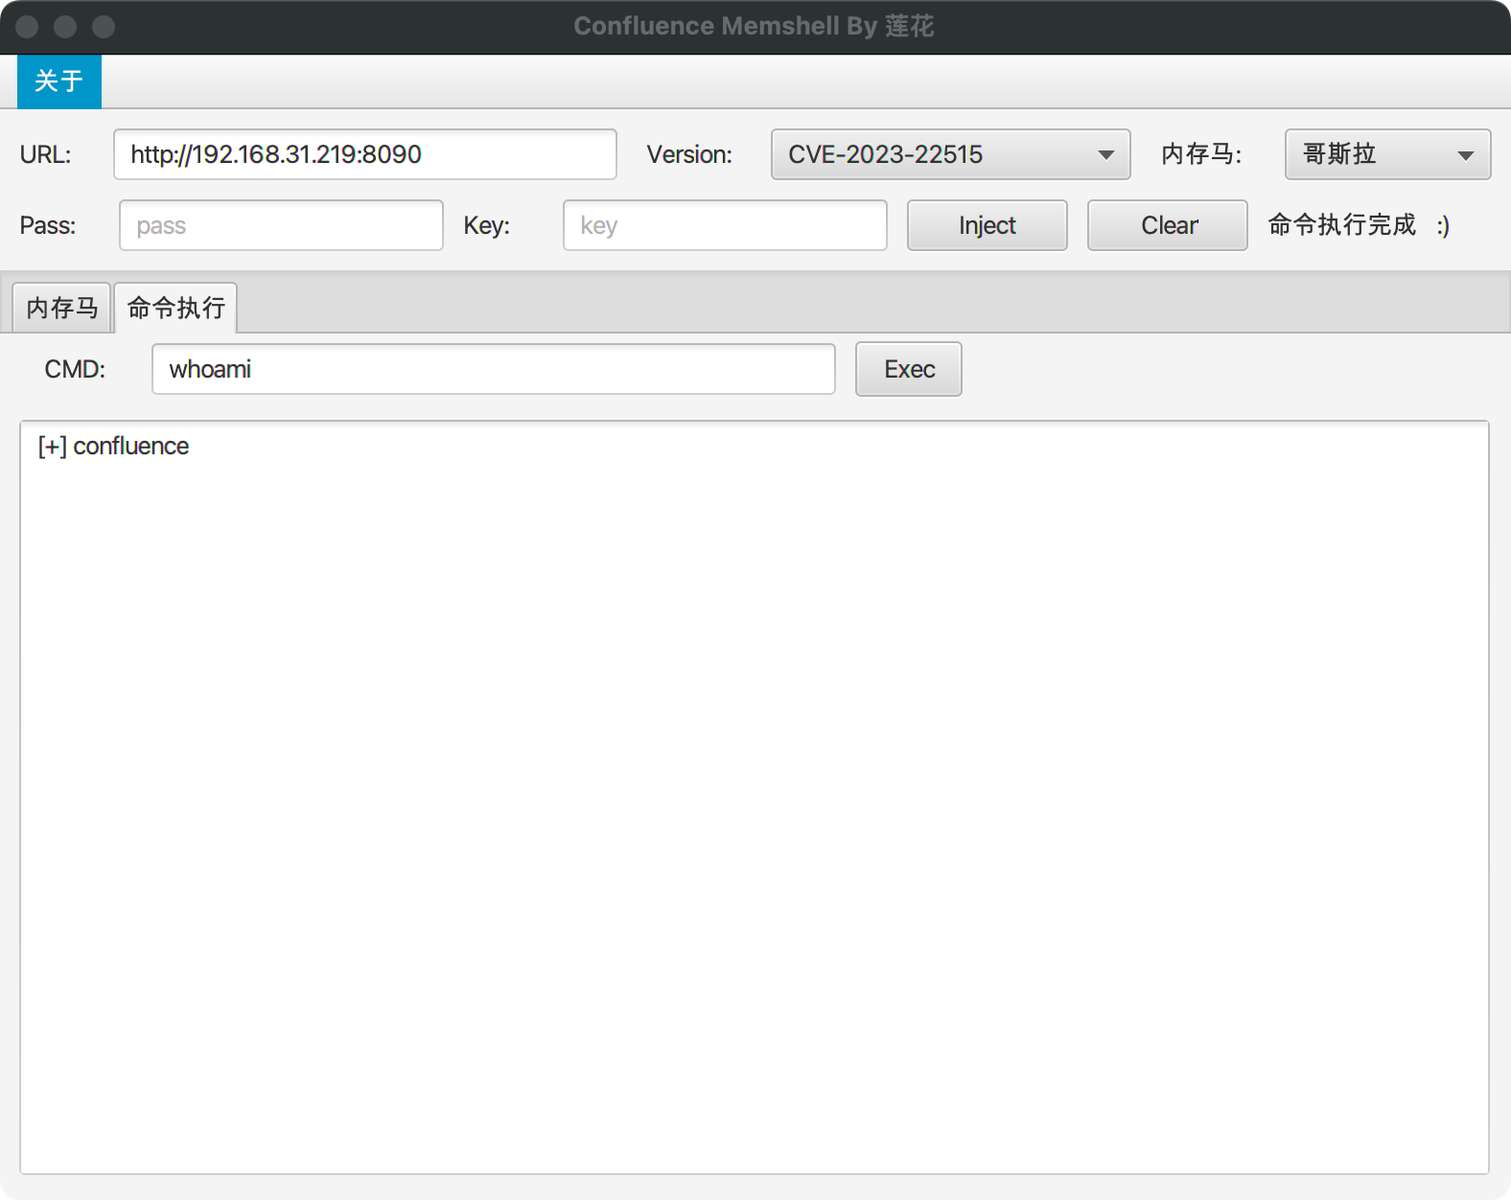
V1.0

  1. Command execution (the same applies to other CVE versions)
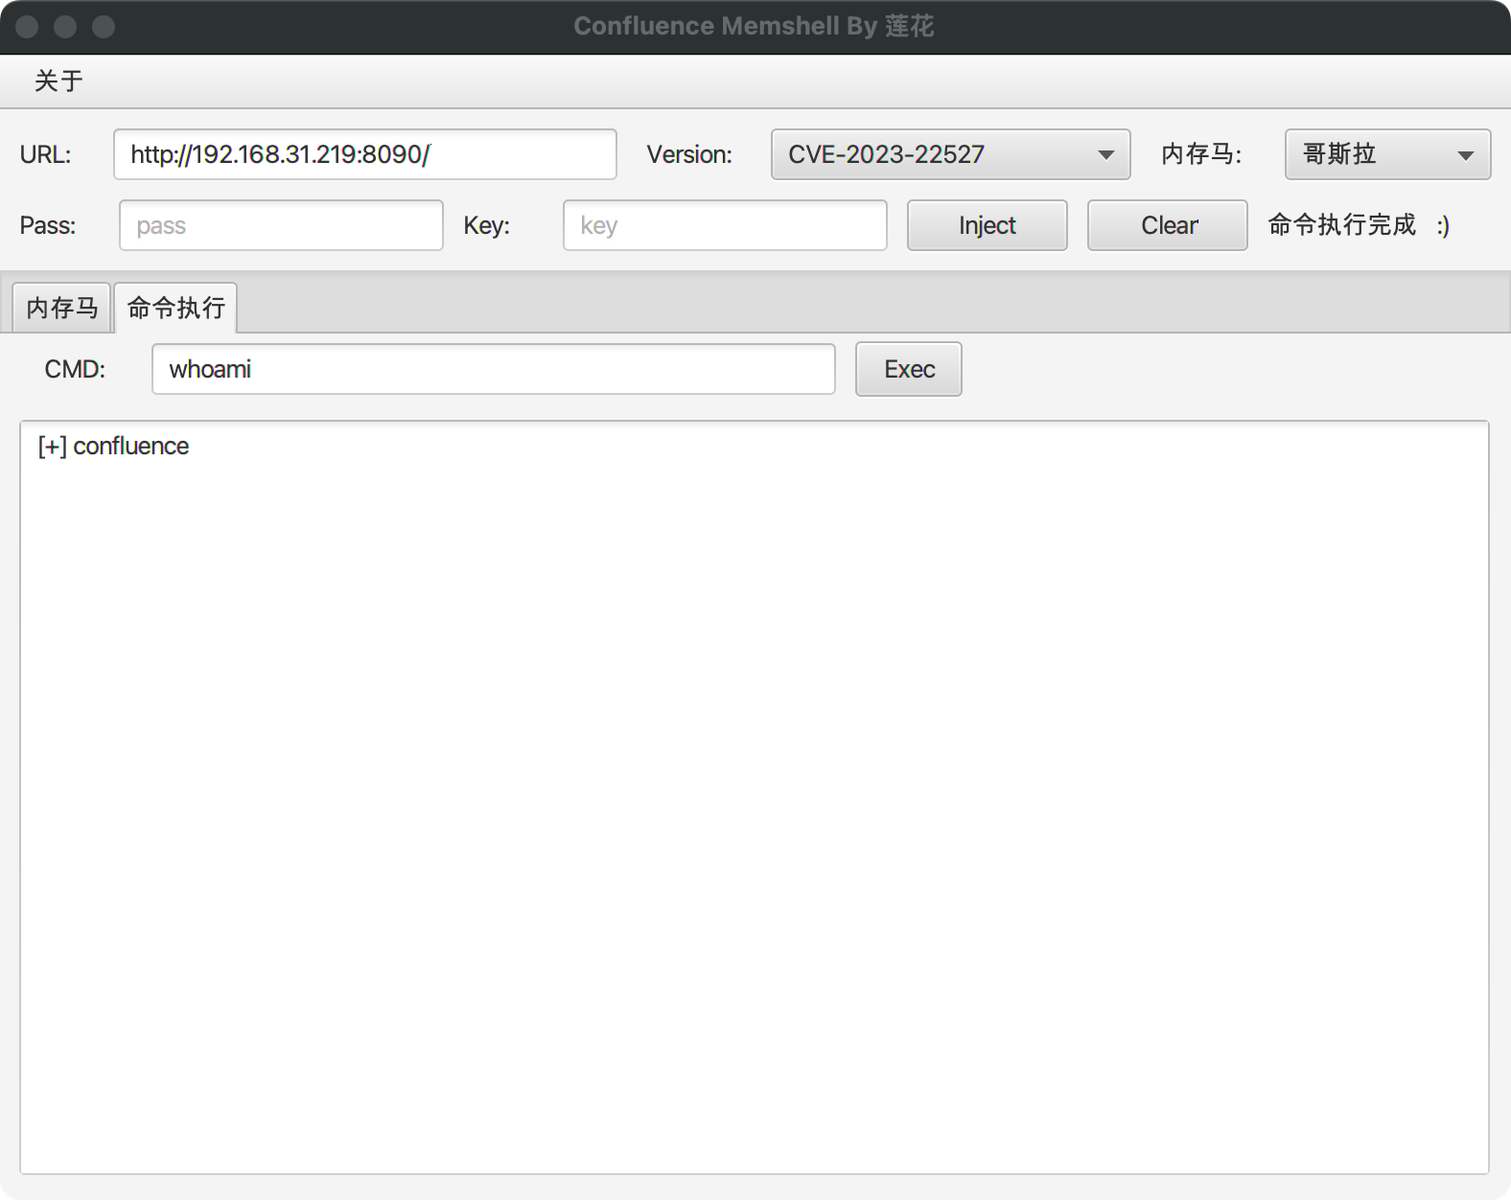
image
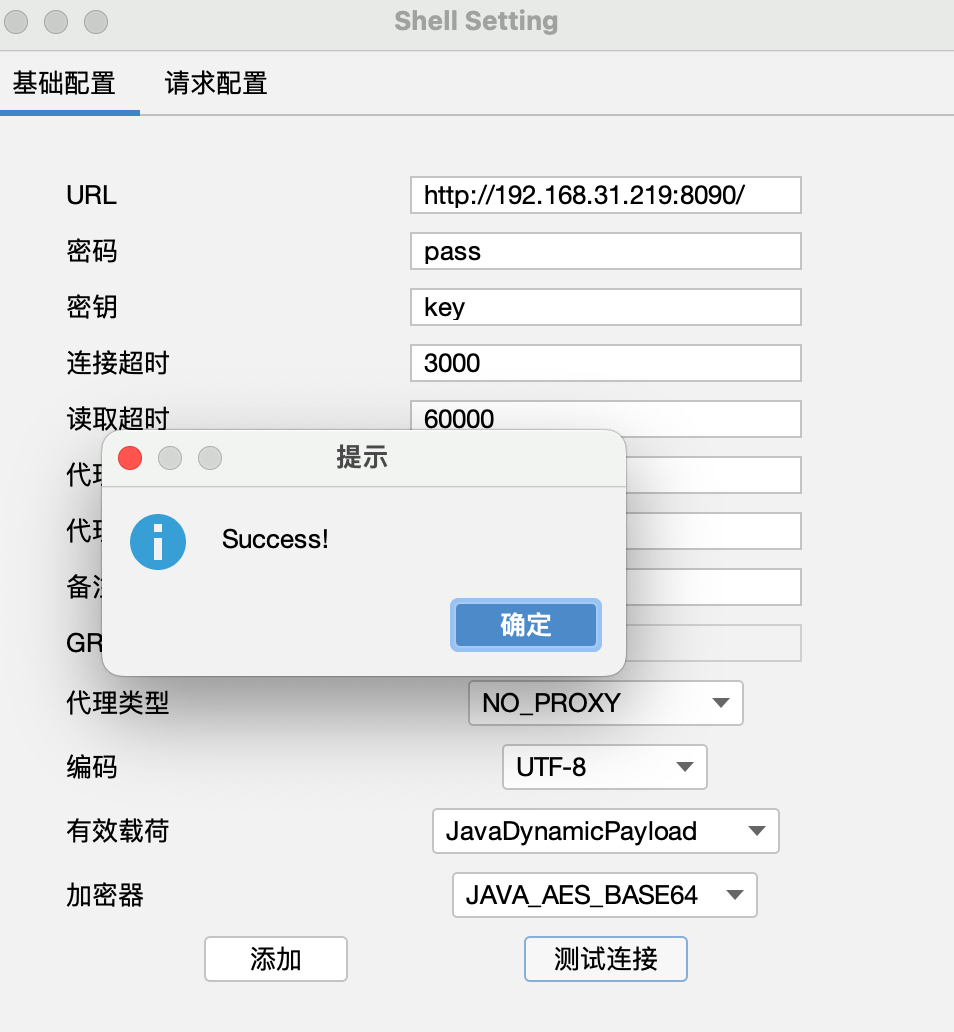
  1. Memory shell injection (the same applies to other CVE versions)
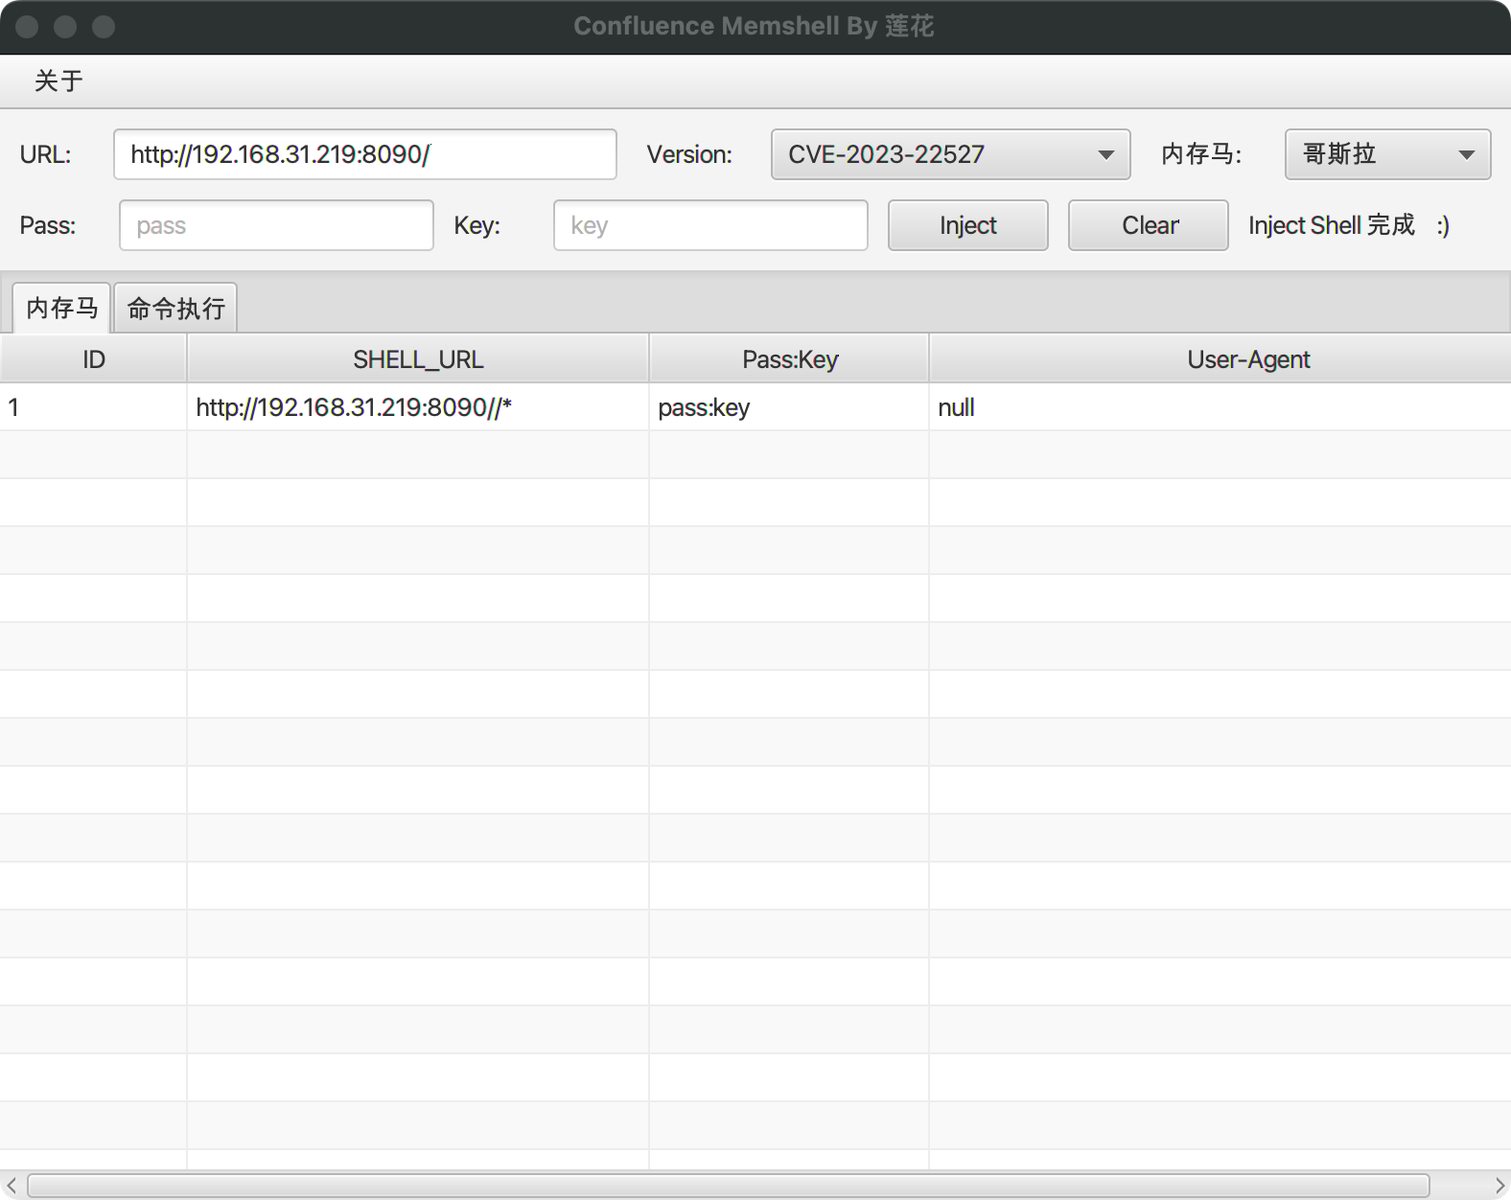
  • Godzilla
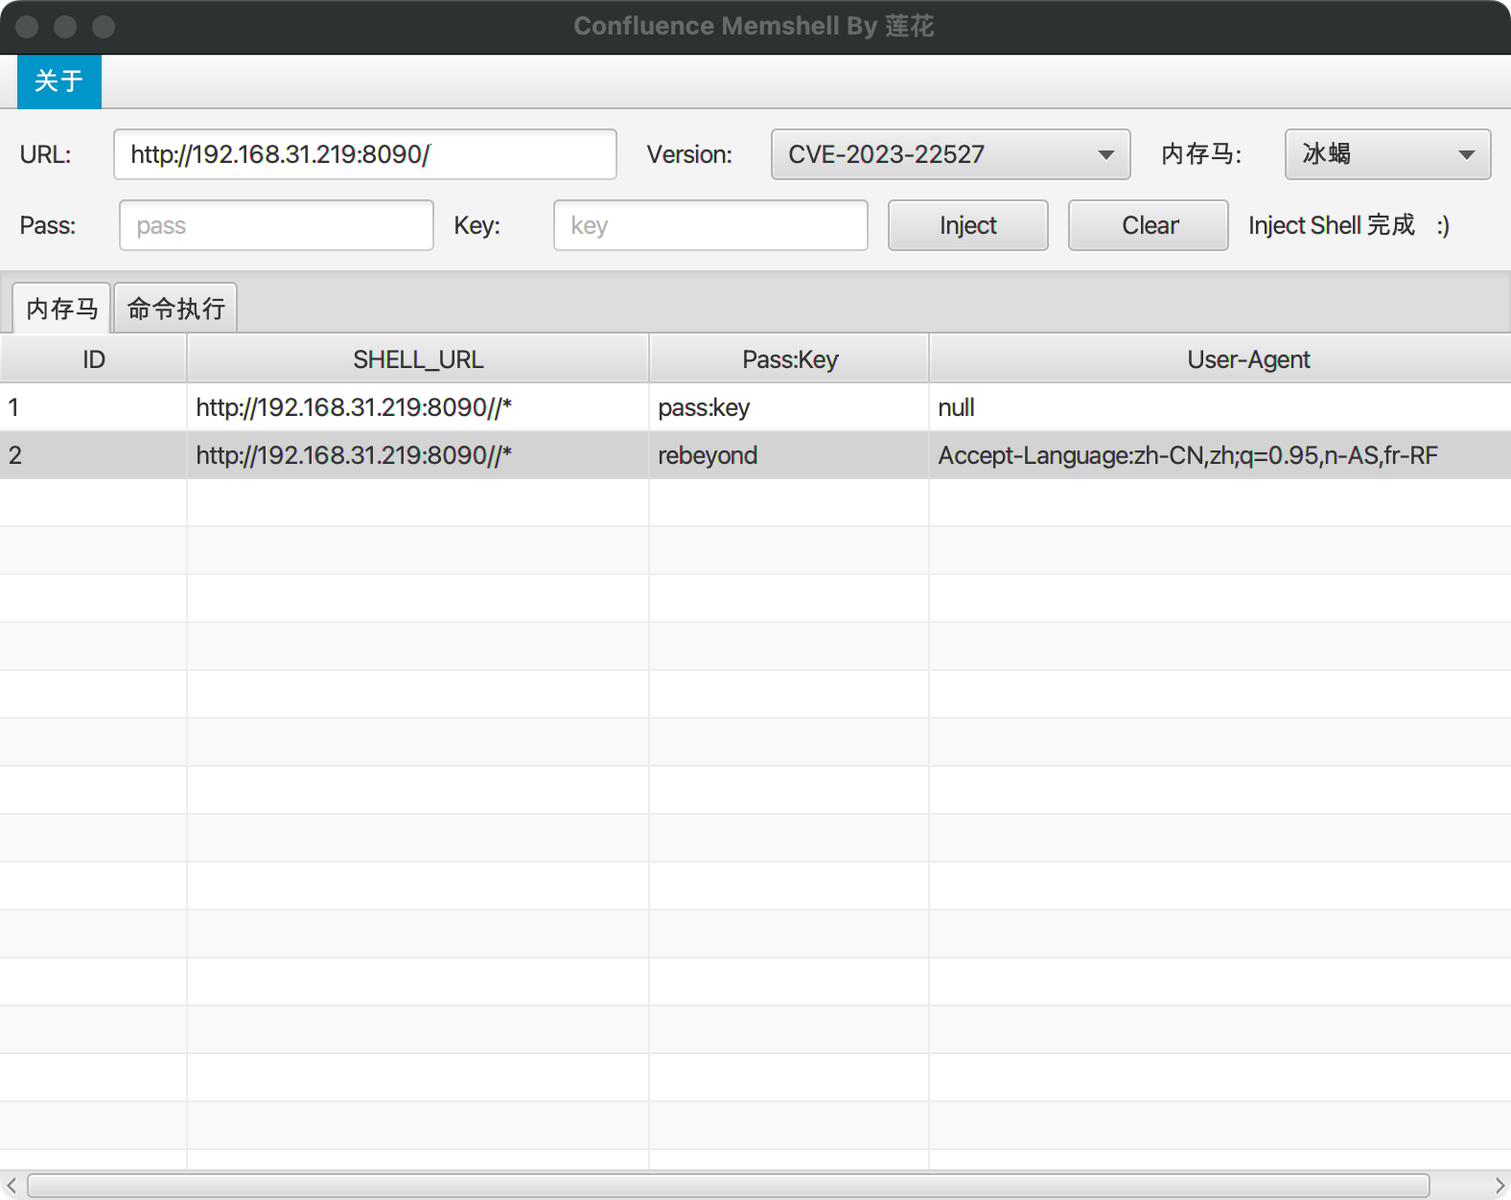
image image
  • Behinder
image image

References

https://github.com/BeichenDream/CVE-2022-26134-Godzilla-MEMSHELL https://github.com/aaaademo/Confluence-EvilJar

Disclaimer

This tool can only be used in enterprise security construction with sufficient legal authorization. During the use of this tool, you should ensure that all your actions comply with local laws and regulations.

If you engage in any illegal behavior during the use of this tool, you will bear all consequences yourself, and all developers and all contributors of this tool assume no legal or joint liability.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →