

ARES
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
cloud-securitycommand-and-controldefensive-tools+5
582
mafifrizi/aresAutonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
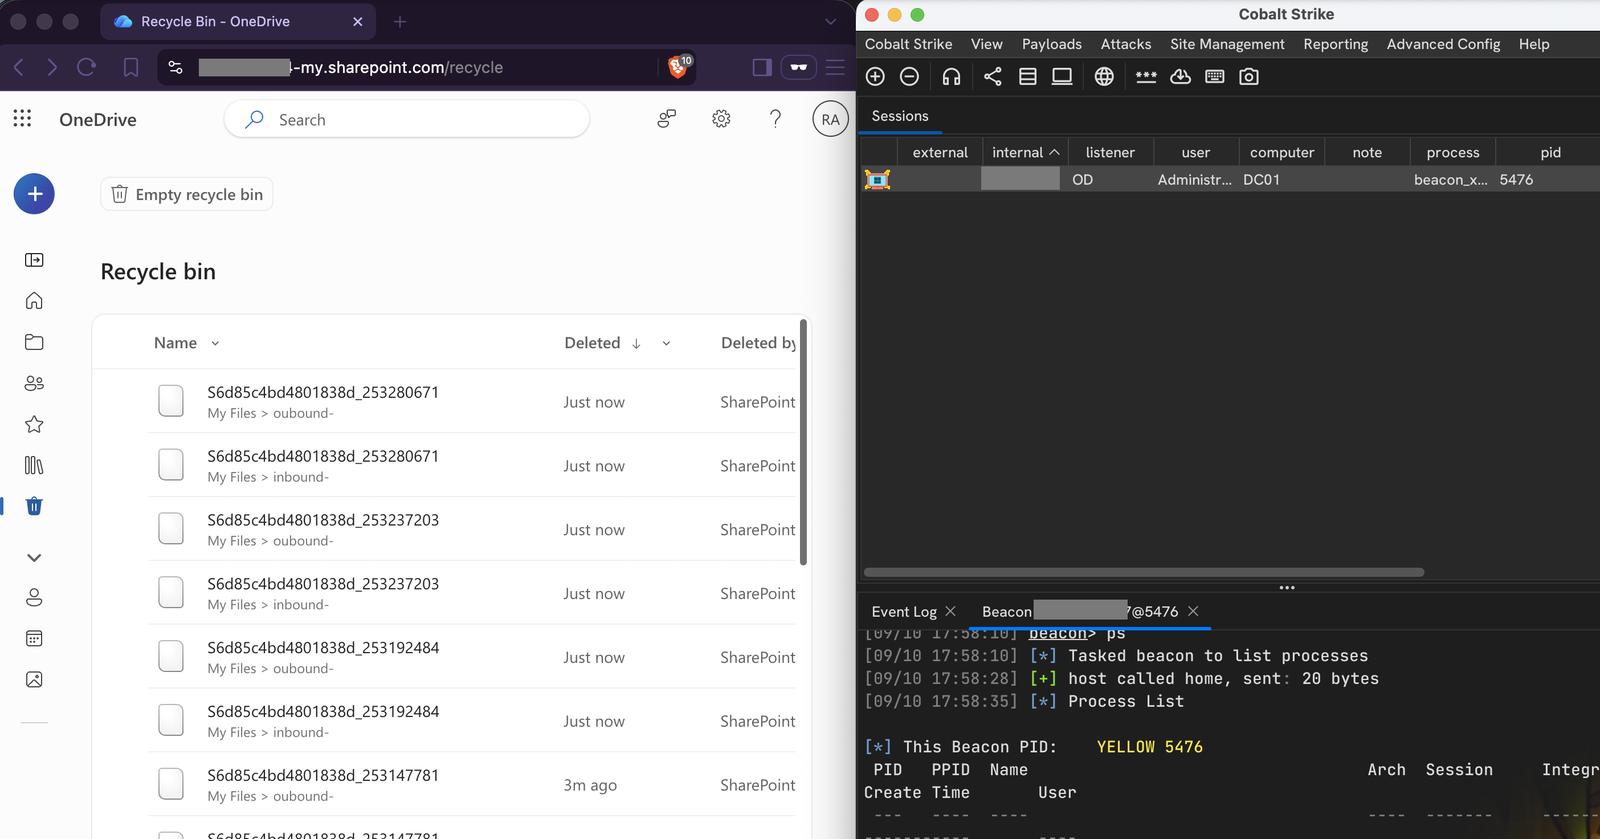 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
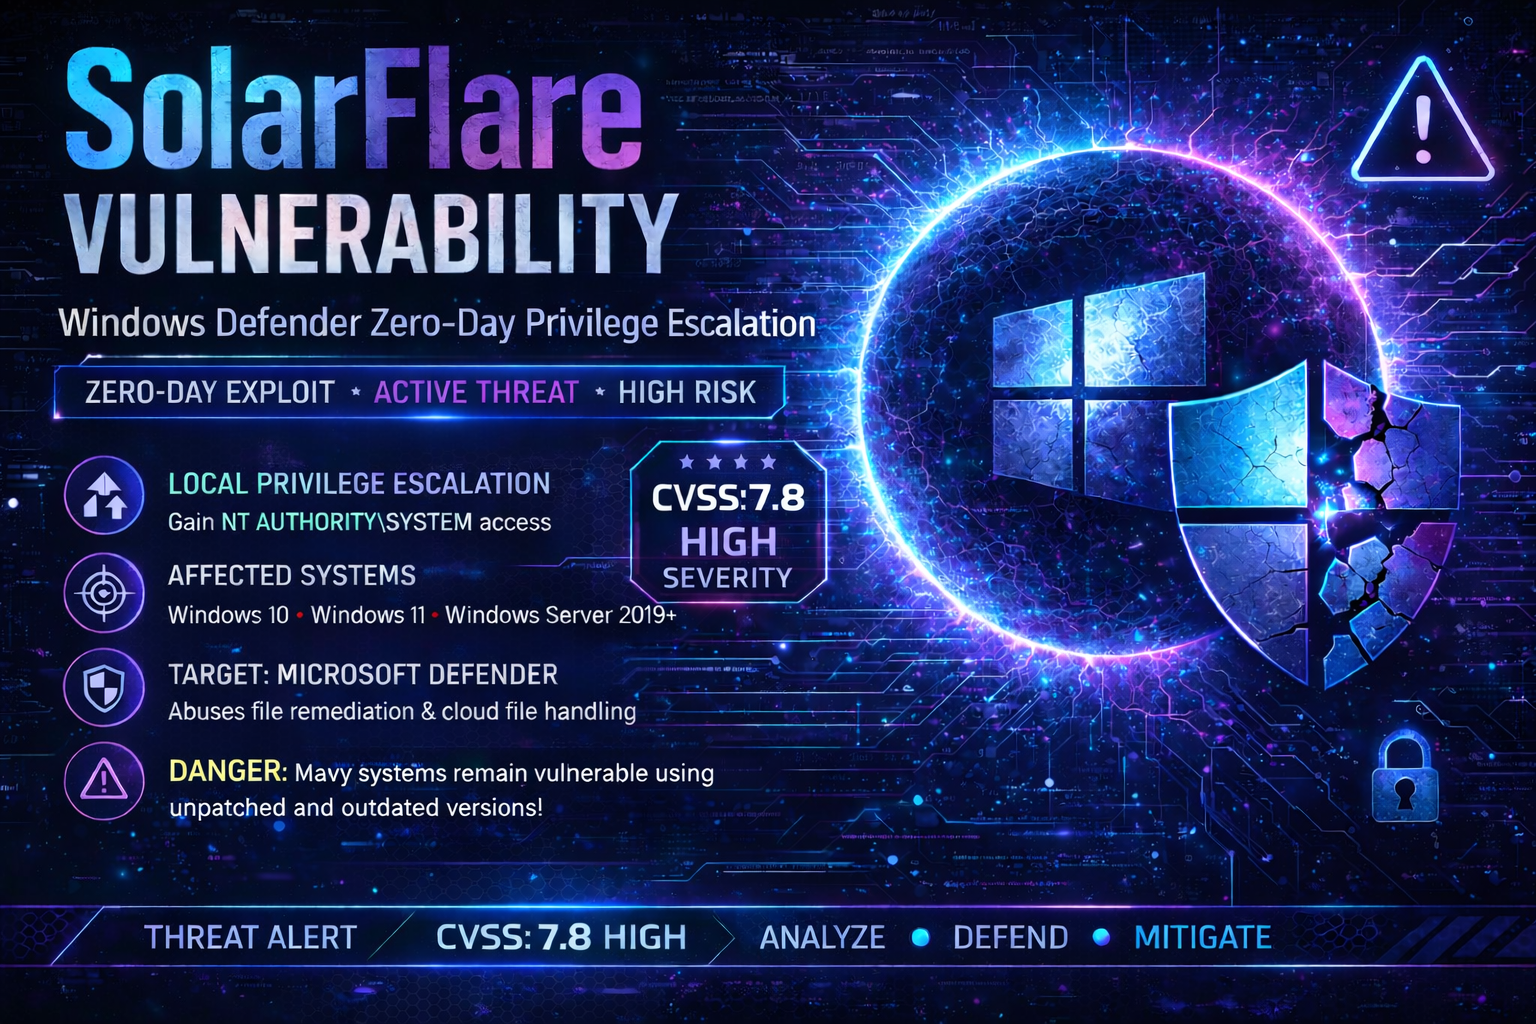 tc4dy/cve-2026-41091-poc-exploit
CVE-2026-41091 RedSun | Microsoft Defender LPE exploit. Low-privileged users gain NT AUTHORITY\SYSTEM 🔥 via Cloud Files API + NTFS junction…
 gmh5225/cve-2022-44721-csfalconuninstaller
Exploit for CVE-2022-44721 that bypasses CrowdStrike Falcon uninstall protection token check on Windows, allowing attackers with admin privileges to…
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 28zaaky/khaos-c2
KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.
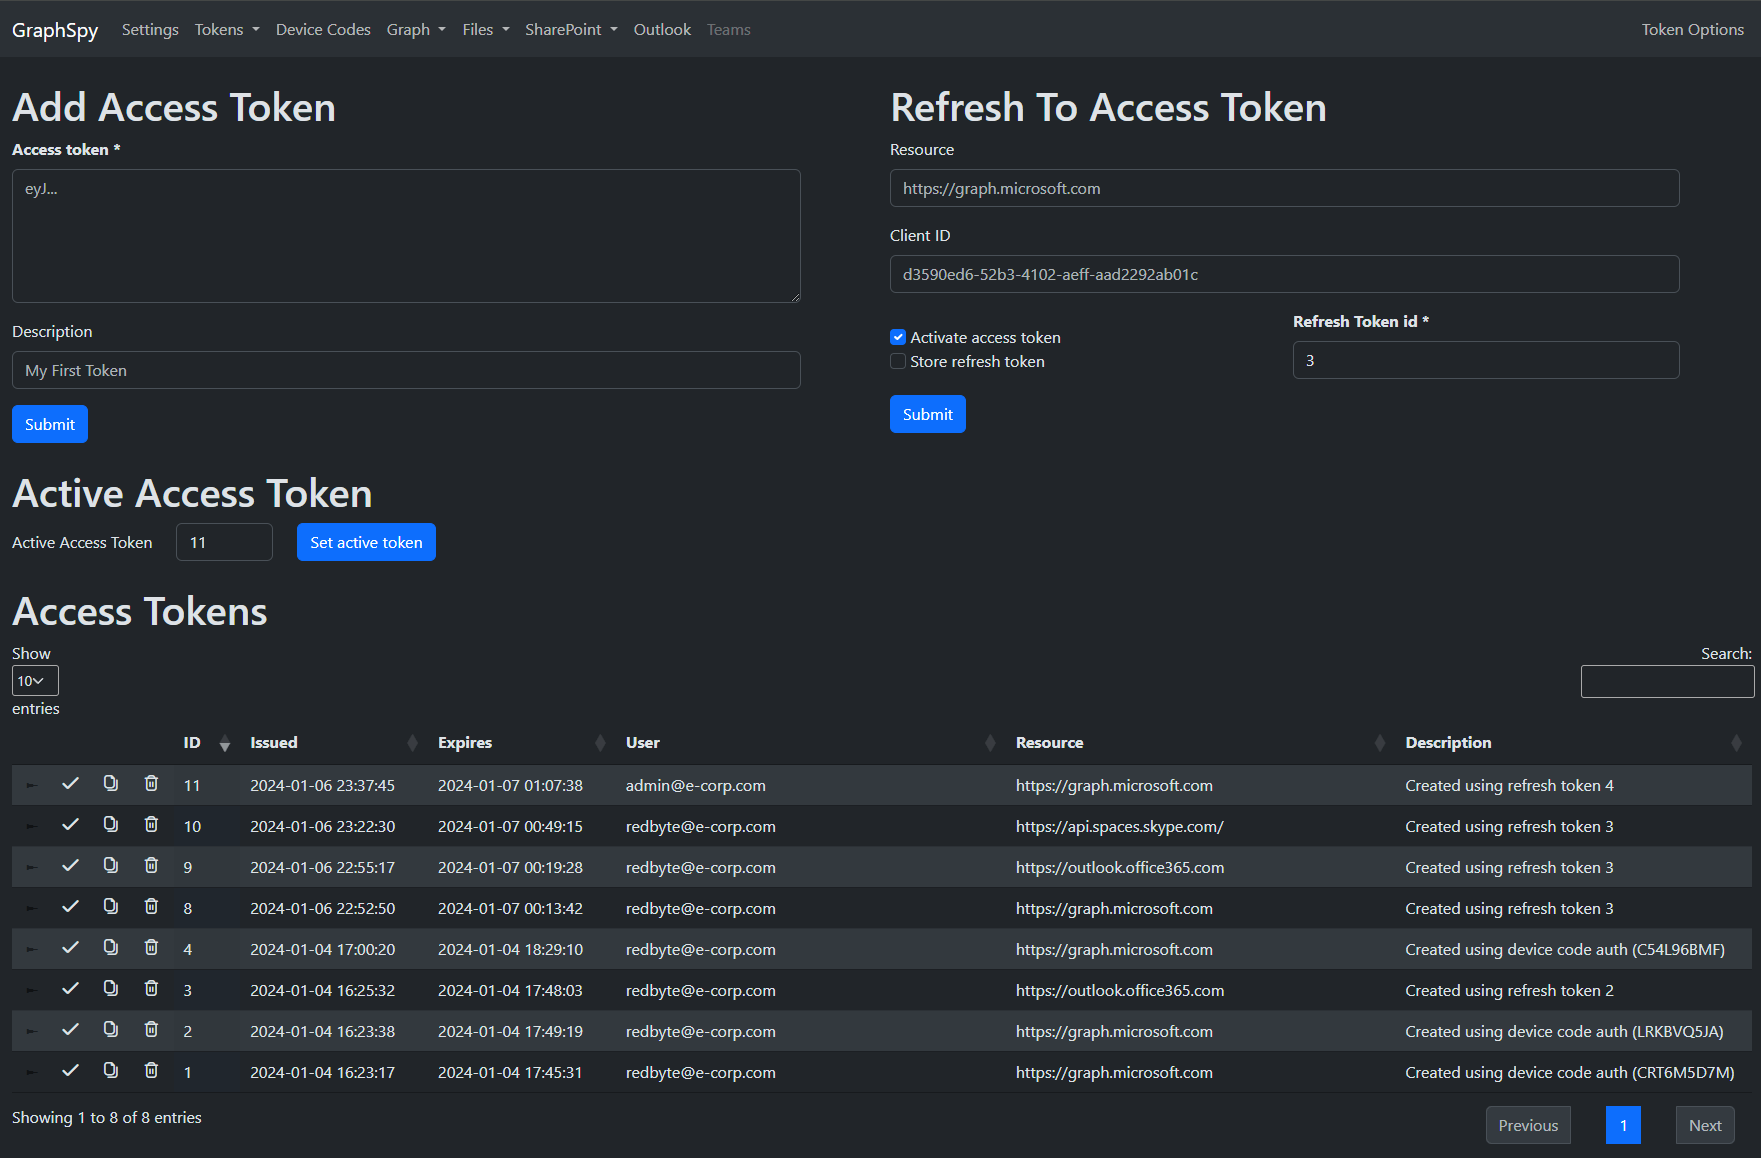 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
 paradoxis/adsyncdump-bof
The ADSyncDump BOF is a port of Dirk-Jan Mollema's adconnectdump.py / ADSyncDecrypt into a Beacon Object File (BOF) with zero dependencies.
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it