 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA tracking for detection development.

This tool is used to emulate attack patterns inside of the AWS Controlplane. Each attack is tagged with a specific UA for the blue team to signal off of.
This is still an active work in progress. **Lots of Bugs
Not ready for production
Where to file issues: https://github.com/grines/scour/issues
Maintained by: grines
Scour is a modern module based AWS exploitation framework written in golang, designed for red team testing and blue team analysis. Scour contains modern techniques that can be used to attack environments or build detections for defense.
Scour is written in golang so its easy to ship around as a binary.
##Gettable
go get github.com/grines/scour
##Build
go build main.go
For a more detailed and user-friendly set of user instructions, please check out the Wiki's installation guide. **coming soon
Scour uses a range modules:
The first time Scour is launched,
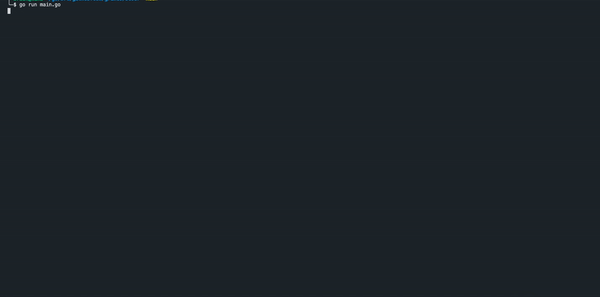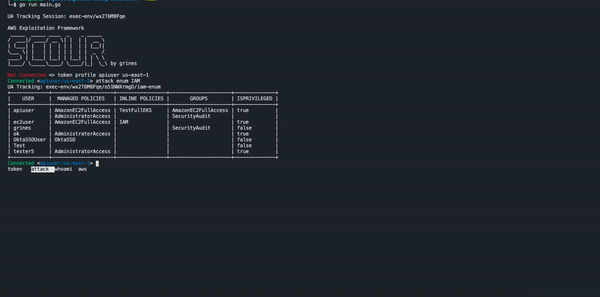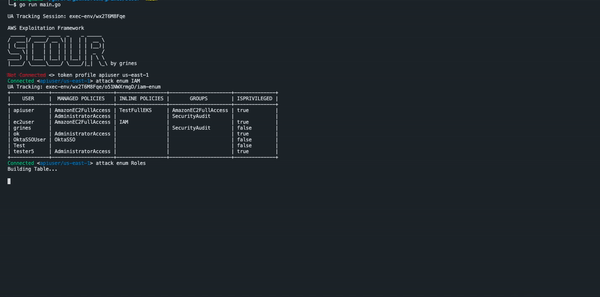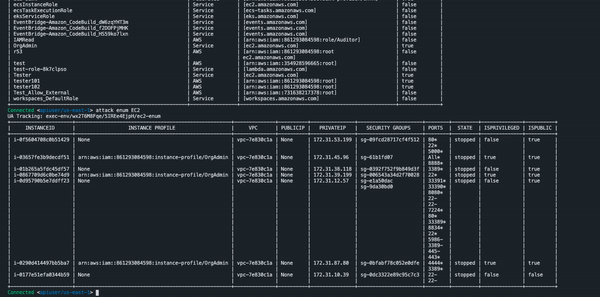
token profile <profile_name> <region> will list the available aws profiels stored in ~/aws/credentials.token AssumeRole <role_name> <region> will assume role from same or cross account. ** requires active sessionhelp module will return the applicable help information for the specified module. **help TBDattack evasion <tactic> will run the specified module with its default parameters.scour will enter cli modeNot Connected <> token profile apiuser us-east-1 sets the session to use for commands that require oneConnected <apiuser/us-east-1> actively connected to an aws profile from (~,/aws/credentials) in (region)Connected <apiuser/us-east-1> attack enum <attack> tab completion with list available enumeration tacticsConnected <apiuser/us-east-1> attack privesc <attack> tab completion with list available privilege escalation tacticsConnected <apiuser/us-east-1> attack lateral <attack> tab completion with list available lateral tacticsConnected <apiuser/us-east-1> attack evasion <attack> tab completion with list available evasion tacticsConnected <apiuser/us-east-1> attack creds <attack> tab completion with list available credential discovery tacticsConnected <apiuser/us-east-1> attack execute <attack> tab completion with list available execution tacticsConnected <apiuser/us-east-1> attack persist <attack> tab completion with list available persistance tacticsConnected <apiuser/us-east-1> attack exfil <attack> tab completion with list available exfiltration tactics