

Koi
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
37
b3rt1ng/koiMulti-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra - taken past the base PoC to show how a common…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
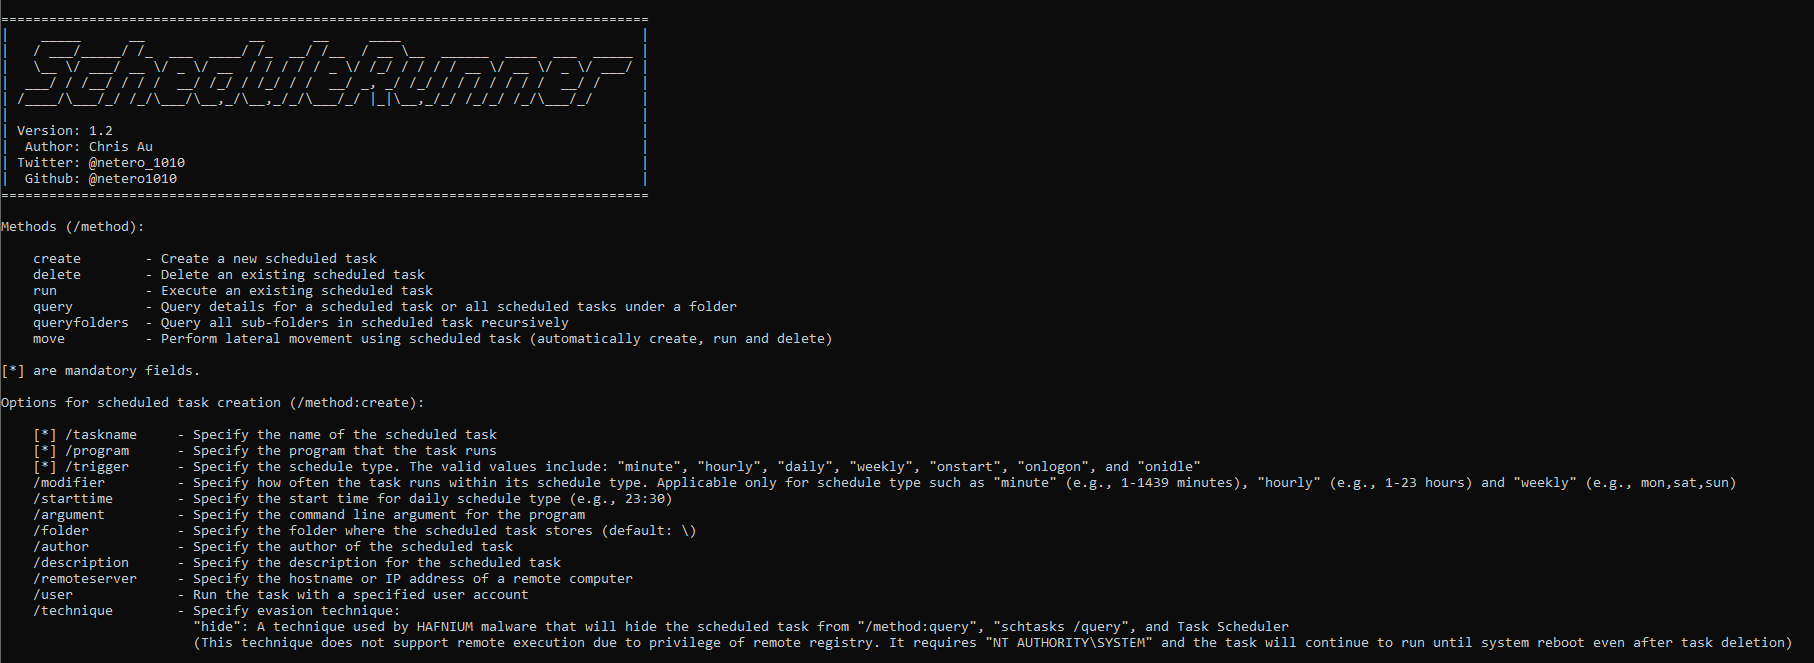 netero1010/schedulerunner
A C# tool with more flexibility to customize scheduled task for both persistence and lateral movement in red team operation
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
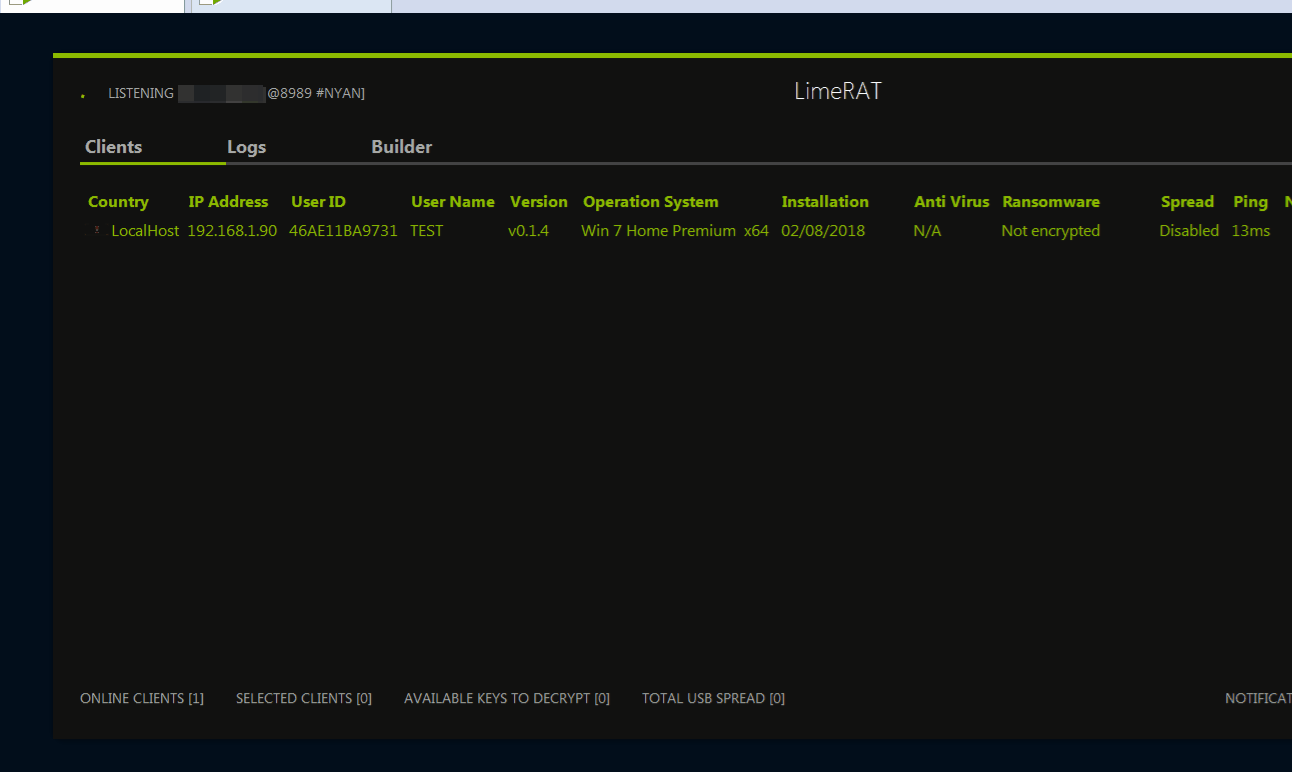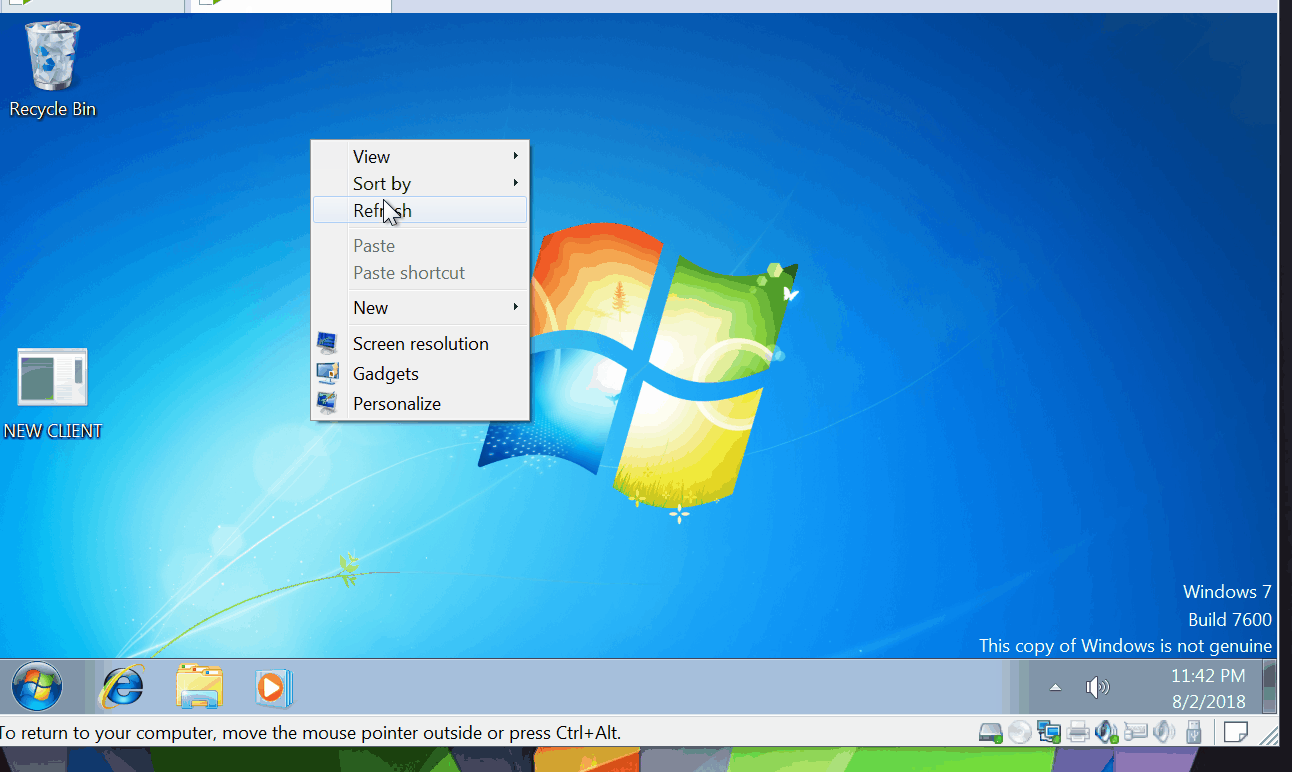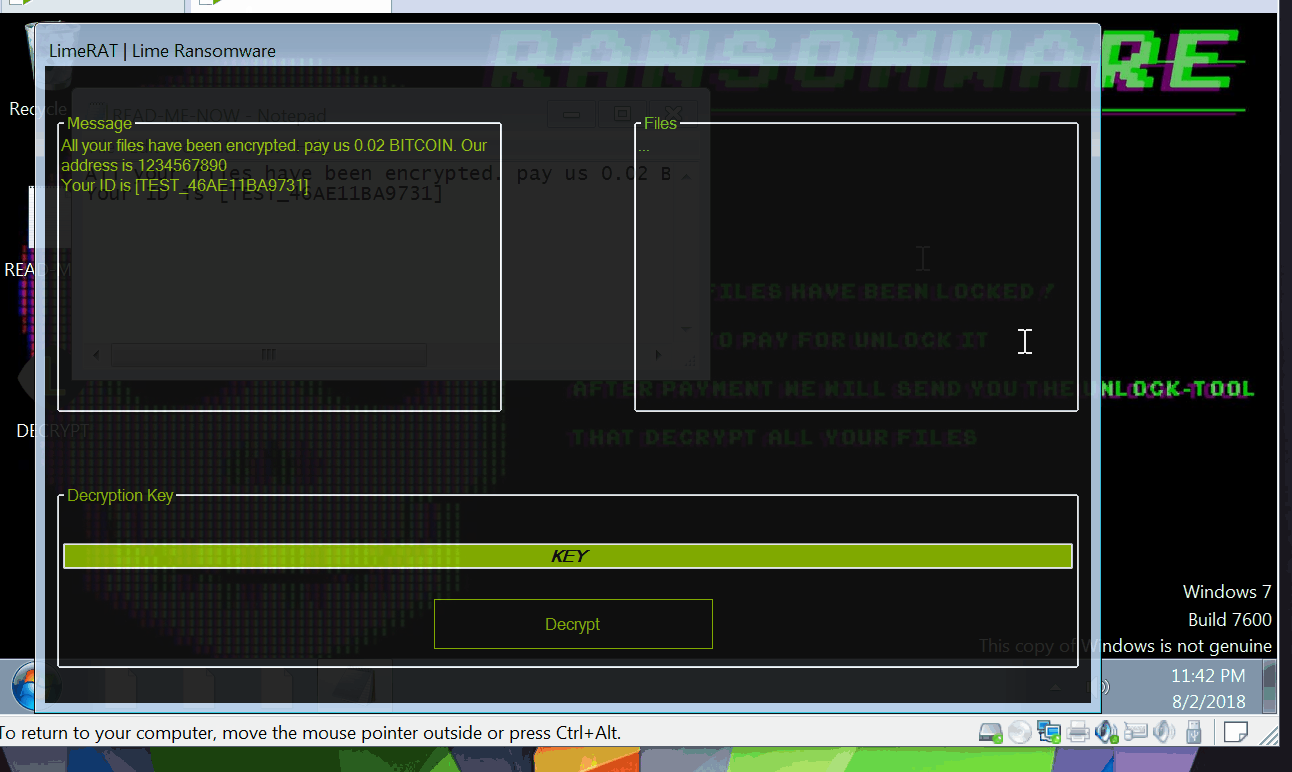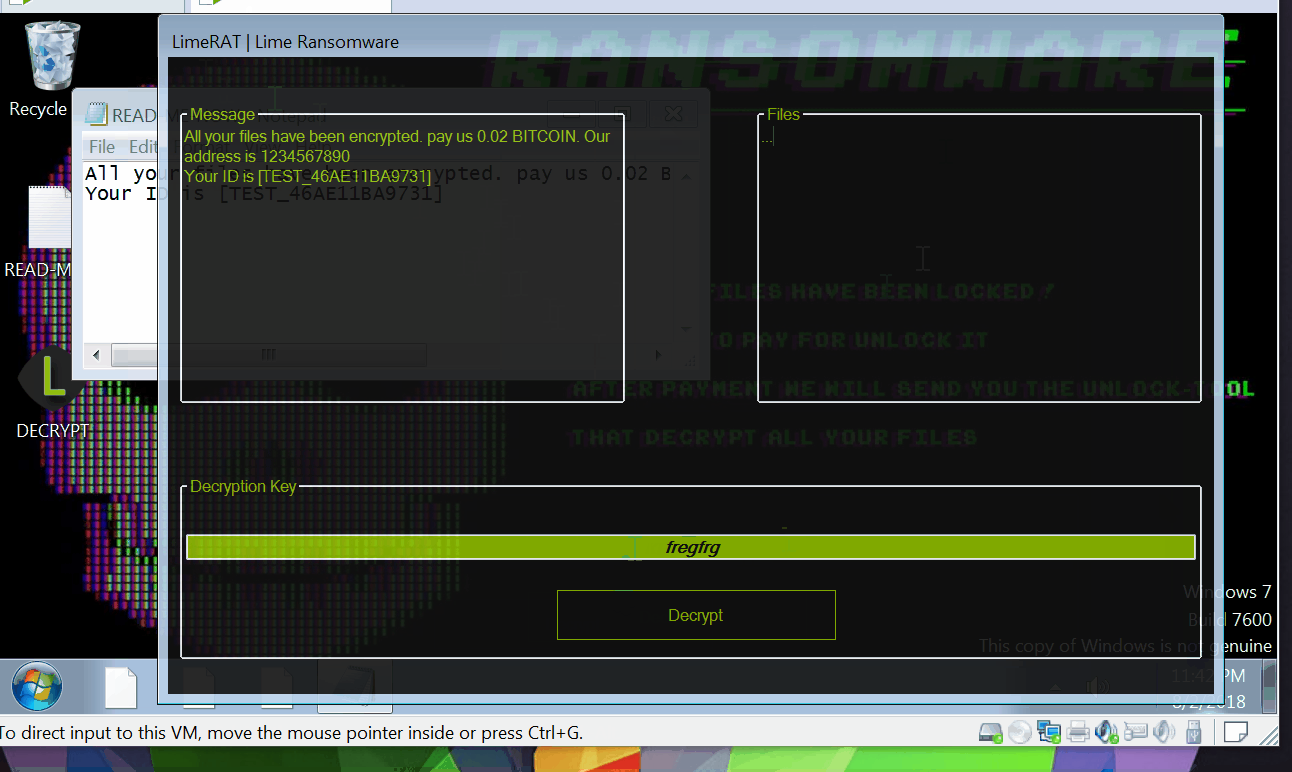 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 asekon/rootkit
A rootkit for ubuntu-16.04.6 (Linux 4.4). Can hide a process, give root access and hide itself