

CVE-2026-34910-PoC
 boreas37/cve-2026-34910-poc
CVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
api-security-testingauthenticationexploitation+3
7
boreas37/cve-2026-34910-pocCVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
 yutusec/apisix_crack
Apisix系列漏洞:未授权漏洞(CVE-2021-45232)、默认秘钥(CVE-2020-13945)批量探测。
 hannah-portswigger/totpauthenticate
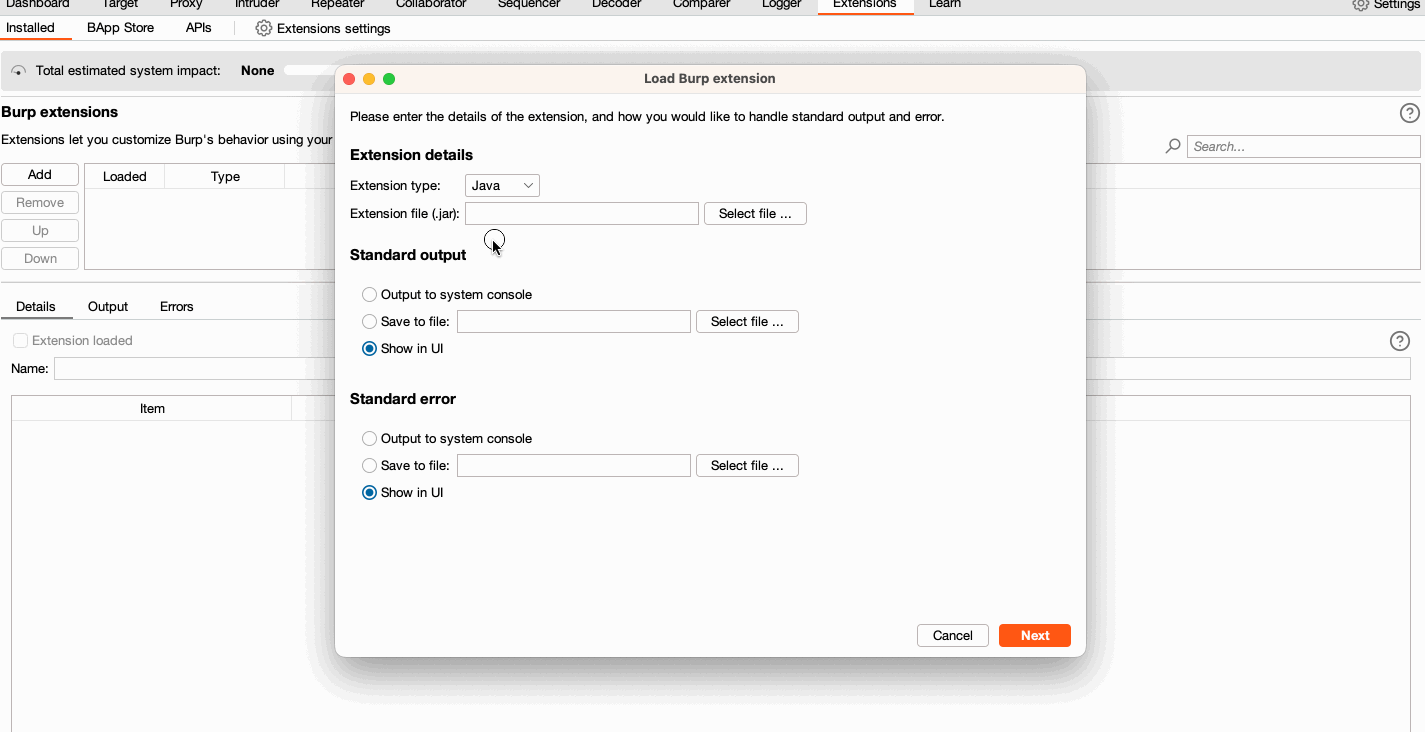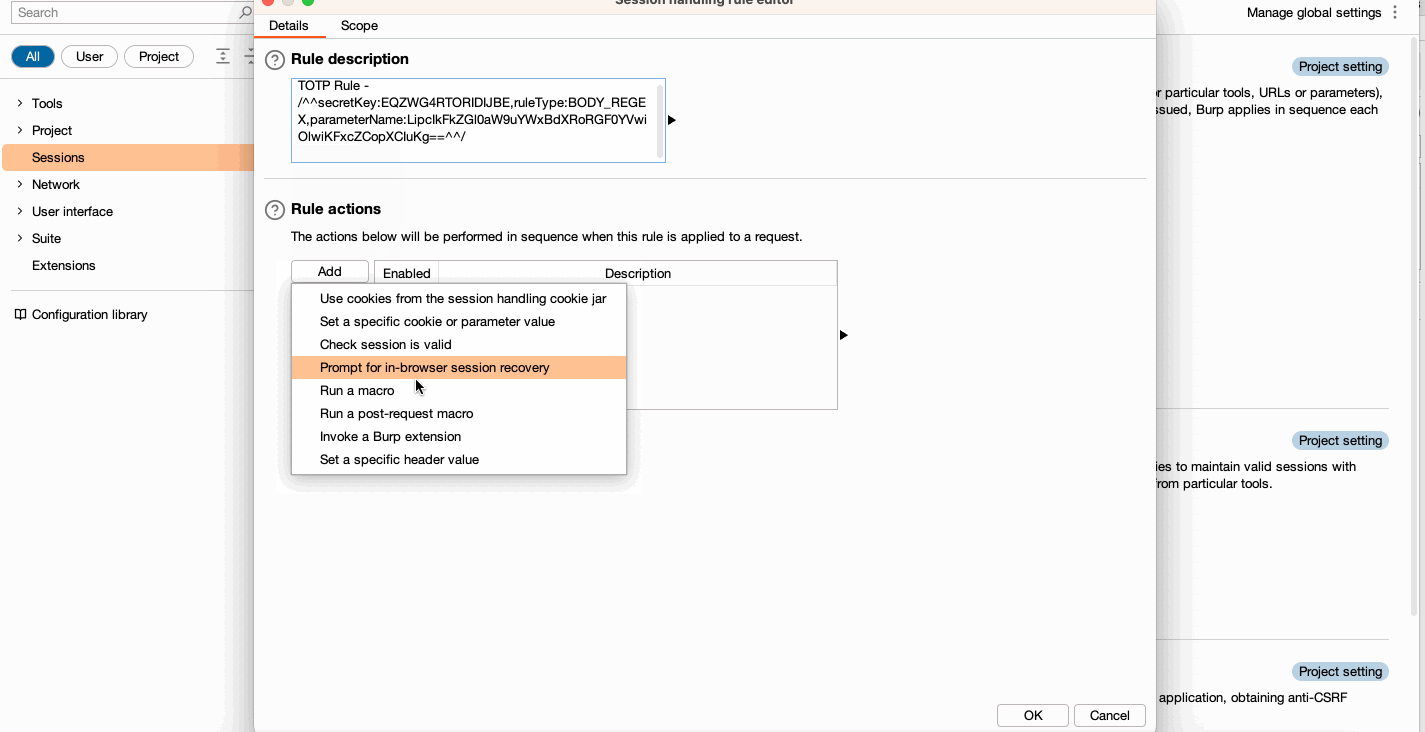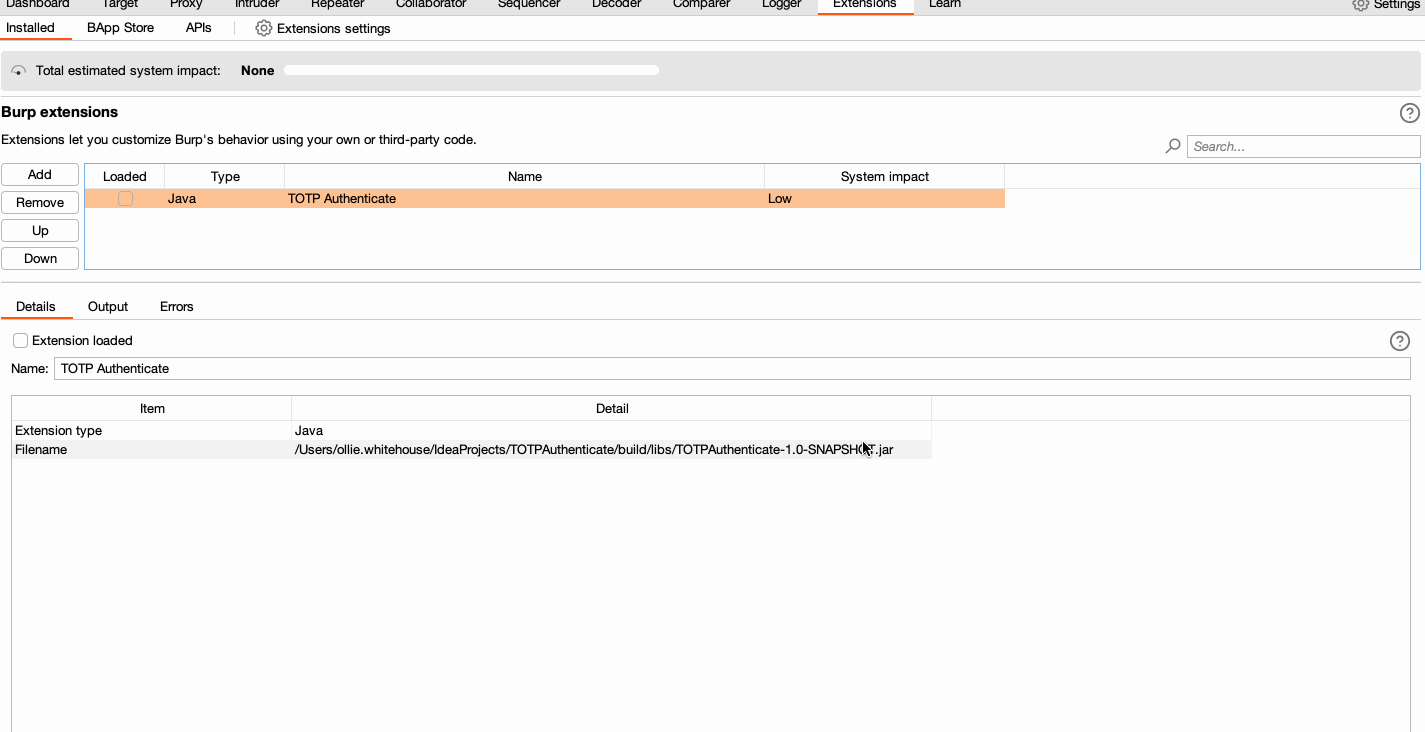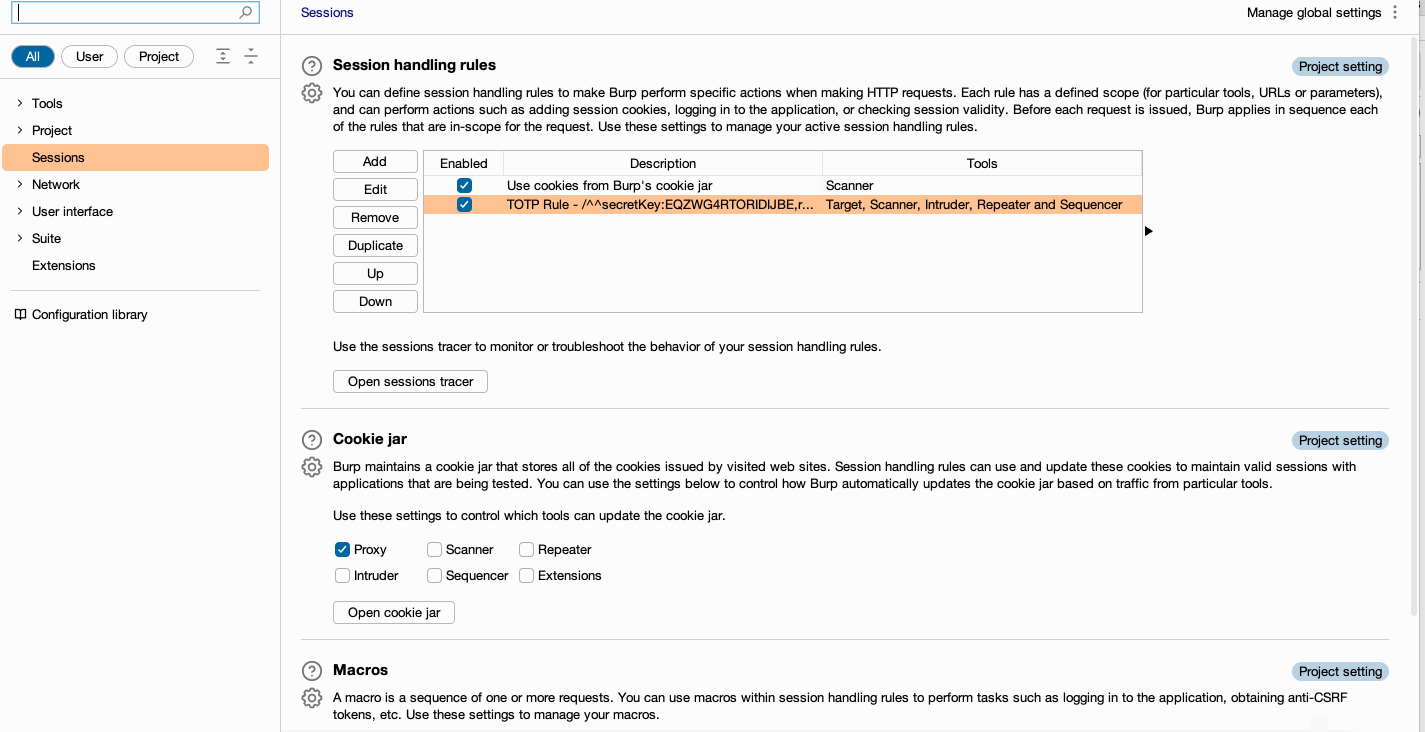
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
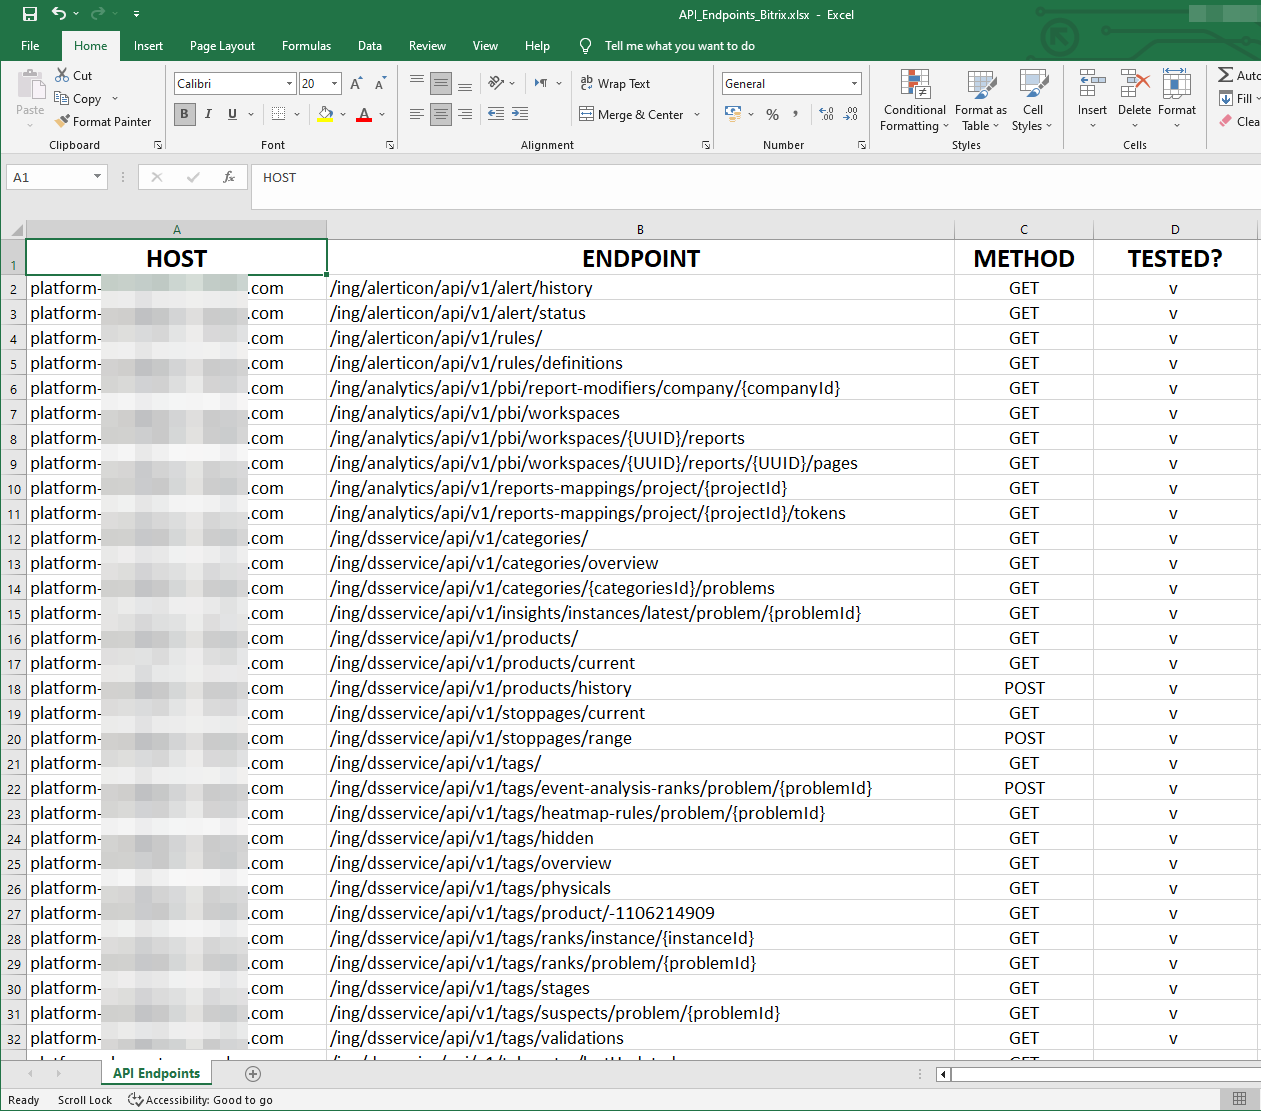 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 yutusec/spel
Spring Cloud Gateway Actuator API SpEL表达式注入命令执行(CVE-2022-22947)批量检测工具
 hunzi0/cve-2022-22947-rce_poc
批量url检测Spring-Cloud-Gateway-CVE-2022-22947
 ajinabraham/oauth-request-crafter
OAuth Request Crafter
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 hunt-benito/your-bot-my-inbox-cve-2026-68929-fastgpt-unauthenticated-wechat-channel-hijack
Proof-of-concept exploit for CVE-2026-68929, demonstrating unauthenticated cross-tenant takeover of FastGPT WeChat channels via public shareId,…
 infobyte/alexafaraday
Alexa skill example for Faraday API
 licitrasimone/cve-2026-75157-poc
Standalone authorized universal HTTP PoC for CVE-2026-75157
 isaca0315/cve-2026-65013-bola-idor
Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners