subdomain-bruteforce-list

Large wordlist (34M+ entries) for subdomain bruteforcing and DNS reconnaissance during penetration testing and attack surface discovery.

Large wordlist (34M+ entries) for subdomain bruteforcing and DNS reconnaissance during penetration testing and attack surface discovery.

Wordlist of virtual host names for vhost discovery and enumeration during web reconnaissance, designed for use with virtual-host-discovery and…

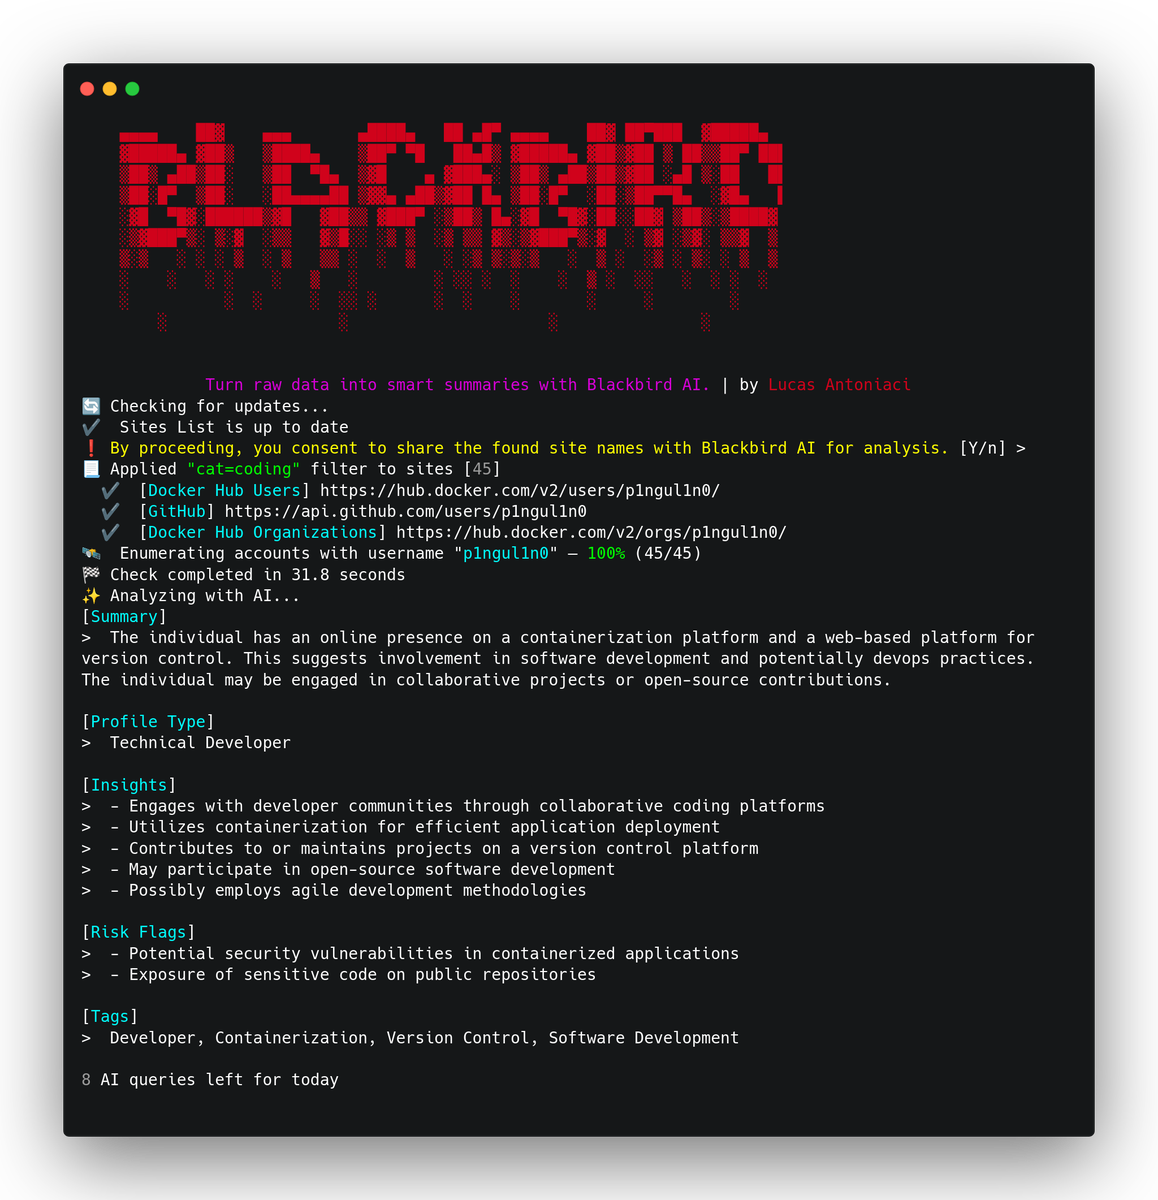
An OSINT tool to search for accounts by username and email in social networks.

About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers

C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…

Fast HTTP parameter discovery for authorized security testing

Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.

Terminal UI for attack surface discovery: DNS recon, subdomain enumeration, port scanning, reverse IP, leaked login URLs, and JavaScript secret…

Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…

Forgejo 16.0.5 - High - Remote - SSRF - OpenID discovery fetches attacker-controlled URLs

Proof-of-concept and analysis for CVE-2023-5612, a GitLab CE/EE webhook SSRF. Includes curl PoC steps and custom NSE scripts to verify and…

Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…

Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…

Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…

Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…

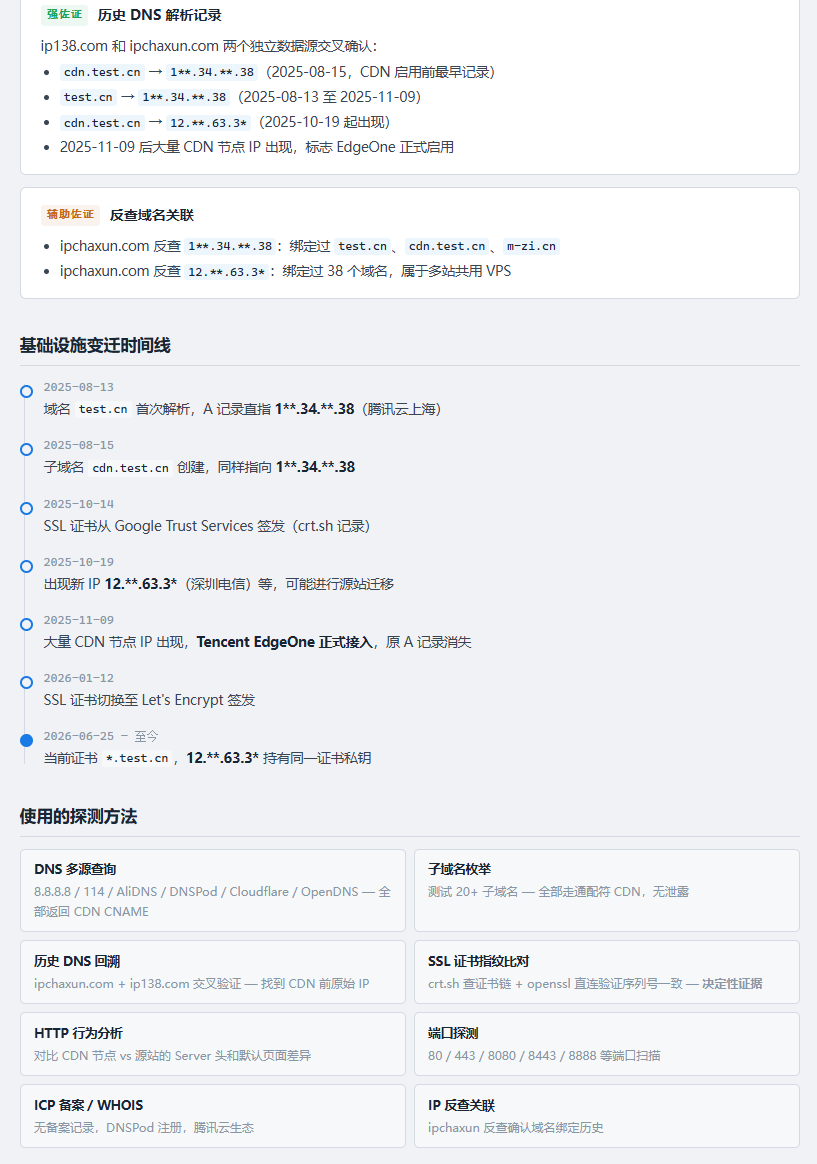
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…

Exploit for CVE-2024-29269 enabling unauthenticated OS command execution on TLR-2005KSH routers, with ZoomEye and Leakix dork queries for target…

Python 3 checker and exploit helper for CVE-2026-19658, a WordPress Give Tributes PHP object injection flaw, with FOFA target discovery and legacy…