
Atomic-Red-Team-C2
ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…

ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…

FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…

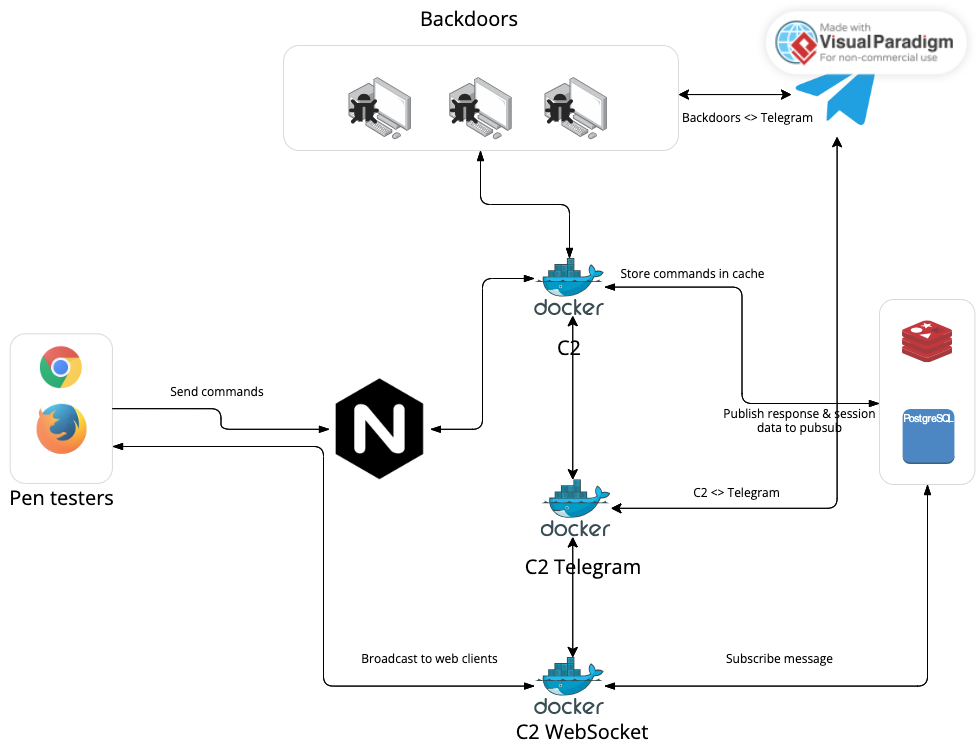
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…

DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…

A collaborative web exploitation framework.

The Havoc Framework

A webshell framework for penetration testers.

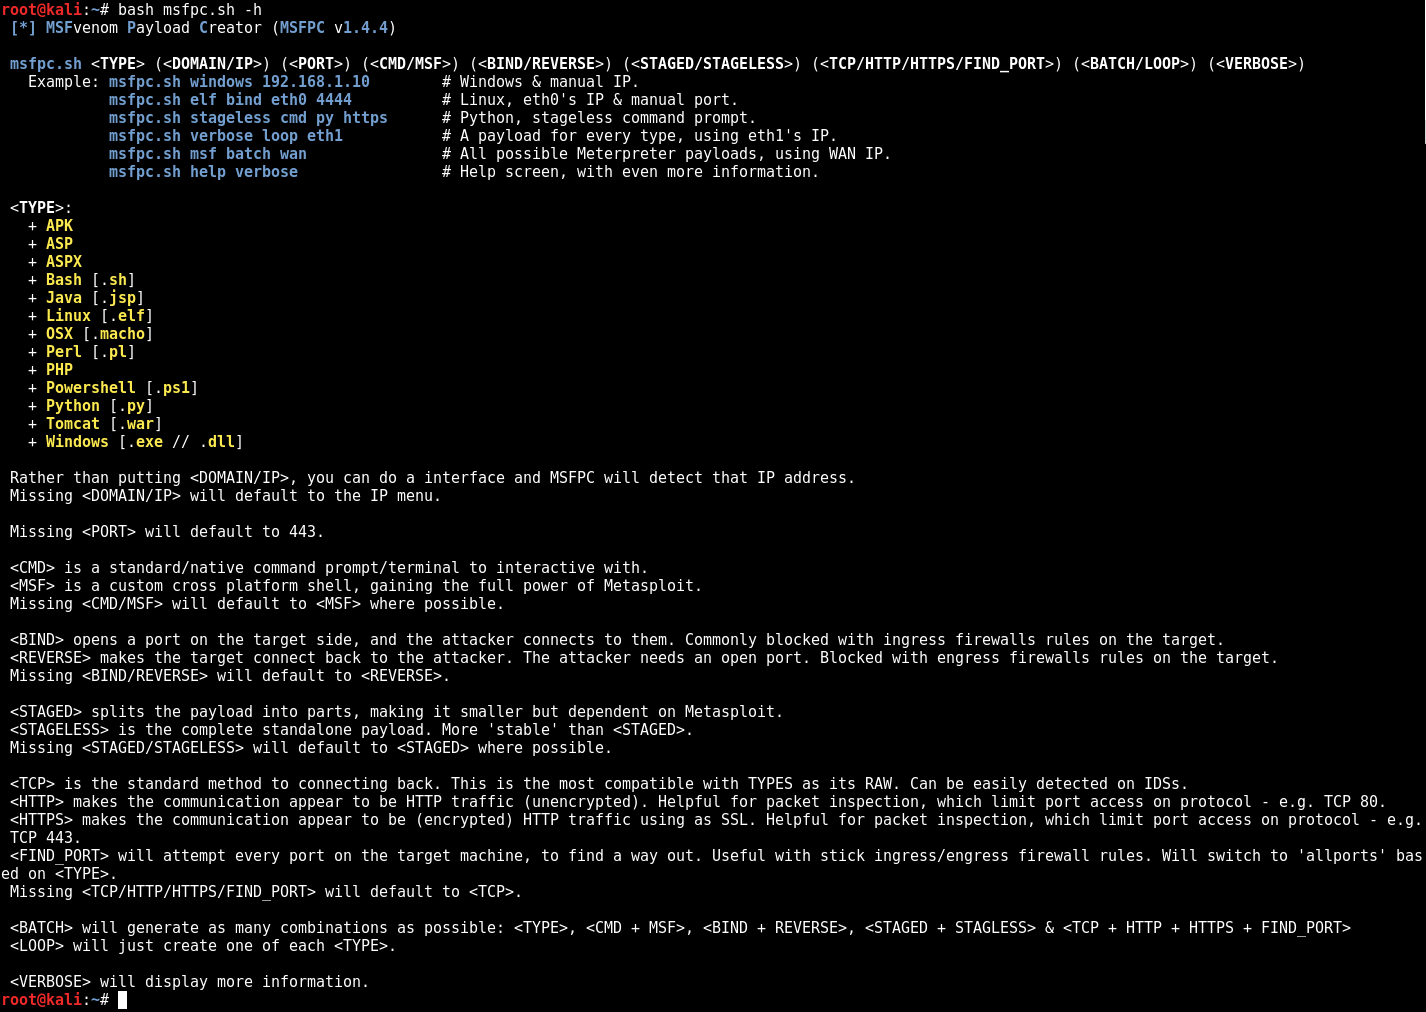
MSFvenom Payload Creator (MSFPC)

Powershell C2 Server and Implants

Automated Mass Exploiter

PowerShell Runspace Post Exploitation Toolkit

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Undetectable Windows Payload Generation

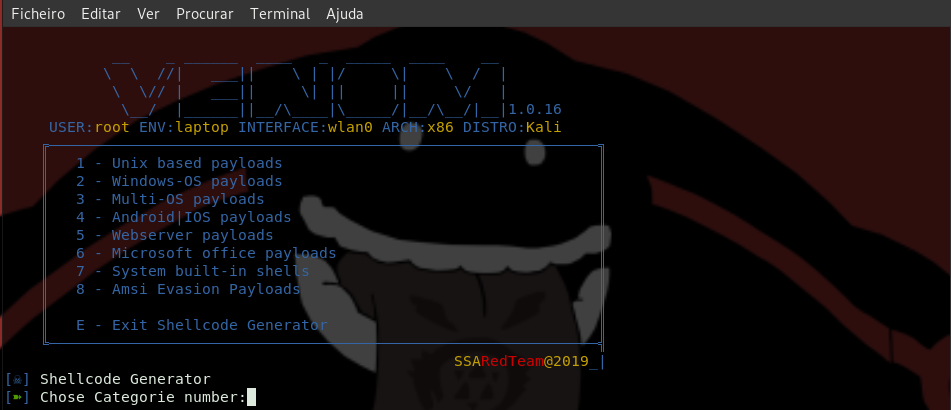
venom - C2 shellcode generator/compiler/handler

generate CobaltStrike's cross-platform payload

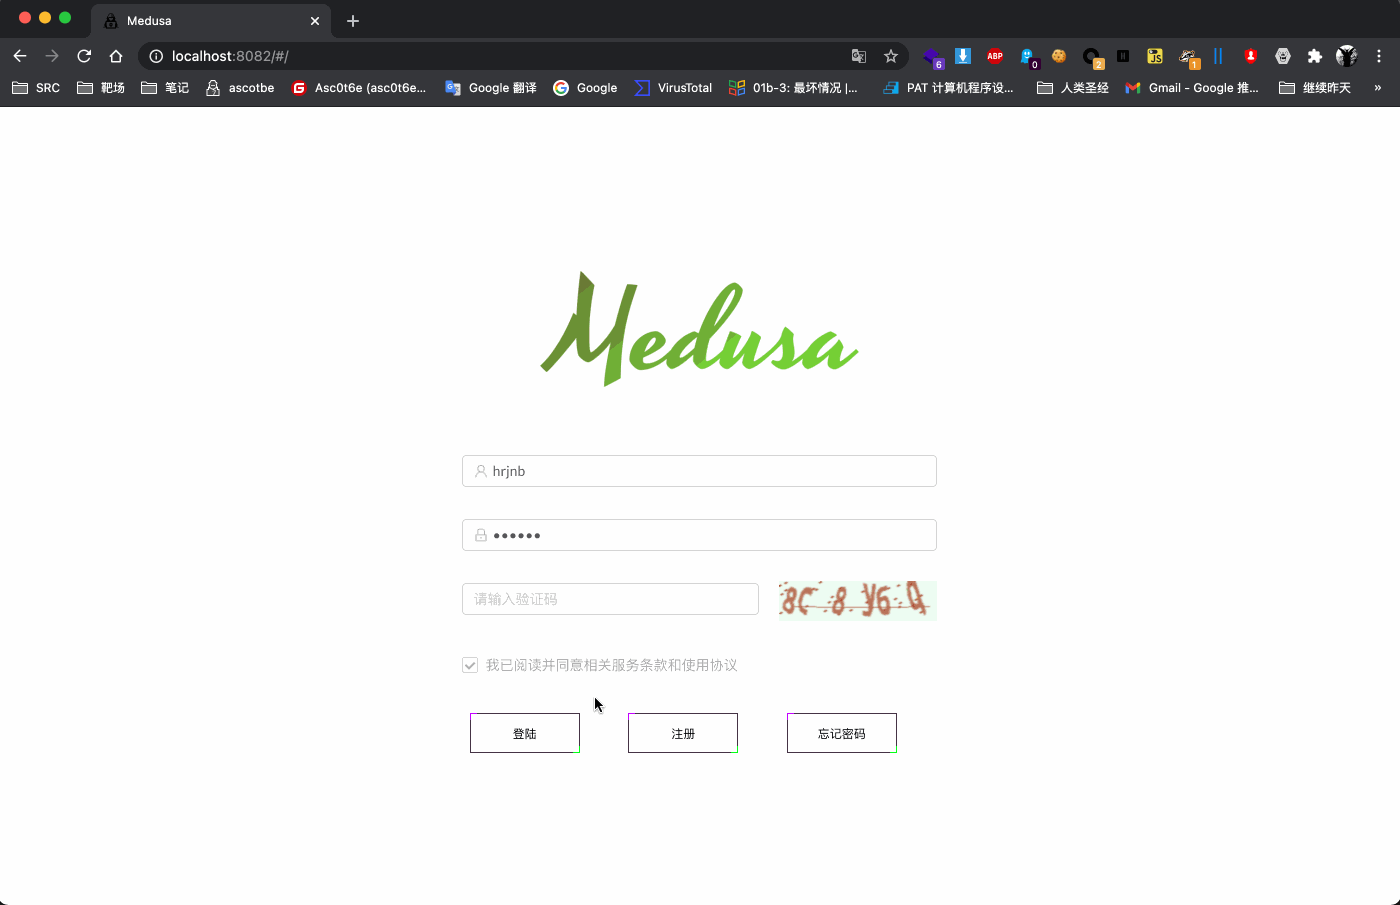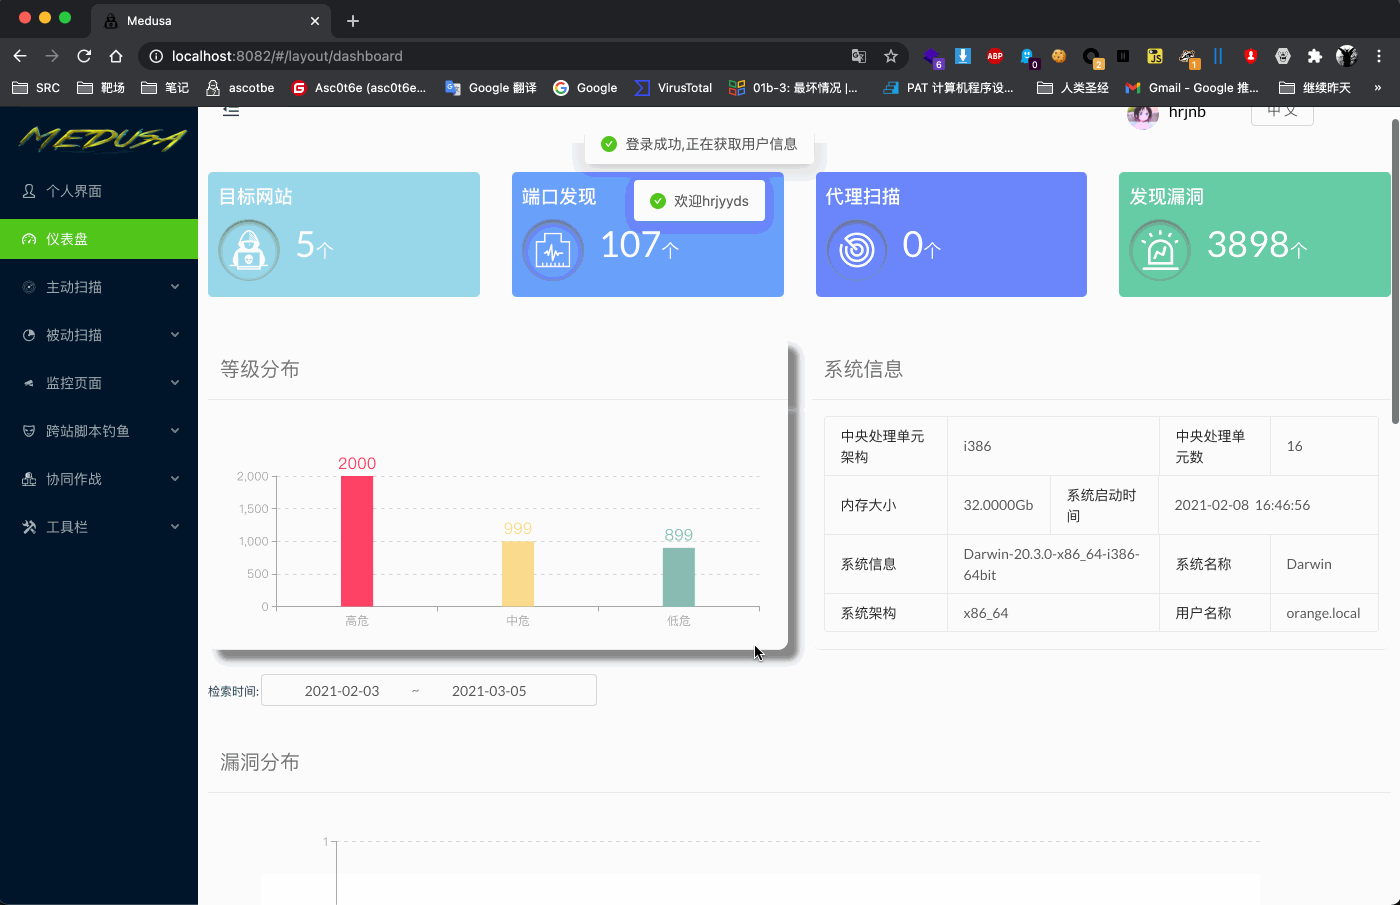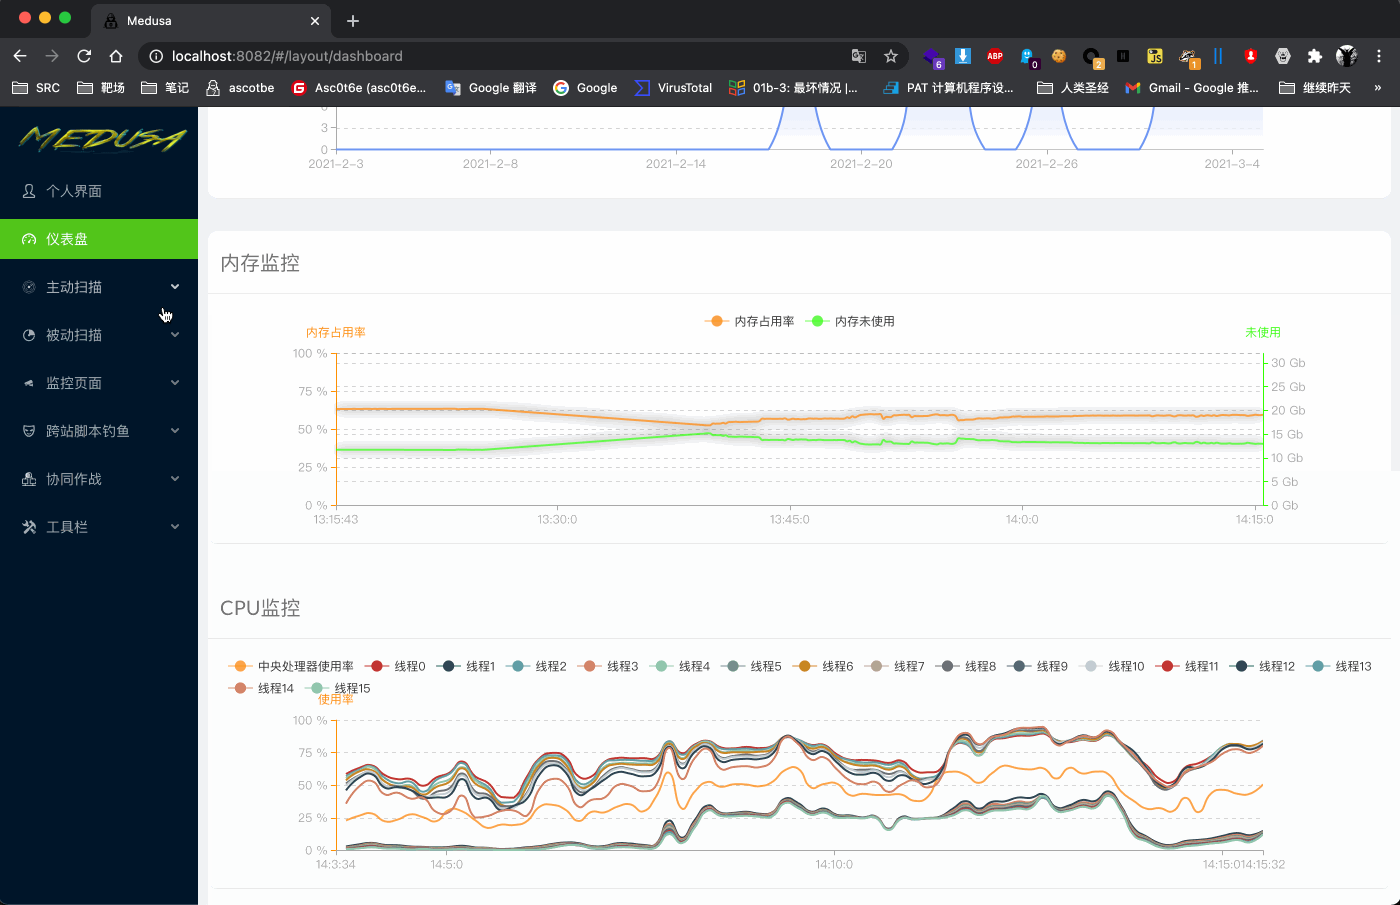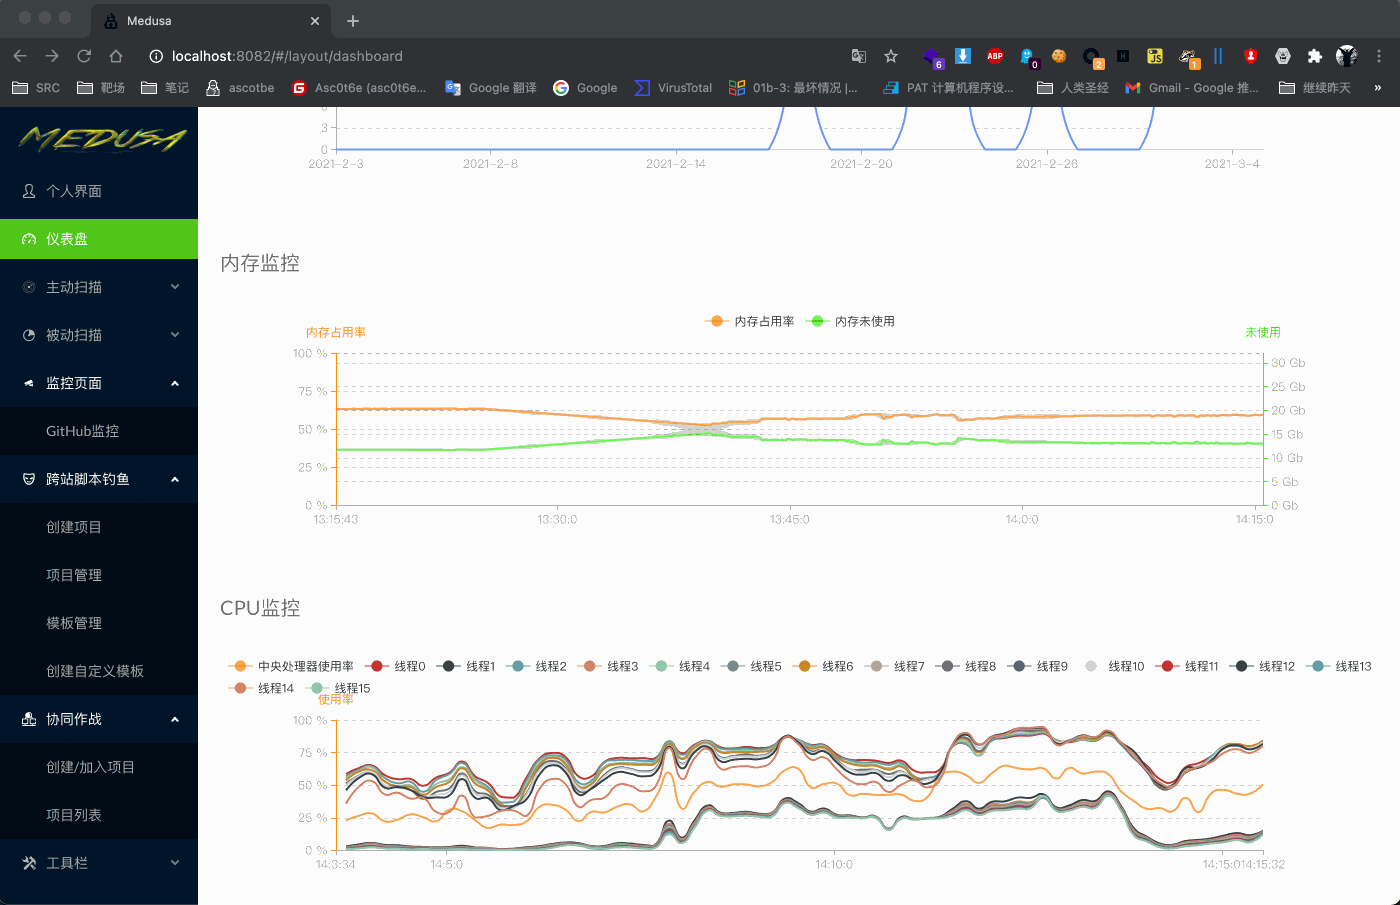
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中

Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…

Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…