Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Medusa — 🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中 | Kitploit
Tools/GitHubGitHub/ascotbe/medusa
Penetration Testing FrameworksExploit FrameworksPayload GenerationPhishingWeb SecurityRed TeamingDNS Analysis
GitHubascotbe/medusa

Medusa

🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中

View Repository
2.2k341573 years agoReviewed by Kitploit
Website
Share
Medusa

Release Release Release Release Release Release Release Release

Welcome to Medusa

👉About Medusa

The project is licensed under GPL.Free for non-commercial use.

Due to the lack of front -end, the project restart time is unknown. If you can provide help, please submit the issue

中文文档 | EnglishDocumentation

💡Document

http://medusa.ascotbe.com

📋Web Ver. installation instructions

https://medusa.ascotbe.com/Documentation/#/Installation

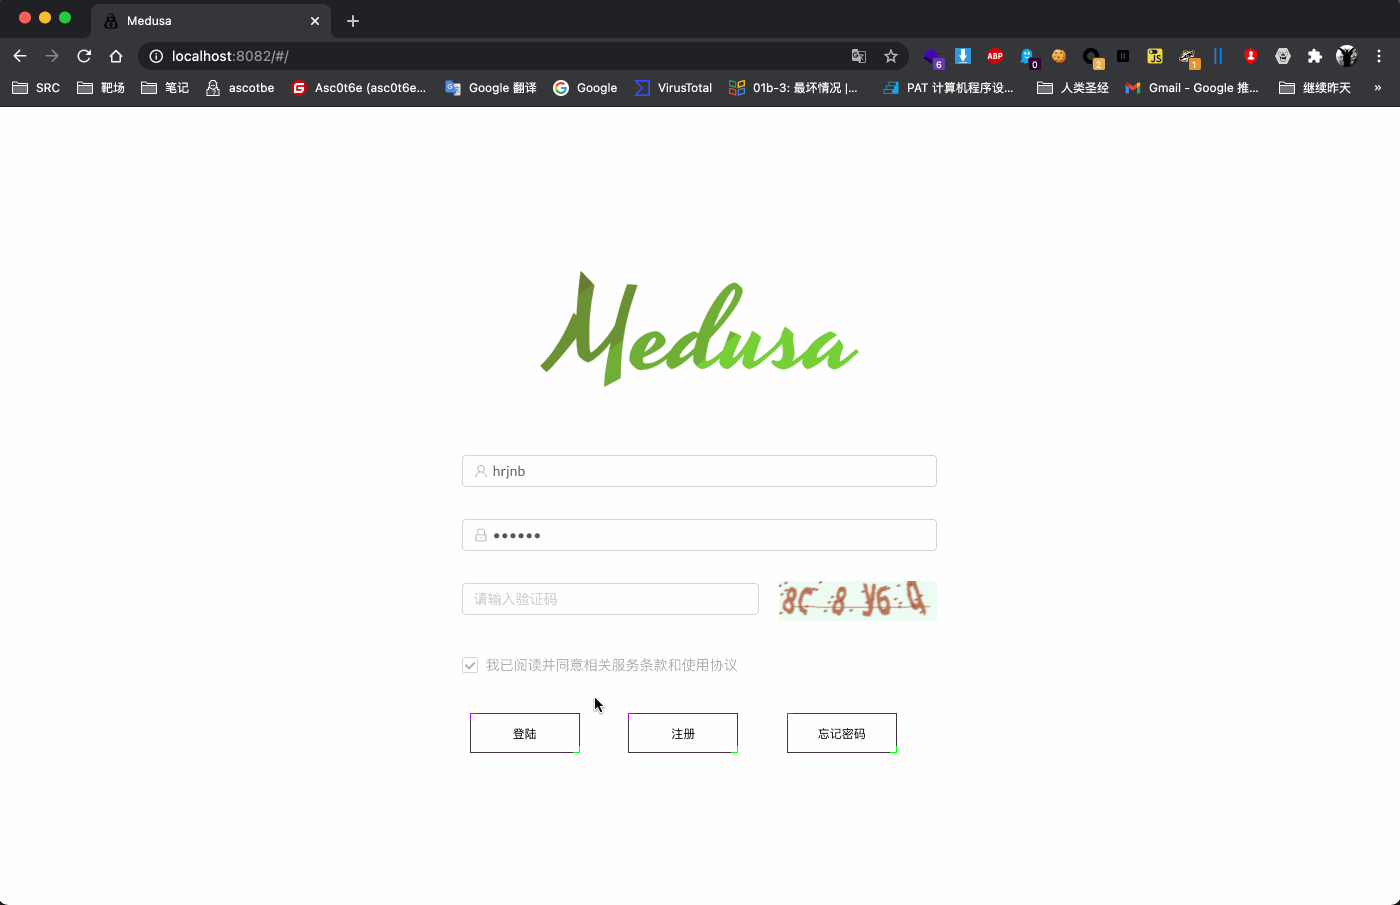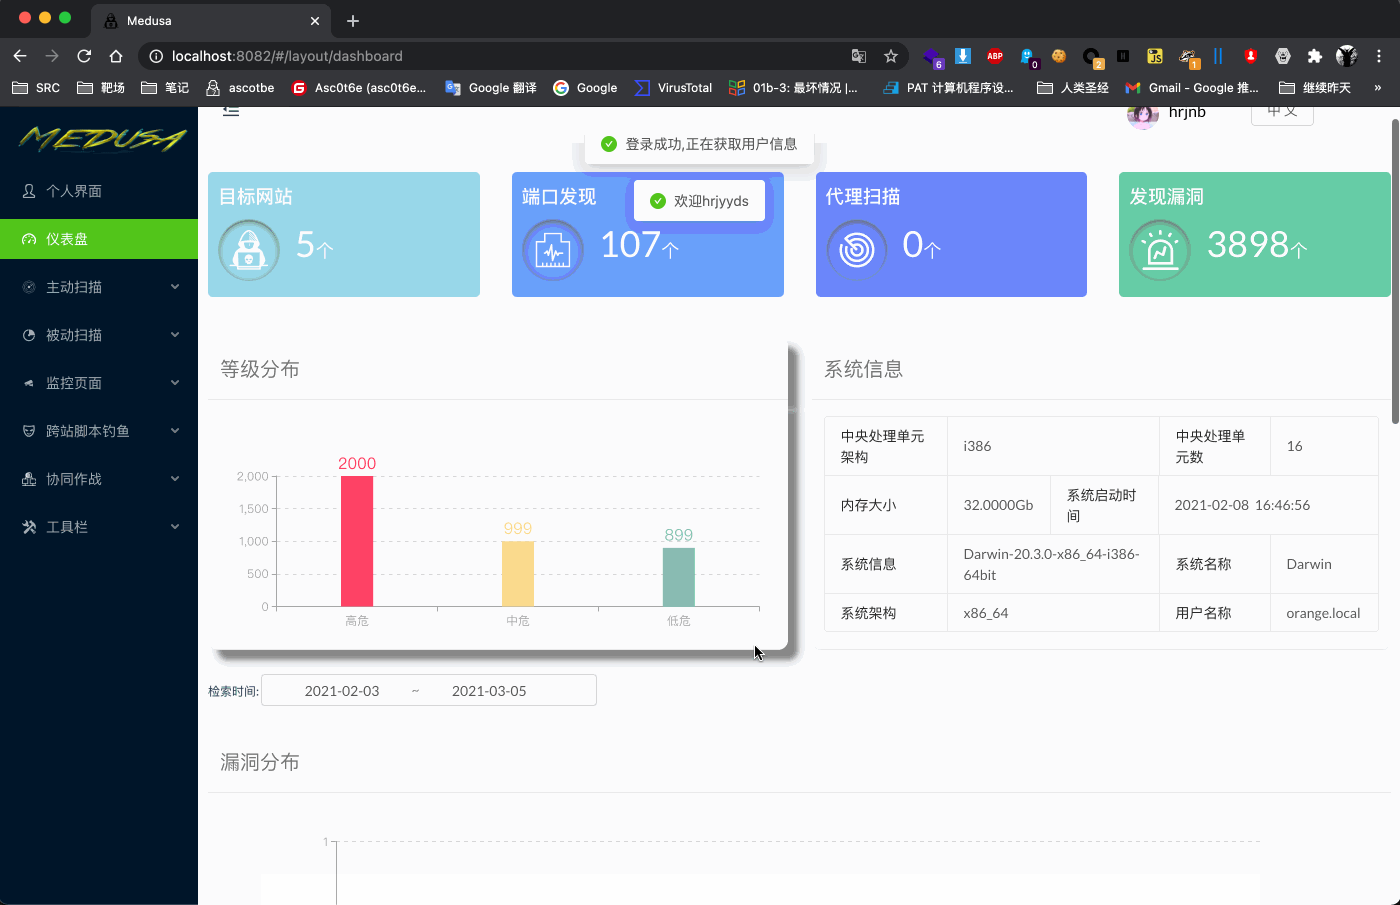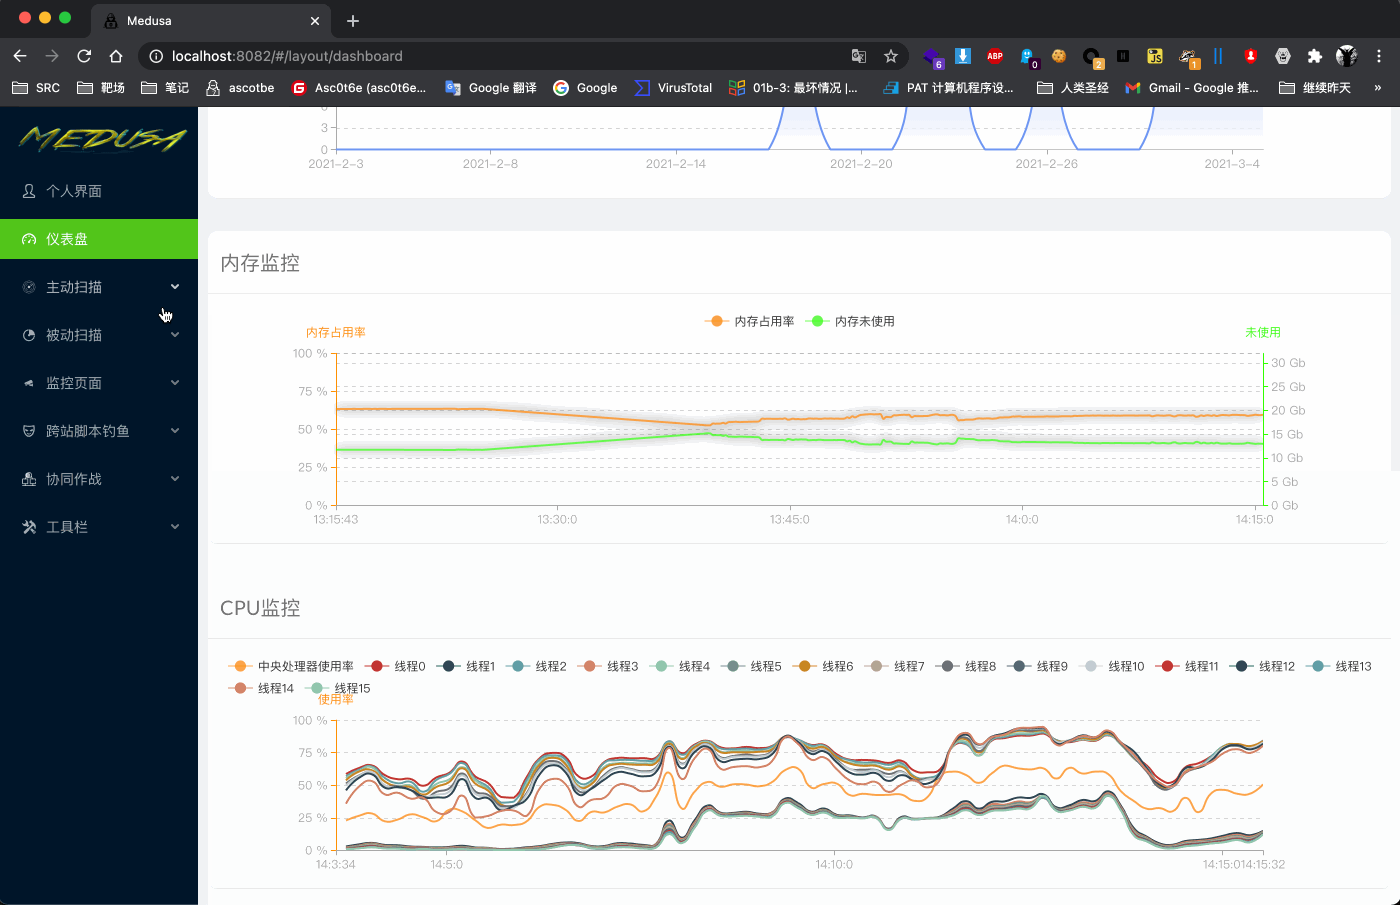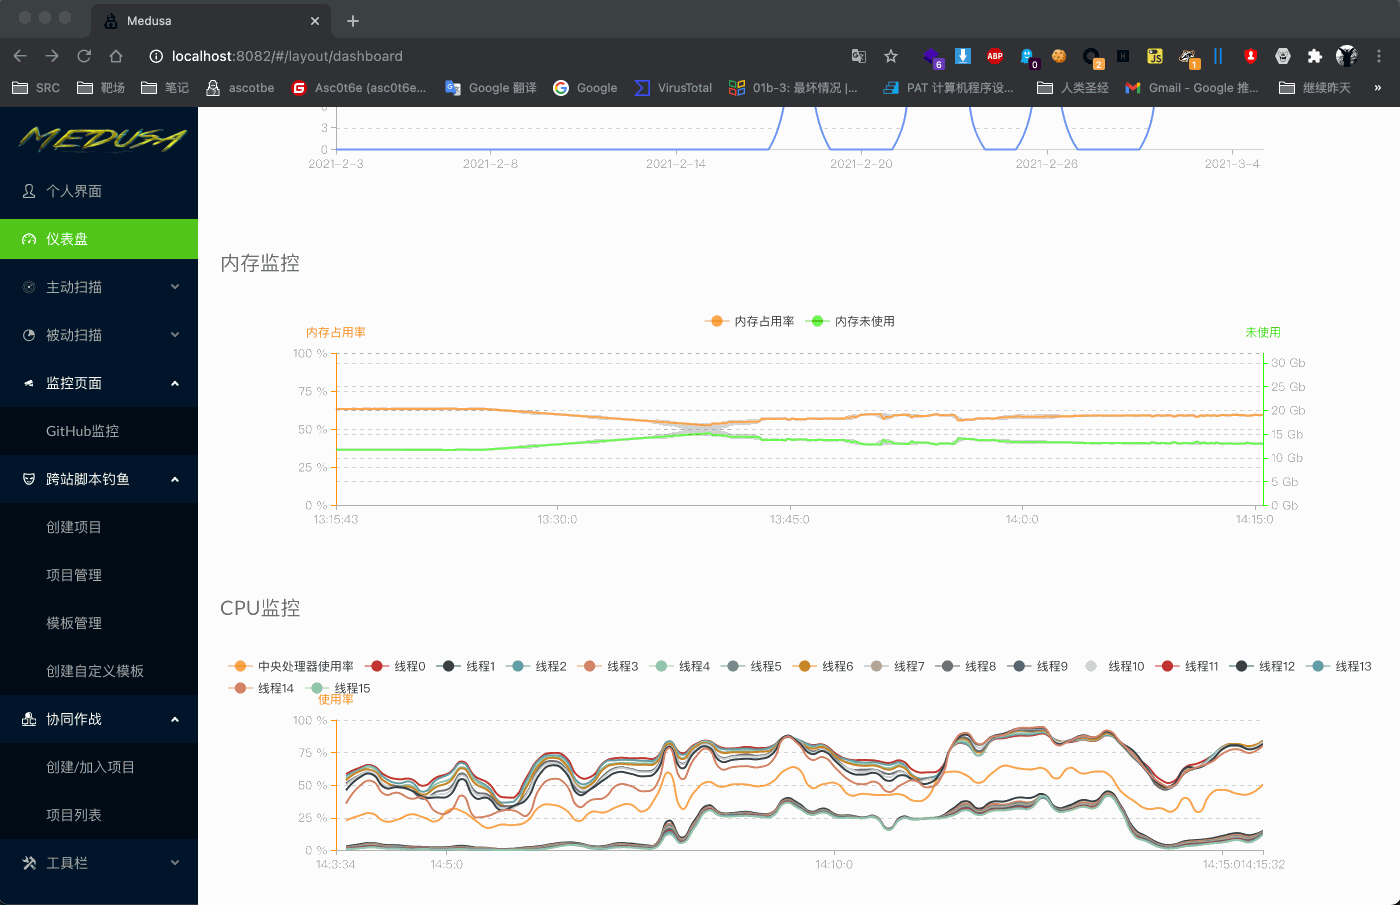
👾Web interface

demo

🍀Updating logs

http://medusa.ascotbe.com/Documentation/#/UpDataLog

💚Discussion

  • If you find that the corresponding vulnerability cannot be scanned by the plug-in, please submit the [Bug] issue
  • If you have any problems that cannot be solved by the documentation, please submit an issue of [help]
  • If you have any good comments or ideas, please submit [idea] issue

⚠️Disclaimer

Add the following content to the original protocol:

  • If there is any ambiguity, the Chinese version of the description shall be the only explanation
  • Commercial use after secondary development is prohibited in this project
  • Unauthorized commercial use is prohibited for this project
  • This project is only for the safe construction activities of enterprises that are legally authorized. When using this project for testing, you should ensure that the behavior complies with local laws and regulations and has obtained sufficient authorization.
  • If you have any illegal behavior in the process of using this project, you need to bear the corresponding consequences yourself, and we will not bear any legal and joint liabilities.
  • Before using this project, please read carefully and fully understand the content of each clause. Restrictions, exemption clauses or other clauses involving your major rights and interests may be bolded, underlined, etc. to remind you to pay attention. Unless you have fully read, fully understood and accepted all the terms of this agreement, please do not use this item. Your use behavior or your acceptance of this agreement in any other express or implied manner shall be deemed to have been read and agreed to be bound by this agreement.

🌴Contributors

commit

🏁Timeline

Alt

star

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →