
fuzz
 xsscx/fuzz
Commodity Injection Signatures, Malicious Inputs, XSS, HTTP Header Injection, XXE, RCE, Javascript, XSLT
curated-resourcesexploitationfuzzing+6
xsscx/fuzzCommodity Injection Signatures, Malicious Inputs, XSS, HTTP Header Injection, XXE, RCE, Javascript, XSLT
 cujanovic/crlf-injection-payloads
Collection of CRLF injection payloads gathered from bug bounty reports, used as a reference for testing HTTP header and response splitting…
 cujanovic/open-redirect-payloads
Curated collection of open redirect payloads sourced from bug bounty reports, with a shell script to substitute a target whitelisted domain for…
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 d4t4s3c/offensivereverseshellcheatsheet
Curated cheat sheet of reverse shell payloads in Bash, Netcat, PHP, PowerShell, Python, Perl, Ruby, and msfvenom, plus webshells, log poisoning, and…
 caveeroo/cve-2026-111497-wordpress-poc
CVE-2026-111497 RCE PoC for one pinned Docker Official Image for WordPress
 threekiii/awesome-redteam
一个攻防知识库。A knowledge base for red teaming and offensive security.
 zarcolio/flipperzero
This repo contains my own Ducky/BadUSB scripts, related PowerShell scripts and other Flipper Zero related stuff.
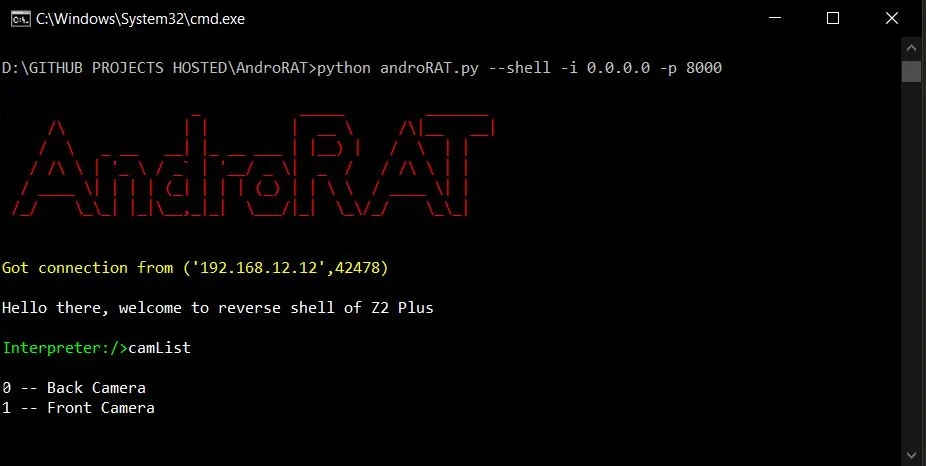 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 nydubh3/cuiri
一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 stormshadow07/hacktheworld
An Python Script For Generating Payloads that Bypasses All Antivirus so far .
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 gmh5225/packer-payload-entropyreducer
Reduce Entropy And Obfuscate Youre Payload With Serialized Linked Lists
 0xblackash/cve-2026-111497
Advisory and proof-of-concept toolkit for CVE-2026-111497 (Node2Shell), a Brotli heap overflow in Node.js, with trigger scripts, version checker, and…
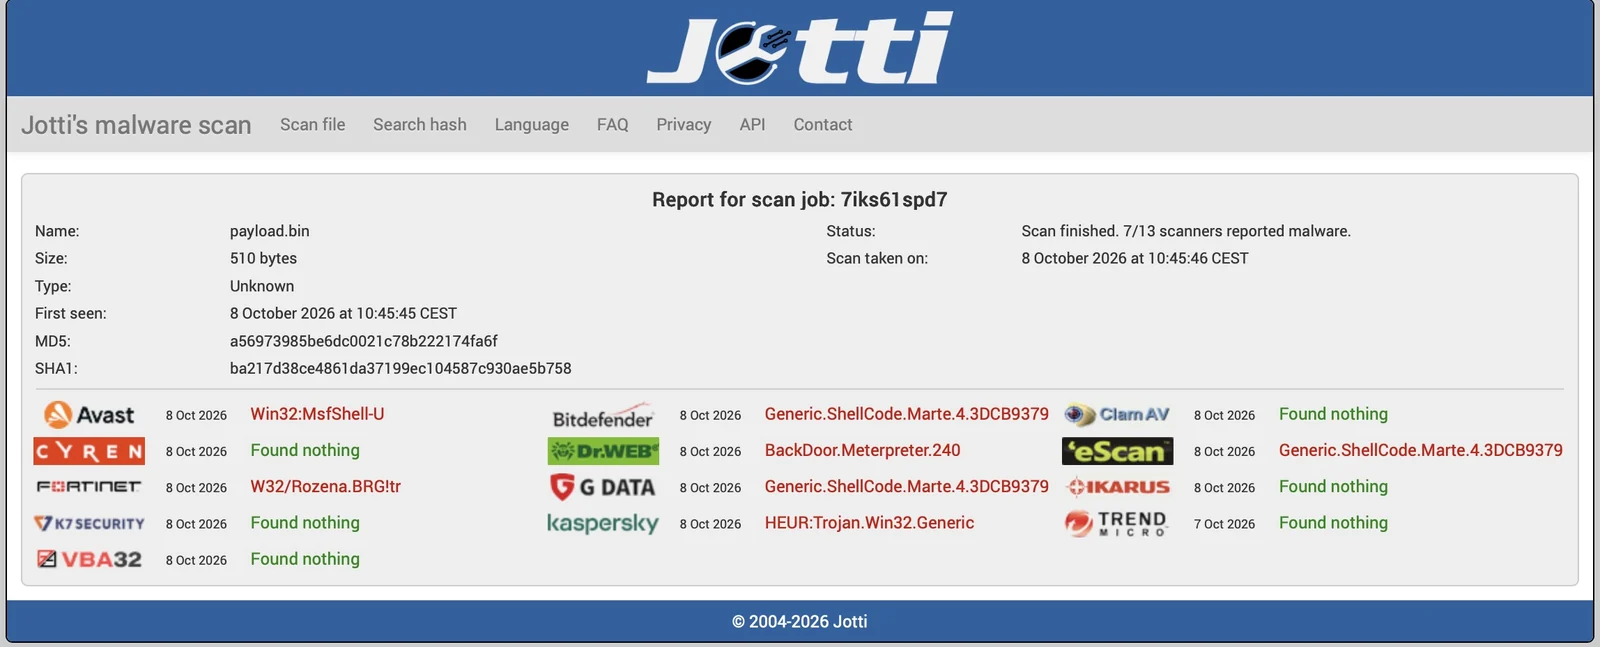 i014n/pngloader
Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
 ardakocadoru/xss-cheatsheet
Comprehensive XSS reference covering reflected, stored, DOM and blind payloads, filter bypass, WAF evasion, CSP bypass, mXSS, and real-world CVE case…
 tonixtoolkitofficial-afk/esp32-blue-ducky
ESP32 firmware that emulates a Bluetooth HID keyboard to auto-pair with Android phones and inject scripted keystrokes for authorized security testing.