Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Esp32-Blue-Ducky — ESP32 firmware that emulates a Bluetooth HID keyboard to auto-pair with Android phones and inject scripted keystrokes for authorized security testing. | Kitploit
Tools/GitHubGitHub/tonixtoolkitofficial-afk/esp32-blue-ducky
Embedded Systems SecurityBluetooth SecurityPayload GenerationWireless SecurityHardware HackingPenetration TestingHardware & IoT SecurityRed Teaming
Share
GitHub
tonixtoolkitofficial-afk/esp32-blue-ducky

Esp32-Blue-Ducky

ESP32 firmware that emulates a Bluetooth HID keyboard to auto-pair with Android phones and inject scripted keystrokes for authorized security testing.

View RepositoryWebsite
2110511 days agoNot yet reviewed

"ESP32 BLUEDECKY" 🦆

⚠️ DISCLAIMER ⚠️ FOR EDUCATIONAL PURPOSES AND CYBERSECURITY TESTING ONLY. This project is created solely for educational purposes, security research, and testing. Unauthorized use on devices without explicit permission is strictly prohibited and illegal. The developer assumes no responsibility or liability for any misuse or damage caused by this software.
image


🌟 WHAT'S NEW IN THIS UPDATE (v2.0.0)

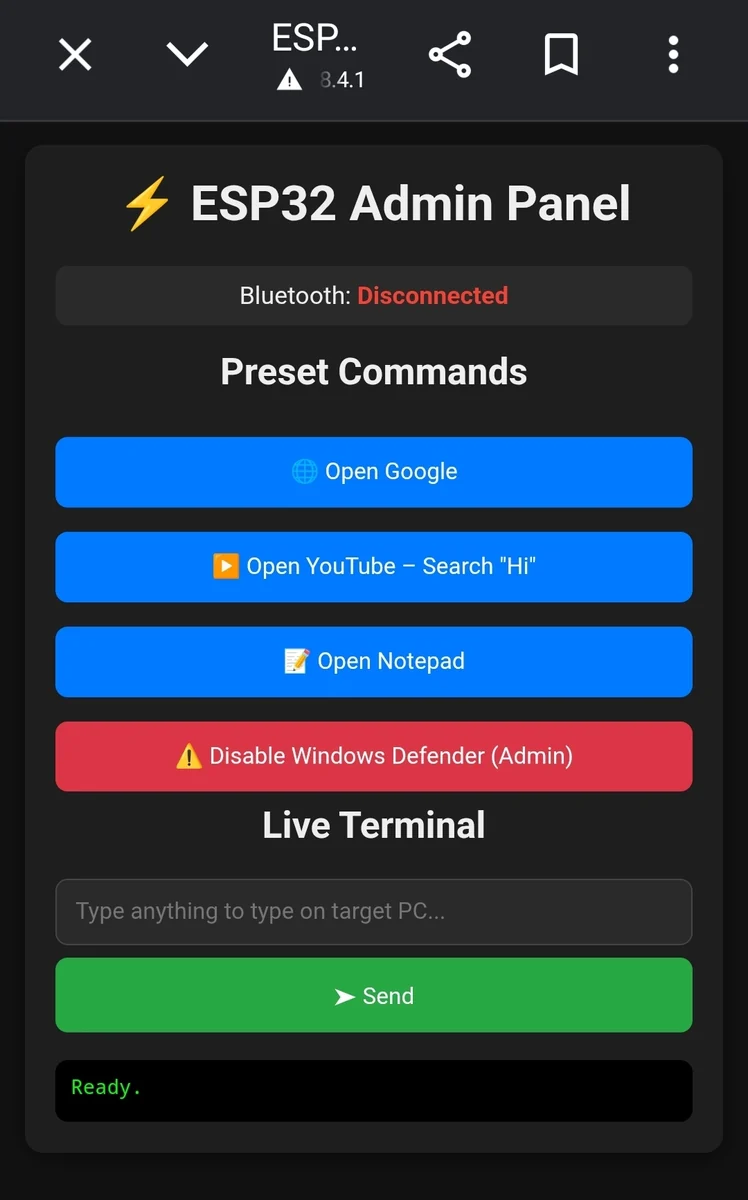
  • Wi-Fi Admin Panel (http://192.168.4.1): Connect to the device's Wi-Fi Access Point and access the admin panel via browser at 192.168.4.1.
  • Automatic Keylogger: The firmware runs an automatic keylogger in the background.
  • Custom Payload Control: Easily customize pre-set scripts and send live commands directly through the admin panel.

image

How It Works & Installation

🌏 Flash Firmware: 📥 Flash/Install the .bin files onto your ESP32 board using your preferred ESP flashing tool.

⚡ Power Up: Flash the .bin code now using this web flasher: https://esptool.spacehuhn.com/


FLASHING INSTRUCTION

File NameOffset
bootloader.bin0x1000
partitions.bin0x8000
firmware.bin0x10000

Features & Usage

⚙️ 1. Power & Bluetooth Connection: 📱🔗

  • Provide power supply to the ESP32 board via USB or an external battery source.
  • Turn on Bluetooth on your mobile device and connect to the device named "Bluedecky".

⚙️ 2. Automated Execution & Keylogger: 🤖

  • Pair your Android smartphone with the ESP32 BlueDecky (Bluetooth device name: "Bluedecky").
  • The device automatically executes pre-configured automated tasks on your connected device.
  • Simultaneously runs background keystroke recording logic (Keylogger).

🌐 3. Wi-Fi Admin Panel Access: 💻

  • Turn on Wi-Fi on your phone or PC and connect to the ESP32 Wi-Fi Hotspot network.
  • Open any web browser and go to: http://192.168.4.1
  • From the Admin Panel, you can:
    • View logged keystrokes.
    • Manage pre-set configuration scripts.
    • Send customized rubber ducky codes directly to the device.

Requirements

⚙️ ESP32 Development Board
⚙️ Power Cable / Battery Source 🔋
⚙️ Smartphone (Android) 📱
⚙️ Web Browser (Chrome/Firefox for accessing 192.168.4.1)
⚙️ IDE (Windows Working Environment)


DEVELOPER

@TONIX

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    911
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    362
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    311
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    287

Explore all tools

Browse our collection of tools

View all tools →