
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Awesome-Redteam — 一个攻防知识库。A knowledge base for red teaming and offensive security. | Kitploit
Tools/GitHubGitHub/threekiii/awesome-redteam
Privilege EscalationPayload GenerationExploitationLateral MovementReverse EngineeringInformation GatheringPost-ExploitationPenetration TestingCommand and ControlLearning & EducationRed TeamingCurated Resources
4.4k7553284 months agoReviewed by Kitploit
Share
GitHubthreekiii/awesome-redteam

Awesome-Redteam

一个攻防知识库。A knowledge base for red teaming and offensive security.

View Repository

Awesome-Redteam

stars forks last-commit

❗Disclaimer: The technologies, concepts, and tools provided in this Git repository are intended for educational and research purposes only. Any use for illegal activities, unauthorized penetration testing, or commercial purposes is strictly prohibited. Please read the Awesome-Laws before using this repository.

📖 A knowledge base for red teaming and offensive security.

👍 means recommend
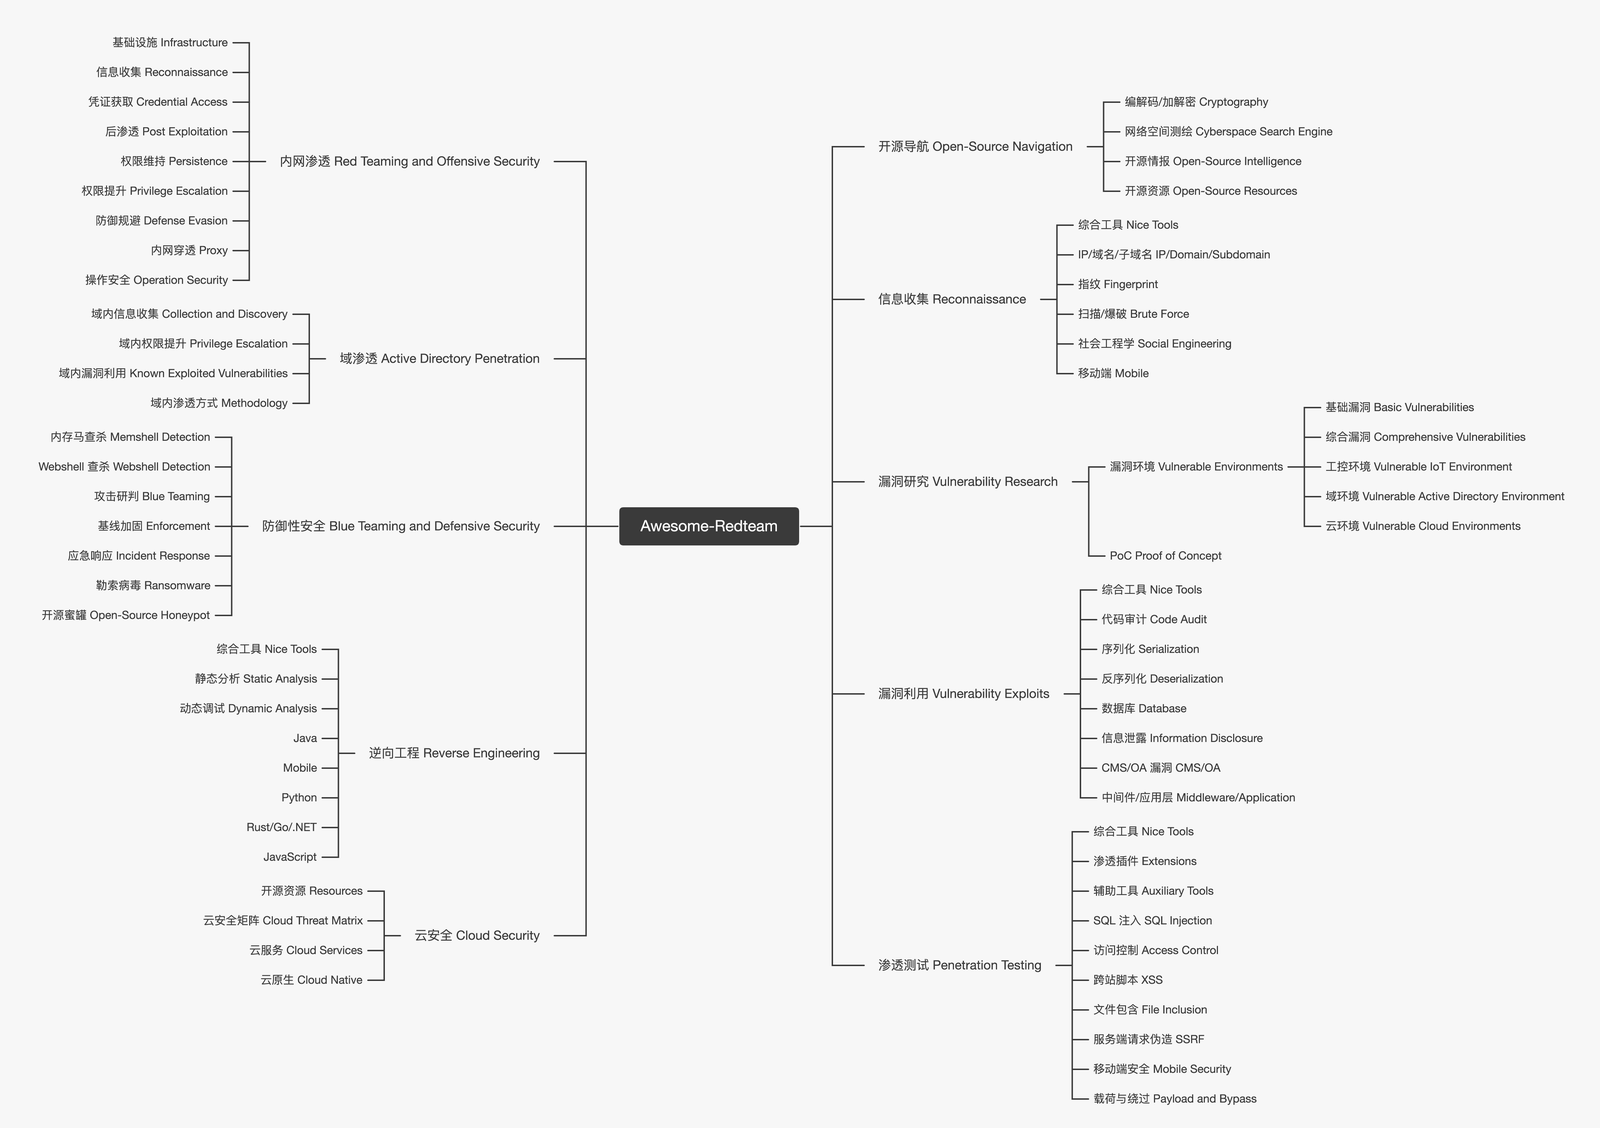
Roadmap

Contents

  • Open-Source Navigation
    • Cryptography
      • Online Tools
      • Offline Tools
      • Encode/Decode
      • Regular Expressions
      • Hash Algorithms
      • RSA
      • SM Algorithms
    • Cyberspace Search Engine
      • Nice Tools
      • Web/Ports
      • Google Hacking
      • GitHub Dork
    • Open-Source Intelligence
      • Nice Tools
      • Threat Intelligence
      • Disclosed Vulnerabilities
      • API Search
      • Source Code Search
    • Open-Source Resources
      • Communities/Knowledge Base
      • Mindmap/Cheat Sheets
      • Red Teaming and Offensive Security
      • Blue Teaming and Defensive Security
      • Operation Security
      • Learning and Practice Platforms
  • Reconnaissance
    • Nice Tools
    • IP/Domain/Subdomain
    • Fingerprint
      • Fingerprint Collection
      • Fingerprint Reconnaissance
      • Waf Checks
    • Brute Force
      • Brute Force Tools
      • Brute Force Dictionaries
      • Generate a Custom Dictionary
      • Default Credentials
    • Social Engineering
      • Leaked Credentials
      • Email
      • SMS Online
      • Phishing
    • Mobile
  • Vulnerability Research
    • Vulnerable Environments
      • Basic Vulnerabilities
      • Comprehensive Vulnerabilities
      • Vulnerable IoT Environment
      • Vulnerable Active Directory Environment
      • Vulnerable Cloud Environments
    • Proof of Concept
      • PoC/ExP
      • PoC Templates
  • Vulnerability Exploits
    • Nice Tools
    • Code Audit
    • Serialization
      • Java
    • Deserialization
      • Java
      • PHP
    • Database
      • Redis
      • MySQL
      • Oracle
      • MSSQL
    • Information Disclosure
    • CMS/OA
    • Middleware/Application
  • Penetration Testing
    • Nice Tools
    • Extensions
      • Chrome
      • Burp Suite
      • Yakit
    • Auxiliary Tools
      • Open-Source Toolkit
      • DNSLog
      • Command Line
      • Beautifier
      • Generator
    • SQL Injection
    • Access Control
      • Bypass 40X errors
    • XSS
    • File Inclusion
    • SSRF
    • Mobile Security
      • Mini Program
      • APK
      • SessionKey
    • Payload and Bypass
  • Red Teaming and Offensive Security
    • Infrastructure
    • Reconnaissance
    • Credential Access
      • Credential Dumping
      • Local Enumeration
      • NTLM Cracking
    • Post Exploitation
      • Nice Tools
      • Binaries and Libraries
    • Persistence
      • MemShell
      • Webshell Management
      • Webshell Bypass
      • Reverse Shell Management
    • Privilege Escalation
      • Linux Local Enumeration
      • Windows Local Enumeration
      • Windows Exploits
      • Linux Exploits
      • Database Exploits
    • Defense Evasion
      • Linux Defense Evasion
      • Windows Defense Evasion
    • Proxy
      • Proxy Client
      • Proxy Tools
      • DNS Tunnel
      • ICMP Tunnel
      • Port Forwarding
    • Operation Security
  • Active Directory Penetration
    • Collection and Discovery
    • Privilege Escalation
    • Known Exploited Vulnerabilities
      • MS14-068
      • noPac
      • Zerologon
      • ProxyLogon/ProxyShell
      • ProxyNotShell
      • Printnightmare
    • Methodology
      • Coerce and Relay
      • Delegation
      • ADCS
      • ACLs and ACEs
  • Blue Teaming and Defensive Security
    • Memshell Detection
    • Webshell Detection
    • Blue Teaming
    • Enforcement
    • Incident Response
    • Ransomware
      • Search Engine
      • Decryption Tools
    • Open-Source Honeypot
    • Reverse Engineering
      • Nice Tools
      • Static Analysis
      • Dynamic Analysis
      • Java
      • Mobile
      • Python
      • Rust/Go/.NET
  • Cloud Security
    • Resources
    • Cloud Threat Matrix
    • Cloud Services
      • Management Tools
      • AK/SK Exploit
    • Cloud Native
      • Nice Tools
      • Docker
      • Kubernetes
  • Productivity-Boosting Usage Methods
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →








