
Archived
AhMyth-Android-RAT
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
android-securitycommand-and-controlpayload-generation+3
5.3k
ahmyth/ahmyth-android-ratAndroid Remote Administration Tool
 bishopfox/sliver
Adversary Emulation Framework
 sabri-zaki/easy_hack
Hack the World using Termux
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…
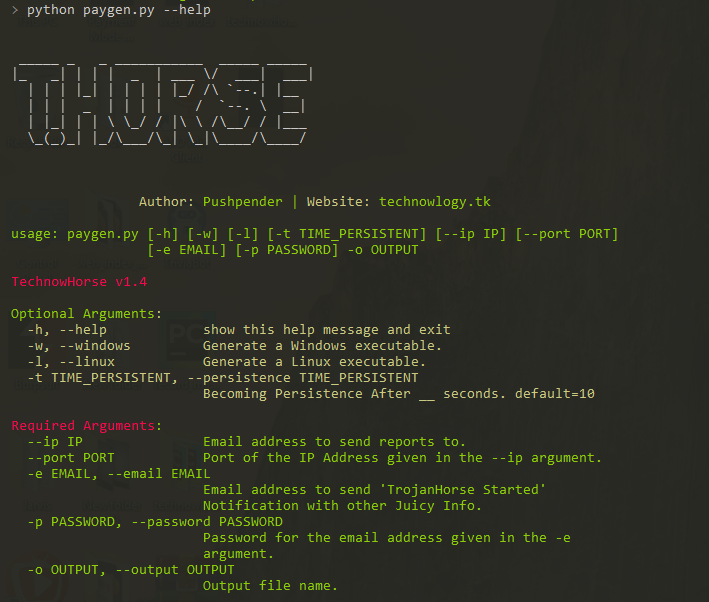 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.

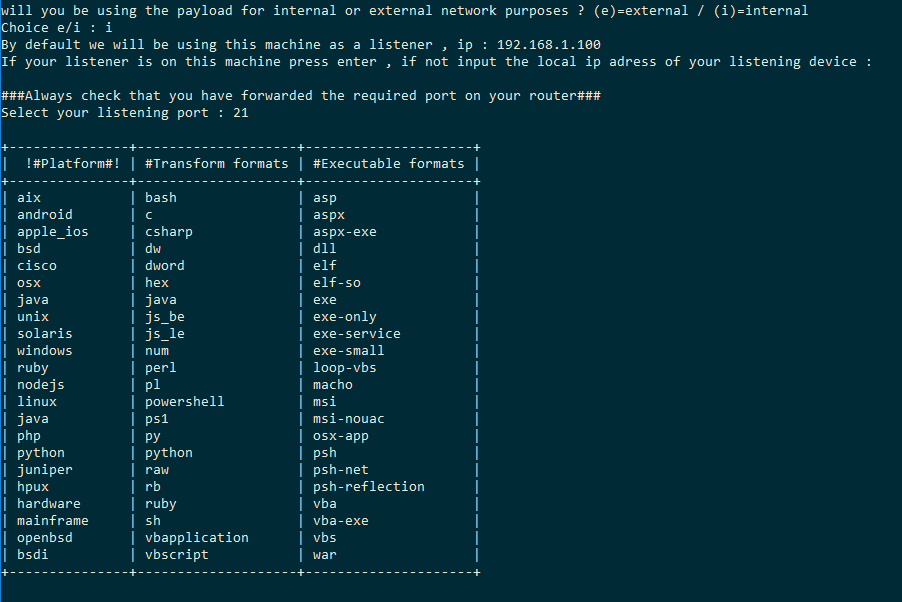 ceh-tn/the-axer
Automated payload generator wrapping msfvenom to streamline creation of platform-specific, encoded, and binded payloads for penetration testing…
 cedowens/mythic-macro-generator
Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens