
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
BadAssMacros — C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations. | Kitploit
Tools/GitHubGitHub/inf0secrabbit/badassmacros
Exploit FrameworksPayload GenerationShellcodeRed Teaming
GitHubinf0secrabbit/badassmacros

BadAssMacros

C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.

View Repository
44485905 years agoReviewed by Kitploit
Share

Supported Python versions

BadAssMacros


Description

Proof of Concept tool to generate malicious macros leveraging techniques like VBA Purging and Shellcode Obfuscation to evade AV engines.

This tool takes in raw shellcode that can be generated by popular C2 frameworks like (Metasploit,Cobalt Strike etc) and outputs a VBA macro.

The tool takes in the malicious doc/excel file ready and embedded with the generated VBA code and performs VBA purging.

Current Features

BadAssMacros features currently include:

  • Classic VBA shellcode injection.
  • Indirect VBA shellcode injection (using LoadLibrary).
  • Sandbox Detection.
  • VBA Purging.
  • Shellcode obfuscation.
  • Variable name Randomization.

Shellcode Injection Techniques

|   Name   | x32 |     x64     |
| -------- | --- | ----------- |
| Classic  | Yes | Yes         |
| Indirect | Yes | In Progress |

Ethical use

The BadAssMacros tool is meant to only be used for ethical purposes. Don't use it for bad things.

Build Instructions

Build from sources

BadAssMacros require 3rd party libraries that can be installed from the NuGet package manager.

  • Clone the repository in Visual Studio
  • Once project is loaded in Visual Studio go to "Tools" --> "NuGet Package Manager" --> "Package Manager Settings" --> "NuGet Package Manager" --> "Package Sources"
  • Check if there is a package source with URL - "https://api.nuget.org/v3/index.json". If not create the same.
  • Run the following commands
    • Install-Package Costura.Fody -Version 3.3.3
    • Install-Package OpenMcdf -Version 2.2.1.3
    • Install-Package Fody -Version 4.0.2
  • Build the project :)

The BadAssMacros.exe will be inside the bin directory.

Examples

  • Show Help
BadAssMacros.exe -h
  • Create VBA for classic shellcode injection from raw shellcode
BadAssMacros.exe -i <path_to_raw_shellcode_file> -w <doc/excel> -p no -s classic -c <caesar_shift_value> -o <path_to_output_file>

ClassicVBA

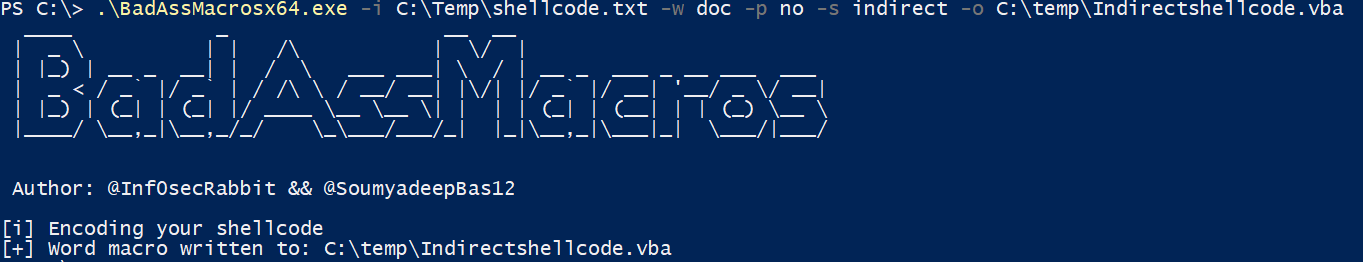
  • Create VBA for indirect shellcode injection from raw shellcode
BadAssMacros.exe -i <path_to_raw_shellcode_file> -w <doc/excel> -p no -s indirect -o <path_to_output_file>
IndirectVBA

  • List modules inside Doc/Excel file
BadAssMacros.exe -i <path_to_doc/excel_file> -w <doc/excel> -p yes -l

ListingModules

  • Purge Doc/Excel file
BadAssMacros.exe -i <path_to_doc/excel_file> -w <doc/excel> -p yes -o <path_to_output_file> -m <module_name>

PurgedDocument

Detection

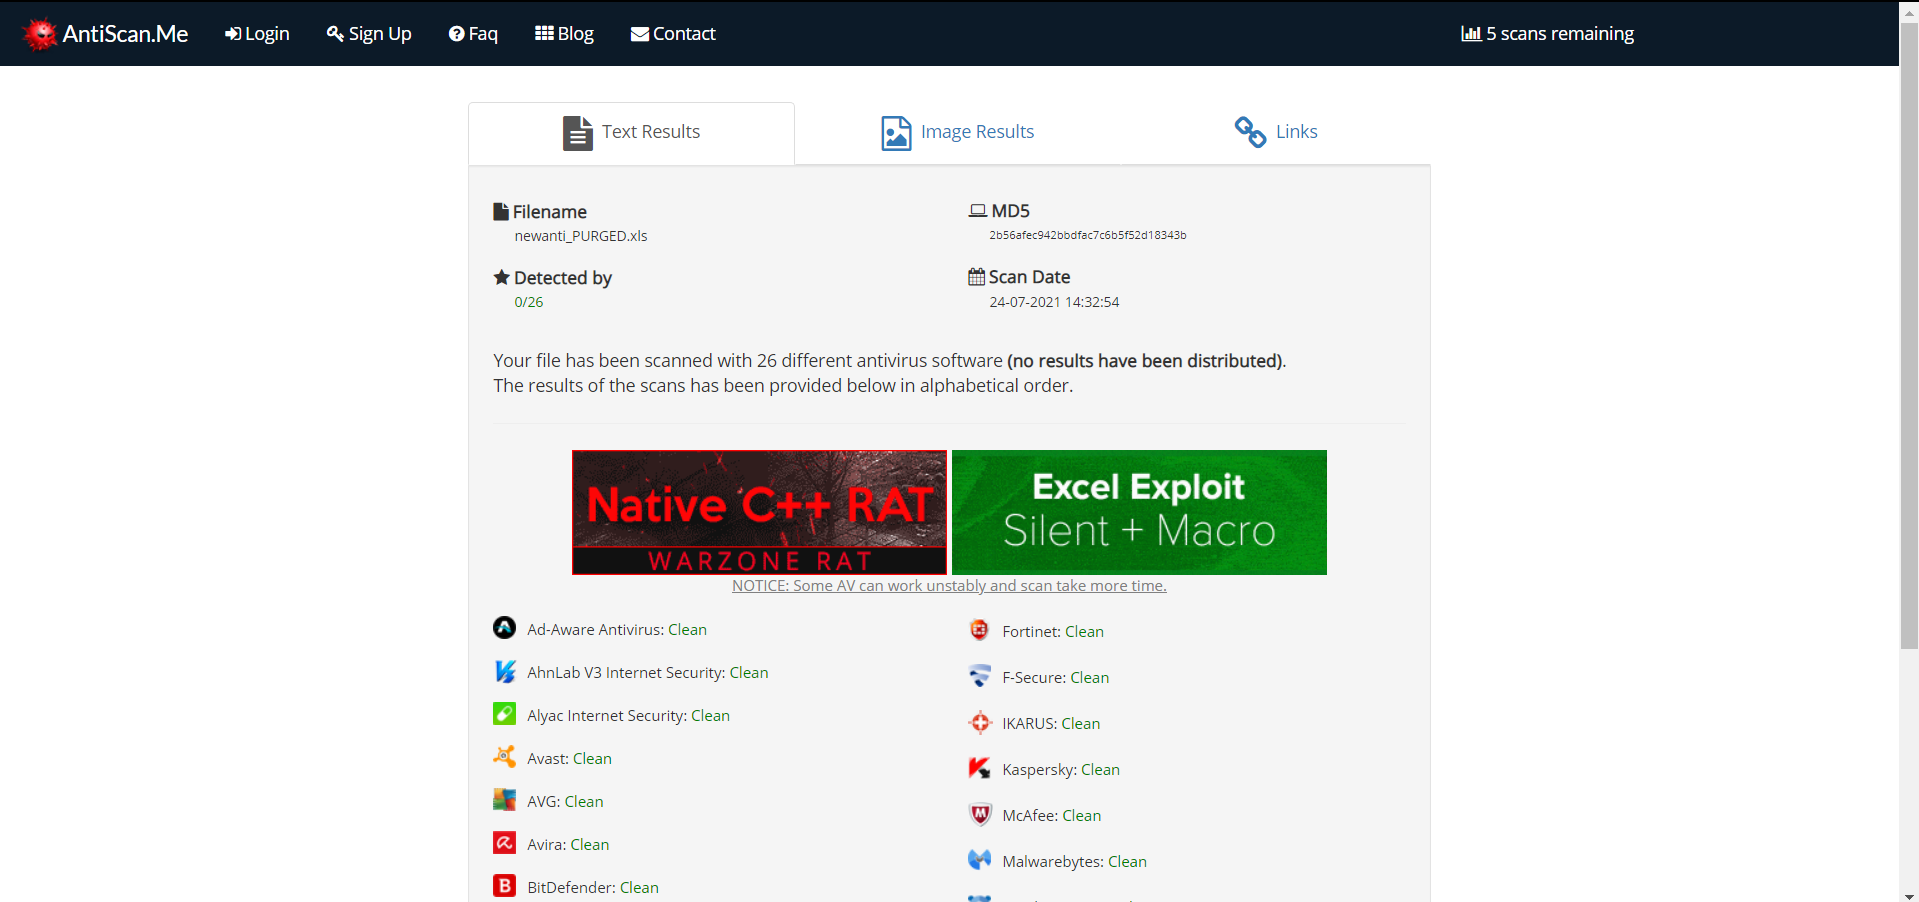
BadAssMacro was tested against local Antivirus solutions and online services like antiscan.me. The results of testing the same using the Indirect shellcode execution method is attached below.
NOTE: Please do not submit the samples to VirusTotal


Contact

  • @Inf0secRabbit
  • @SoumyadeepBas12

Credits

  • OfficePurge by FireEye here
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    696
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    499
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    396
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    340
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →




