

Koi
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
37
b3rt1ng/koiMulti-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 jas502n/cve-2019-11581
Atlassian JIRA Template injection vulnerability RCE
 asaurusrex/forblaze
Forblaze - A Python Mac Steganography Payload Generator
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 immunityinc/log4j-jndiserver
This project will help to test the Log4j CVE-2021-44228 vulnerability.
 kosmicowl045/ict287-cve-2022-42889
Setup and exploit recreation for CVE-2022-42889 Text4Shell.
 tonixtoolkitofficial-afk/esp32-blue-ducky
ESP32 firmware that emulates a Bluetooth HID keyboard to auto-pair with Android phones and inject scripted keystrokes for authorized security testing.
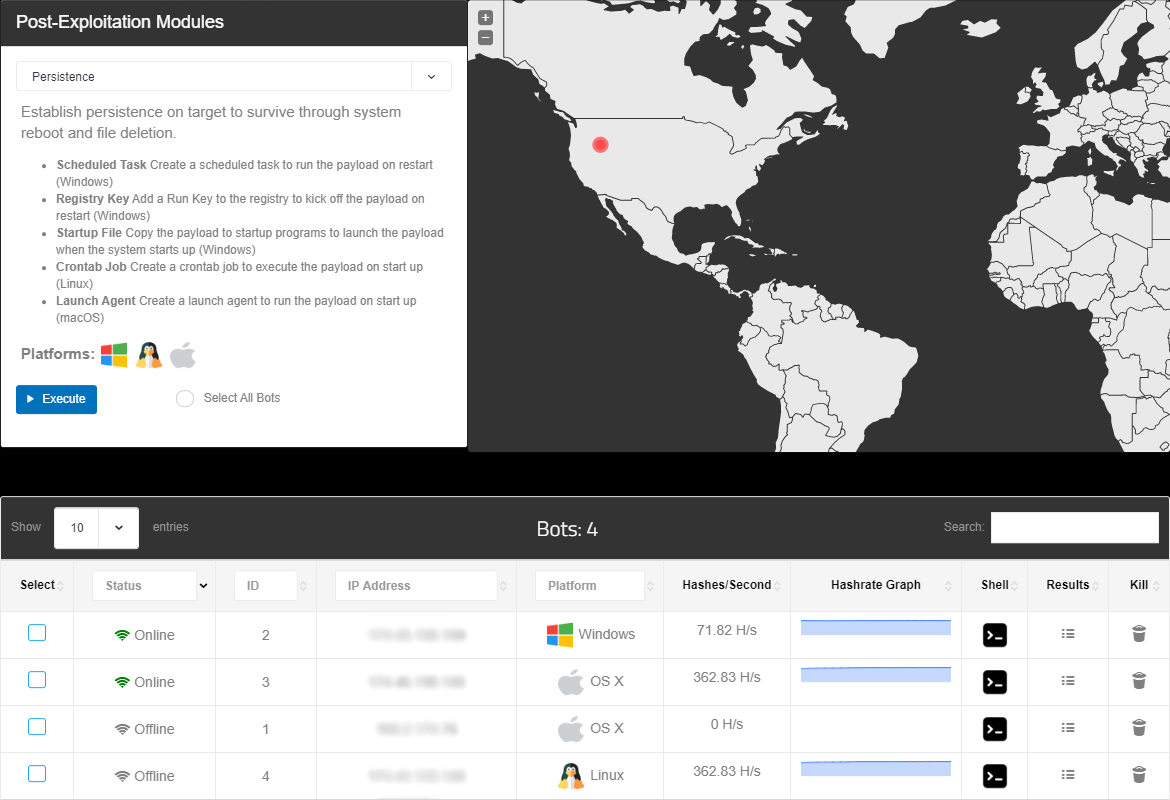 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 haxorstars/cve-2025-54068
A tool designed to exploit CVE-2025-54068 and Remote Command Execution of the Livewire project.
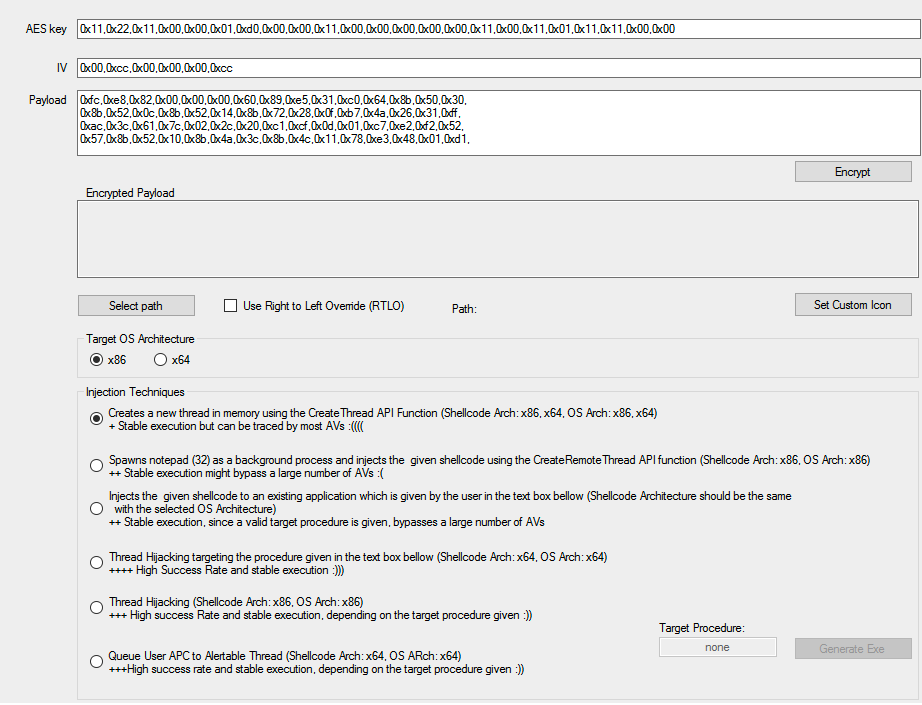 ch0pin/aviator
Antivirus evasion project
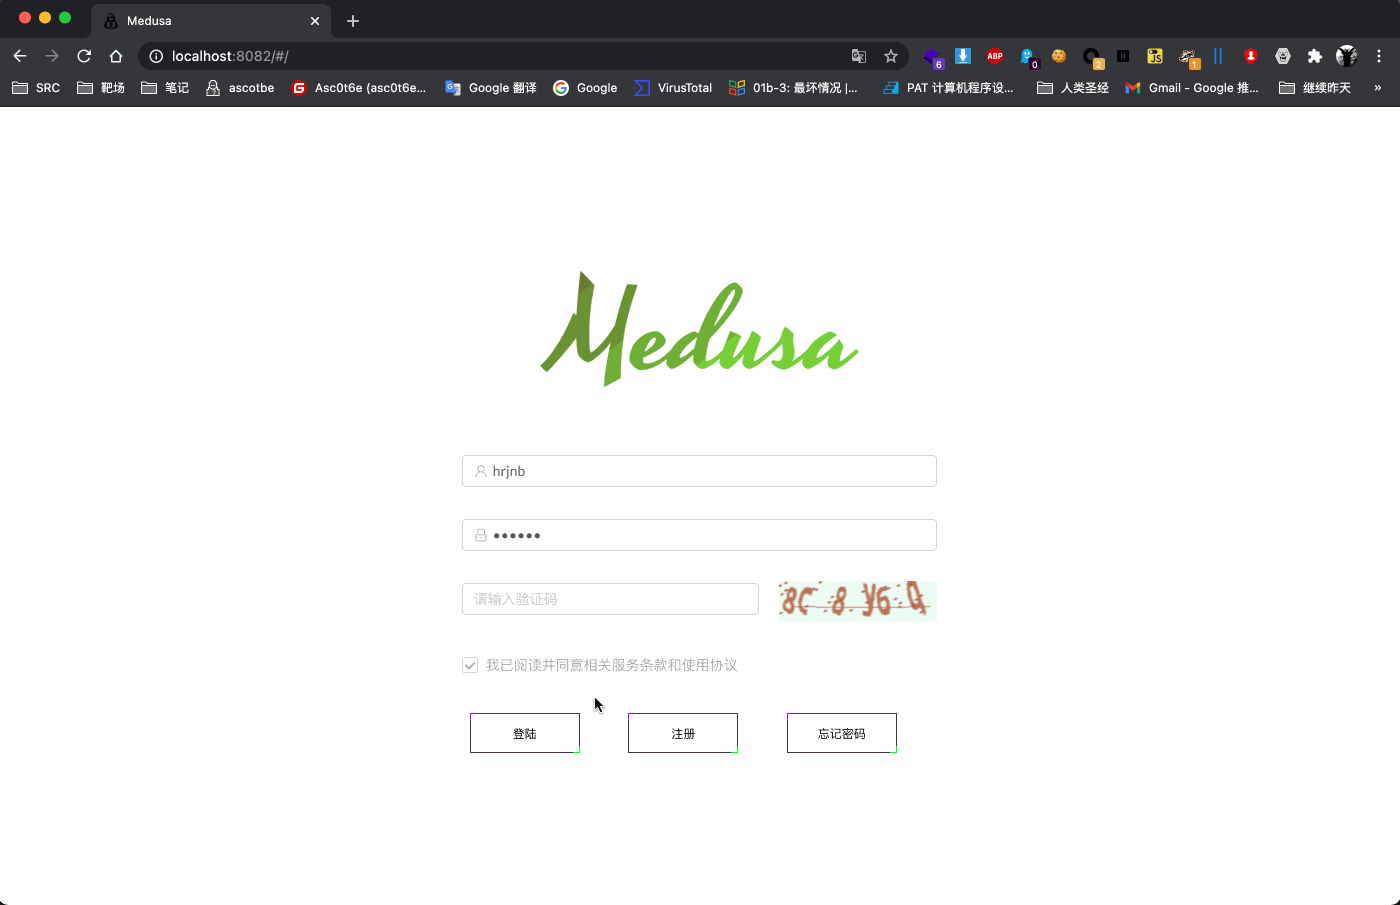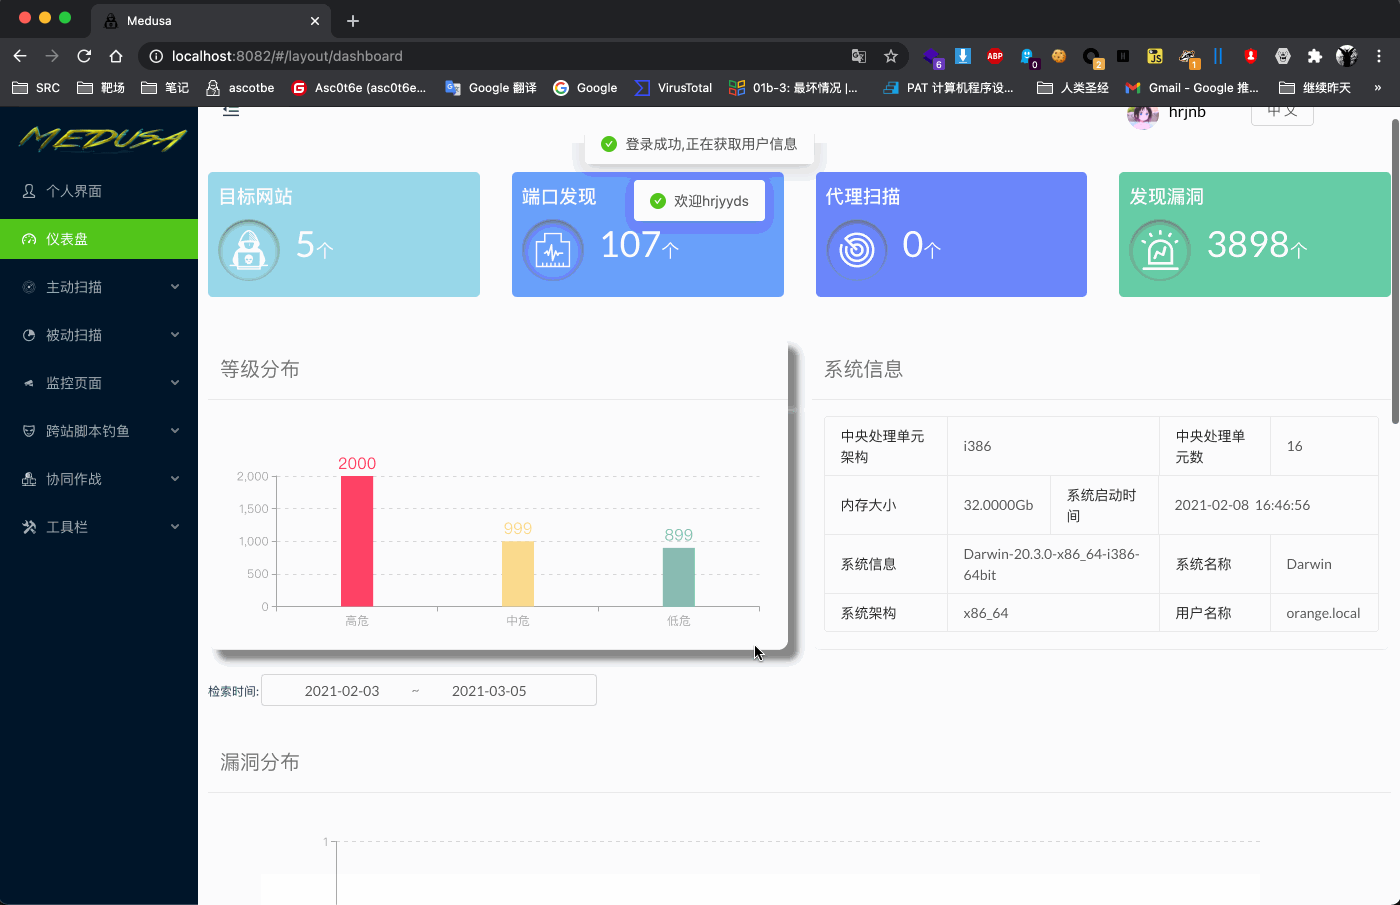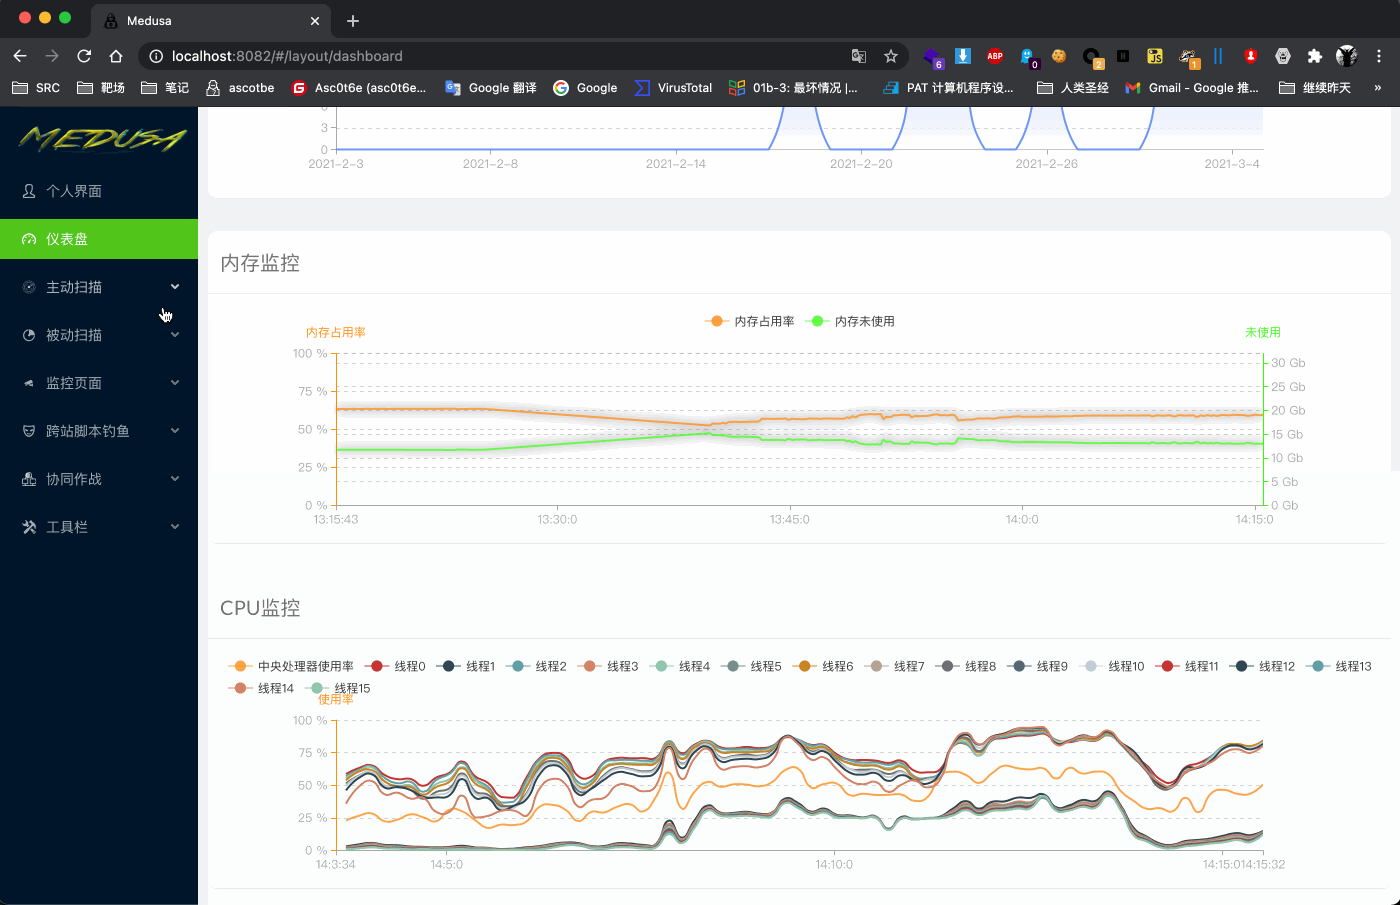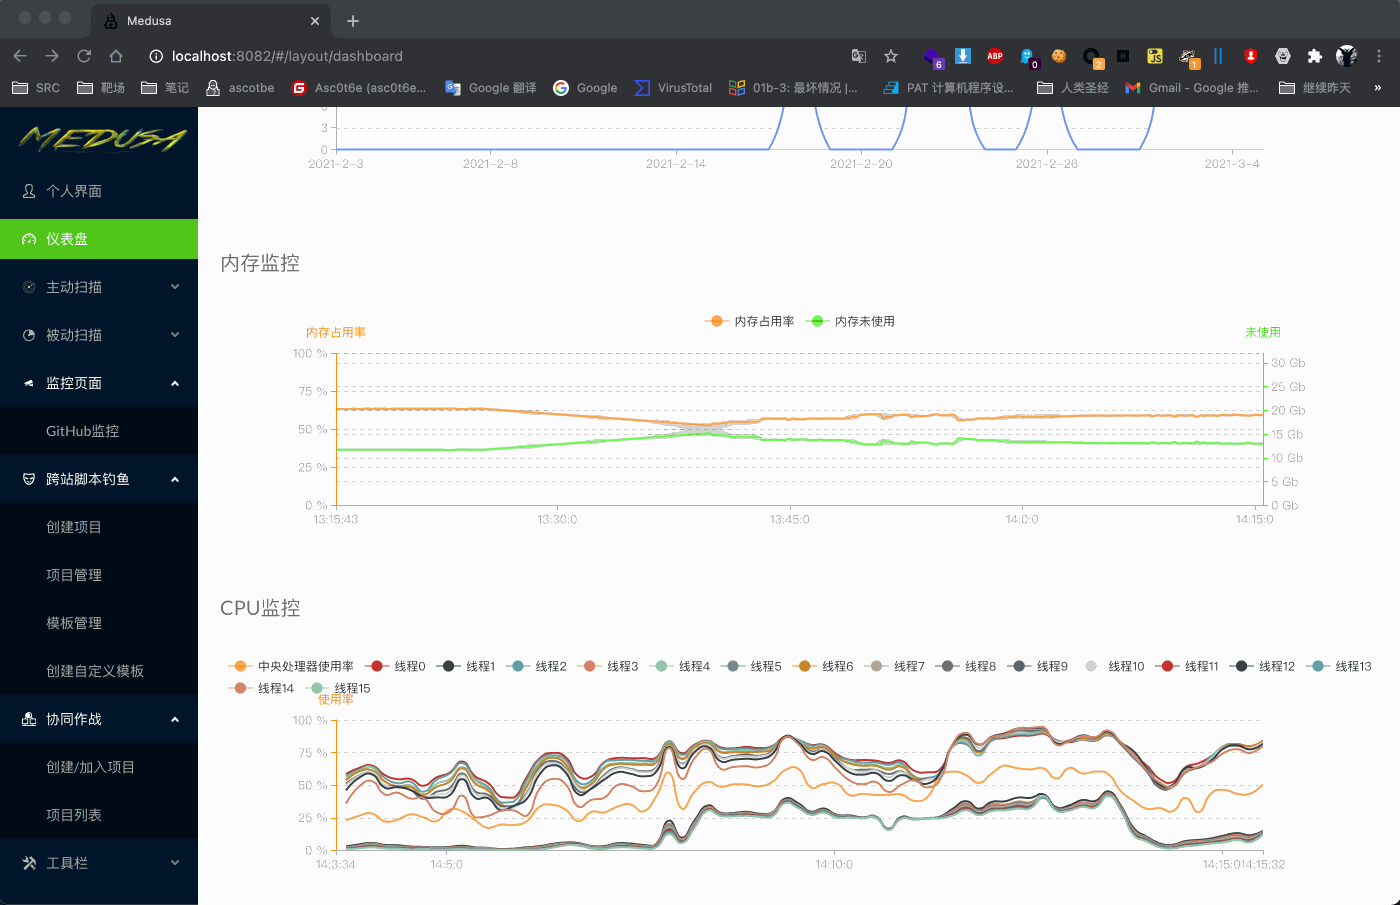 ascotbe/medusa
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
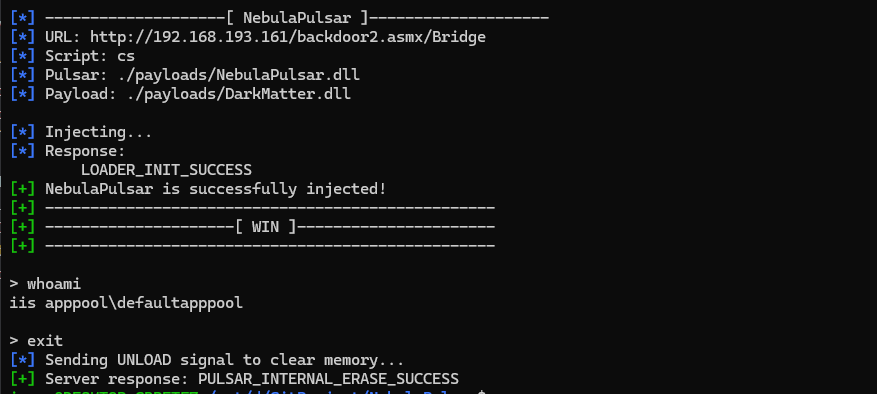 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 i014n/pngloader
Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
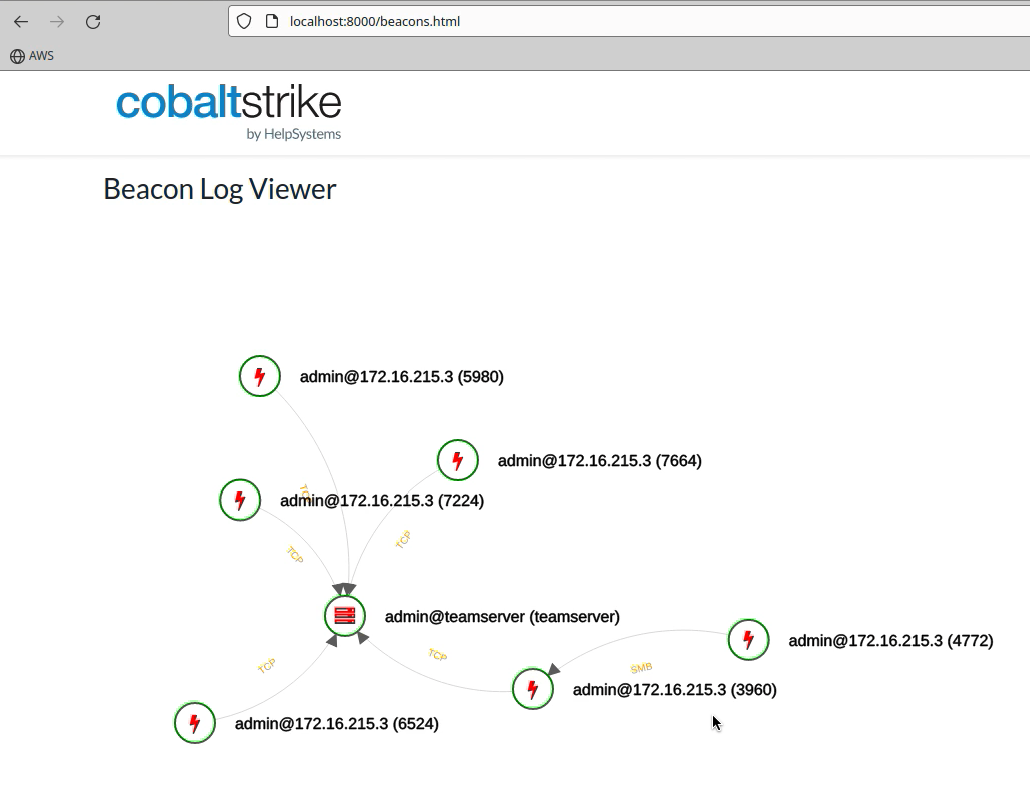 cobalt-strike/sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
 iamblacksolo2-bugbounty/poc2-cve-2025-55182
Multi-mode vulnerability scanner for Next.js RCE (CVE-2025-66478/55182) with safe side-channel detection, RCE proof-of-concept, WAF bypass…
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.