
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
415 results
wnfexec preview

wnfexec

GitHubustayready/wnfexec

WNF Code Execution Library Using C#

binary-exploitationexploitationpayload-development+4
1106 years ago
CasperStager preview

CasperStager

GitHubustayready/casperstager

PoC for persisting .NET payloads in Windows Notification Facility (WNF) state names using low-level Windows Kernel API calls.
exploitationpayload-developmentpersistence-mechanisms+2
1527 years ago
CLR-Unhook preview

CLR-Unhook

GitHubhwbp/clr-unhook

Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…

defensive-toolsexploitationpayload-development+3
2149 months ago
VeeamDumper-BOF preview

VeeamDumper-BOF

GitHubmwr-cybersec/veeamdumper-bof

A credential extraction BOF for Veeam Backup and Replication and Veeam One
password-attackspayload-developmentpenetration-testing+2
801 day ago
doublepulsar-usermode-injector preview

doublepulsar-usermode-injector

GitHubwithsecurelabs/doublepulsar-usermode-injector

A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
exploitationmalware-analysispayload-development+2
1239 years ago
Jormungandr preview

Jormungandr

GitHubidov31/jormungandr

Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.

adversarial-attackpayload-developmentpost-exploitation+1
2452 years ago
VBA-macro-experiments preview

VBA-macro-experiments

GitHubadepts-of-0xcc/vba-macro-experiments

Collection of VBA macro published in our twitter / blog
adversarial-attackpassword-attackspayload-development+2
1574 years ago
HintInject preview

HintInject

GitHubfrkngksl/hintinject

A PoC project for embedding shellcode to Hint/Name Table
binary-analysisexploitationpayload-development+3
1135 months ago
REC2 preview

REC2

GitHubg0h4n/rec2

REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…

command-and-controlpayload-developmentpenetration-testing+3
1612 years ago
WPTaskScheduler_CVE-2024-49039 preview

WPTaskScheduler_CVE-2024-49039

GitHubje5442804/wptaskscheduler_cve-2024-49039

WPTaskScheduler RPC Persistence & CVE-2024-49039 via Task Scheduler
exploitationpayload-developmentpersistence-mechanisms+4
1481 year ago
SCCM-CVE-2026-47301-Remote-Code-Execution-Exploit preview

SCCM-CVE-2026-47301-Remote-Code-Execution-Exploit

GitHubomribaso/sccm-cve-2026-47301-remote-code-execution-exploit

Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…

exploitationpayload-developmentpenetration-testing+3
1011 month ago
JavaPayload preview

JavaPayload

GitHubschierlm/javapayload

JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
exploitationmisconfigurationpayload-development+3
1281 year ago
NimDllSideload preview

NimDllSideload

GitHubbyt3bl33d3r/nimdllsideload

DLL sideloading/proxying with Nim!
binary-analysispayload-developmentpayload-generation+2
1753 years ago
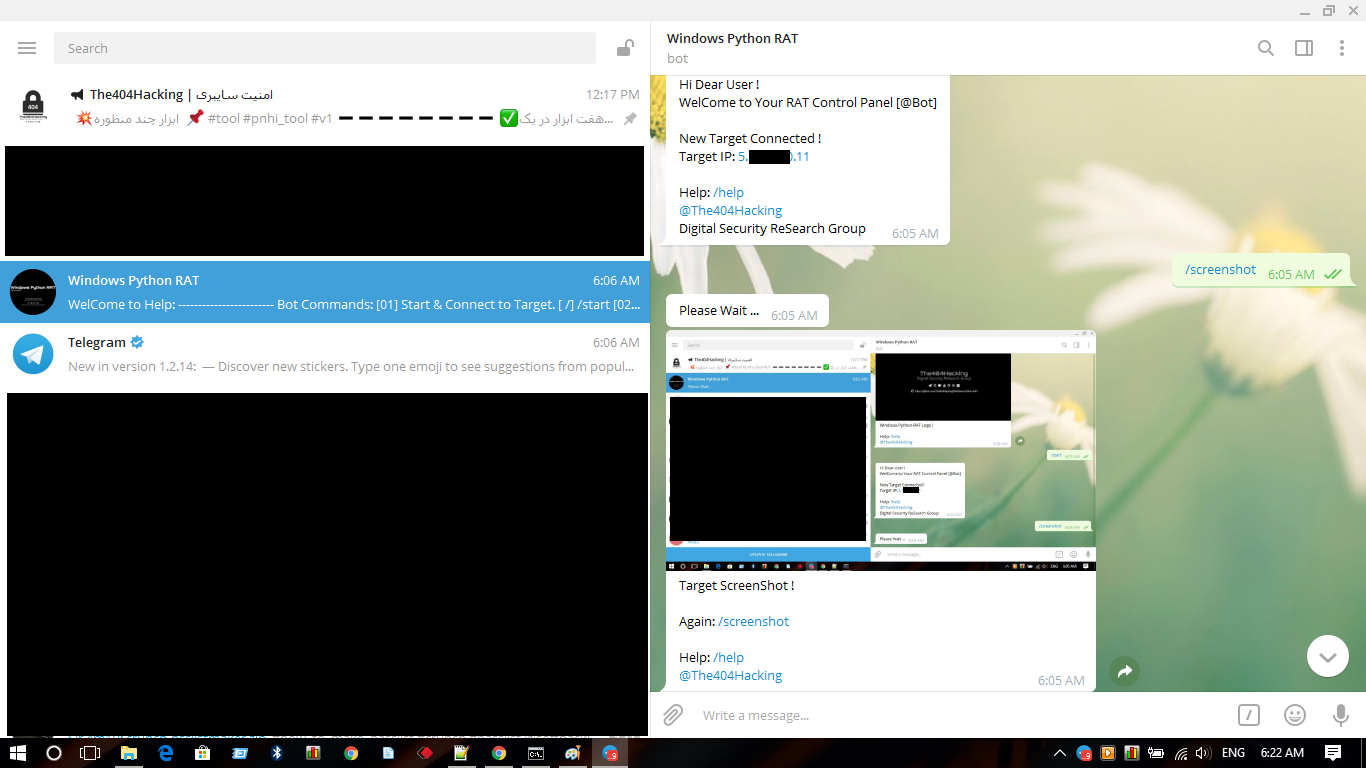
Windows-Python-RAT preview

Windows-Python-RAT

GitHubthe404hacking/windows-python-rat

A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
api-securitycommand-and-controlpayload-development+3
1186 years ago
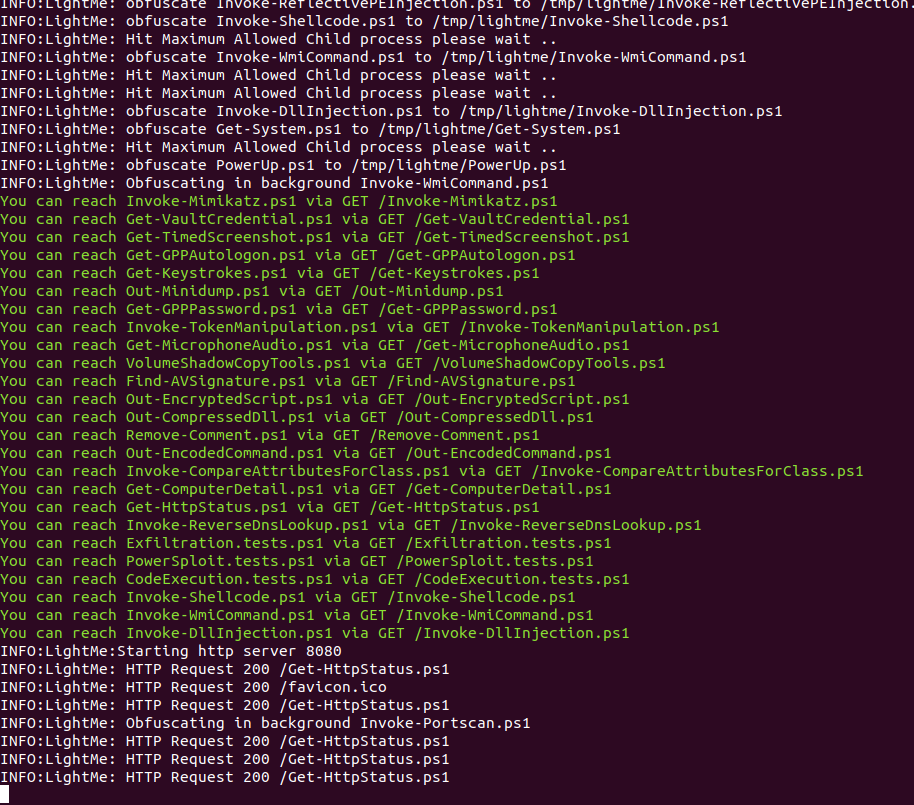
LightMe preview

LightMe

GitHubsafebuffer/lightme

HTTP Server serving obfuscated Powershell Scripts/Payloads
command-and-controlpayload-developmentpayload-generation+2
955 years ago
CVE-2020-1066-EXP preview

CVE-2020-1066-EXP

GitHubcbwang505/cve-2020-1066-exp

Local privilege escalation exploit for CVE-2020-1066 targeting Windows 7 and Server 2008 R2. Leverages arbitrary file replacement via Windows…
binary-exploitationexploitationpayload-development+3
1866 years ago
execute-assembly-pico preview

execute-assembly-pico

GitHubofasgard/execute-assembly-pico

A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.
payload-developmentpenetration-testingpost-exploitation+2
1447 months ago
asminject preview

asminject

GitHubbishopfox/asminject

Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…

container-escapepayload-developmentpenetration-testing+2
1493 years ago
Previous1…789…24Next