
 idov31/jormungandr
Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.


Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel. The only supported type of COFF is an x64 kernel COFF (meaning, a COFF that uses functions from either NTOSKRNL or SSDT). This project is not supported to run with VBS enabled because it is using pools with execute permissions but this project should work for any version of Windows starting from Windows 7.
If you are unfamiliar with COFF and COFF loading, please refer to TrustedSec's blog post about COFF loaders.
To communicate with the driver, you can use and compile the example file with CMake. This is an example of the most basic usage:
int main() {
    HANDLE hDrv = CreateFile(DRIVER_NAME, GENERIC_WRITE | GENERIC_READ, 0, nullptr, OPEN_EXISTING, 0, nullptr);

    // ...

    BOOL result = WriteFile(hDrv, &data, sizeof(data), &bytesWritten, NULL);

    // ...
}
To run and execute the existing example, all you have to do is create your own COFF or use the example:
JormungandrExample.exe example.out
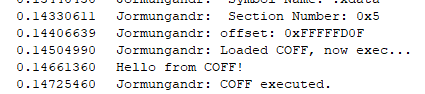
To write a kernel COFF, create a new C file and import the functions you want as follows:
DECLSPEC_IMPORT <FUNCTION_RETURN_TYPE> __cdecl <LIBRARY>$<FUNCTION_NAME>(<PARAMETERS>);
Replace the <FUNCTION_RETURN_TYPE> with the return type of the function you want, the <LIBRARY> can be either ntoskrnl or ntdll the rest is the signature of the function. After the function is imported, you can use it the way you are used to writing code.
To build the COFF, use mingw with the following command:
x86_64-w64-mingw32-gcc -c example.c -o example.out
To compile the client, you will need to install CMake and Visual Studio 2022 installed and then just run:
cd <JORMUNGANDR PROJECT DIRECTORY>/Example
mkdir build
cd build
cmake ..
cmake --build .
To compile the project, you will need the following tools:
Clone the repository and build the driver.
To test it in your testing environment run those commands with elevated cmd:
bcdedit /set testsigning on
After rebooting, create a service and run the driver:
sc create nidhogg type= kernel binPath= C:\Path\To\Driver\Nidhogg.sys
sc start nidhogg
To debug the driver in your testing environment run this command with elevated cmd and reboot your computer:
bcdedit /debug on
After the reboot, you can see the debugging messages in tools such as DebugView.
Thanks a lot to those people that contributed to this project:







