

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
execute-assembly-pico — A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory. | Kitploit
Tools/GitHubGitHub/ofasgard/execute-assembly-pico
ShellcodePost-ExploitationPenetration TestingRed TeamingPayload Development
GitHubofasgard/execute-assembly-pico

execute-assembly-pico

A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.

View Repository
14218359 months agoReviewed by Kitploit
Share

Execute Assembly PICO

A PICO for Crystal Palace that implements native CLR hosting to execute an appended .NET assembly in memory, using the same technique as the donut shellcode generator. This allows you to load .NET tools like Rubeus or Seatbelt from position-independent code without dropping them on the disk.
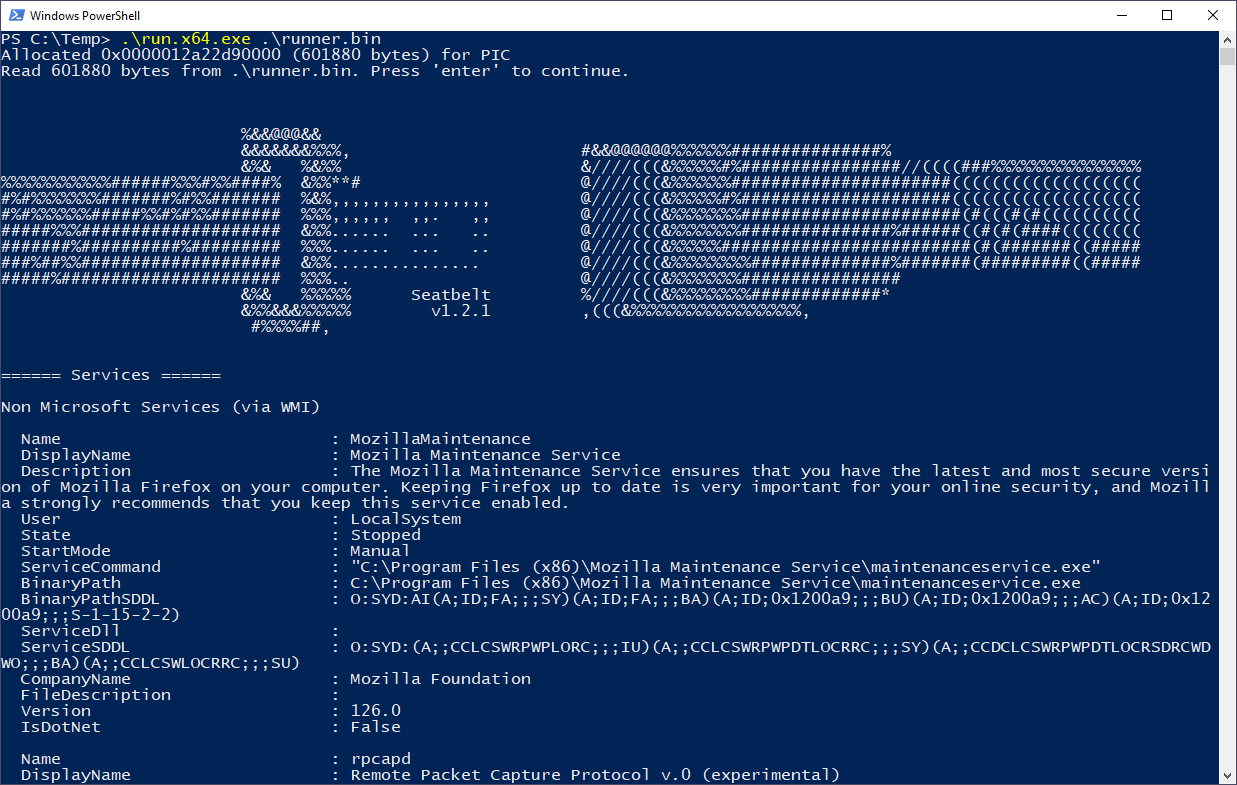
A screenshot of the PICO in action, executing an appended Seatbelt assembly

Building

You will need MinGW GCC, the zip utility, and the CPL executables needed to link the project. Modify config.spec to specify the .NET assembly you want to link with the project and the commandline arguments you want to pass. Modify Makefile to specify the location of crystalpalace.jar.

To build the PICO by itself (as a COFF), run make pico. To build the example runner and link it with the PICO, run make runner.

The example runner is written to out/runner.bin. The default configuration invokes an appended Rubeus assembly to execute "asktgt" with some generic dummy creds when you execute it:

A screenshot of the PICO in action, executing an appended Rubeus assembly

Using the PICO

The signature of the PICO's entrypoint is:

HRESULT (*EXECUTE_ASSEMBLY_PICO)(char *assembly, size_t assembly_len, WCHAR *argv[], int argc);

The first two arguments should contain a pointer to a raw .NET assembly and its size. The second two arguments are used to pass string parameters to the assembly when it is invoked.

Capturing Output

This PICO just invokes the assembly with the arguments you provided. It doesn't make any attempt to capture the output.

If you need to provide input via STDIN or capture the output from STDOUT, you should modify your loader to use WIN32 API calls like CreatePipe() and SetStdHandle() and connnect the standard I/O devices for your process to an anonymous pipe. Then you can read from and write to it as usual.

Credits

  • Raphael Mudge for Crystal Palace and LibTCG.
  • XPNSec for this gist which helped me understand the basic process of CLR hosting.
  • TheWover for the Donut generator/loader. I referenced its in-memory assembly execution extensively and used clr.h directly in the PICO.
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →






