

evil-winrm-py
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
authenticationcommand-and-controllateral-movement+7
418
adityatelange/evil-winrm-pyExecute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 0xtriboulet/revenant
Revenant - A 3rd party agent for Havoc that demonstrates evasion techniques in the context of a C2 framework
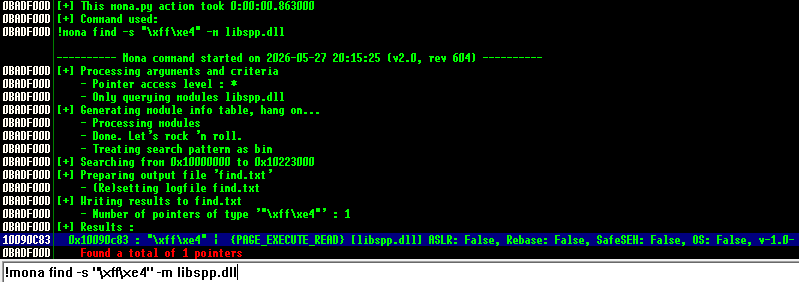 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 gabemarshall/brosec
Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.
 dereeqw/netspy
NetSpyC2 – Python C2 Server with RSA Key Exchange and AES-GCM Encrypted Sessions
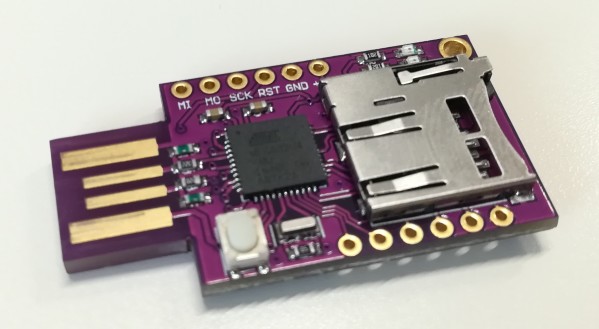 mharjac/bad_ducky
Rubber Ducky compatible clone based on CJMCU BadUSB HW.
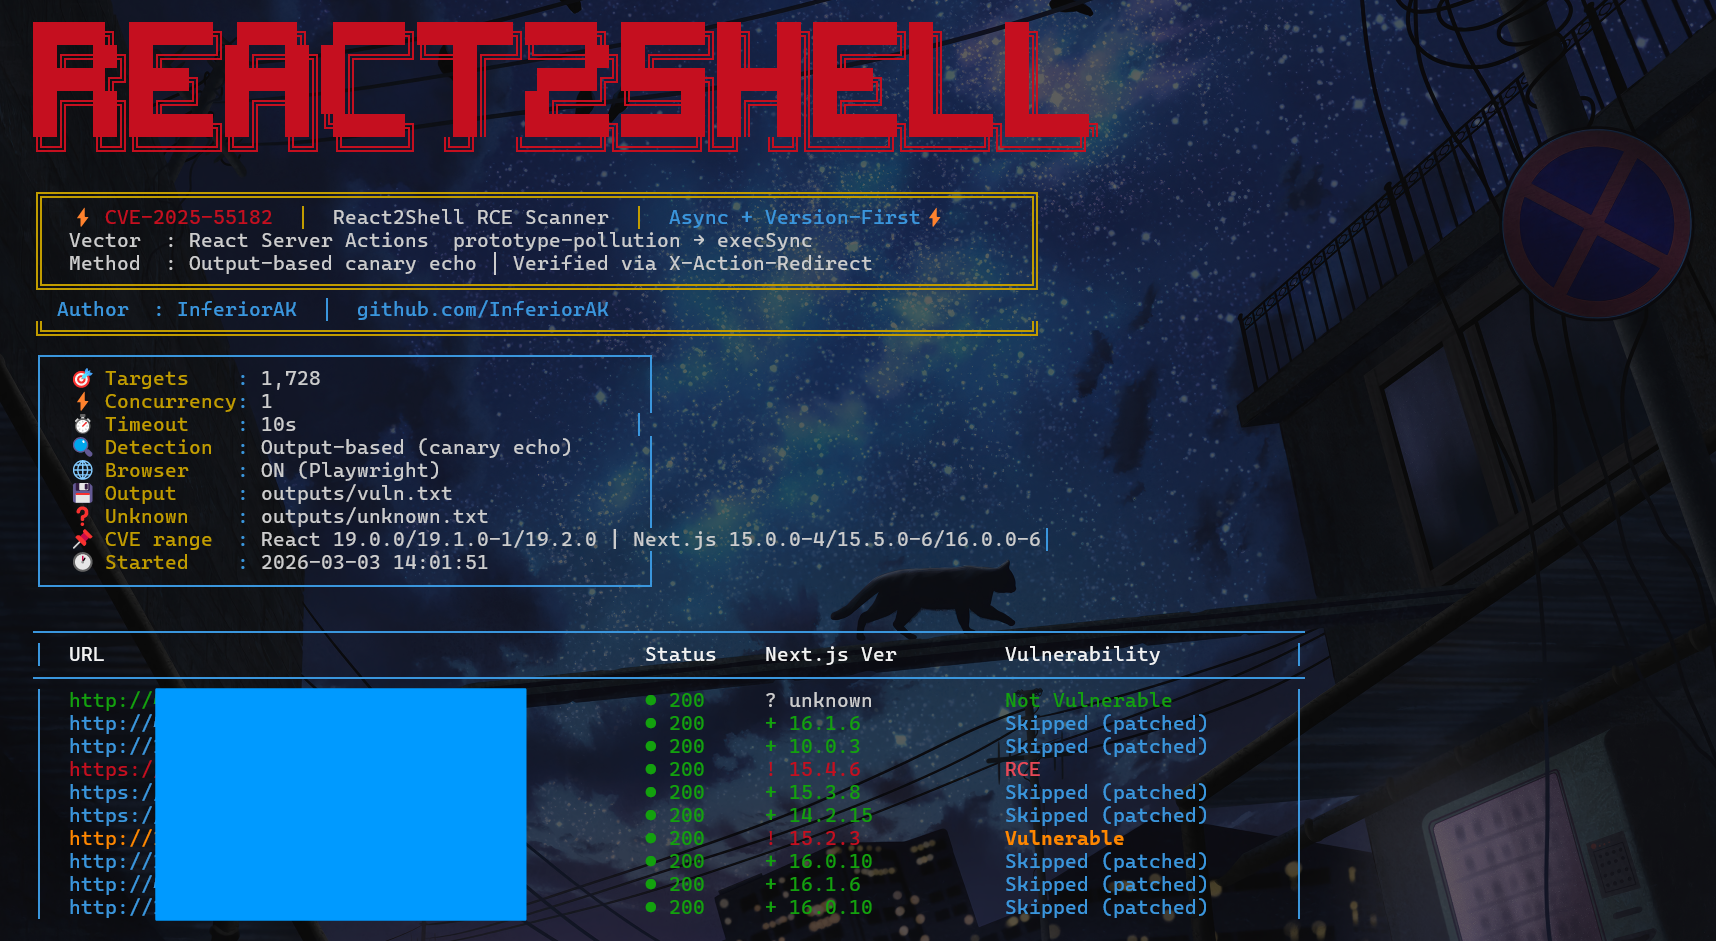 inferiorak/cve-2025-55182-react2shell-async-scanner
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 mr-un1k0d3r/thundershell
Python / C# Unmanaged PowerShell based RAT
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
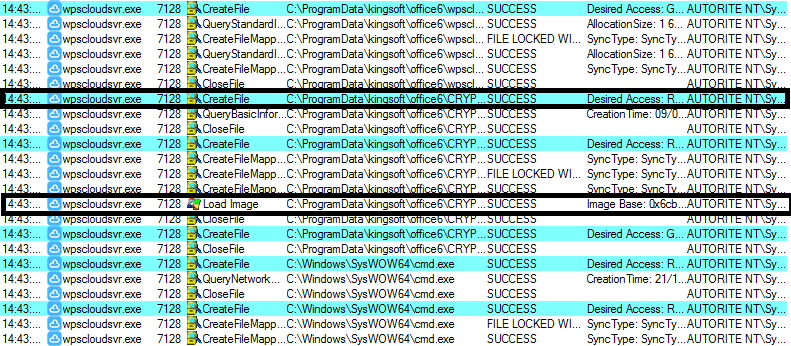 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943