

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
KINGSOFT-WPS-Office-LPE — CVE-2022-25943 | Kitploit
Tools/GitHubGitHub/hadimed/kingsoft-wps-office-lpe
Privilege EscalationExploitationLateral MovementPost-ExploitationMisconfigurationPayload DevelopmentBinary Exploitation
GitHubhadimed/kingsoft-wps-office-lpe

KINGSOFT-WPS-Office-LPE

CVE-2022-25943

View Repository
5815464 years agoReviewed by Kitploit
Share

JVN Advisory

https://jvn.jp/en/vu/JVNVU90673830/

The following CVE number have been assigned:

  • CVE-2022-25943

KINGSOFT WPS Office LPE

WPS Office is an office suite for Microsoft Windows, macOS, Linux, iOS, Android, and HarmonyOS developed by Zhuhai-based Chinese software developer Kingsoft.

Exploring WPS

One of the nicest features that WPS offers is a cloud service to save your documents , work etc ... , this service by default is set to manual , it's started only if you navigate to WPS cloud into the WPS office panel but the service gets started with the current user privilege (Low priv).

Vulnerability

Looking into the early imports done by wps cloud service once started , it looks like it will first try to import a DLL called CRYPTSP.DLL and other ones from *C:\ProgramData\kingsoft\office6* if they aren't there and by default they aren't , the service will load it from System32 as you can see :
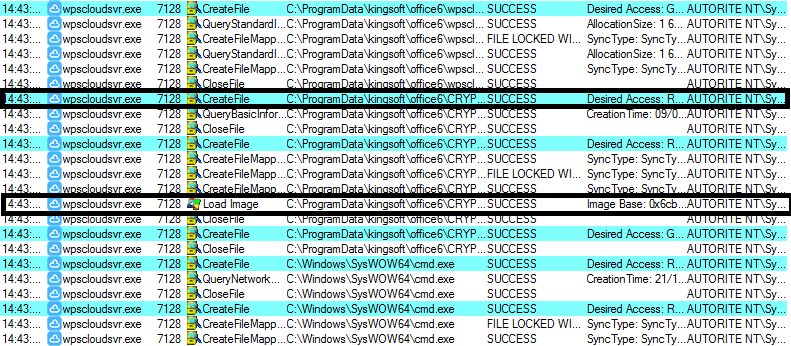


The issue here is that the ACL for that directory is configured as read write to all users, an attacker can plant a malicious DLL there and restart the executable , but it gets started as current priv level (low priv user) , unless we start the executable as service (Since it's installed as one) with something like net start wpscloudsvr which will start the service as NT AUTHORITY .
The issue here seems to be more of an ACL misconfiguration .

Exploit

My exploit is simple , it will copy the crafted DLL ( change Administrator password ) to the target directory restart the service , now an access to administrator account is available , which means I have access to sedebugpriv from there I steal the winlogon token and start cmd as NT AUTHORITY / System .


PoC

https://user-images.githubusercontent.com/57273771/152659158-7f3a5607-40d9-41b6-85c5-7ed3ca83d0e5.mp4

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    591
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    481
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    389
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    332
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    255
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    247

Explore all tools

Browse our collection of tools

View all tools →





