

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
DeepSleep — A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC | Kitploit

Tools/GitHubGitHub/theflink/deepsleep
Memory ForensicsExploitationRed TeamingPayload Development
GitHubtheflink/deepsleep

DeepSleep

A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC

View Repository
376551464 years agoReviewed by Kitploit
Share

DeepSleep

A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC.

Huge thanks to @waldoirc for documenting large parts of this technique on his blog
This implementation is different in that it does not make use of any APCs and is fully implemented as PIC.

Description

I have created this to better understand how to evade memory artifacts using a Gargoyle like technique on x64. The idea is to set up a ROPChain calling VirtualProtect() -> Sleep() -> VirtualProtect() to mark my own page as N/A while Sleeping.

Unlike Gargoyle and other Gargoyle-like implementations, I fully rely on ROP and do not queue any APC. DeepSleep itself is implemented as fully PIC, which makes it easier to enumerate which memory pages have to be hidden from scanners.

While the thread is active, a MessageBox pops up and DeepSleep's page is marked as executable. While Sleeping, the page is marked as N/A.

This effectively bypasses Moneta at the time of writing if DeepSleep is injected and the executing thread's base address does not point to private commited memory.

I have verified this using the Earlybird injection technique to inject DeepSleep.bin into notepad.exe
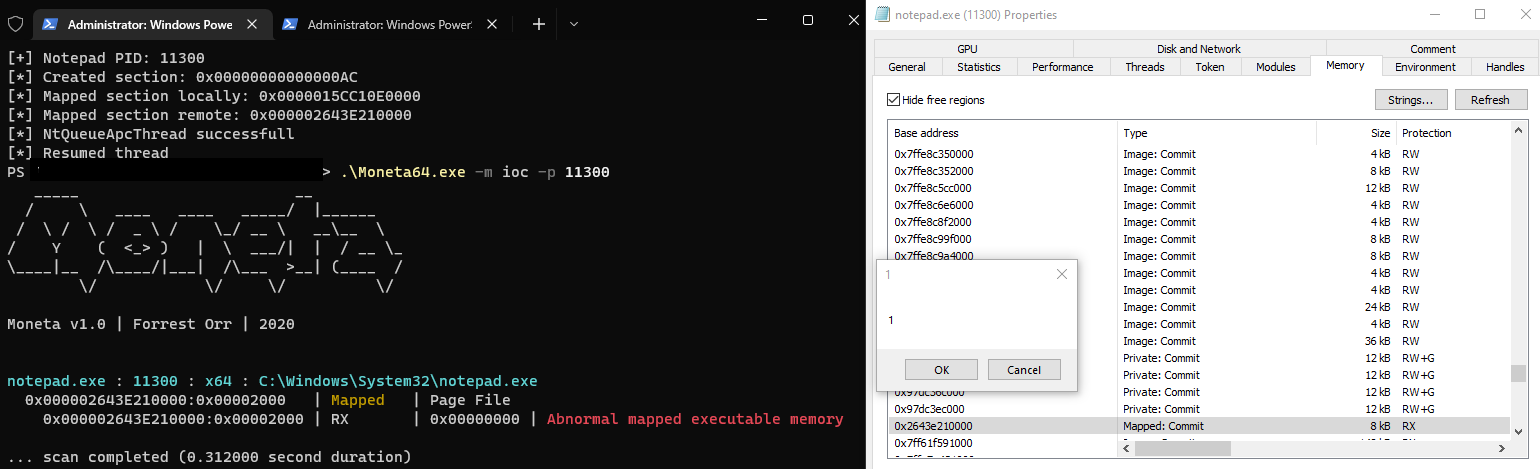
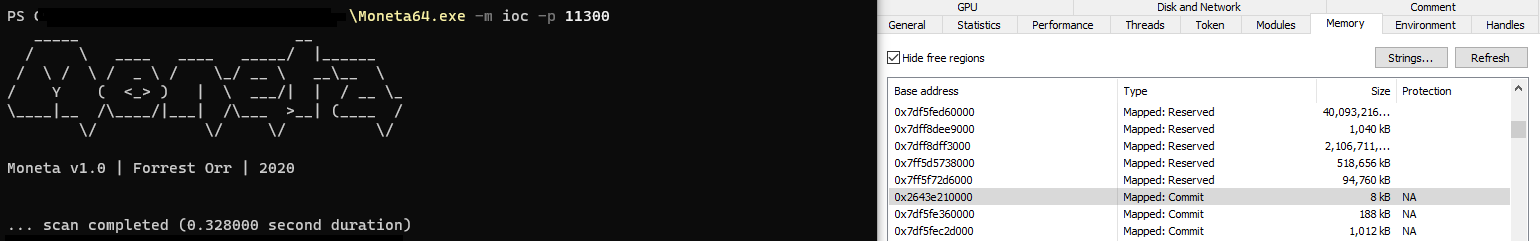
Moneta finding DeepSleep while showing msgbox Moneta not finding DeepSleep while showing msgbox

Usage

Using Mingw:
Type make and a wild DeepSleep.bin appears.
Alternatively use the precompiled DeepSleep.bin :-)

Future Work and limitations

Future Work

I might release a loader for CS or other C2 agents. Similarly to YouMayPasser, the loader would hook sleep using HW breakpoints to avoid suspicious modifications of kernel32.dll.

Limitations

This was tested on 10.0.19044 N/A Build 19044

The ROPgadgets I am relying on might not exist in ntdll.dll in other versions of Windows. It is probably a good idea to make use of smaller and more generic ROPgadgets and to enumerate the gadgets in more dlls than ntdll.dll.

Detection

The callstack to a thread in the DelayExecution state includes unknown/tampered memory regions and additionally includes addresses to VirtualProtect(). Hunt-Sleeping-Beacons detects this.
It may be possible to apply that metric to other C2 using a different technique to wait between callbacks.

Weird Stack

Credits

@waldoirc for documenting large parts of the technique here
@forrest Orr for Moneta
Josh Lospinoso for the original Gargoyle technique


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →




